cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

625 articles

Detection & Defense · huntress.com

Huntress Shares Practical Defenses Against Ransomware Targeting ESXi Hypervisors

Huntress reports a rise in hypervisor ransomware in its 2025 case data and offers ESXi defenses, including MFA, network segregation, runtime hardening, patching, immutable backups, and log monitoring.
Dec 8, 2025
Detection & Defense · huntress.com

Huntress Adds Datacenter Infrastructure to Identity Attack Detection

Huntress describes a detection method that evaluates datacenter-originated identity logins using Autonomous System context and activity baselines. The company says it reduced millions of events to hundreds of daily investigations and helped expose missed initial access.

Dec 2, 2025
Detection & Defense · wiz.io

Detect OAuth Abuse in Entra ID: Device-Code Phishing, ROPC and Persistence

Wiz describes how attackers abuse device-code phishing and legacy ROPC flows in Azure environments, including device registration for persistence, and provides Entra ID log patterns and KQL queries to detect the activity.

Nov 27, 2025
Detection & Defense · hunt.io

HuntSQL Recipes Help Analysts Find and Track Cobalt Strike Infrastructure

The guide presents HuntSQL queries for detecting and clustering Cobalt Strike infrastructure using fingerprints such as watermarks, public keys, beacon behavior, URIs, and hosting data.

Nov 19, 2025
Detection & Defense · hunt.io

Threat Detection Lead Details ClickFix Investigation and SOC Hunting Practices

Joseph Harrison discusses threat hunting and SOC operations, including an investigation that traced a blocked PowerShell download cradle to a ClickFix phishing page and led to new indicators being blocked.

Oct 23, 2025
Detection & Defense · huntress.com

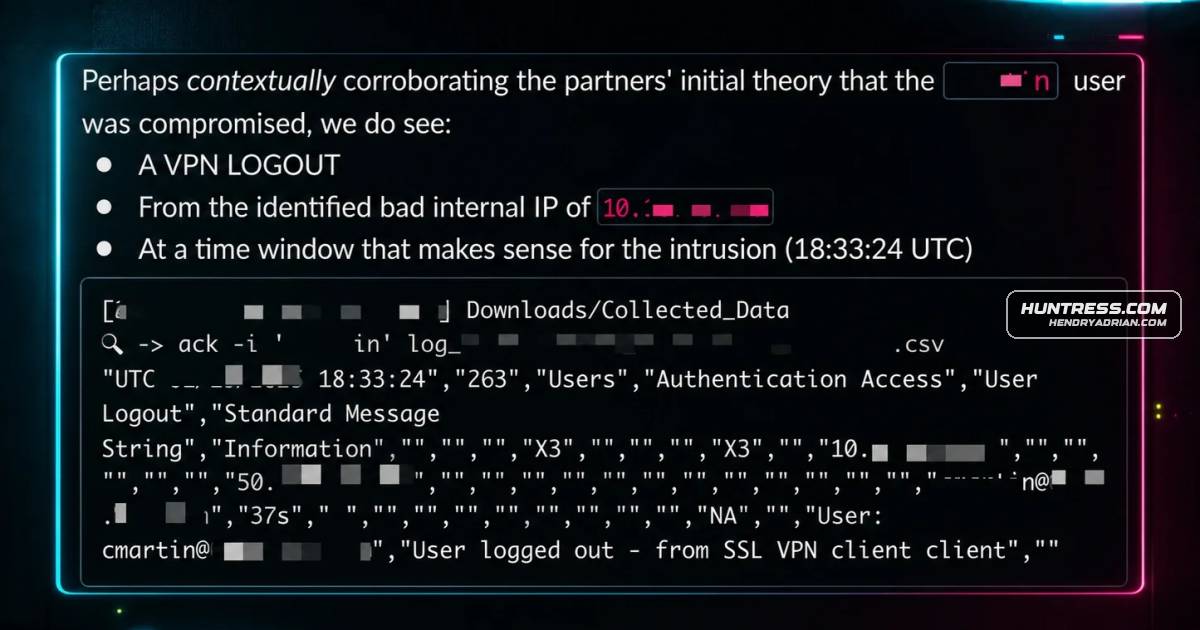
How Incident Responders Can Investigate Intrusions Despite Missing Telemetry

Huntress responders share ways to investigate with incomplete Windows, VPN and cloud logs, using available evidence as pivots, explaining uncertainty, and improving logging and retention.

Oct 21, 2025
Detection & Defense · darkowl.com

Cyber Hygiene Tips to Protect Work and Home

A practical guide to reducing cyber risk at work and home with phishing-resistant MFA, unique passwords, software updates, safer Wi-Fi, cautious handling of links and QR codes, and regular account and device checkups.

Oct 16, 2025
Detection & Defense · wiz.io

How to Defend Internet-Exposed Databases from Ransomware

Attackers can abuse weakly protected, internet-exposed databases to steal or destroy data using legitimate database commands. The article outlines exposure reduction, strong authentication, backups, and checks for ransom-note indicators.

Oct 6, 2025
Detection & Defense · hunt.io

Guide Shows How to Hunt Exposed C2 Panels Using Web Fingerprints

A practical guide demonstrates how defenders can identify exposed Supershell, HookBot, Chaos RAT, UnamWebPanel, Metasploit, and Mythic panels using URL paths, page titles, favicon hashes, and other web artifacts, then block and report exposed instances.

Sep 25, 2025
Detection & Defense · wiz.io

Wiz Finds Common Security Risks in Vibe-Coded Apps and Offers Mitigations

Wiz Research says one in five organizations build on vibe-coding platforms and highlights risks including client-side authentication, exposed secrets, permissive database access, and public internal apps, with mitigation guidance.

Sep 18, 2025
Detection & Defense · huntress.com

How to Defend Against Hackers Impersonating IT Staff

The article describes how threat actors may use false identities and deepfakes to obtain IT jobs and privileged access, and recommends stronger hiring checks, access controls, monitoring, and insider-threat response plans.

Sep 18, 2025
Detection & Defense · cloudsek.com

CloudSEK Finds SPF Misconfiguration That Could Enable Vendor Email Spoofing

CloudSEK found a logistics SaaS vendor’s SPF record set to soft fail, potentially allowing unauthorized emails to be delivered as if they came from the vendor. It recommends stricter SPF, DKIM, and DMARC controls.

Sep 4, 2025
Detection & Defense · huntress.com

Hidden Email Text Can Turn Gemini Summaries Into Phishing Lures; MSPs Urged to Add Safeguards

A researcher demonstrated that hidden HTML or CSS instructions can influence Gemini email summaries to display phishing messages. The article says exploitation in the wild is not known and advises MSPs to use safeguards rather than disable Gemini.

Aug 26, 2025
Detection & Defense · huntress.com

How to Spot Recruiting Scams and Verify Legitimate Job Offers

Huntress outlines recruiting-scam red flags and ways to verify job offers, including checking official channels, avoiding links in suspicious messages, and never paying fees. It also describes monitoring for impersonators and removing fake postings.

Aug 5, 2025
Detection & Defense · team-cymru.com

Team Cymru Adds Tags for Neptune Loader, Gremlin Stealer and Unam Panels

Team Cymru describes fingerprinting Neptune Loader, Gremlin Stealer and Unam Web Panel controllers with service banners, then using Scout tags and NetFlow pivots to identify communicating IPs and potential victims.

Aug 4, 2025
Detection & Defense · huntress.com

Huntress Explains How to Turn Windows Event Logs Into Intrusion Insights

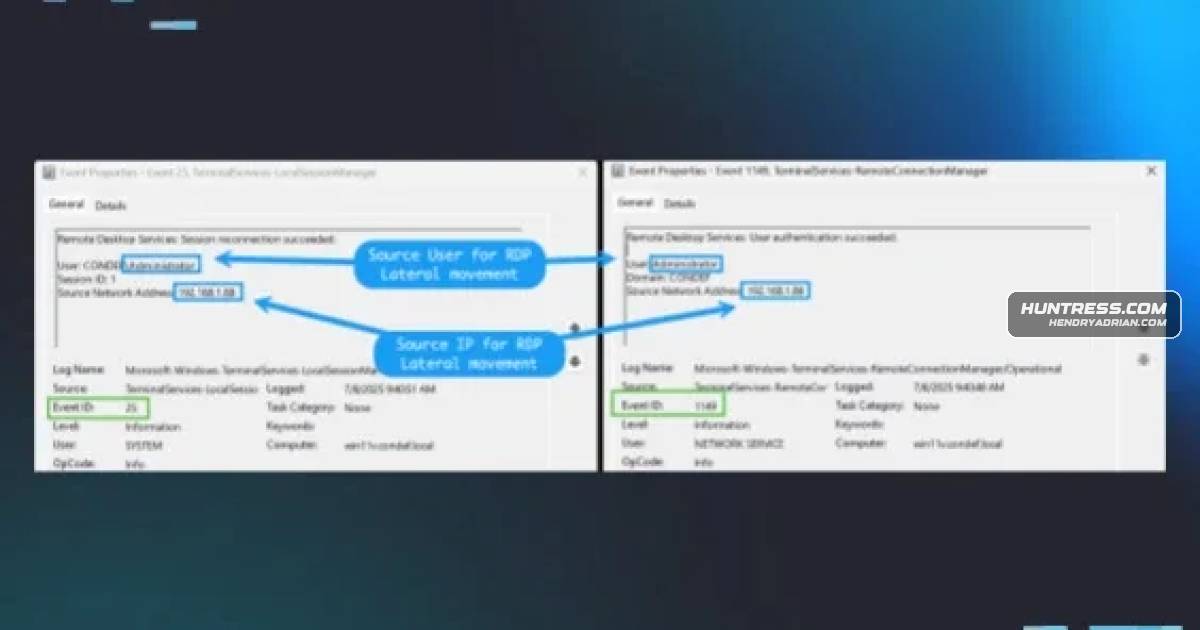
Huntress outlines practical methods for analyzing Windows authentication, credential-access and RDP logs to investigate suspicious activity, including approaches that work without a SIEM.

Jul 30, 2025
Detection & Defense · darktrace.com

Darktrace Shows Cyber AI Analyst Investigating Four Advanced Threat Incidents

Darktrace presents four customer investigations involving ShadowPad, Blind Eagle, ransomware, and RansomHub to show how Cyber AI Analyst correlates activity across attack chains and supports faster threat triage and containment.

Jul 30, 2025
Detection & Defense · cloudsek.com

How Security Teams Can Separate Real Breaches From Recycled Data

The article explains how recycled, scraped, or fabricated breach claims create alert fatigue, and offers security teams a checklist for validating sources, samples, and data before prioritizing a response.

Jul 9, 2025
Detection & Defense · team-cymru.com

Team Cymru Details Telemetry Signals for Detecting DPRK Remote IT Workers

Team Cymru outlines telemetry signals for spotting DPRK operatives posing as remote IT contractors, including VPN and network patterns, remote-access tools, certificate fingerprints, and unusual outbound activity. It also cites an incident involving LND[.]fi.

Jun 30, 2025
Detection & Defense · huntress.com

Huntress Review Finds ActivTrak Exclusion on Medical Clinic Systems

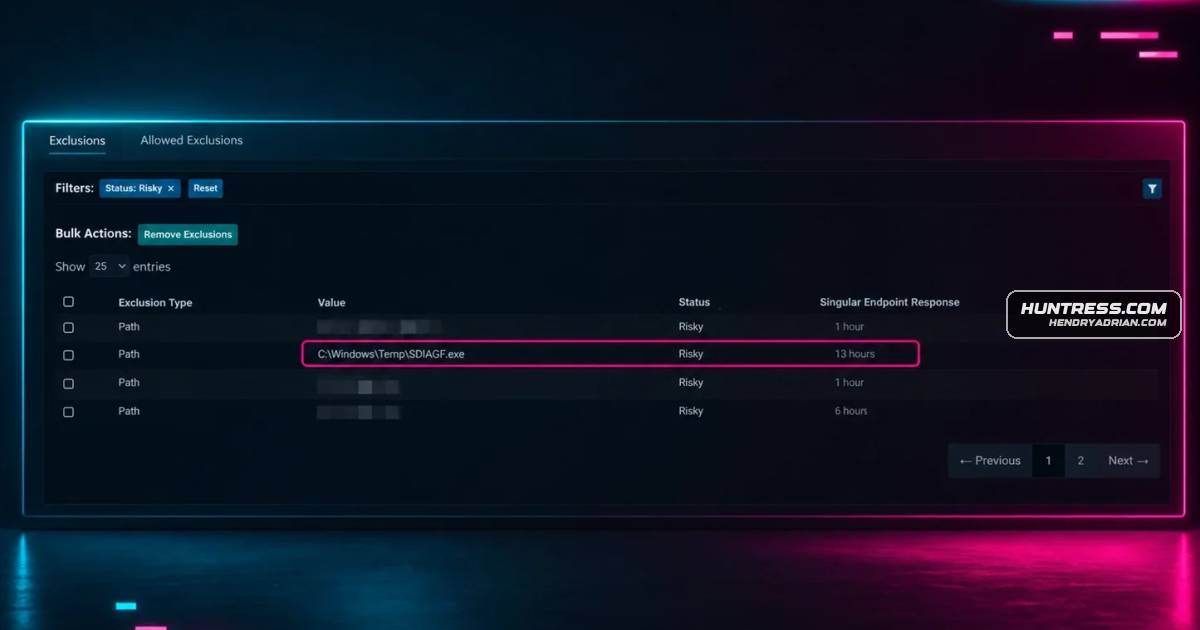
A Huntress review found a Defender exclusion for ActivTrak’s BGStart.exe on 13 hosts at a medical clinic, including a hypervisor, domain controller and X-ray machine. The clinic decided not to renew the software; Huntress reported no evidence of tenant compromise.

Jun 17, 2025
Detection & Defense · wiz.io

How to Build a Cloud-Focused Security Operations Center

The article outlines how to adapt SOC teams, processes, and technology for cloud security, recommending cloud-focused training, contextualized telemetry, threat hunting, response automation, and outcome-based metrics.

Jun 11, 2025
Detection & Defense · wiz.io

Wiz Shares Security Rules for AI-Assisted Coding Tools

Wiz describes how security-focused rules files can guide AI coding assistants, reviews research on reducing vulnerabilities through prompting, and shares baseline rules for several languages, frameworks, and tools.

Jun 6, 2025
Detection & Defense · huntress.com

Defending Against Common Brute-Force, VPN, and Credential Attacks

Huntress describes common attacker techniques—including brute force, VPN compromise, tunneling, credential theft, and lateral movement—and recommends practical defenses such as MFA, account cleanup, network segmentation, and monitoring.

Jun 5, 2025
Detection & Defense · darkowl.com

What to Do After a Data Breach: Secure Accounts and Protect What Remains

The article explains why searching the dark web for stolen data is risky and unlikely to help, and recommends securing compromised accounts, changing passwords, enabling two-factor authentication, and monitoring finances.

May 27, 2025
PreviousPage 21 of 27 Next
© 2026 cyber.hendryadrian.com