cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

625 articles

Detection & Defense · netspi.com

NetSPI Details Command Execution Methods for Azure VMs and VM Scale Sets

NetSPI demonstrates Entra ID-authenticated command execution methods for Azure VMs and VM scale sets, and describes Azure Activity Log opportunities and caveats for detecting their use.
Mar 5, 2026
Detection & Defense · huntress.com

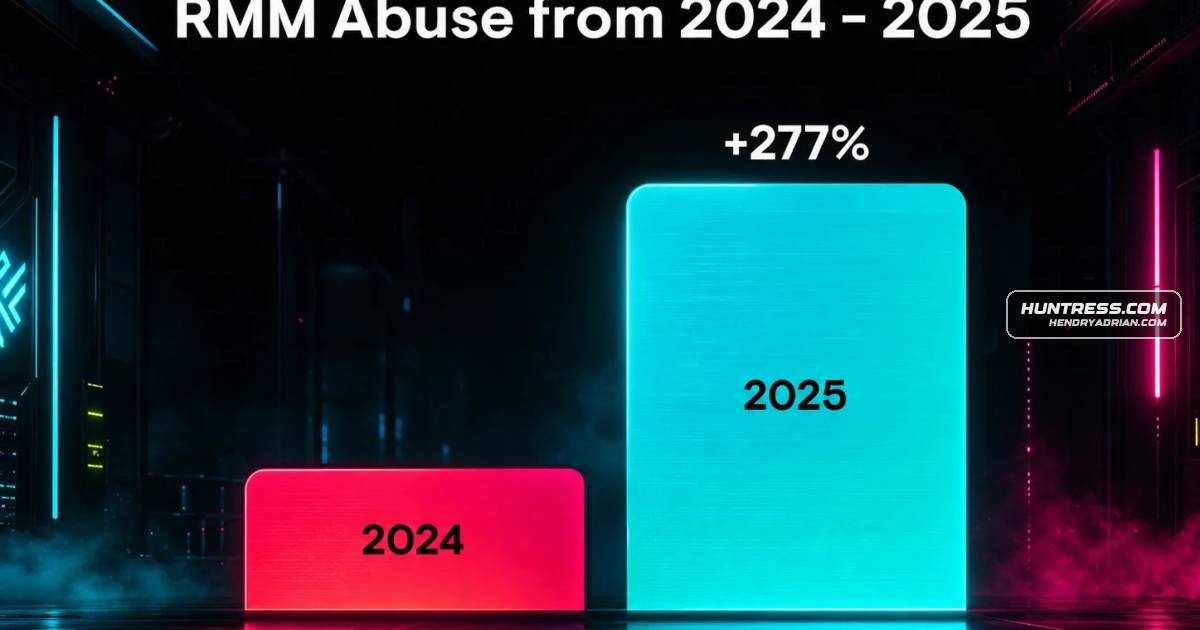
RMM Abuse Rose 277% in 2025 as Attackers Exploited Trusted Remote-Management Tools

Huntress reports RMM abuse rose 277% in 2025. Attackers use phishing or stolen credentials to gain access through legitimate tools; Huntress recommends baselining activity, fingerprinting approved tools, and monitoring anomalies.

Mar 5, 2026
Detection & Defense · cisecurity.org

How Organizations Can Defend Against Iran’s Cyber Retaliation Tactics

CIS advises organizations, especially U.S. SLTT governments, to prepare for Iranian cyber activity by patching internet-facing devices, enforcing MFA, training staff, and detecting credential abuse and living-off-the-land techniques.

Mar 4, 2026
Detection & Defense · hunt.io

Guide to Hunting Cobalt Strike, Part 4: Automating C2 Feeds for Detection

A practical walkthrough for retrieving Hunt.io’s Cobalt Strike C2 feed, filtering and structuring indicators, and deploying them in SIEM, network, and endpoint detection workflows.

Mar 3, 2026
Detection & Defense · darkowl.com

Seven Early Warning Signs Organizations Can Detect Before a Cyberattack

The article outlines seven early indicators of attacks, from unusual logins and MFA prompts to network anomalies and exposed credentials, and recommends correlating telemetry, investigating weak signals, and acting early to limit attacker dwell time.

Feb 26, 2026
Detection & Defense · elastic.co

Elastic Demonstrates LLM-Augmented Alert Triage with ES|QL COMPLETION

Elastic describes using ES|QL COMPLETION to add LLM reasoning to security-alert triage, with workflows for correlating alerts, structuring context, parsing verdicts, and filtering results before alerting.

Feb 24, 2026
Detection & Defense · thehackernews.com

Microsoft 365 Configuration Backlogs Could Let AI Scale Attacks, Expert Warns

An MSP security specialist argues that unenforced Conditional Access and identity-risk policies, legacy authentication, and over-permissioned app registrations leave Microsoft 365 tenants exposed to AI-automated attacks; he urges organizations to enforce existing mitig

Feb 23, 2026
Detection & Defense · bleepingcomputer.com

Why Workforce Access Security Must Look Beyond Identity

This sponsored article argues that identity checks alone can miss changing device risk and gaps in legacy or non-browser access. It recommends continuous user and device verification, device-based controls, proportionate enforcement, and self-service remediation.

Feb 23, 2026
Detection & Defense · microsoft.com

Microsoft Details Security Risks and Defenses for Self-Hosted OpenClaw Agents

Microsoft warns that OpenClaw can run untrusted skills and instructions with host credentials, risking data exposure, persistent state changes, and host compromise. It recommends isolation, dedicated low-privilege credentials, monitoring, and rebuild plans.

Feb 20, 2026
Detection & Defense · elastic.co

Elastic Shows Automated Triage Workflow for Chrysalis Backdoor Alerts

Elastic describes combining Attack Discovery, Workflows and Agent Builder to validate and triage alerts tied to the Chrysalis backdoor, using VirusTotal, ES|QL, case creation and Slack coordination. Elastic says the process took under four minutes.

Feb 19, 2026
Detection & Defense · huntress.com

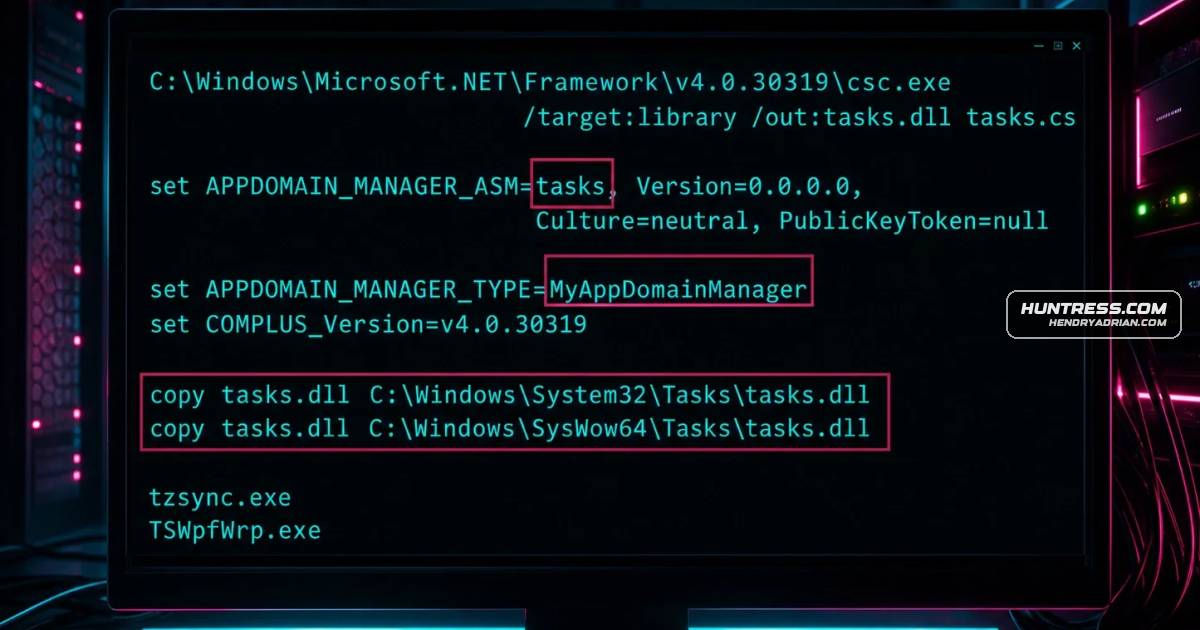
How App Domain Manager Injection Abuses Trusted .NET Applications—and How to Detect It

Huntress explains how attackers can use .NET configuration files or environment variables to load malicious assemblies through trusted applications, and recommends monitoring execution paths, configuration changes, and assembly loading.

Feb 19, 2026
Detection & Defense · team-cymru.com

Team Cymru Outlines OT Threat Hunting After Reported Polish Energy Attacks

Team Cymru uses CERT-PL’s account of reported attacks on Polish energy infrastructure to outline OT defenses, including monitoring exposed FortiGate VPNs, tracking suspicious network traffic, and using passive visibility to reduce blind spots.

Feb 17, 2026
Detection & Defense · hunt.io

Researchers Find 17,500+ Internet-Exposed OpenClaw Instances Vulnerable to Credential Theft

Hunt.io researchers identified over 17,500 exposed OpenClaw and fork instances vulnerable to unauthenticated access to stored API tokens, and detailed fingerprinting methods and mitigations for finding and securing them.

Feb 3, 2026
Detection & Defense · huntress.com

Practical Ways for Security Teams to Reduce Alert Fatigue

Huntress recommends reducing alert fatigue by prioritizing threats, reviewing the attack surface, tuning alert rules, using automation, sharing workloads, and tracking SOC response metrics.

Feb 2, 2026
Detection & Defense · darkowl.com

Five Cybersecurity Habits to Strengthen Defenses in 2026

The article recommends five repeatable security habits for 2026: strengthen identity controls, retain useful logs, prioritize exploited vulnerabilities, reduce alert noise, and practice incident response.

Jan 29, 2026
Detection & Defense · huntress.com

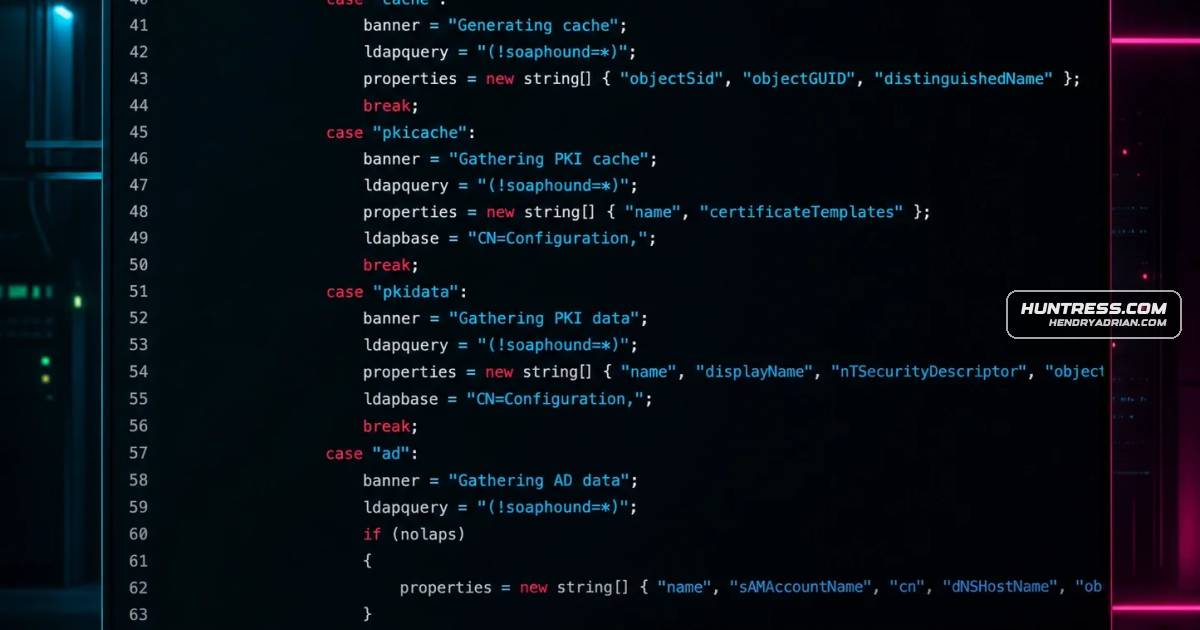
Huntress Shows How to Detect SOAPHound’s LDAP Enumeration in Event ID 1644

Huntress explains how Active Directory transforms SOAPHound’s non-existent-attribute LDAP filter into `(! (FALSE))` in Event ID 1644 logs, and describes detection patterns using the filter, attributes, client details and SDFlags.

Jan 29, 2026
Detection & Defense · team-cymru.com

Team Cymru Shares Scattered Spider Infrastructure Profile and Hunting Guidance

Team Cymru profiles infrastructure reported in Scattered Spider operations—including VPNs, residential proxies, tunneling and file-sharing services, RMM tools and SSO-phishing domains—and provides Scout queries and behavioral hunting guidance.

Jan 21, 2026
Detection & Defense · huntress.com

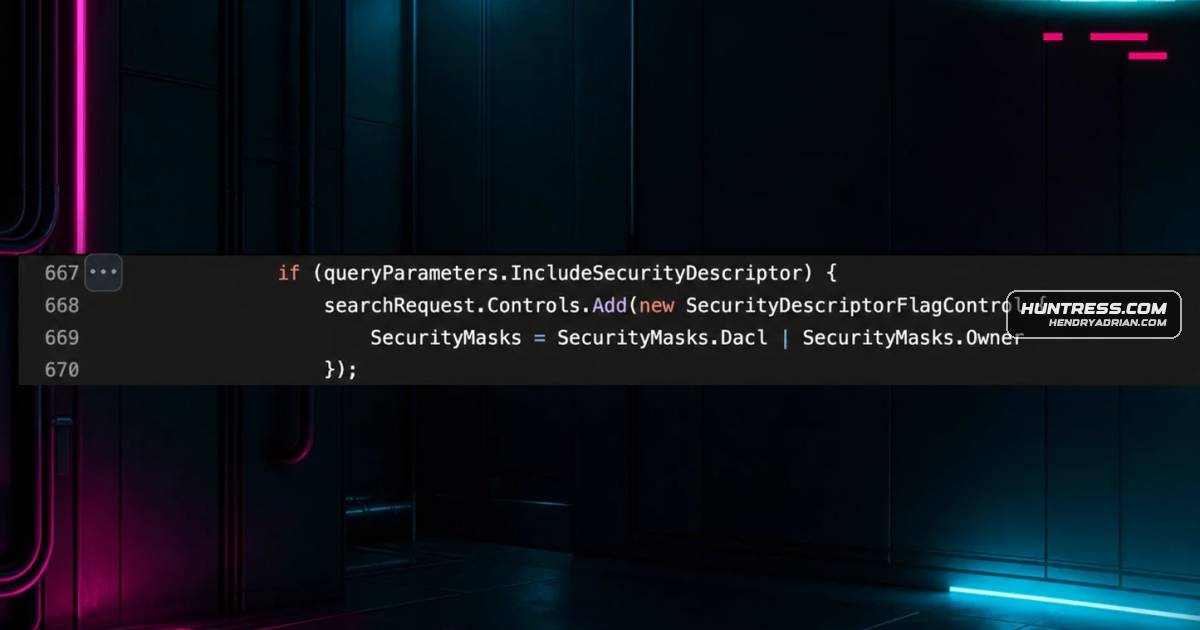
Detecting Active Directory Attack-Path Enumeration with SDFlags

The article explains how SDFlags in Event ID 1644 can help detect SharpHound-style mass LDAP enumeration of nTSecurityDescriptor, and shares tested patterns and sample detection logic for defenders.

Jan 15, 2026
Detection & Defense · hunt.io

How to Hunt Cobalt Strike C2 Infrastructure with Automated Discovery

Hunt.io’s guide demonstrates using its C2 dashboard, certificate and header pivots, and HuntSQL queries to find Cobalt Strike infrastructure, and outlines network and endpoint defenses against beacon activity.

Jan 6, 2026
Detection & Defense · huntress.com

How to Make Sigma Rules Detect LDAP Activity Despite Whitespace Variations

The article explains why Active Directory Event 1644 LDAP filters can contain inconsistent whitespace after OID-to-bitwise transformation, and shows how regex-tolerant Sigma rules and testing with real logs can improve detection.

Dec 30, 2025
Detection & Defense · huntress.com

Holiday Security Guide Covers React2Shell, ClickFix, Phishing and Practical Defenses

A Huntress webinar recap discusses active React2Shell exploitation, ClickFix, phishing through trusted services, and online scams, then offers practical steps for families to improve account, device, and social-media security.

Dec 23, 2025
Detection & Defense · team-cymru.com

Court Records and Network Telemetry Help Hunt North Korean Remote-Worker Activity

Team Cymru describes using details from a criminal complaint and global telemetry to hunt suspicious activity linked to North Korean fake IT workers, identifying a residential IP, Astrill VPN communications, and eight North Korean IPs.

Dec 18, 2025
Detection & Defense · team-cymru.com

Team Cymru Adds Pure Signal Queries to Synapse Enterprise

Team Cymru's Synapse Enterprise Power-Up brings Pure Signal telemetry into the platform, with Scout query examples for network communications, phishing infrastructure, certificate analysis, and investigating tagged IPs.

Dec 17, 2025
Detection & Defense · huntress.com

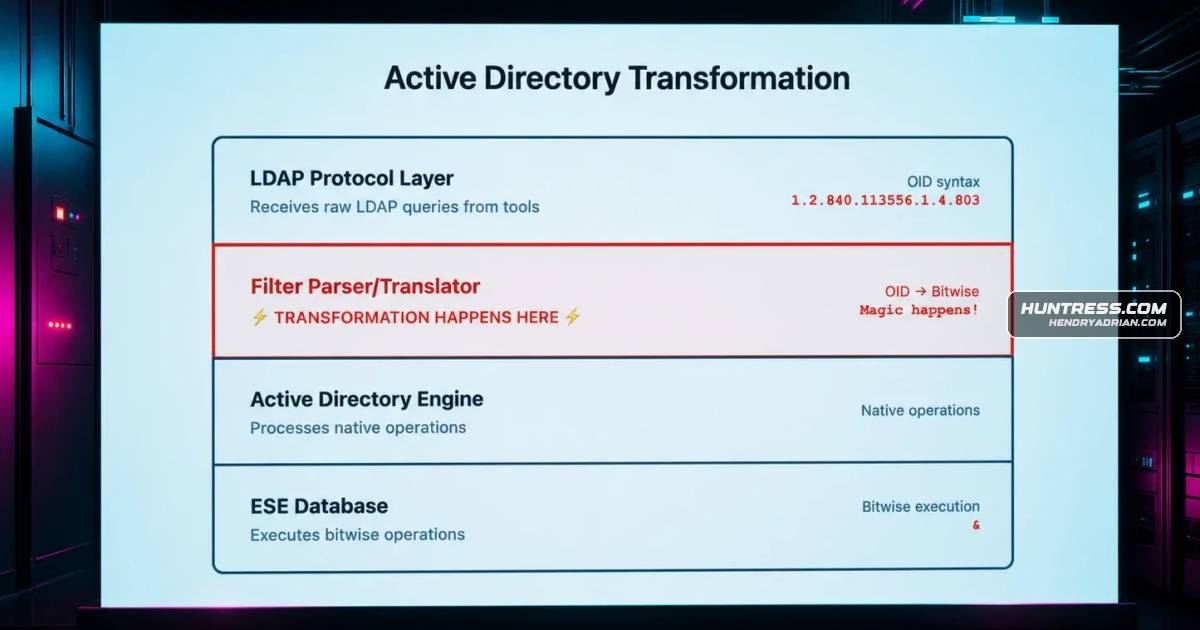
How Active Directory Transforms LDAP OIDs—and How to Build Detections That Work

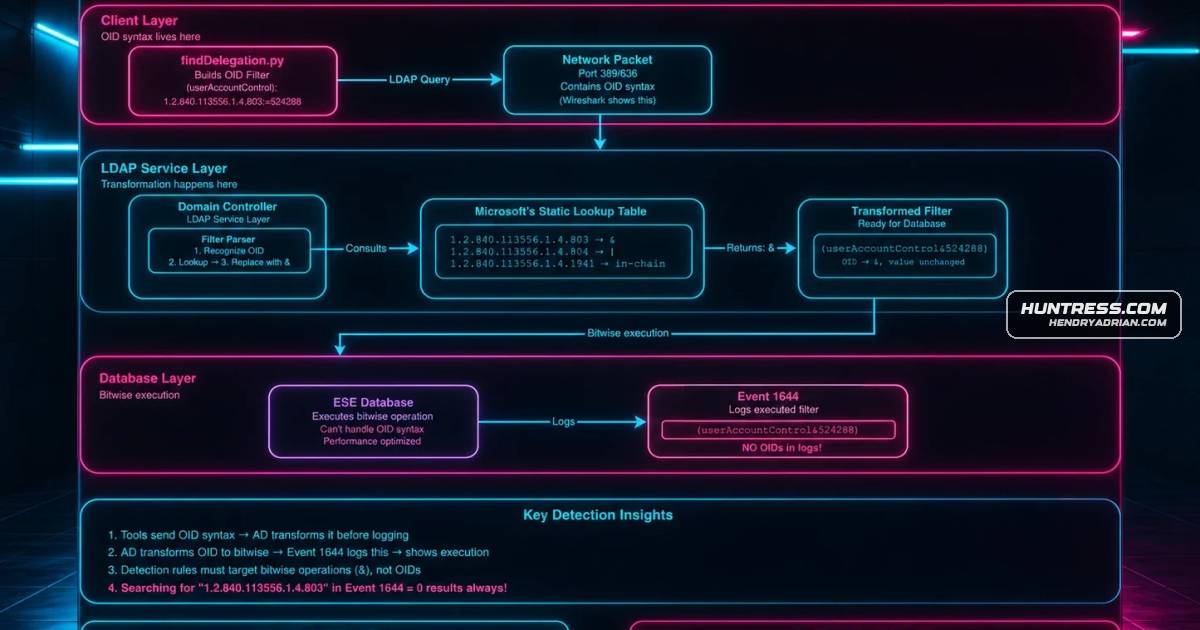
Huntress explains that Active Directory Event 1644 logs LDAP bitwise matching rules as operators rather than OIDs, causing rules that search for OIDs to miss them. It outlines enabling logs, correlating client Event 30, and validating Sigma detections.

Dec 16, 2025
PreviousPage 20 of 27 Next
© 2026 cyber.hendryadrian.com