
How to Make Sigma Rules Detect LDAP Activity Despite Whitespace Variations
Summary
The article explains why Active Directory Event 1644 LDAP filters can contain inconsistent whitespace after OID-to-bitwise transformation, and shows how regex-tolerant Sigma rules and testing with real logs can improve detection.
Key points
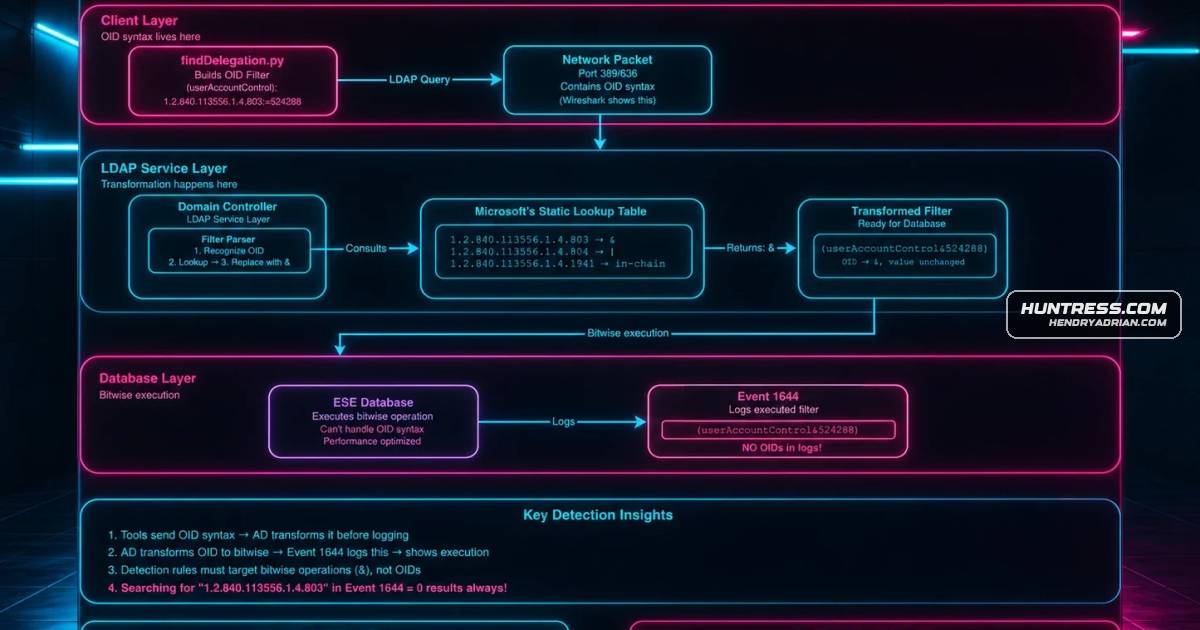
- The author says Active Directory transforms LDAP OID syntax into bitwise operations before recording filters in Event 1644, so rules should target the transformed form.
- Whitespace and capitalization can vary in logged filters, causing exact-string rules to miss activity.
- Regex patterns that allow whitespace around operators and parentheses can make detections more robust.
- The article recommends testing against real Event 1644 logs and a collection of observed formatting variations, rather than relying only on lab data.
- It advises including relevant attribute and operator context to avoid overly broad matches, and pre-filtering before regex to reduce SIEM workload.
Article Details
- Defense Focus
- Improve detection of LDAP queries by accounting for whitespace, parentheses, and case variations introduced when Active Directory transforms OID filters before logging Event 1644.
- Detection Methods
- Use whitespace-tolerant regular expressions against the Event 1644 LDAPFilter field, matching the attribute name, bitwise operator, and relevant flag.
- Allow for spacing around parentheses and negation, and use case-insensitive matching where appropriate.
- For findDelegation.py-related detection, correlate Event 1644, requested attributes, delegation-related LDAP filter criteria, userAccountControl bits, and a source IP:port pattern.
- Use a string prefilter for userAccountControl before applying more expensive regular expressions.
- Test detection patterns against varied, real Event 1644 data rather than relying only on lab-generated logs.
- Data Sources
- Windows Event 1644, including LDAPFilter, AttributesRequested, and Source fields
- Rule Types
- Sigma detection rules
- Regular-expression matching
- String-match prefiltering
- Platforms
- Active Directory
- SIEM
- Defensive Actions
- Collect representative Event 1644 logs from real environments and test rules against observed formatting variations.
- Include whitespace tolerance around LDAP attributes, bitwise operators, parentheses, and negation; account for case variations.
- Avoid matching only OID syntax in Event 1644 because the article says it is transformed to bitwise operations before logging.
- Avoid overly broad patterns that match only a numeric flag; include the relevant attribute and operator.
- Enable detailed logging to review what rules match and miss, and monitor detection performance after deployment.
Products
Tools
findDelegation.pyWhere we finally celebrated understanding that findDelegation.py searches for userAccountControl&524288?GetUserSPNs.pyGetUserSPNs.py uses userAccountControl&2 (in the !(userAccountControl&2) exclusion filter)ImpacketThat deep-dive post where we spent all that time figuring out that Impacket tools use bitwise operations instead of OID values?