AI-Driven Phishing Uses Deepfakes, Voice Cloning and Personal Data
Summary
The article warns that threat actors use AI-generated phishing, deepfake video, cloned voices and personal data to make scams more convincing, and recommends verification steps and stronger privacy and account protections.
Key points
- AI can generate polished phishing messages, fake profiles and voice messages, making grammar errors less reliable as a warning sign.
- The article describes deepfake video calls that impersonate executives to request urgent wire transfers.
- It says attackers may clone a person's voice from as little as 30 seconds of audio; the company reports a 40% uptick in urgent-voicemail scams impersonating executives.
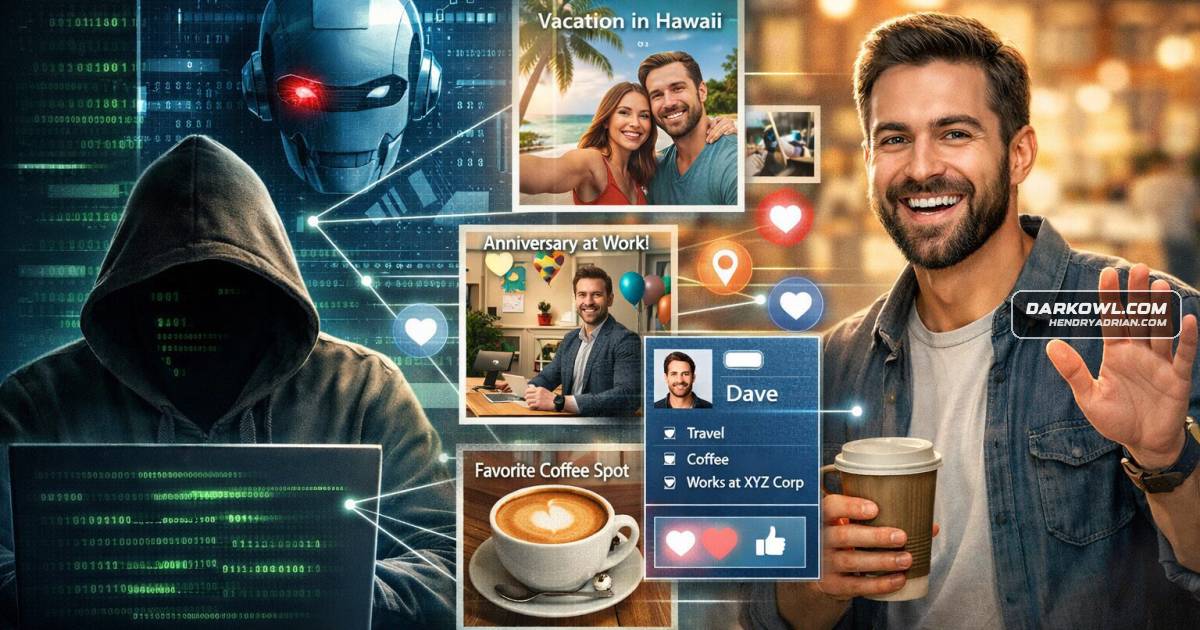
- Personal details gathered online can be used to tailor social-engineering messages, potentially leading victims to install infostealers.
- For unusual requests, verify through a known, trusted phone number; teams can also establish offline challenge-response phrases for high-stakes transactions.
- The article recommends limiting exposed personal information, enabling multi-factor authentication, using unique passwords and verifying before clicking.
Article Details
- Defense Focus
- Reduce susceptibility to AI-assisted phishing, deepfake impersonation, voice-cloning scams, and personalized social engineering.
- Detection Methods
- Watch for unnatural blinking, visual glitches around the neck, or delays between a speaker's mouth movements and audio in video calls.
- Treat urgent or unusual requests made by voice or video with skepticism, even when the speaker appears or sounds familiar.
- Verify unexpected messages and links, including personalized messages that refer to public posts or recent events.
- Defensive Actions
- Establish an offline challenge-response phrase for high-stakes financial transactions.
- For unusual requests received by voice or video, end the call and call back using a known, trusted number.
- Tighten online privacy settings and limit publicly available personal information.
- Enable multi-factor authentication and use strong, unique passwords.
- Verify links before clicking and remain alert to suspicious requests.
MITRE ATT&CK
T1204.001 · Malicious LinkIn the article's illustrative scenario, clicking a link in a personalized message results in installation of an infostealer.T1566.002 · Spearphishing LinkAn illustrative LinkedIn message impersonates a conference attendee and offers a link that leads to installation of an infostealer.T1566.004 · Spearphishing VoiceThe article describes voice-phishing scams using cloned voices in voicemails to impersonate executives and request password resets.T1656 · ImpersonationThe article describes threat actors impersonating executives or other familiar people using deepfake video and cloned voices.