cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

624 articles

Detection & Defense · huntress.com

How to Spot Living-off-the-Land Abuse in Normal Admin Activity

Attackers use legitimate tools such as PowerShell, WMI, and RMM software to blend in. Assess the user, system, process chain, command, and follow-on activity; improve logging and restrict access to high-risk tools.
Jul 8, 2026
Detection & Defense · toxsec.com

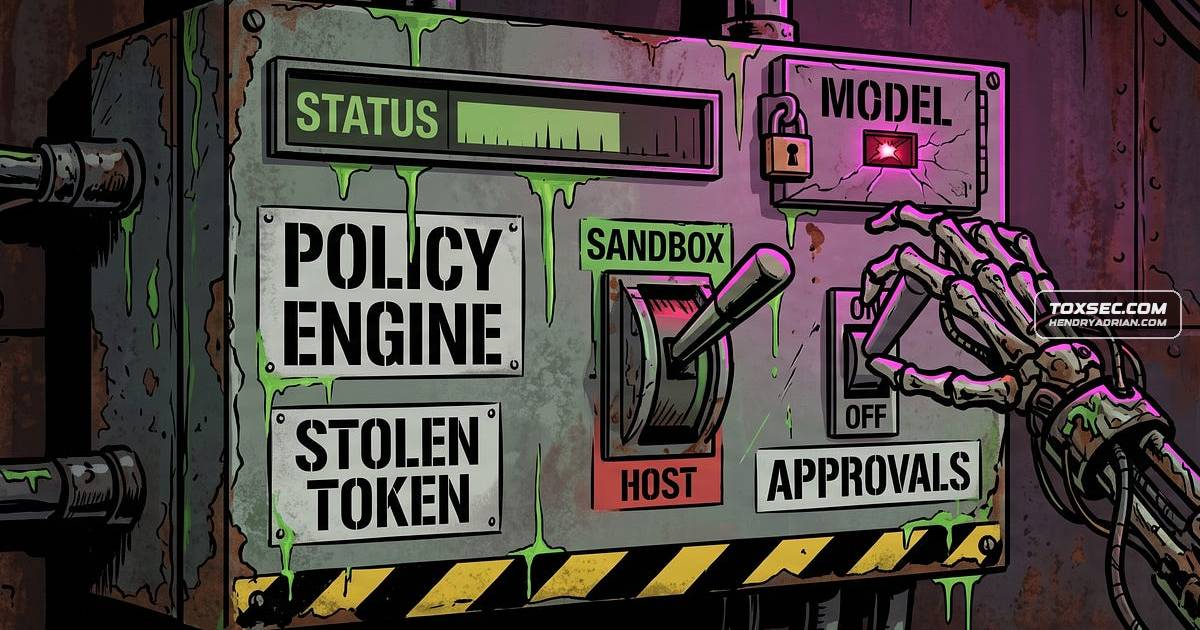
OpenClaw Flaw Shows How Attackers Can Bypass AI-Agent Build-Time Policies

Using OpenClaw’s CVE-2026-25253 as a case study, the article explains how stolen gateway credentials could alter live agent policies and recommends runtime monitoring, stronger gateway authentication, origin checks, and least privilege.

Jul 7, 2026
Detection & Defense · thehackernews.com

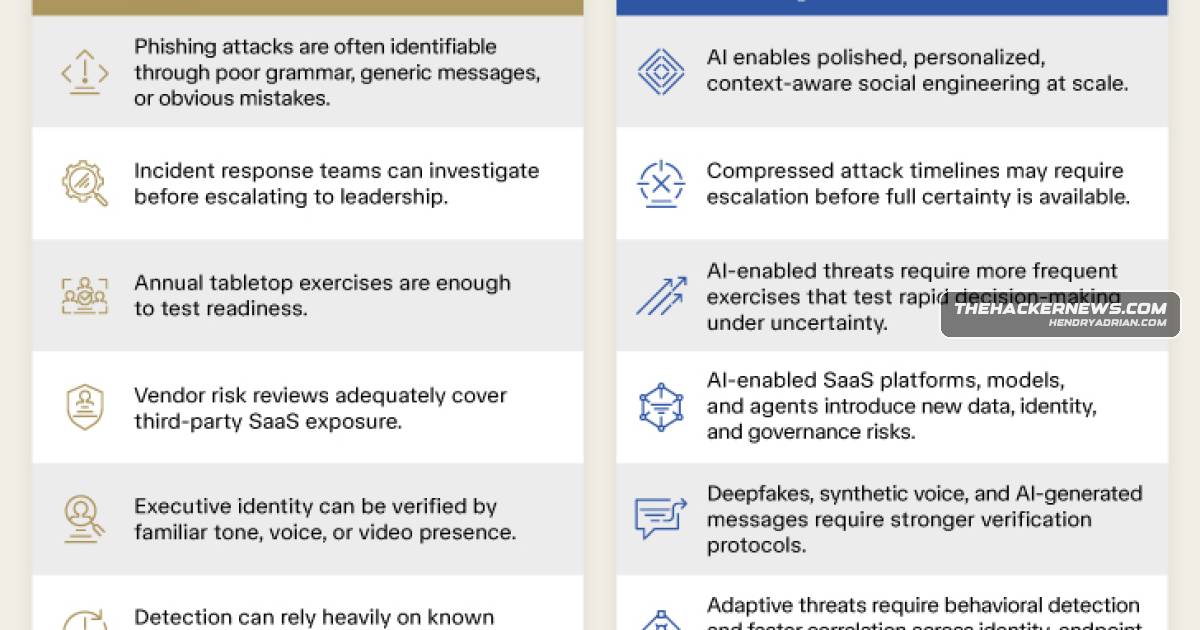
AI-Speed Attacks Push Organizations to Rethink Incident Response

AI can accelerate social engineering, reconnaissance, and malware adaptation, compressing response time. The article recommends stronger identity checks, behavioral detection, AI governance, and exercises that test decisions under uncertainty.

Jul 6, 2026
Detection & Defense · securitylabs.datadoghq.com

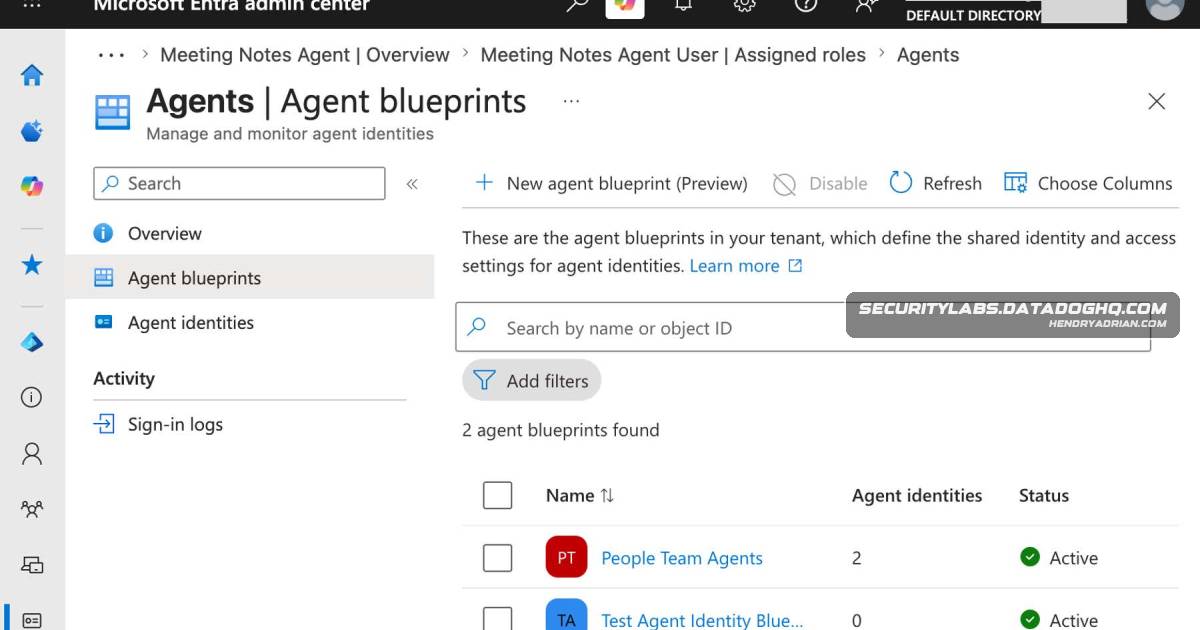
How to Protect, Monitor, and Respond to Entra Agent Identity Risks

Datadog Security Labs recommends restricting Entra agent-management permissions, avoiding blueprint secrets, reviewing third-party agents, monitoring credential changes, and preparing to disable or delete compromised agents.

Jul 6, 2026
Detection & Defense · security.com

Behavioral Monitoring Can Detect BYOVD Attacks That Evade Driver Blocklists

A Symantec whitepaper explains how BYOVD lets attackers use signed but vulnerable Windows drivers to disable AV/EDR, argues kernel hardening and blocklists have limits, and recommends behavioral monitoring of driver interactions and anomalous IOCTLs.

Jul 1, 2026
Detection & Defense · huntress.com

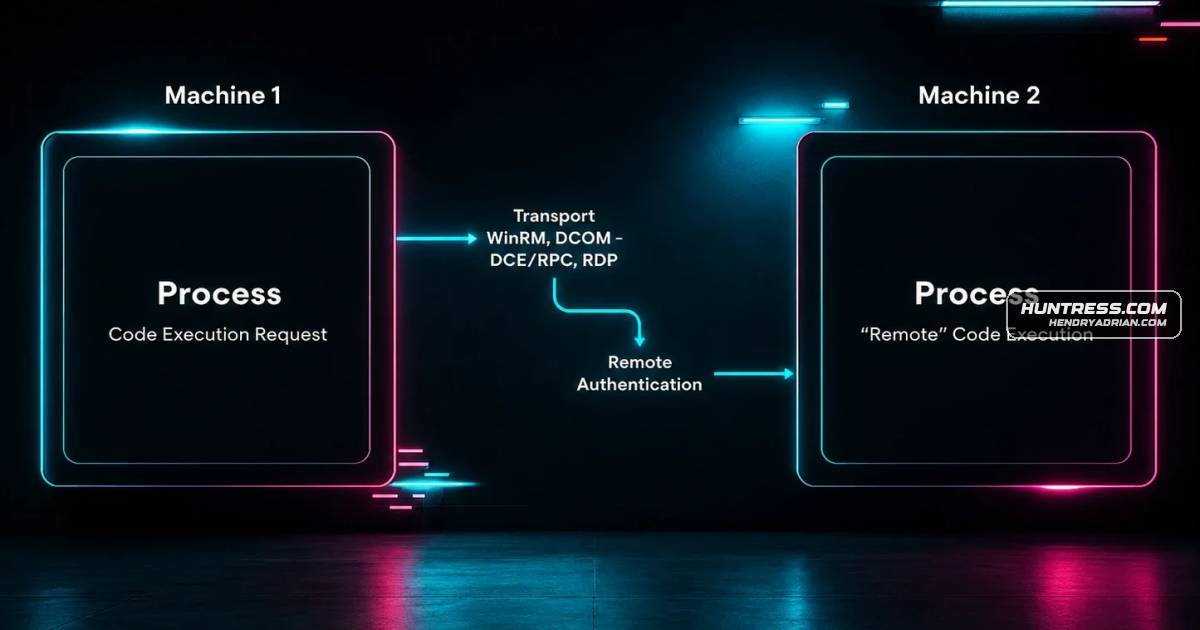
Huntress Details Its Approach to Detecting Lateral Movement

Huntress describes correlating remote authentication and process execution to detect lateral movement, with examples involving DCOM, RDP, credential dumping, and ransomware precursors. It also recommends least privilege, MFA, segmentation, and protocol hardening.

Jul 1, 2026
Detection & Defense · bleepingcomputer.com

Underground BEC Discussions Reveal AI Tactics, Call-Center Pressure and Cash-Out Challenges

Flare’s analysis of underground BEC discussions describes targeting finance and SaaS accounts, AI-generated correspondence, and call-center pressure. It recommends targeted training, exposure monitoring, MFA, password resets, and session revocation.

Jun 30, 2026
Detection & Defense · abstract.security

How to Detect Compromised GitHub Actions Through CI Runner Telemetry

The article uses the Trivy GitHub Actions compromise to explain how Tetragon telemetry can reveal CI runner attacks, and provides detection ideas and hardening measures for credential theft, persistence and exfiltration.

Jun 30, 2026
Detection & Defense · wazuh.com

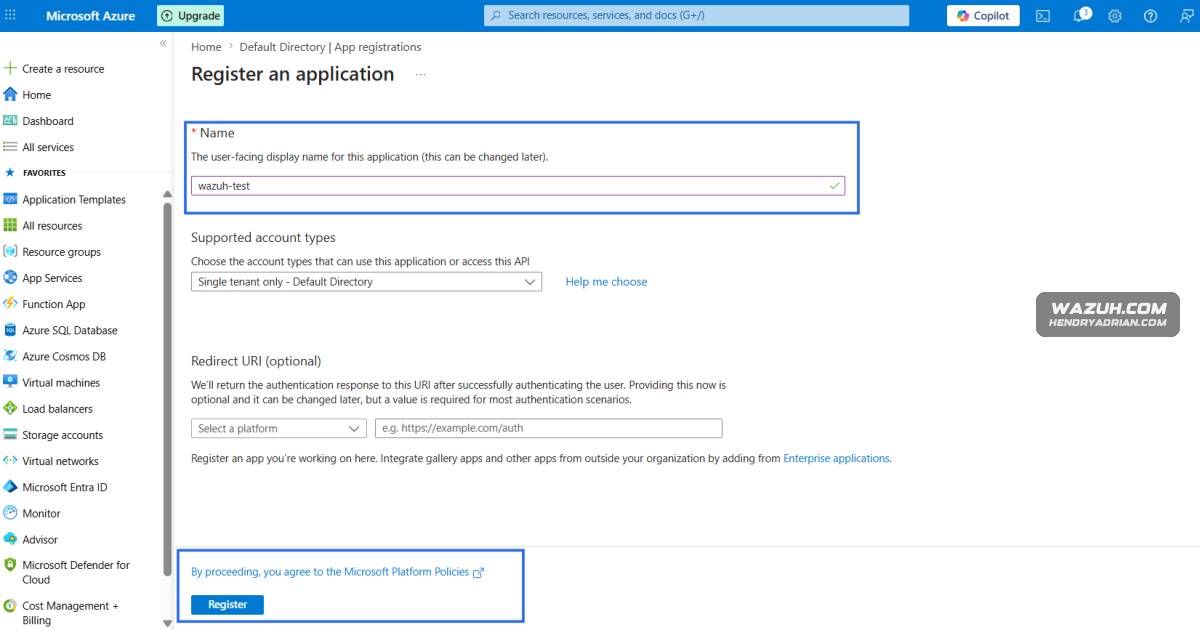
How to Detect Azure and Entra ID Attack Techniques with Wazuh

A Wazuh walkthrough configures Azure Activity, Entra ID and Storage logs through Log Analytics, then uses Stratus Red Team to emulate eight cloud attack scenarios and validate custom rules for persistence, privilege escalation, exfiltration and resource-lock deletion.

Jun 29, 2026
Detection & Defense · esentire.com

After Klue Incident, eSentire Recommends Auditing and Hardening Connected Integrations

After a threat actor used a compromised legacy credential to steal OAuth tokens and access Klue customers’ connected-platform data, eSentire recommends revoking tokens, auditing access, and hardening integrations.

Jun 26, 2026
Detection & Defense · thehackernews.com

Richard Bejtlich’s NDR Guide Advocates Evidence-Led Hunting and Network Interdiction

Richard Bejtlich’s NDR guide recommends using network evidence to test threat-hunting hypotheses, disrupt malicious activity before attackers reach their goals, and apply AI with human verification.

Jun 25, 2026
Detection & Defense · bleepingcomputer.com

Four Monitoring Layers Can Help Detect Account-Takeover Fraud

A sponsored article outlines transaction-, account-, platform-, and network-level monitoring for detecting account takeover and multi-account fraud, with indicators including contact changes, devices, geolocation, and transfer patterns.

Jun 25, 2026
Detection & Defense · bleepingcomputer.com

How Attackers Exploit Service Desks—and How Organizations Can Defend Them

A sponsored explainer describes how social engineers impersonate employees to obtain credential resets or MFA changes, citing reported incidents and recommending stronger identity checks, monitoring, and limits on service desk privileges.

Jun 24, 2026
Detection & Defense · huntress.com

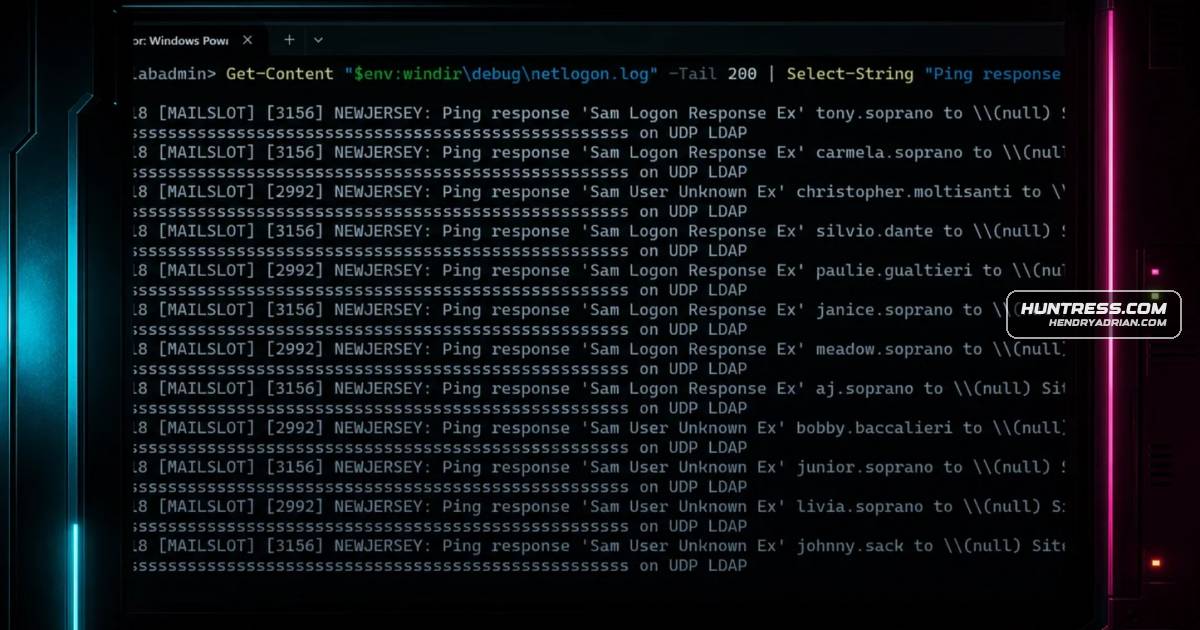
Detecting Active Directory LDAP Ping: Correlating Netlogon Logs and Event 5156

LDAP Ping bypasses Event 1644. For TCP-based ldapnomnom, netlogon.log records probed usernames and Event 5156 provides source IPs; true UDP cLDAP lacks Event 5156 attribution, requiring network-layer monitoring or MDI.

Jun 24, 2026
Detection & Defense · wiz.io

Wiz Outlines Real-Time Detection and Containment for AI-Era Threats

Wiz describes using cross-layer telemetry, AI-assisted threat investigation, and automated or human-approved response workflows to help security teams detect and contain AI-era threats faster.

Jun 23, 2026
Detection & Defense · thehackernews.com

How Defenders Can Disrupt AI-Driven Social Engineering Campaigns

The article describes a five-stage social engineering attack chain and recommends cross-channel visibility, instrumented honeypots, and API-driven takedowns to disrupt campaigns beyond blocking individual lures.

Jun 23, 2026
Detection & Defense · bleepingcomputer.com

TTP-Chain Validation Offers a Way to Assess Exploitability Without Live Exploits

Picus-sponsored article describes mapping a CVE to its required attacker techniques and testing those steps against deployed controls to assess exploitability when no safe exploit exists or live testing is too risky.

Jun 23, 2026
Detection & Defense · securitylabs.datadoghq.com

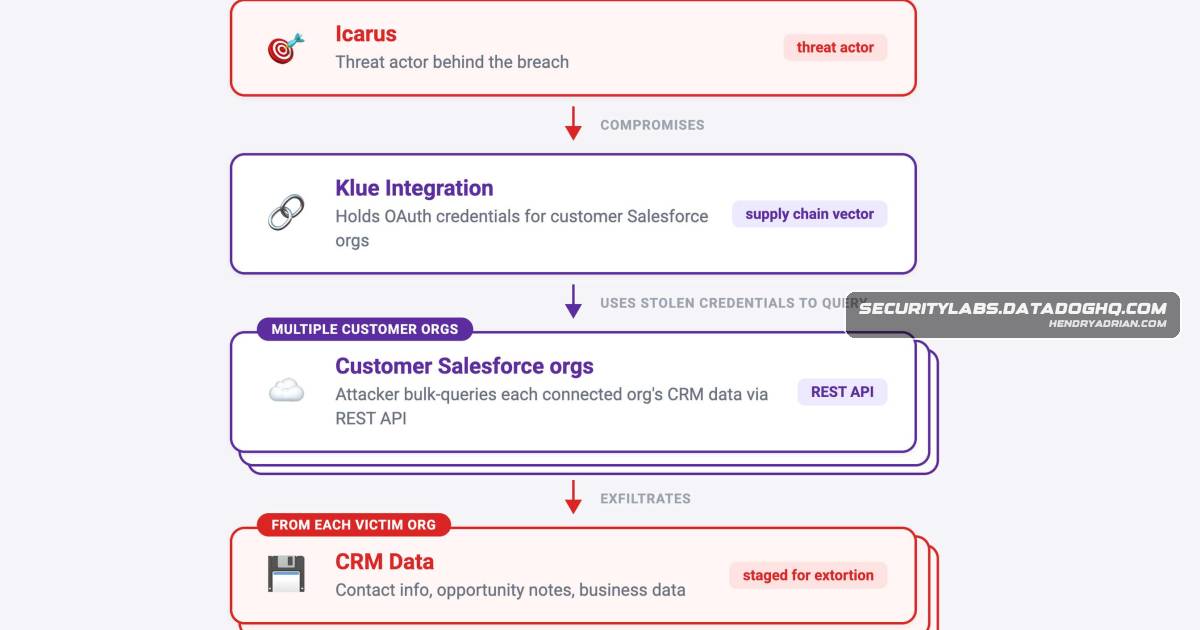
How to Detect Klue Supply-Chain Attack Activity in Salesforce

Attackers used a dormant Klue credential to steal OAuth tokens and query connected Salesforce environments. Datadog shares log indicators, API activity patterns, and SIEM rules to help identify related data exfiltration.

Jun 22, 2026
Detection & Defense · elastic.co

Elastic Adds Azure AD Graph Activity Log Ingestion and Detection Guidance

Elastic's Azure integration now ingests Azure AD Graph Activity Logs, enabling defenders to hunt enumeration using user-agent, API-version, client/user, ASN and 4xx patterns. The article also provides setup steps, detection rules and mitigations.

Jun 20, 2026
Detection & Defense · bleepingcomputer.com

Every AI Agent Is an Identity, but Most Organizations Don’t Treat Them That Way

A sponsored article argues that organizations should govern AI agents as identities by inventorying their access, limiting permissions to their intended purpose, and continuously monitoring their behavior and integrations.

Jun 19, 2026
Detection & Defense · cisecurity.org

CIS Releases and Updates Benchmarks for Cloud, Operating Systems, Kubernetes and More

CIS announced new and updated security benchmarks and build kits covering platforms including Google Cloud, Microsoft 365, Linux, Kubernetes, and Amazon EKS, with changes ranging from new recommendations to audit and remediation enhancements.

Jun 18, 2026
Detection & Defense · thehackernews.com

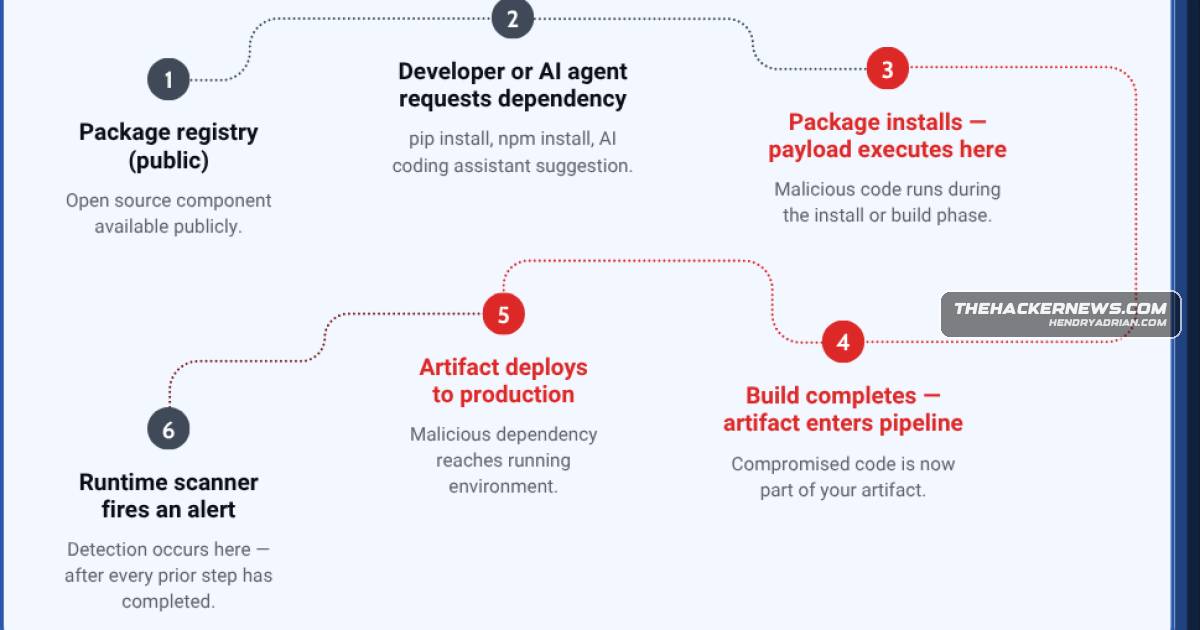
Why Runtime Scanning Can Miss Supply Chain Threats Before They Execute

The article argues runtime scanners may detect malicious dependencies only after execution. It recommends governing package ingestion with an approved internal catalog, proxy enforcement, source builds and provenance checks, citing the xz Utils backdoor as an example.

Jun 16, 2026
Detection & Defense · securitylabs.datadoghq.com

Datadog Shares Threat-Hunting Queries for Detecting Suspicious Salesforce Activity

Datadog provides Salesforce log queries and guidance to help security teams hunt for suspicious access, weak-MFA login attempts, OAuth token misuse, and API reconnaissance that may precede data exfiltration.

Jun 16, 2026
Detection & Defense · reversinglabs.com

YARA Rules and Patching Guidance Target ITScape KVM/arm64 Flaw

ITScape (CVE-2026-46316) is a KVM/arm64 vGIC-ITS race-condition flaw that can enable guest-to-host kernel execution; ReversingLabs details two YARA detections and advises patching affected kernels.

Jun 12, 2026
PreviousPage 15 of 26 Next
© 2026 cyber.hendryadrian.com