Huntress traces web intrusion using Nezha and Ghost RAT across 100+ potential victims
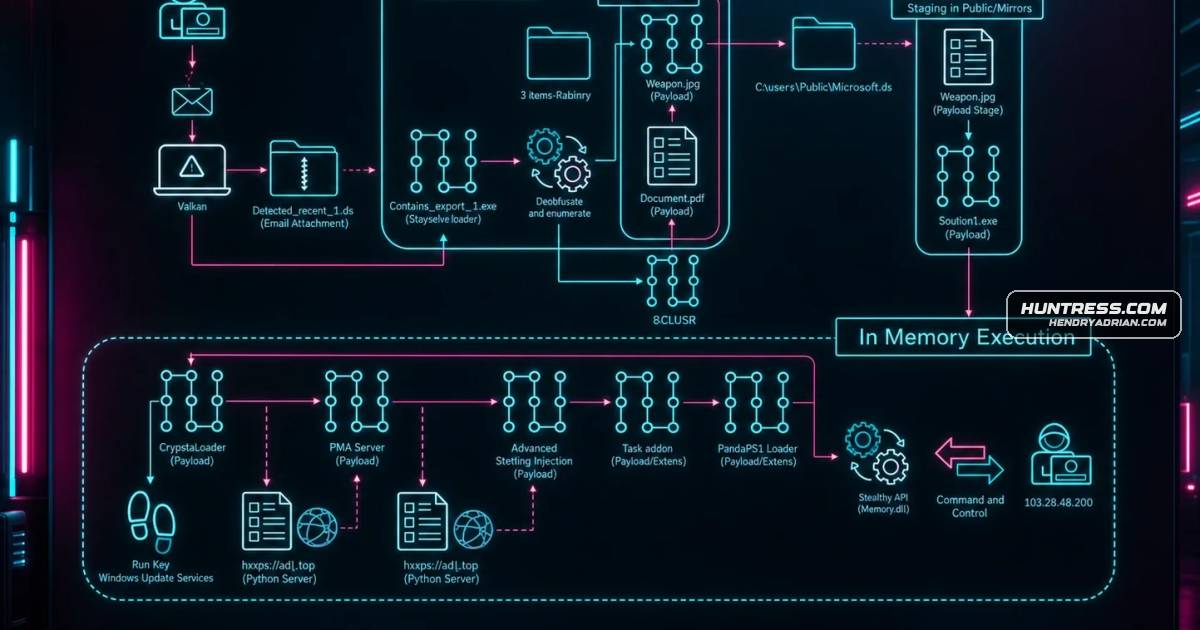
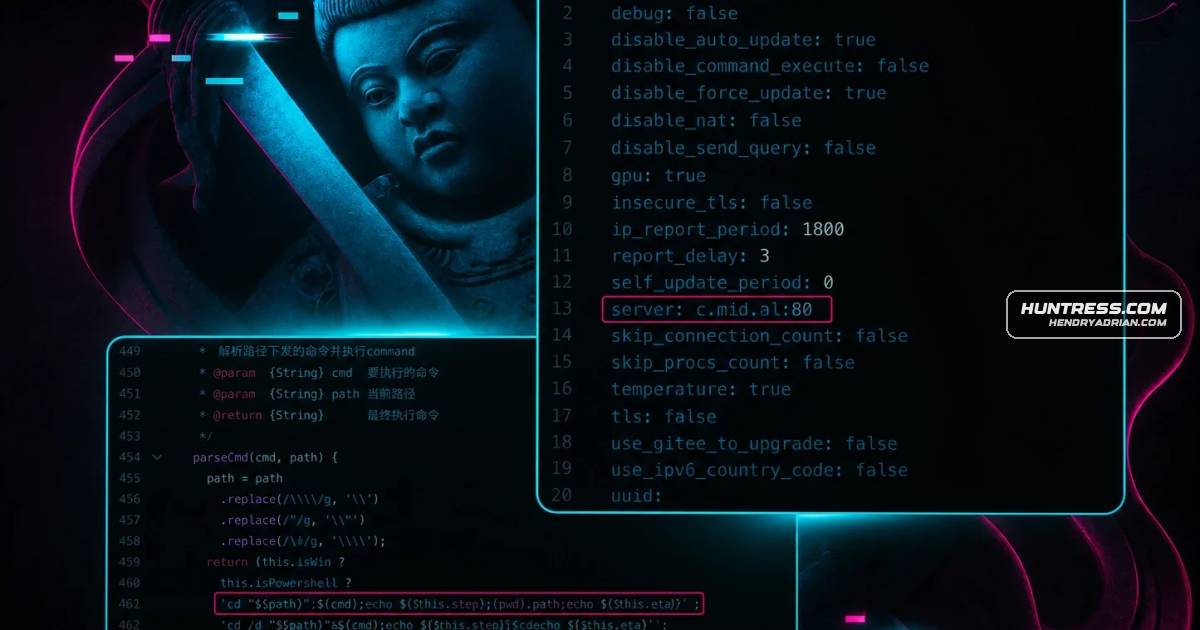
Huntress traced an August 2025 intrusion using exposed phpMyAdmin, MariaDB log poisoning, a web shell, Nezha and Ghost RAT across 100+ potential victims. A China-nexus attribution was later questioned by an unverified tip.