Huntress Recommends Practical Alternatives to Common Cybersecurity Advice
Summary
Huntress argues that vague security advice is ineffective and recommends practical measures such as password managers, independent verification of unexpected messages, automatic updates, stronger MFA, and technical controls that reduce reliance on user vigilance.
Key points
- The article says advice such as “be careful online” or “don’t click suspicious links” is too vague to reliably change behavior.
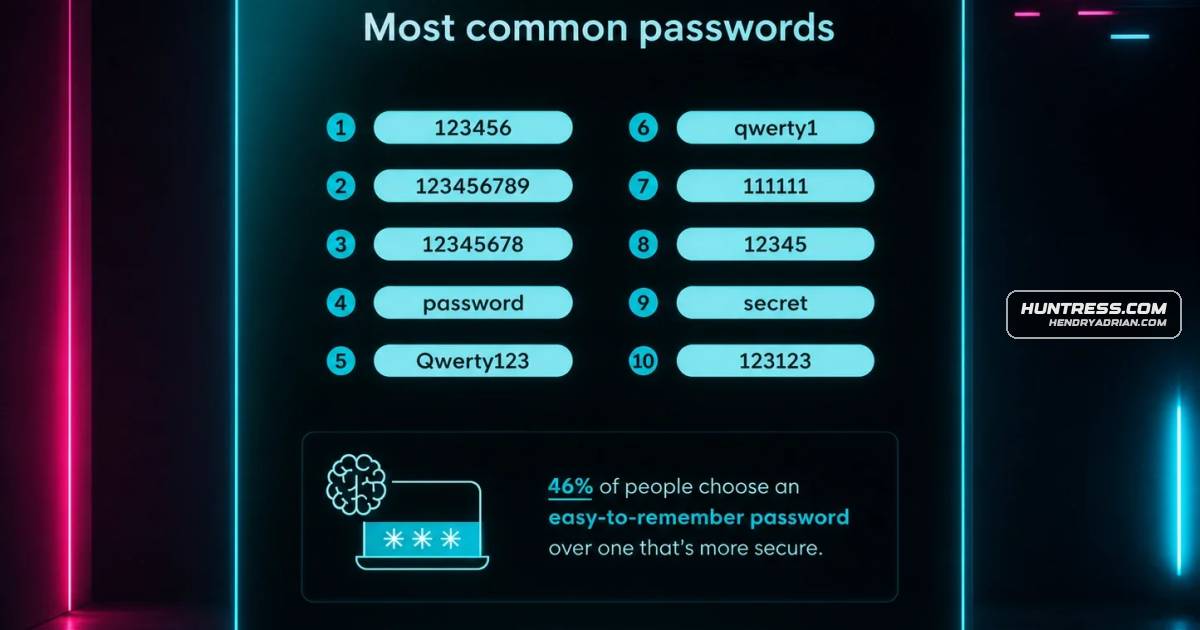
- It recommends password managers for generating and storing unique passwords, and advises against forced periodic password changes unless compromise is suspected.
- For unexpected links or attachments, it advises verifying through an independent channel and reporting suspected phishing.
- It recommends automatic software updates and centralized patch management for organizations.
- It says app-based authenticators or hardware security keys offer stronger MFA options than SMS codes.
- It argues organizations should support user awareness with technical controls, including endpoint protection and identity monitoring.
Article Details
- Topic
- Practical cybersecurity guidance, emphasizing effective security controls over vague or outdated advice.
Vendors
Products
AuthyTurn it up a notch: Recommend app-based authenticators like Authy, Google Authenticator, or Microsoft Authenticator as the baseline. For high-value accounts, suggest hardware tokens like YubiKeys.Google AuthenticatorTurn it up a notch: Recommend app-based authenticators like Authy, Google Authenticator, or Microsoft Authenticator as the baseline. For high-value accounts, suggest hardware tokens like YubiKeys.Managed Microsoft DefenderHere’s another approach: Combine Managed Endpoint Detection and Response (EDR) capabilities with Managed Microsoft Defender to sniff out shady attackers roaming around your systems and networks.Microsoft AuthenticatorTurn it up a notch: Recommend app-based authenticators like Authy, Google Authenticator, or Microsoft Authenticator as the baseline. For high-value accounts, suggest hardware tokens like YubiKeys.YubiKeysTurn it up a notch: Recommend app-based authenticators like Authy, Google Authenticator, or Microsoft Authenticator as the baseline. For high-value accounts, suggest hardware tokens like YubiKeys.