ClickFix Variants, Deepfake Scams and ViewState Attacks Feature in 2025 Threat Trends
Summary
Huntress reviews 2025 threat trends, including cross-platform ClickFix lures, deepfake-enabled social engineering and attacks exploiting exposed ASP.NET machine keys for ViewState code injection.
Key points
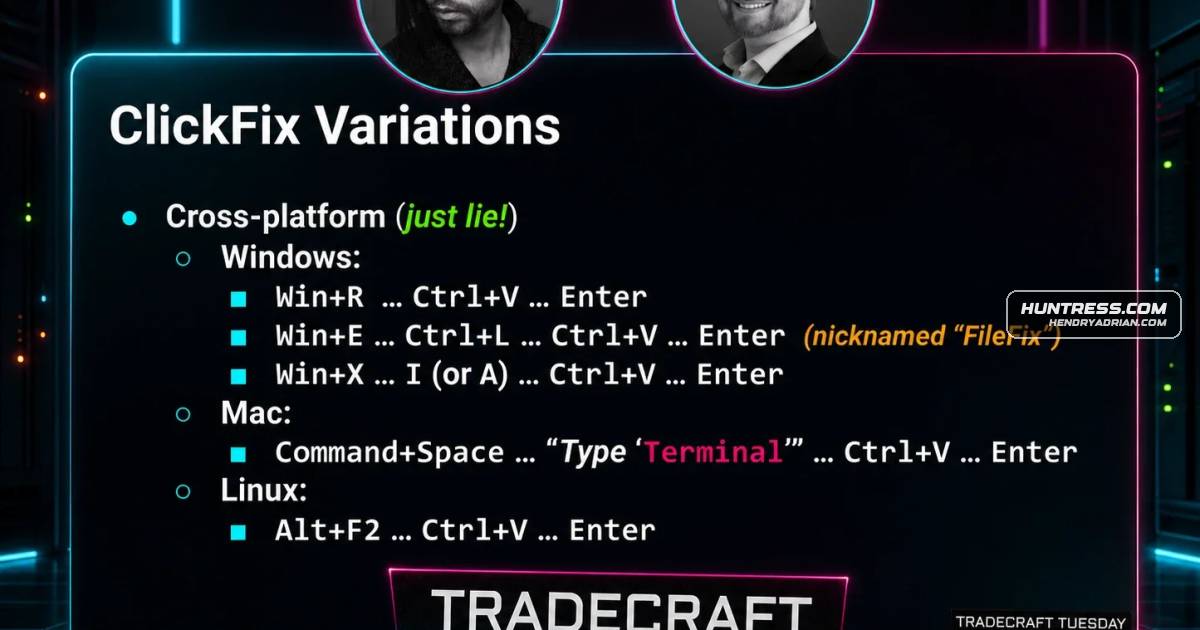
- ClickFix lures victims into pasting attacker-supplied commands; variants target macOS and Linux, while FileFix uses Windows File Explorer.
- A reported fake AnyDesk installer attack used a Cloudflare Turnstile lure and an MSI disguised as a PDF to deliver MetaStealer, an infostealer that harvests credentials and files.
- Huntress recommends restricting Windows shortcuts and clipboard use to help mitigate ClickFix attacks.
- Deepfake video in a Zoom meeting reportedly persuaded an employee at a Web3 organization to download a malicious extension; the article also describes deepfakes used in fraud and job-related infiltration.
- The article recommends preparing for deepfake impersonation with response plans, physical validation and strict account-reset controls.
- Microsoft identified more than 3,000 publicly disclosed ASP.NET machine keys that could enable ViewState code injection if used on servers.
- The article cites ViewState attacks involving hardcoded keys in Gladinet CentreStack and Triofox, and a zero-day affecting Sitecore deployments (CVE-2025-53690).
Article Details
- Event Type
- Huntress reported 2025 cyber threat trends involving ClickFix-style social engineering, deepfake-enabled attacks, and exploitation of ASP.NET ViewState weaknesses.
- Impact
- Reported attacks have led to delivery of MetaStealer to steal credentials and files, employee compromise through deepfake impersonation, financial fraud, and arbitrary code execution through ViewState deserialization. The article cites a $25 million fraud loss at Arup and exploitation affecting Gladinet CentreStack/Triofox and Sitecore deployments.
CVE
CVE-2025-30406In April, threat actors targeted ViewState while exploiting critical flaws in the Gladinet CentreStack and Triofox flaw (CVE-2025-30406).CVE-2025-53690More recently, in September, Mandiant researchers revealed a ViewState deserialization zero day attack (CVE-2025-53690) that was impacting Sitecore deployments.
People
Malware
Vendors
GladinetIn April, threat actors targeted ViewState while exploiting critical flaws in the Gladinet CentreStack and Triofox flaw (CVE-2025-30406).Huntress– The Craftiest Trends, Scams, and Tradecraft of 2025 (So Far) – John Hammond and Greg Linares with Huntress dove into the top types of tricky tradecraft that threat actors are using to target businesses.MandiantMore recently, in September, Mandiant researchers revealed a ViewState deserialization zero day attack (CVE-2025-53690) that was impacting Sitecore deployments.MicrosoftTo understand ViewState, you need to first understand ASP.NET, which is a server-side web app framework that was made by Microsoft for building web pages, applications, and service.SitecoreMore recently, in September, Mandiant researchers revealed a ViewState deserialization zero day attack (CVE-2025-53690) that was impacting Sitecore deployments.
Products
AnyDeskThe attack started with a fake AnyDesk installer while searching for the AnyDesk remote tool.ASP.NETExposed ASP.NET machine keys that open the door for ViewState deserialization attacks against company servers.Gladinet CentreStackIn April, threat actors targeted ViewState while exploiting critical flaws in the Gladinet CentreStack and Triofox flaw (CVE-2025-30406).SitecoreMore recently, in September, Mandiant researchers revealed a ViewState deserialization zero day attack (CVE-2025-53690) that was impacting Sitecore deployments.ZoomHere, the threat actors tricked an employee at the company by inviting them to a Zoom meeting with video deepfakes of known senior leadership.