Five Microsoft 365 Identity Security Myths—and What Defenders Should Know
Summary
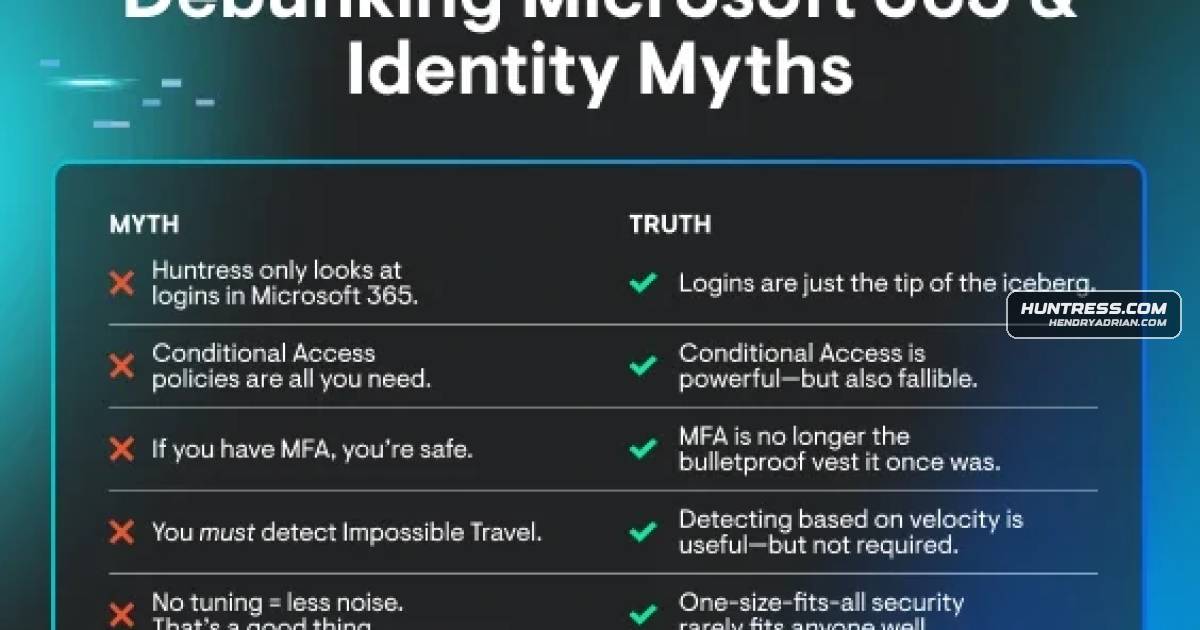
Huntress challenges five Microsoft 365 identity-security assumptions, arguing that defenders should look beyond logins, MFA and impossible-travel alerts, account for Conditional Access gaps, and tune detections to their environments.
Key points
- Huntress says identity monitoring should cover signals such as role changes, inbox rules, mailbox permissions and OAuth app consent—not only login events.
- The company reports that 24% of P1 and 9% of P2 license holders do not configure Conditional Access policies; it also warns that misconfigurations can leave gaps.
- Huntress says MFA does not prevent every account takeover: attackers may use adversary-in-the-middle phishing or steal session tokens to bypass challenges.
- The article argues that impossible-travel alerts alone can miss attackers using residential proxies or cloud hosts, and recommends considering other activity and context.
- Huntress advocates customizable detection rules and alert suppression to account for differences between environments and reduce false positives.
Article Details
- Topic
- Huntress Managed ITDR capabilities for detecting Microsoft 365 identity threats and addressing common security misconceptions
People
Vendors
HuntressHere at Huntress, we believe in clarity over cloudiness. So let’s bust some of the most common Microsoft 365 and identity security myths floating around out there. If you’ve heard statements like “logins are only 2% ofMicrosoftHomeBlogCloudy with a Chance of Misinformation: Debunking Microsoft 365 & Identity Myths
Products
Azure ADfrom the only signal Huntress Managed ITDR pays attention to. Our telemetry includes signals from Azure Active Directory and Microsoft Exchange, covering a range of events from group membership changes and roleConditional AccessMyth #2: “Conditional Access policies are all you need.”Huntress Managed ITDRYes, login events are important, but they’re far from the only signal Huntress Managed ITDR pays attention to. Our telemetry includes signals from Azure Active Directory and Microsoft Exchange, covering a range ofMicrosoft 365 Apps for EnterpriseHomeBlogCloudy with a Chance of Misinformation: Debunking Microsoft 365 & Identity MythsMicrosoft ExchangeManaged ITDR pays attention to. Our telemetry includes signals from Azure Active Directory and Microsoft Exchange, covering a range of events from group membership changes and role escalations to suspicious inboxMicrosoft OneDrivelike malicious inbox rules. But we’re not stopping there. We're actively expanding into SharePoint, OneDrive, and additional Microsoft event categories to make sure defenders have visibility across the entire killMicrosoft SharePointcontext, like malicious inbox rules. But we’re not stopping there. We're actively expanding into SharePoint, OneDrive, and additional Microsoft event categories to make sure defenders have visibility across the