cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2499 articles

Threat Research · cloudsek.com

Researchers Demonstrate Hidden Prompt Injection That Turns AI Summaries into ClickFix Lures

A proof of concept showed that CSS-hidden instructions repeated in HTML could steer tested AI summarizers to present ClickFix steps, including a benign test command. The article describes the technique, risks, limitations, and possible defenses.
Aug 25, 2025
Threat Research · wiz.io

AWS Bedrock API Keys Introduce Long-Lived Bearer Credentials, Wiz Finds

Wiz analyzes Bedrock’s long- and short-term API keys, their creation and logging, and risks from long-lived credentials. AWS says it added the keys to secrets scanning and quarantined previously exposed keys it found.

Aug 21, 2025
Threat Research · huntress.com

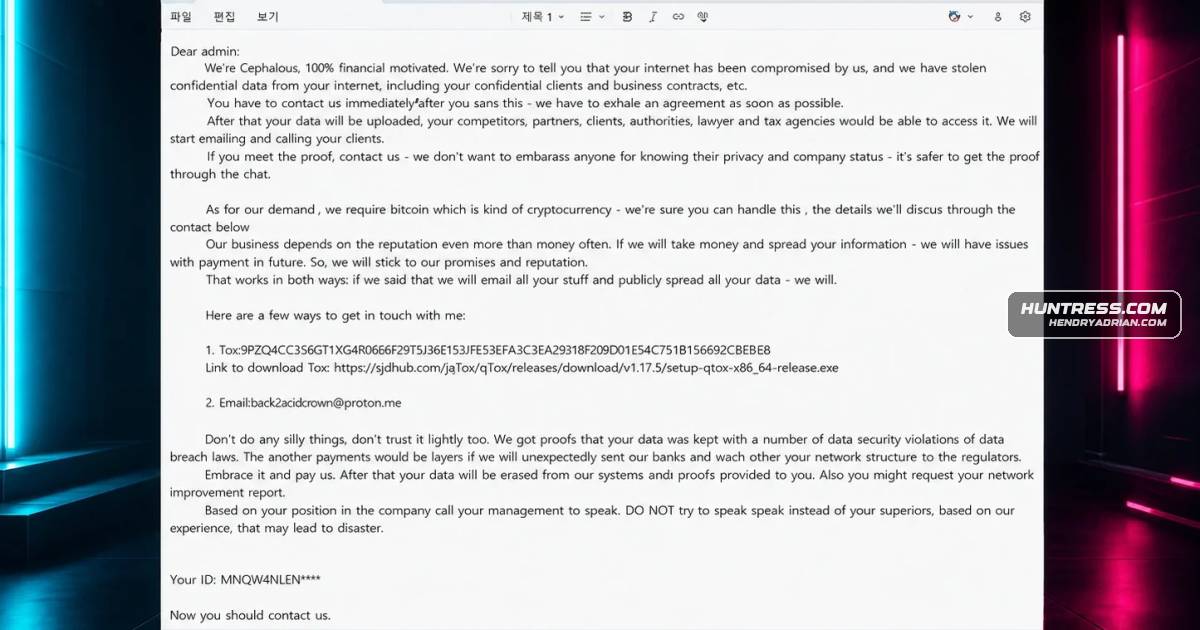
Cephalus Ransomware Used SentinelOne DLL Sideloading in Two Incidents

Huntress analyzed two Cephalus ransomware incidents involving RDP access through accounts without MFA, likely data exfiltration via MEGA, and DLL sideloading through a legitimate SentinelOne executable. One deployment was stopped by Microsoft Defender.

Aug 21, 2025
Threat Research · cloudsek.com

APT36 Campaign Uses Linux .desktop Files to Deliver Malware via Google Drive

CloudSek details an APT36-attributed campaign that disguises a malicious Linux .desktop file as a PDF, downloads a Go payload from Google Drive, and uses persistence, anti-analysis checks, and WebSocket C2.

Aug 21, 2025
Threat Research · cloudsek.com

TA-NATALSTATUS Turns Exposed Redis Servers Into Persistent Cryptojacking Infrastructure

CloudSEK details TA-NATALSTATUS’s use of exposed, unauthenticated Redis servers to install persistent cryptominers, evade detection, and scan for more victims. The report includes indicators, investigation steps, and remediation guidance.

Aug 21, 2025
Threat Research · darktrace.com

Darktrace Details SaaS Account Hijacks Using VPS Infrastructure

Darktrace describes suspicious SaaS activity across two customer environments, including rare VPS logins, inbox-rule manipulation, email deletion, and phishing-related behavior. The investigation suggests attackers used hijacked sessions to maintain access and conceal

Aug 21, 2025
Threat Research · blog.talosintelligence.com

Static Tundra Targets Unpatched Cisco Network Devices in Long-Running Espionage Campaign

Talos reports that Russian state-sponsored group Static Tundra exploits unpatched Cisco devices, including through CVE-2018-0171, to steal configurations and maintain long-term access. It recommends patching the flaw or disabling Smart Install.

Aug 20, 2025
Threat Research · deepinstinct.com

DBatLoader Uses Delphi, Obfuscation and Anti-Analysis Techniques to Evade Detection

A vendor analysis describes DBatLoader as a Delphi-compiled Windows malware sample with obfuscation, anti-analysis and import-hiding techniques, plus capabilities associated with persistence, surveillance and system manipulation.

Aug 20, 2025
Threat Research · hunt.io

MuddyWater-Linked Phishing Campaign Uses Fake Recruiter Lures to Install NetBird

Researchers detail a multi-stage phishing campaign targeting finance executives with fake recruiter and Google Drive lures. VBS payloads install NetBird and OpenSSH, create hidden administrator access, and enable RDP; infrastructure and tool overlaps suggest a MuddyW...

Aug 20, 2025
Threat Research · huntress.com

Huntress Details Data Exfiltration Tactics Used in Ransomware Incidents

Huntress analysts describe attackers staging and exfiltrating data with tools such as WinRAR, RClone, backup utilities and s5cmd, and explain detection challenges, including a Qilin incident involving exposed RDP and disabled Defender protections.

Aug 19, 2025
Threat Research · huntress.com

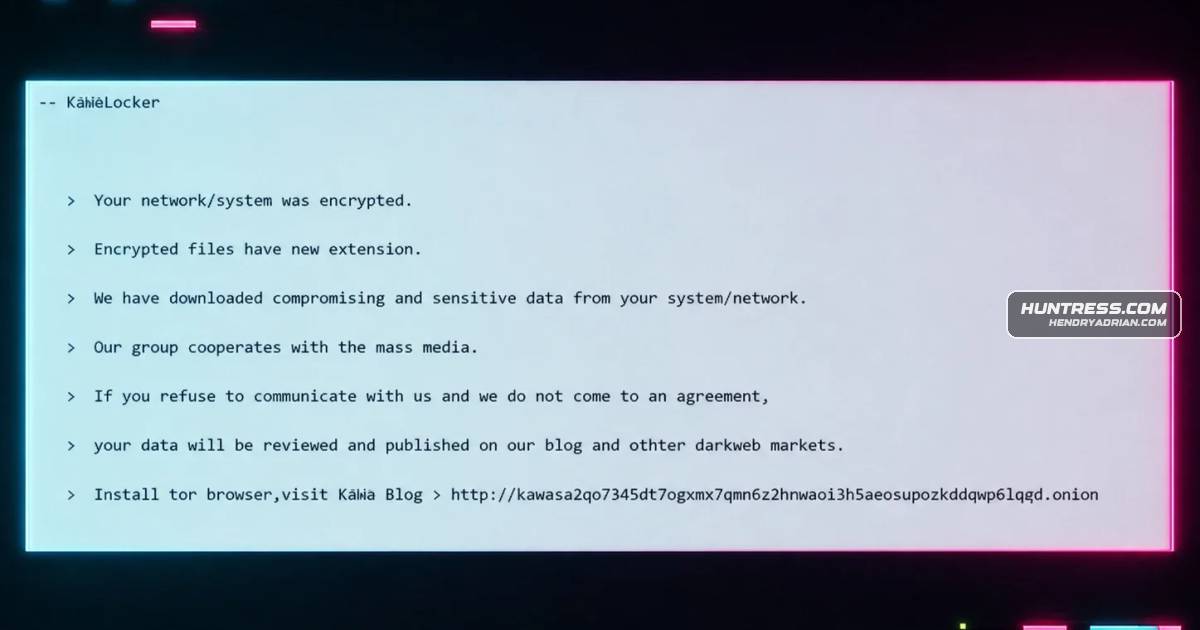
Huntress Details KawaLocker Ransomware Attack and Attempts to Disable Security Tools

Huntress traced a KawaLocker attack that began with RDP access using a compromised account. Attackers disabled security tools, attempted to enable RDP on other endpoints, and encrypted files; Huntress response prevented further access.

Aug 14, 2025
Threat Research · threatfabric.com

PhantomCard Android Trojan Relays Brazilian Users’ Bank Card Data Over NFC

ThreatFabric describes PhantomCard, an Android Trojan distributed through fake card-protection app pages in Brazil. It relays EMV card data and PINs to enable remote payment or ATM fraud, and is reportedly a customized NFU Pay malware-as-a-service product.

Aug 14, 2025
Threat Research · hunt.io

ERMAC 3.0 Source Leak Reveals Android Banking Trojan’s Capabilities and Infrastructure

Analysis of leaked ERMAC 3.0 source code details an Android banking trojan targeting more than 700 apps, its command-and-control infrastructure, data theft capabilities, and security weaknesses defenders can use to detect and disrupt it.

Aug 14, 2025
Threat Research · huntress.com

Huntress Reports SonicWall VPN Intrusions Linked to Akira Ransomware and Vulnerable-Driver Abuse

Huntress details SonicWall VPN intrusions involving credential theft, lateral movement, defense evasion and Akira ransomware. SonicWall says activity correlates with CVE-2024-40766, not a zero-day; Huntress also observed vulnerable-driver abuse.

Aug 13, 2025
Threat Research · darktrace.com

Ivanti EPMM Flaws Exploited to Deliver KrustyLoader Malware

Darktrace reports observing exploitation of Ivanti EPMM vulnerabilities CVE-2025-4427 and CVE-2025-4428 across customer environments, including OAST-based validation, AWS-hosted payloads, and KrustyLoader delivery.

Aug 8, 2025
Threat Research · hunt.io

Researchers Link Multilingual Asian Phishing Sites Through Shared Delivery Toolkit

Hunt.io researchers linked 28 Chinese-, English-, and Japanese-language phishing pages across three clusters, finding shared templates, scripts, hosting patterns, and ZIP/RAR lures themed around government, tax, and financial documents.

Aug 8, 2025
Threat Research · thedfirreport.com

Bing Search Poisoning Led to Bumblebee Infection and Akira Ransomware

A July 2025 SEO-poisoning campaign delivered Bumblebee through trojanized IT-tool installers, enabling attackers to steal credentials, exfiltrate data, and deploy Akira ransomware across enterprise domains.

Aug 5, 2025
Threat Research · wiz.io

Wiz Details Triton Inference Server Vulnerability Chain That Could Enable Remote Takeover

Wiz describes how flaws in Triton’s Python backend could let an unauthenticated remote attacker access internal shared memory and potentially take over a server. NVIDIA patched the issues in version 25.07.

Aug 4, 2025
Threat Research · huntress.com

Huntress Details Reused Ransomware Playbook That Disables Microsoft Defender

Huntress describes a ransomware intrusion using a modified script based on a 2021 playbook to disable Microsoft Defender and impair monitoring. Its SOC intervened before file encryption.

Jul 31, 2025
Threat Research · hunt.io

APT36 Uses Linux Desktop Lures and Poseidon Backdoor in Campaign Targeting India

Researchers detail APT36 infection chains using Linux .desktop files disguised as PDFs, cron-based persistence, Mythic-based Poseidon malware, and more than 100 phishing domains impersonating Indian government organizations.

Jul 31, 2025
Threat Research · wiz.io

Wiz Finds Base44 Authentication Flaw That Exposed Private Applications

Wiz says unauthenticated Base44 registration and OTP endpoints let attackers use public app IDs to bypass SSO and access private apps. Wix fixed the flaw within 24 hours; it reported no evidence of exploitation.

Jul 29, 2025
Threat Research · cloudsek.com

Deepfake Influencer Ads Drive Investment Fraud Across Social Media

CloudSEK investigated a scam using deepfake influencer videos and social-media ads to lure victims into Telegram investment schemes, where scammers withheld funds and demanded further payments. It identified over 120 ads across 20 Facebook accounts.

Jul 29, 2025
Threat Research · wiz.io

TraderTraitor’s Tradecraft: North Korean Crypto Theft Through Social Engineering and Supply-Chain Attacks

Wiz examines TraderTraitor, a North Korean-linked cluster attributed to major crypto thefts, and details its use of social engineering, trojanized software, supply-chain compromises and cloud access to steal digital assets.

Jul 28, 2025
Threat Research · cloudsek.com

ClickFix Campaign Uses ActiveX to Deliver Epsilon Red Ransomware

CloudSEK found a ClickFix campaign using fake verification pages and ActiveX to silently download and run Epsilon Red. Related lures impersonate Discord, streaming services, and dating sites.

Jul 25, 2025
PreviousPage 90 of 105 Next
© 2026 cyber.hendryadrian.com