cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2499 articles

Threat Research · huntress.com

Investigation Traces Phishing Campaign From Python Infostealer to PureRAT

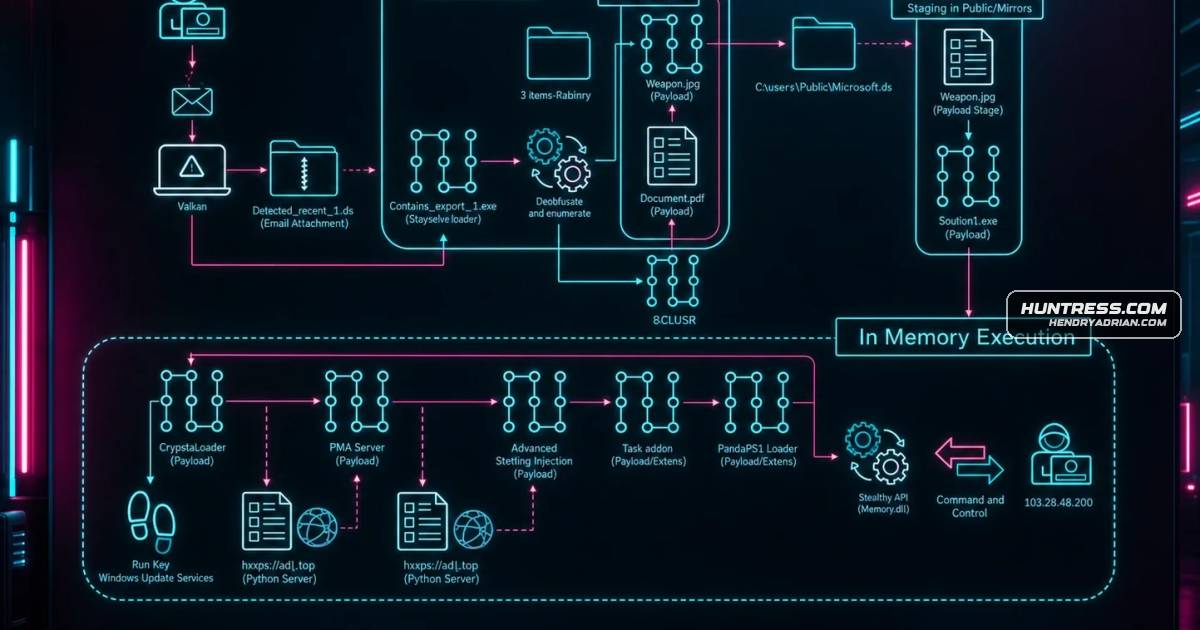
Huntress details a 10-stage phishing infection chain that progressed from Python loaders and an infostealer to PureRAT, explaining its persistence, evasion, host fingerprinting and encrypted C2. SOC remediation stopped deployment of additional plugins.
Sep 25, 2025
Threat Research · cloudsek.com

CloudSEK Finds Botnet Loader Service Distributing RondoDoX, Mirai and Morte Payloads

CloudSEK analyzed six months of exposed botnet logs showing attacks on routers, IoT devices and enterprise applications, including command injection, default-credential attempts and delivery of RondoDoX, Mirai and Morte payloads.

Sep 25, 2025
Threat Research · blog.sucuri.net

WordPress Backdoors Create Hidden Admin Accounts and Exfiltrate Credentials

An analysis of two malicious WordPress files found them creating and restoring a hidden administrator account, concealing the account and plugin, and sending credentials to an attacker-controlled server. The article lists indicators and cleanup steps.

Sep 24, 2025
Threat Research · blog.talosintelligence.com

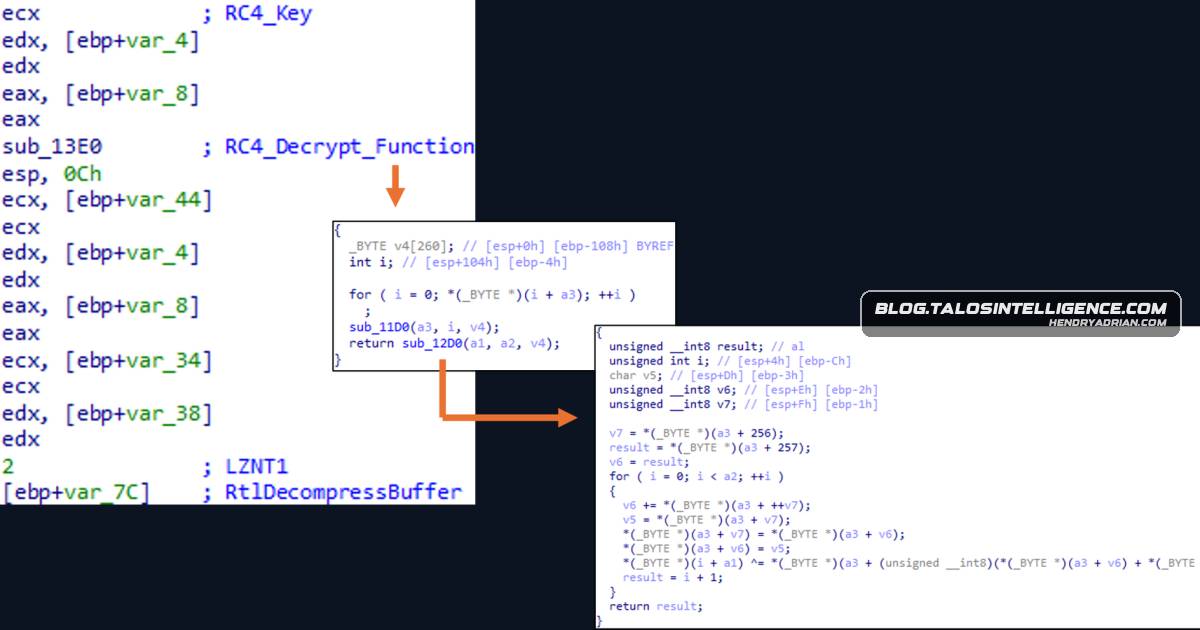
Talos Details DLL-Sideloading Campaign Using RainyDay, Turian and a New PlugX Variant

Talos analyzed a campaign active since 2022 targeting telecom and manufacturing organizations in Central and South Asia. Its new PlugX variant shares loader techniques and configuration traits with RainyDay and Turian; Talos assesses a Naikon link with medium confidence

Sep 23, 2025
Threat Research · darktrace.com

ShadowV2 Botnet Targets Exposed Docker Daemons and Offers DDoS-for-Hire Capabilities

Darktrace analyzes ShadowV2, a campaign using a Python spreader and Go-based RAT to infect exposed Docker daemons, control compromised systems through an API, and launch HTTP flood and HTTP/2 rapid reset attacks.

Sep 23, 2025
Threat Research · wiz.io

Anomalous IMDS Access Uncovers Exploited Pandoc and ClickHouse SSRF Paths

Wiz researchers describe hunting for anomalous cloud metadata access that uncovered exploitation of a Pandoc zero-day (CVE-2025-51591) and SSRF abuse in ClickHouse. IMDSv2 and limited instance privileges reduced impact.

Sep 22, 2025
Threat Research · feeds.feedblitz.com

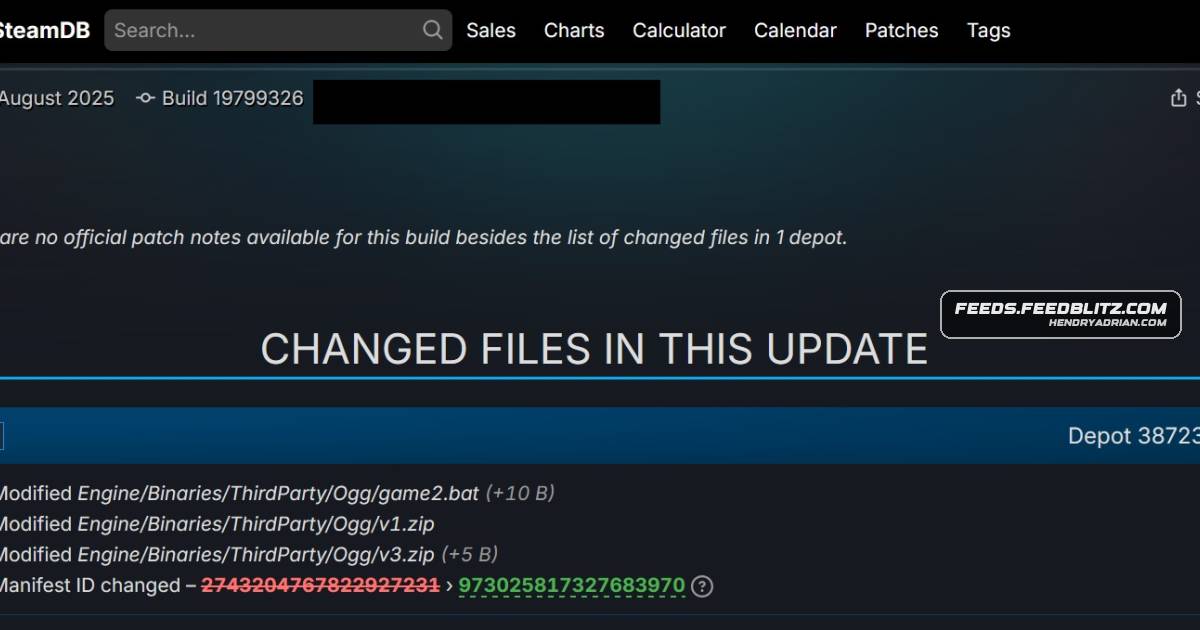
Malicious BlockBlasters Steam Patch Delivered StealC and a Backdoor

A malicious August 30 BlockBlasters patch used scripts to steal Steam, browser, and crypto-wallet data and install StealC and a backdoor. The game was removed from Steam after more than 100 downloads were reported.

Sep 22, 2025
Threat Research · hunt.io

AsyncRAT Campaign Uses Trojanized ScreenConnect Installers and Open Directories

Hunt.io researchers traced AsyncRAT and a custom PowerShell RAT delivery campaign through trojanized ScreenConnect installers, open directories, ClickOnce redirects, and adaptable loaders with scheduled-task persistence and rotating C2 infrastructure.

Sep 18, 2025
Threat Research · wiz.io

Shai-Hulud npm Worm Steals Secrets and Spreads by Publishing Malicious Packages

Wiz details how malicious npm packages stole secrets and used npm tokens to spread. Researchers found exposed credentials and publicized private repositories, and recommend removing affected versions, auditing GitHub, and rotating secrets.

Sep 16, 2025
Threat Research · darktrace.com

SEO-Poisoned Fake PuTTY Downloads Deliver Oyster Backdoor

Darktrace analyzed a campaign that used fake PuTTY download sites promoted through search results to deliver the Oyster backdoor, observing persistence, command-and-control traffic, possible data exfiltration, and unusual RDP activity.

Sep 11, 2025
Threat Research · huntress.com

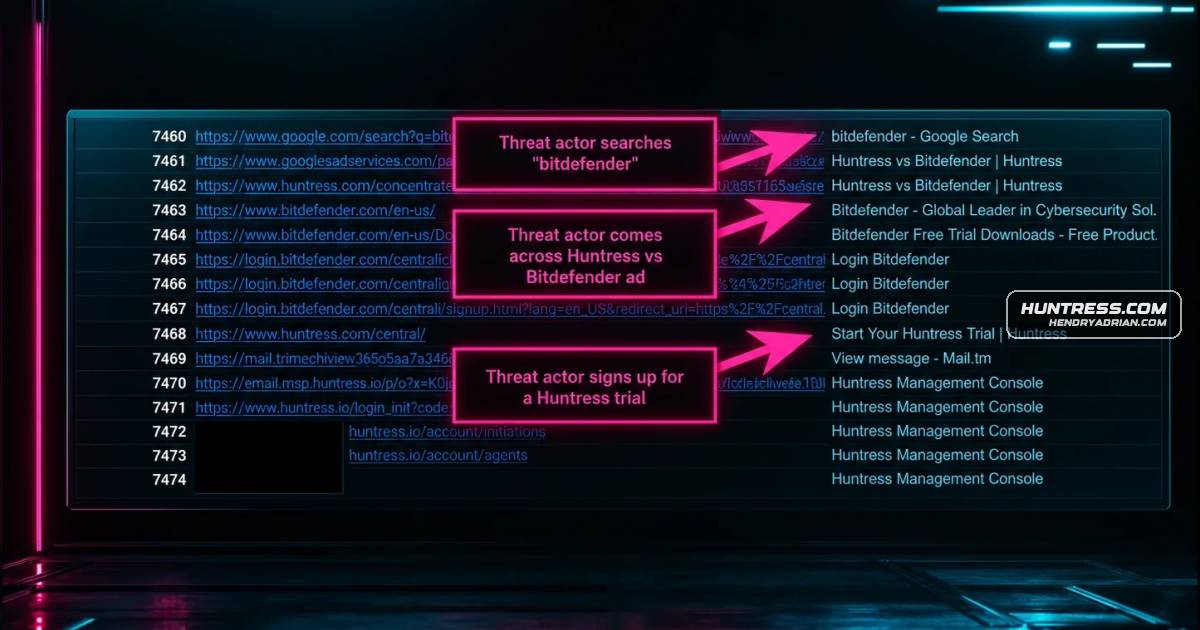
Huntress Details Attacker Workflows Revealed by a Security-Agent Trial

Huntress used browser history and EDR telemetry to investigate an attacker who installed its agent, documenting reconnaissance, automated workflows, and identity-related activity. The company later clarified its analysts removed the agent after 84 minutes.

Sep 9, 2025
Threat Research · threatfabric.com

RatOn Android Trojan Combines NFC Relay, Remote Control and Automated Transfers

ThreatFabric analysts describe RatOn, an Android trojan that combines remote control, NFC relay, automated transfers through a Czech bank app, and cryptocurrency wallet theft. They assess its campaign as targeting Czech users, with Slovakia possibly next.

Sep 9, 2025
Threat Research · global.ptsecurity.com

PhantomCore Campaign Compromises 181 Russian Hosts in Cyberespionage Operation

Researchers detail PhantomCore’s espionage campaign against Russian organizations, reporting 181 compromised hosts, a varied malware toolkit and segmented infrastructure. They also identify evidence suggesting a lower-skilled splinter group.

Sep 9, 2025
Threat Research · thedfirreport.com

DFIR Report Links Intrusion to Tools Used by Three Ransomware Groups

An intrusion began with a fake EarthTime installer that delivered SectopRAT. The attacker used SystemBC and Betruger, stole credentials, and exfiltrated files over unencrypted FTP before being evicted; no ransomware was deployed.

Sep 8, 2025
Threat Research · hexastrike.com

Silver Fox Uses a Signed Driver to Kill Security Products

Analysis of a Silver Fox campaign found fake installers dropping a signed kernel driver that terminates targeted security processes. The report details the driver-loading and termination mechanisms, detection guidance, and containment considerations.

Sep 7, 2025
Threat Research · cloudsek.com

Fake Microsoft Teams Site Uses ClickFix to Deliver Odyssey macOS Stealer

CloudSEK reports a ClickFix campaign using a fake Microsoft Teams download site to deliver Odyssey, which steals credentials, browser data, Apple Notes, and crypto-wallet files before exfiltrating them and establishing persistence.

Sep 5, 2025
Threat Research · wiz.io

Wiz Details AWS SES Abuse Campaign Using Compromised Keys to Enable Phishing

Wiz traced a May 2025 campaign from compromised AWS keys to SES production-mode access and phishing setup. Multi-region API activity and rapid sender configuration provided indicators for detection; the credential theft campaign’s operator remains unattributed.

Sep 4, 2025
Threat Research · wiz.io

Wiz Details Nx Supply-Chain Attack’s Impact and AI-Assisted Data Theft

Wiz reports that malicious Nx packages exposed secrets and private repositories through a three-phase attack. Its analysis found AI-assisted file discovery succeeded in under a quarter of cases, while many leaked credentials remained valid.

Sep 3, 2025
Threat Research · huntress.com

Huntress Analyzes New Obscura Ransomware Variant

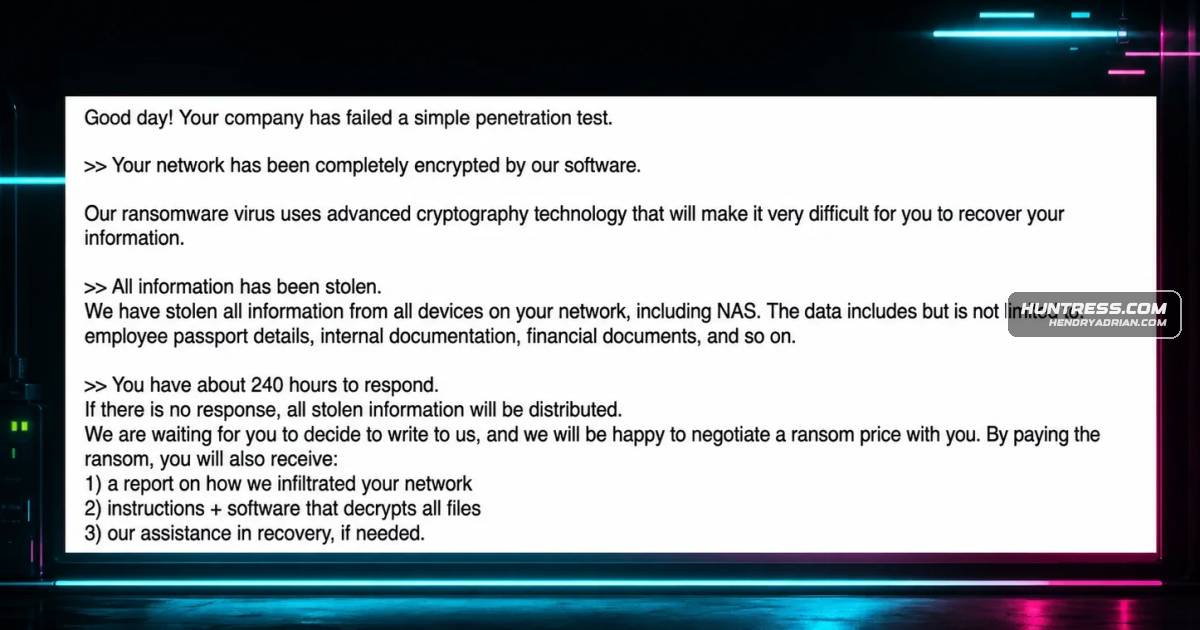
Huntress analyzed a previously unseen ransomware variant found across a victim organization’s hosts. Its investigation details deployment through a domain controller’s NETLOGON share, security-process termination, recovery deletion, and file encryption; initial access

Sep 2, 2025
Threat Research · hunt.io

TinyLoader Uses USB and Network Shares to Spread Malware and Hijack Crypto Transactions

An investigation maps TinyLoader infrastructure and details how the loader delivers Redline Stealer and DCRat, persists and spreads through USB drives and network shares, and replaces copied cryptocurrency addresses.

Sep 2, 2025
Threat Research · huntress.com

Fake AnyDesk Installer Uses Windows Search Redirect to Deliver MetaStealer

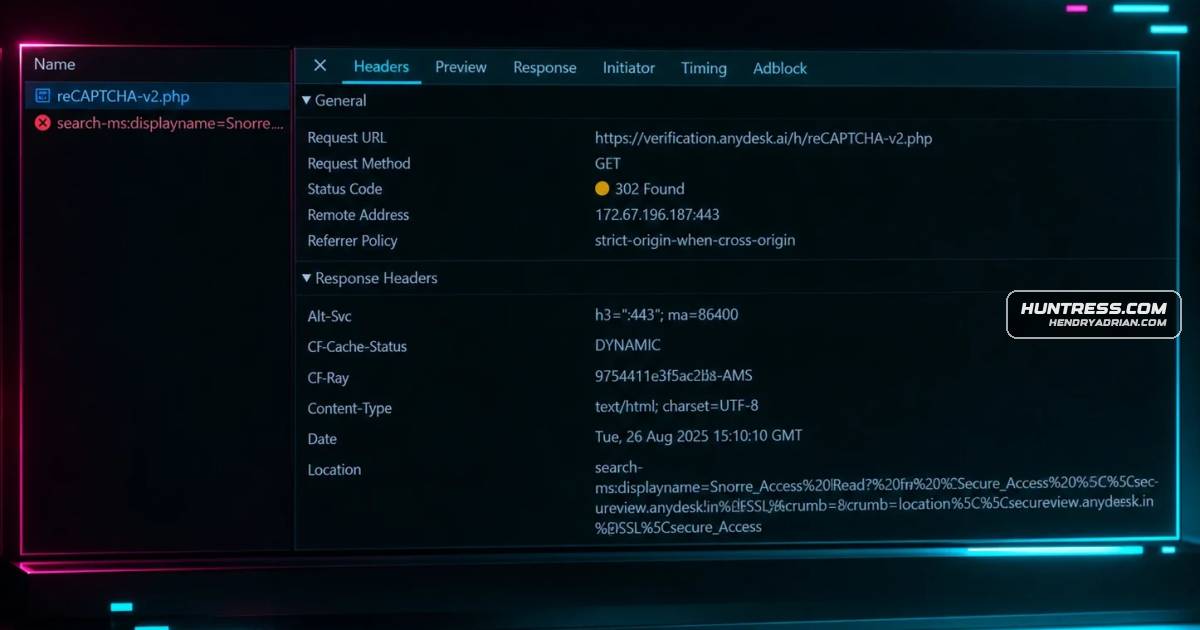
Huntress traced a fake AnyDesk lure through a Cloudflare Turnstile page, Windows File Explorer and an SMB share to an MSI package that collected the victim’s hostname and dropped MetaStealer.

Aug 29, 2025
Threat Research · cloudsek.com

TASPEN-Impersonating Android Malware Targets Indonesian Pensioners

A technical analysis describes an Android malware campaign impersonating Indonesia’s TASPEN pension fund to steal credentials, SMS OTPs, contacts and facial video. The malware uses phishing, encrypted C2 and anti-analysis techniques.

Aug 27, 2025
Threat Research · bitdefender.com

Facebook Ads Spread Brokewell Android RAT Disguised as TradingView App

Bitdefender reports an active Facebook malvertising campaign that uses fake TradingView Android ads to deliver a Brokewell-based RAT capable of stealing crypto and credentials, intercepting SMS, and remotely controlling infected devices.

Aug 26, 2025
Threat Research · threatfabric.com

Android Droppers Adapt to Evade Google Play Protect’s Pilot Program

ThreatFabric reports that Android droppers are increasingly used to deliver even basic spyware and SMS stealers, concealing payloads until after installation to evade Google Play Protect’s Pilot Program checks.

Aug 25, 2025
PreviousPage 89 of 105 Next
© 2026 cyber.hendryadrian.com