cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2377 articles

Threat Research · huntress.com

Amazon-Themed ClickFix Campaign Uses Windows Finger to Deliver Doina and Lumma Stealer

Huntress traced an Amazon-themed ClickFix campaign affecting at least three customers: a fake login and CAPTCHA used finger.exe to launch a multi-stage chain delivering Doina, allegedly Lumma Stealer, and pirated NetSupport. Google removed the ad, but infrastructure was
Oct 21, 2026
Threat Research · security.com

Symantec Details ‘Skynet’ Agent Hijacking Exposed AI Models to Power Attacks

Symantec researchers used an AI honeypot to capture instructions for an autonomous agent targeting exposed LLMs, plus a separate mining script. The agent was designed to exploit systems, steal data and credentials, and mine cryptocurrency.

Oct 21, 2026
Threat Research · bleepingcomputer.com

Lazarus Uses Post-Quantum Cryptography to Deliver Malware in FlashHole Campaign

Kaspersky says Lazarus’s FlashHole campaign targeted South Korean organizations using a malware chain that included LPEClient and ML-KEM-1024 to secure payload delivery; researchers identified at least three affected companies.

Oct 21, 2026
Threat Research · databreachtoday.com

US, UK and Germany Warn SafePay Ransomware Has Hit at Least 600 Victims

A joint U.S., U.K. and German advisory says SafePay has compromised at least 600 victims since August 2024, using stolen credentials and exploited vulnerabilities to steal data and encrypt systems.

Oct 21, 2026
Threat Research · bleepingcomputer.com

ClickFix Campaigns Expand, Using AI Tools as a Convincing Lure

Push and other researchers report growing ClickFix activity, including fake AI-tool installers and malicious chatbot content. Attackers use search ads, compromised sites, deceptive clipboard commands, and conditional delivery to evade defenses.

Oct 21, 2026
Threat Research · acronis.com

Acronis details The Gentlemen ransomware’s encryption and EDR-killing tactics

Acronis researchers analyze The Gentlemen RaaS, detailing its cross-platform ransomware, data-theft extortion, persistence, evasion, encryption and network propagation, plus an EDR killer that abuses vulnerable Safetica and Lenovo drivers.

Oct 21, 2026
Threat Research · wiz.io

Wiz Details GCP Attacks That Hijack Cloud Billing for Unauthorized LLM Use

Wiz CIRT describes GCP intrusions in which attackers phished privileged users, linked attacker-controlled projects to victims’ billing accounts, and drove unauthorized Gemini API charges reaching tens to hundreds of thousands of dollars.

Oct 20, 2026
Threat Research · ic3.gov

Joint Advisory Details SafePay Ransomware Tactics and at Least 600 Victims

A joint U.S., U.K., and German advisory says SafePay ransomware has affected at least 600 victims. It details credential-based access, vulnerability exploitation, data theft, backup destruction, and encryption, alongside mitigation guidance.

Oct 20, 2026
Threat Research · levelblue.com

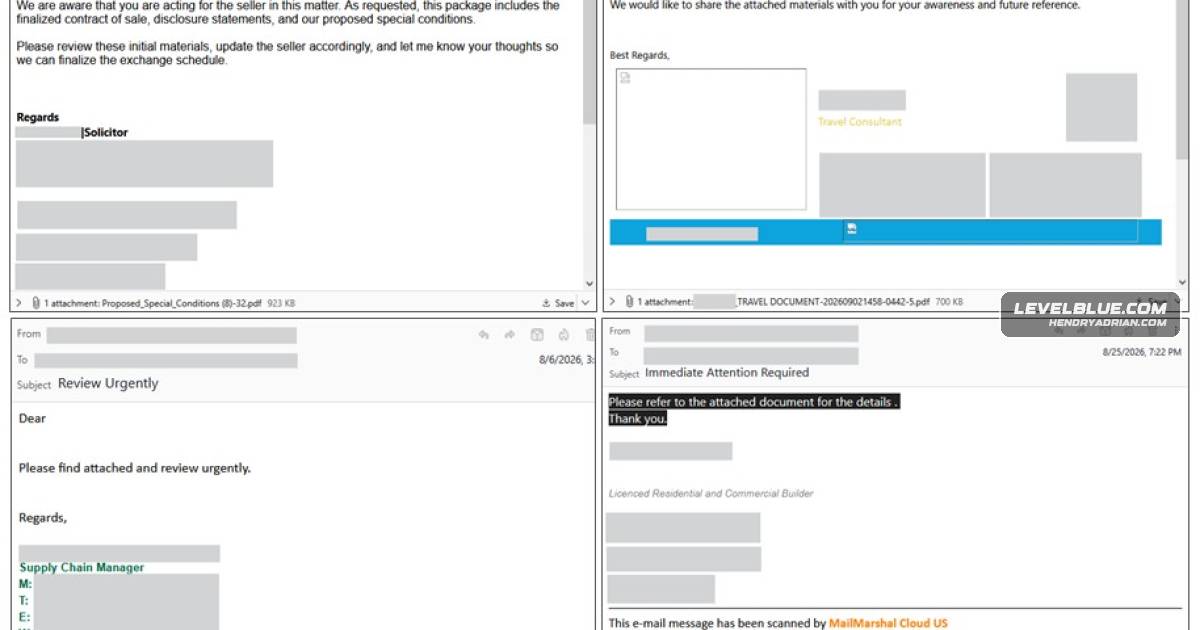
Inside Wazza: Device Code Phishing Kit Targets Microsoft 365 Accounts

LevelBlue SpiderLabs traced Wazza phishing campaigns active since at least July 2026. The kit uses PDF lures, layered redirects, browser checks and Microsoft device code authentication to seek access to Microsoft 365 accounts.

Oct 20, 2026
Threat Research · asec.ahnlab.com

New Rust Infostealer Evades Sandboxes and Can Deploy Additional Malware

AhnLab reports a Rust infostealer distributed as pirated software that uses sandbox evasion and process injection, steals data based on C2 instructions, and can download additional malware.

Oct 20, 2026
Threat Research · blogs.jpcert.or.jp

JPCERT/CC Finds AI-Assisted API Attacks Using APK Analysis and SSRF Testing

JPCERT/CC traced servers linked to attacks on organizations and web services, finding AI-assisted vulnerability scanning, APK analysis and API testing. A separate server contained web shells and EDR-evasion evidence; it was not directly linked to the attacks.

Oct 20, 2026
Threat Research · research.checkpoint.com

Check Point Research Details How AI-Enabled Antidetect Browsers Support Fraud and Influence Operations

Check Point Research examines how Kameleo, AdsPower, and MultiLogin use fingerprint spoofing, proxies, and AI automation to support fraud, account takeovers, phishing, and influence operations, and recommends detection measures.

Oct 20, 2026
Threat Research · securityweek.com

UNC7017 Used Brief AOMEI Backupper Tampering Windows to Deliver Malware

Researchers report that UNC7017 used brief AOMEI Backupper server-tampering windows to deliver CrossRoad and ShinyRoad malware, compromise organizations across multiple sectors, and steal NetNTLMv2 authentication hashes.

Oct 20, 2026
Threat Research · cisa.gov

Joint Advisory Details SafePay Ransomware Tactics After at Least 600 Victims

A joint advisory from CISA, the FBI and international partners says SafePay ransomware has affected at least 600 victims. It details credential-based intrusions, vulnerability exploitation, data theft, backup destruction and encryption.

Oct 20, 2026
Threat Research · rogueauthority.org

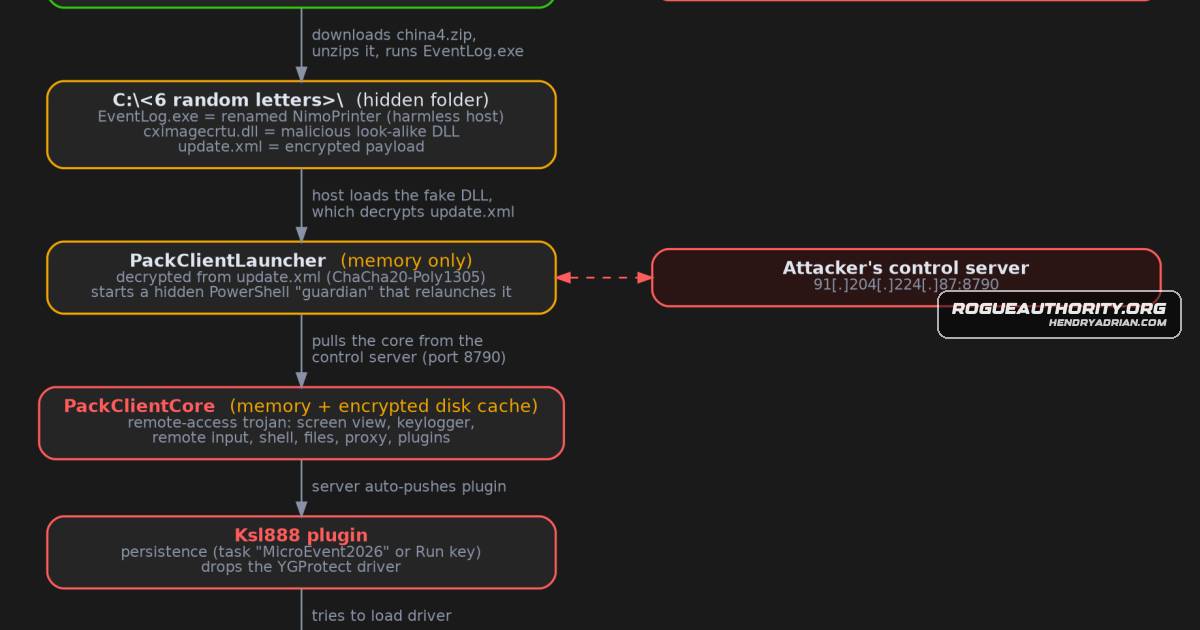
Signed SilentSetup Installer Delays Execution Before Deploying PackClient RAT

Analysis traces a signed Windows installer that waits until a hard-coded date, then uses DLL sideloading to deploy PackClient RAT. Its plugin adds persistence and a signed antivirus-killing driver, which failed to load in three sandbox runs.

Oct 20, 2026
Threat Research · securelist.com

Warehouse Attack Paths Link Scanners, Printers and WMS to Operational Disruption

Kaspersky examines how warehouse scanners, printers, wireless networks and management systems can expose logistics operations to compromise, potentially enabling inventory manipulation, unauthorized shipments and disruption.

Oct 20, 2026
Threat Research · security.com

Swallowtail Used Hookedge, Credential Theft and SSH Tunneling in NATO Defense Intrusion

Symantec traced Swallowtail activity against targets in two NATO countries, including a naval shipbuilder. Its investigation details Hookedge delivery, credential theft, a persistent SSH tunnel and an undocumented loader; the final payload was not recovered.

Oct 20, 2026
Threat Research · socradar.io

SOCRadar Uncovers Exposed AI-Assisted Ransomware Infrastructure Linked to INC and The Gentlemen

SOCRadar says seven exposed servers revealed AI-assisted operations linked to INC and The Gentlemen, including Phantom source code and 46 staged INC encryptors. Operator-reported exploitation counts are unverified; a screenshot showed encryption in progress.

Oct 20, 2026
Threat Research · sophos.com

BRONZE SANDCASTLE Uses DLL Sideloading to Deploy Modified Meterpreter-Based Payloads

Sophos researchers detail BRONZE SANDCASTLE’s DLL sideloading, obfuscated in-memory backdoor, C2 behavior, and credential-theft activity across victims in Asia and Africa. They recommend behavioral, endpoint, and memory-based detection.

Oct 20, 2026
Threat Research · databreachtoday.com

Fake Bank Support Sites Deliver Remote-Access Tools in Phone-Led Fraud Campaign

Lab539 reports an active phone-led fraud campaign using cloned bank support pages to trick customers into installing remote-access tools. The researchers say the campaign has used more than 380 domains and report that two abused signing certificates were revoked.

Oct 20, 2026
Threat Research · hunt.io

Research Details Graylog Log4Shell Activity Against Ukrainian Data-Exchange Systems

Hunt.io researchers traced a Russian-speaking operator’s Graylog Log4Shell activity against Ukrainian organizations, documenting execution on at least two hosts and no observed exfiltration from one data-exchange logging cluster. The operator was not attributed to a

Oct 20, 2026
Threat Research · opensourcemalware.com

Hijacked Contributor Account Used to Replace OVHcloud CLI Release Assets

On Oct. 19, an attacker using a hijacked OVH contributor account replaced assets in five OVHcloud CLI releases with a secret-stealing build. OVH removed them and issued immutable v0.16.0; whether March GlassWorm-linked activity shared the same actor is unconfirmed.

Oct 19, 2026
Threat Research · rapid7.com

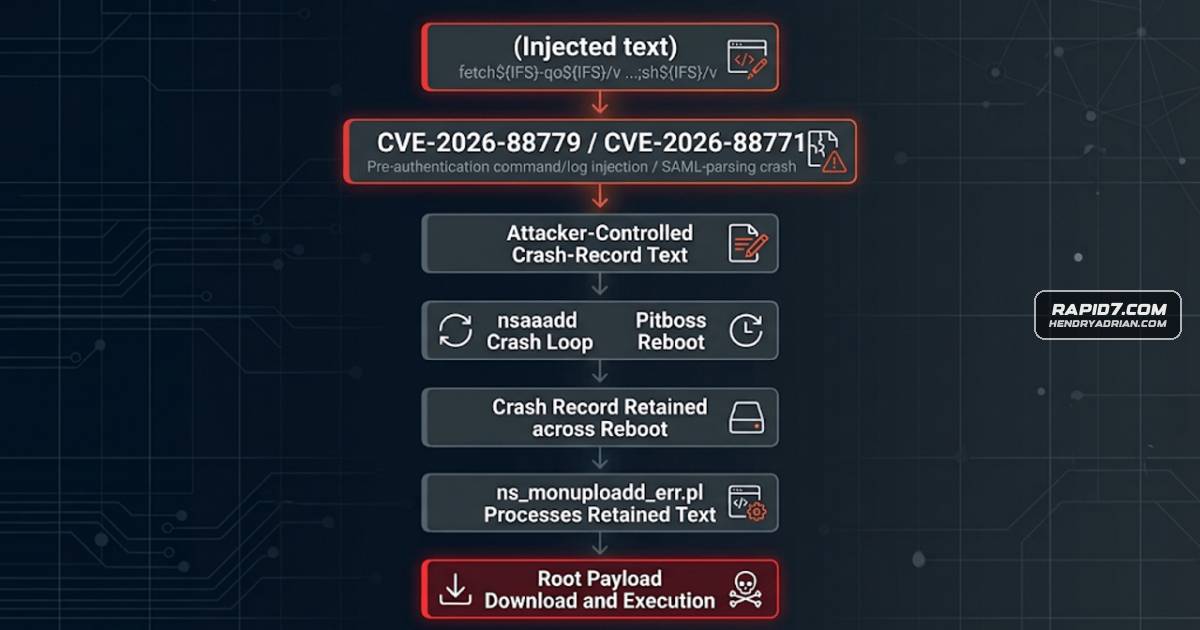
Rapid7 Details NetScaler Intrusion Chaining Two CVEs to Establish Persistent Access

Rapid7 traced a NetScaler intrusion that chained CVE-2026-88771 and CVE-2026-88779 to gain root execution, maintain access, map internal systems, and exfiltrate configuration data. The investigation provides technical findings and defensive guidance.

Oct 19, 2026
Threat Research · thehackernews.com

GhostAction Campaign Adds OAuth Phishing and a Persistent Credential Stealer to 94 GitHub Repositories

OpenSourceMalware says GhostAction attackers used OAuth phishing and a VS Code-triggered stealer in 94 GitHub repositories. The stealer persists on developer machines; researchers recommend revoking access, rotating credentials, and auditing repositories.

Oct 19, 2026
PreviousPage 9 of 100 Next
© 2026 cyber.hendryadrian.com