Acronis details The Gentlemen ransomware’s encryption and EDR-killing tactics
Summary
Acronis researchers analyze The Gentlemen RaaS, detailing its cross-platform ransomware, data-theft extortion, persistence, evasion, encryption and network propagation, plus an EDR killer that abuses vulnerable Safetica and Lenovo drivers.
Key points
- The Russian-speaking group, previously known as ArmCorp or Phantom Mantis, began deploying its own ransomware in 2025 after reportedly affiliating with LockBit and Qilin.
- The group claims more than 800 victims; its ransomware targets Windows, Linux, NAS and BSD systems and uses encryption plus data theft for extortion.
- The ransomware disables Windows Defender monitoring, clears logs and forensic artifacts, establishes persistence through scheduled tasks and registry entries, and removes shadow copies.
- It uses ChaCha20 for file encryption and elliptic-curve cryptography to protect per-file keys; files larger than 1 MB are partially encrypted in multiple chunks.
- With the --spread option, it can identify a domain, alter Windows Defender-related Group Policy settings, and use PsExec to copy and run itself on other workstations.
- Acronis researchers describe an EDR killer that loads vulnerable Safetica ProcessMonitorDriver or Lenovo BootRepair.sys drivers to terminate selected processes. The Safetica issue is tracked as CVE-2025-70795.
- A May 2026 breach of the group’s infrastructure exposed backend data, including communications and affiliate information, which researchers used to examine its operations and ecosystem links.
Article Details
- Attack Vectors
- The Gentlemen ransomware encrypts files and can exfiltrate data for double extortion.
- With the --spread argument, the ransomware identifies the domain and other workstations, then uses PsExec to copy and execute itself on them.
- An EDR-killer dropper installs vulnerable Safetica ProcessMonitorDriver or Lenovo BootRepair.sys drivers and uses them to terminate selected processes.
- The ransomware can search connected network shares for encryption when run with the --shares or --full argument.
- Defensive Notes
- Deploy and maintain endpoint security capable of detecting suspicious process or service termination, security-tool tampering, mass encryption, and unauthorized driver loading.
- Keep operating systems, applications, security products, and third-party drivers updated; apply security patches promptly, especially for vulnerabilities that could enable abuse of kernel drivers.
- Monitor and restrict PowerShell, remote-administration tools, and other utilities commonly abused by ransomware; alert on unusual administrative activity and cross-host execution.
- Maintain regular, tested backups protected from modification or deletion by compromised systems; isolate critical backups where possible.
- Apply least-privilege access controls and network segmentation, and restrict unnecessary administrative privileges and remote access between systems.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| SHA256 | 1334f0189a8e6dbc48456fa4b482c5726ab7609f7fa652fcc4c1a96f2334436f | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | 143af42b492b0f36b296b0b593bd630248b5641c20b1ca1e5603e7e01b5b0676 | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | 228fc86acbaa6626051fd189932cb1768254aec5a9539771cee8a567103bbec1 | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | 363a435e517f344056c42f8d46ef73396220f79e780828ad35ec0a68e7525d02 | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | 3c2466d8a4572c26530e6f6bcef01fc1baefb98dbff2c65efaed5599622f51f3 | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | 403187f08c064f244e101bbc03f1fb5b82af8ebdf4b2be0ba1a70d59ac74b313 | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | 4de88220ff6a6dcb137b17d8d3f77ab4bacc39ea4e4d1147f687b021b7a82b8c | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | 5206a05eb128ccdef497f7f234cb27678046f6c6b12aa7a072672f2a4694c2b9 | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | 586459f1adf018de4586dcd61782839a3ee72d8469944e0f4dd45a6e20598869 | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | 6a70824fc1777f81c8e8289258ac951e6bac7636db5315b6d7e76c5a58b82b6b | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | 7284d45bdbb1e32e3fb1ca6041b448b165795c91a2748de715798238fc8b3bff | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | 7d90023d535096da99bffcb3370008355435d9f022232870f3c27d29be8be60c | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | 7eb2fd5e79e79c3f2a95023d617062908c9d8c5aff9fed8361a5a74dc0d1af75 | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | 9c6f6c0d7127c95aa1360ad6fb0ba5679527a6ea2cc17eb0bc2162dd1e13cd09 | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | a1500204822fb16556a274132d802ba18a7e8b95cf134bd17b473f915e8cda81 | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | a974a9f097bc2e26f285560f1454c70710c88c30c0ae1edfa2977ad862c56716 | Hash listed for a vulnerable driver dropped by the EDR-killer samples. |
| SHA256 | afc30b1a14f2f29572412ba883782eb3ad3a9e6bf9ff9c38aa48ff35a4ee73fa | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | bd5950d4bd3de1c6d1609b8369b7332ada40c50070a9a3cd8e80ec89b19c48dc | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | cd66fb941e63ad9a72687cafb050ed5b4d8b97b34461168581c4f150d6501523 | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | dce2e5cc00eff2493f8ced546dc51f9d5ef78c5ee56805906ec642dfa77a1c70 | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| SHA256 | dfdc8313921c0f594ee1cd41ff7ef73d973c667438c2dfe5c38cafdbba10defb | Hash listed for a vulnerable driver dropped by the EDR-killer samples. |
| SHA256 | f483faa2b9c9815a0efb08023fe5d243b1b9f7e04b95127c506b6aae824c9d09 | SHA-256 hash listed as a Windows IOC for The Gentlemen threat activity. |
| URL | hxxps[:]//smp10[.]simplex[.]im/a#Otp0TGDMNIj_QnXcvh9ABwFsiZEaZY_BovoanW59MXI | Specific SimpleX chat link provided for communication with The Gentlemen threat actors. |
MITRE ATT&CK
T1053.005 · Scheduled TaskThe sample attempts to establish persistence with scheduled tasks named UpdateSystem and UpdateUser.T1059.001 · PowerShellThe ransomware uses embedded PowerShell scripts and commands for system operations, drive discovery, domain discovery, and propagation.T1059.003 · Windows Command ShellThe sample uses Windows command-shell commands, including taskkill, net stop, and commands to clear files and logs.T1070.001 · Clear Windows Event LogsThe ransomware clears the System, Application, and Security Windows event logs.T1070.003 · Clear Command HistoryThe sample deletes PowerShell PSReadLine history files across user profiles.T1070.004 · File DeletionThe ransomware deletes files from locations including Prefetch and Windows Defender Support directories to remove forensic artifacts.T1105 · Ingress Tool TransferWith --spread, the sample downloads PsExec to C:\Temp before using it to propagate.T1135 · Network Share DiscoveryWith --shares or --full, the ransomware loops through drive letters with net use to find connected network shares.T1486 · Data Encrypted for ImpactThe Gentlemen encrypts eligible files, appends encrypted key material, and changes their extensions.T1489 · Service StopThe ransomware terminates selected processes and stops targeted services, including database, virtualization, backup, and security software.T1490 · Inhibit System RecoveryBefore encryption, the sample deletes available Volume Shadow Copies using vssadmin and WMIC.T1547.001 · Registry Run Keys / Startup FolderThe sample creates GupdateS and GupdateU autostart entries under the HKLM and HKCU Run registry keys.T1562.001 · Disable or Modify ToolsThe ransomware disables Windows Defender real-time monitoring and adds exclusions; its spread routine also modifies Defender-related Group Policy settings.T1562.004 · Disable or Modify System FirewallThe sample disables Windows Defender Firewall for Domain, Private, and Public profiles.T1570 · Lateral Tool TransferWith --spread, the sample uses PsExec to copy the ransomware to available workstations on the network.
CVE
People
Threat Actors
ArmCorpName the article says The Gentlemen was previously known by.LockBitThe article reports that The Gentlemen initially operated as an affiliate of LockBit.Phantom MantisName the article says The Gentlemen was previously known by.QilinThe article reports that The Gentlemen initially operated as an affiliate of Qilin and says leaked data provided further evidence linking The Gentlemen's leadership to its ransomware ecosystem.The GentlemenRansomware-as-a-service group; the article says it has claimed more than 800 victims and uses double extortion.
Malware
Vendors
AcronisAcronis Threat Research UnitLenovoIn a recent incident, a custom dropper was observed deploying vulnerable Safetica ProcessMonitor and Lenovo BootRepair.sys drivers to terminate security processes.Safeticaand PhantomKiller_clone_04_94354C0F.sys. They correspond to Safetica Technologies' ProcessMonitorDriver version 11.26.18 and Lenovo's BootRepair.sys driver version 2.5.30.11281,
Products
BootRepair.Sysincident, a custom dropper was observed deploying vulnerable Safetica ProcessMonitor and Lenovo BootRepair.sys drivers to terminate security processes.Microsoft WindowsThe group supports multiple platforms, with ransomware variants targeting Windows, Linux, NAS, and BSD systems allowing its affiliates to target a broad range of enterprise environments.ProcessMonitorDriverand PhantomKiller_clone_04_94354C0F.sys. They correspond to Safetica Technologies' ProcessMonitorDriver version 11.26.18 and Lenovo's BootRepair.sys driver version 2.5.30.11281, respectively.Windows DefenderThe Gentlemen ransomware disables real-time monitoring in Windows Defender and adds the entire C:\ drive, along with its own process name, to the Defender exclusion list.
Tools
Countries
Industries
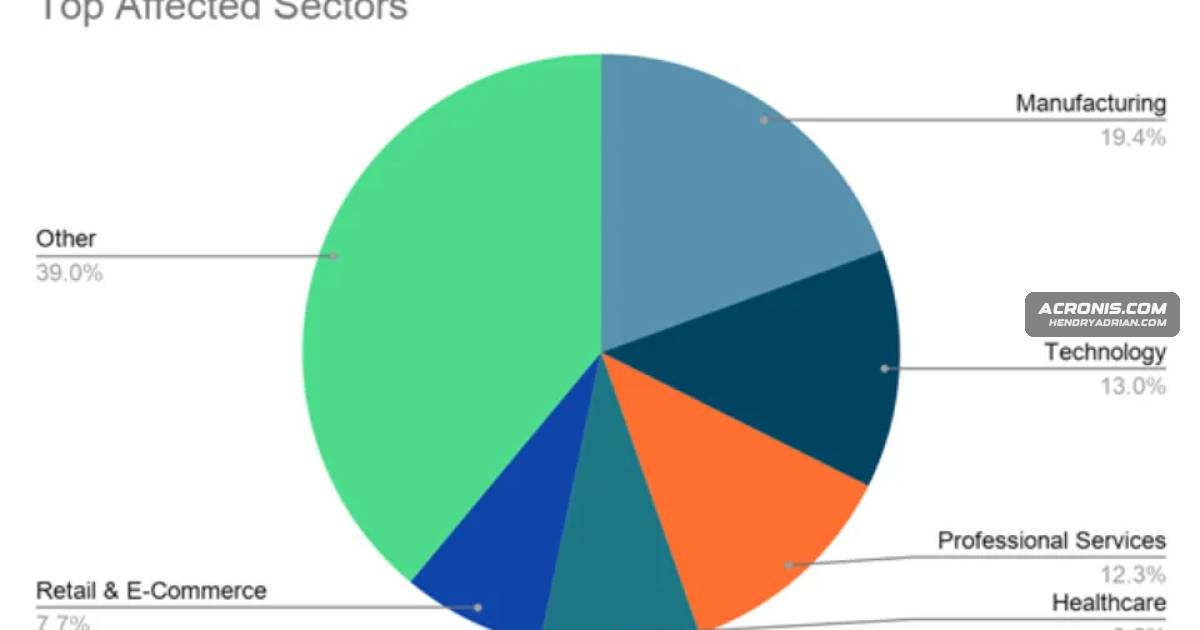
Educationhealth care, professional services and retail. Other affected sectors include organizations in education, financial services, government, energy and transportation.Energyand retail. Other affected sectors include organizations in education, financial services, government, energy and transportation.Financial Servicescare, professional services and retail. Other affected sectors include organizations in education, financial services, government, energy and transportation.Governmentservices and retail. Other affected sectors include organizations in education, financial services, government, energy and transportation.HealthcareThe most frequently targeted sectors include manufacturing, technology, health care, professional services and retail. Other affected sectors include organizations in education, financial services, government, energyManufacturingThe most frequently targeted sectors include manufacturing, technology, health care, professional services and retail. Other affected sectors include organizations in education, financial services, government, energyProfessional ServicesThe most frequently targeted sectors include manufacturing, technology, health care, professional services and retail. Other affected sectors include organizations in education, financial services, government, energyRetailfrequently targeted sectors include manufacturing, technology, health care, professional services and retail. Other affected sectors include organizations in education, financial services, government, energy andTechnologyThe most frequently targeted sectors include manufacturing, technology, health care, professional services and retail. Other affected sectors include organizations in education, financial services, government, energyTransportationOther affected sectors include organizations in education, financial services, government, energy and transportation.