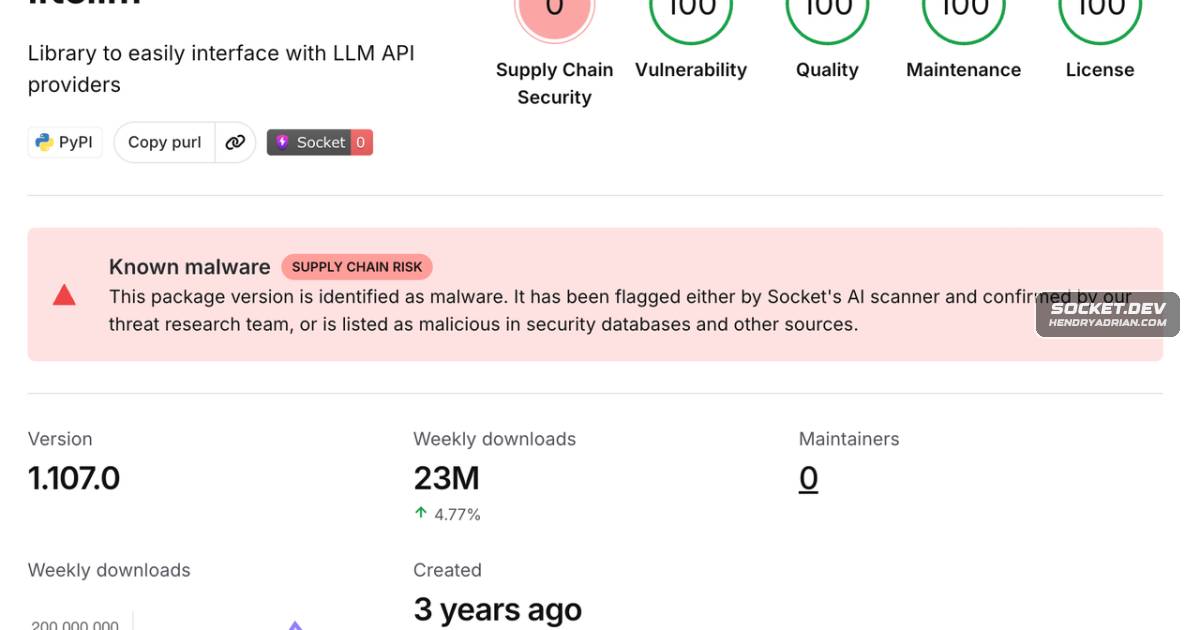
LiteLLM 1.107.0 Supply-Chain Attack Steals Credentials Through PyPI and Docker
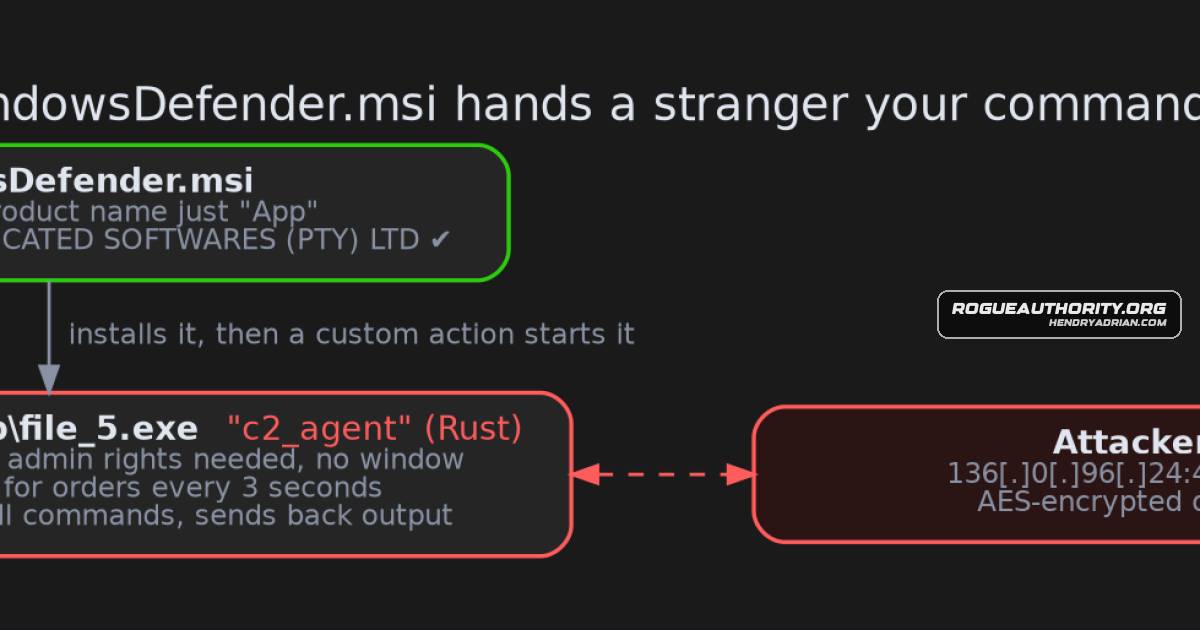
Attackers published trojanized LiteLLM 1.107.0 packages and Docker images, apparently using stolen maintainer tokens. The payload stole credentials and enabled follow-on AWS reconnaissance; artifacts were removed, and users are advised to rebuild affected hosts and