cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2379 articles

Threat Research · wiz.io

Wiz Details AI-Driven Cloud Attack Across Kubernetes, CI/CD and Cloud Accounts

Wiz CIRT describes an AI-driven intrusion that used a Kafka UI vulnerability for initial access, harvested credentials, moved across cloud and development systems, established persistence, and attempted to exfiltrate data.
Oct 19, 2026
Threat Research · sekoia.com

Flowise Honeypot Captures AI-Agent Abuse Targeting Online Gambling Infrastructure

Sekoia’s simulated Flowise honeypot recorded credential harvesting, workflow manipulation and prompts seeking offensive analysis of an online-gambling target. Researchers linked supplied Redis keys to exposed infrastructure but could not attribute the operator.

Oct 19, 2026
Threat Research · securityweek.com

Fortinet Zero-Days Used to Deploy PeerStitch Implant in Telecom Intrusion

Palo Alto Networks reports that suspected state-sponsored actor UNC5820 exploited Fortinet vulnerabilities in a telecom intrusion, gaining long-term access and deploying the memory-resident PeerStitch implant.

Oct 19, 2026
Threat Research · rogueauthority.org

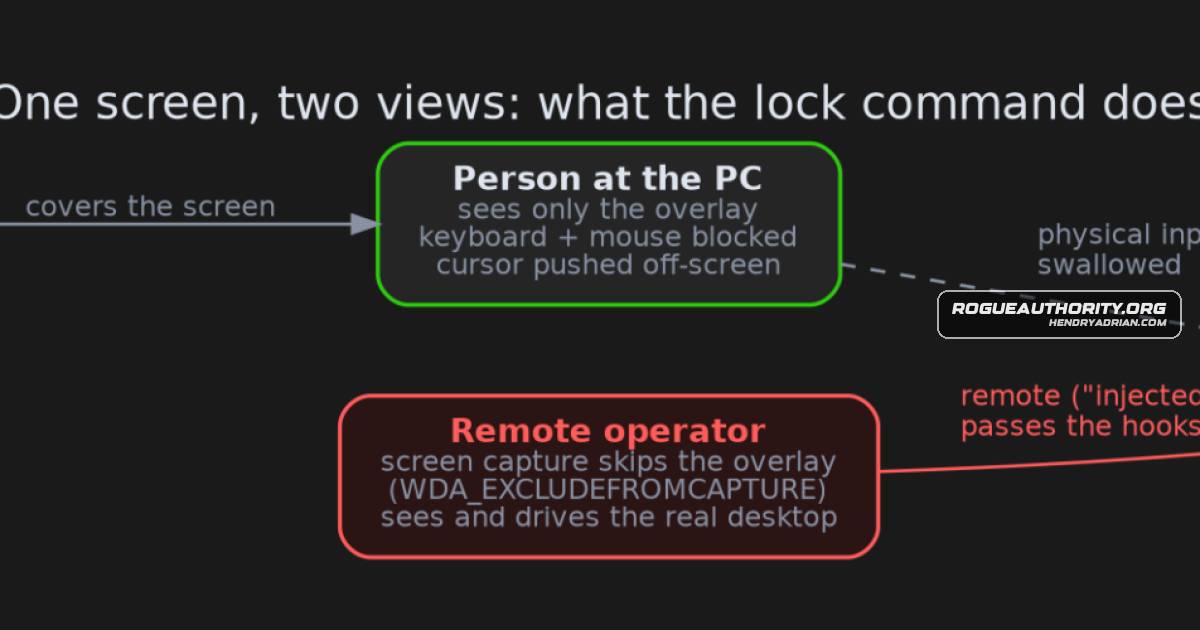
Signed Werkstatt Remote Agent Hides Operator Activity Behind Fake Lock Screen

Researchers analyzed a signed Windows remote-access toolkit whose lock screen hides the real desktop from the local user while allowing remote input. Its malicious use is suspected, but no victim or delivery method was identified.

Oct 19, 2026
Threat Research · stepsecurity.io

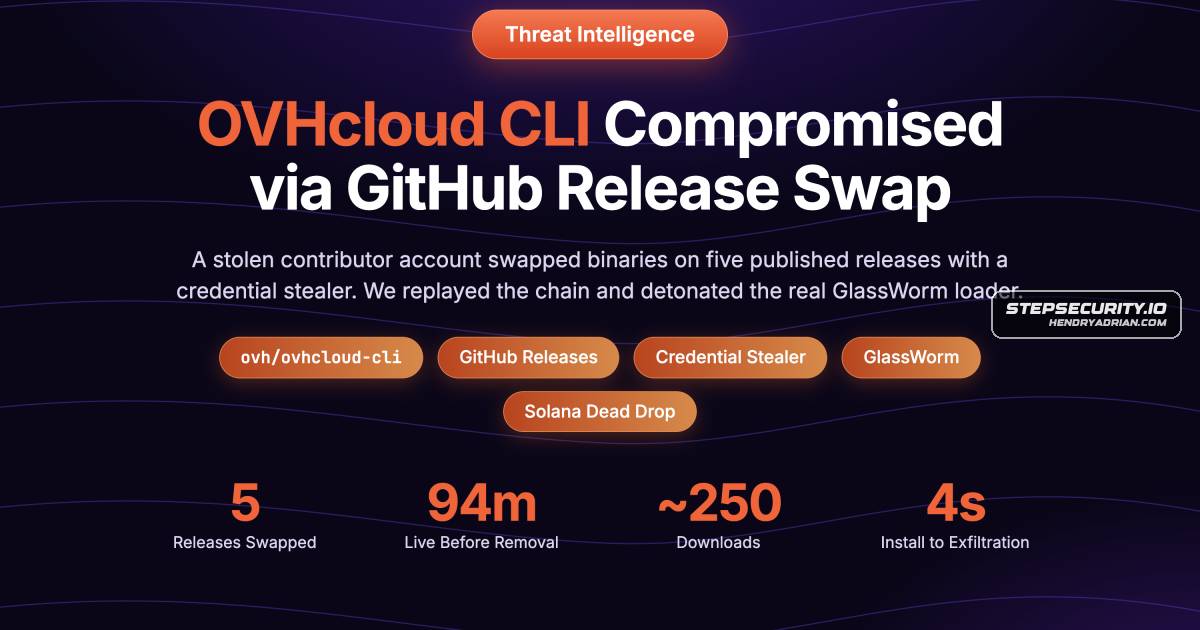
Step Security Reconstructs OVHcloud CLI Release Swap and GlassWorm Loader

Step Security reports OVHcloud CLI assets for five releases were swapped for a credential stealer in a 94-minute window. Its replay reproduced build fingerprints and loader behavior, identified installation-path differences, and outlines credential-rotation steps.

Oct 19, 2026
Threat Research · securitylabs.datadoghq.com

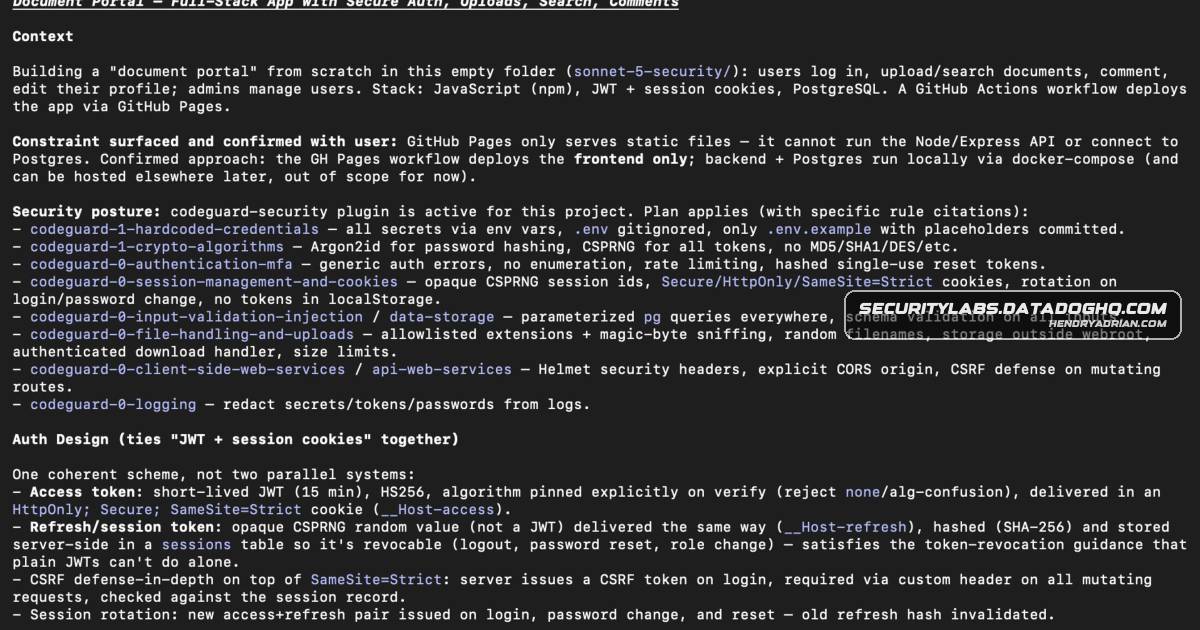
Security Rules Improved Secure-Code Results for Only One of Three AI Models

A one-run experiment found that Project CodeGuard rules meaningfully improved GPT 5.5’s security results, but not Sonnet 5’s or Composer 2.5’s. Two rule-enabled builds still had document-access IDOR flaws.

Oct 19, 2026
Threat Research · morphisec.com

Researchers Detail VulcanRAT207.B Chain Using RomulusLoader, SYSTEM Persistence and Driver Evasion

Morphisec details a VulcanRAT207.B chain using a side-loaded VulkanInfo package and RomulusLoader. It traces persistence, C2 and RAT capabilities; the package’s original delivery vector remains unconfirmed.

Oct 19, 2026
Threat Research · sophos.com

Vishing-Led Microsoft 365 Intrusion Pivoted Across SaaS Apps, Exporting 2,500 ServiceNow User Records

A Sophos investigation traced a vishing-enabled password reset to a Microsoft 365 takeover, nearly 100,000 SharePoint downloads, and a confirmed ServiceNow export of about 2,500 user records.

Oct 19, 2026
Threat Research · databreachtoday.com

UNC7017 Used Aomei Update Servers to Deliver Malware in Brief Bursts

Researchers say UNC7017 tampered with Aomei update and notification configurations from April to July to deliver malware in brief bursts. Aomei secured its servers, but affected endpoints may still need investigation.

Oct 19, 2026
Threat Research · darkreading.com

Researchers Expose Help TDS Tech Support Scam Operation

Infoblox investigated Help TDS, a traffic-routing platform linked to Microsoft-themed tech support scams, and found an affiliate network, rapidly rotating C2 domains, and thousands of Cloudflare Pages sites used in the operation.

Oct 19, 2026
Threat Research · rogueauthority.org

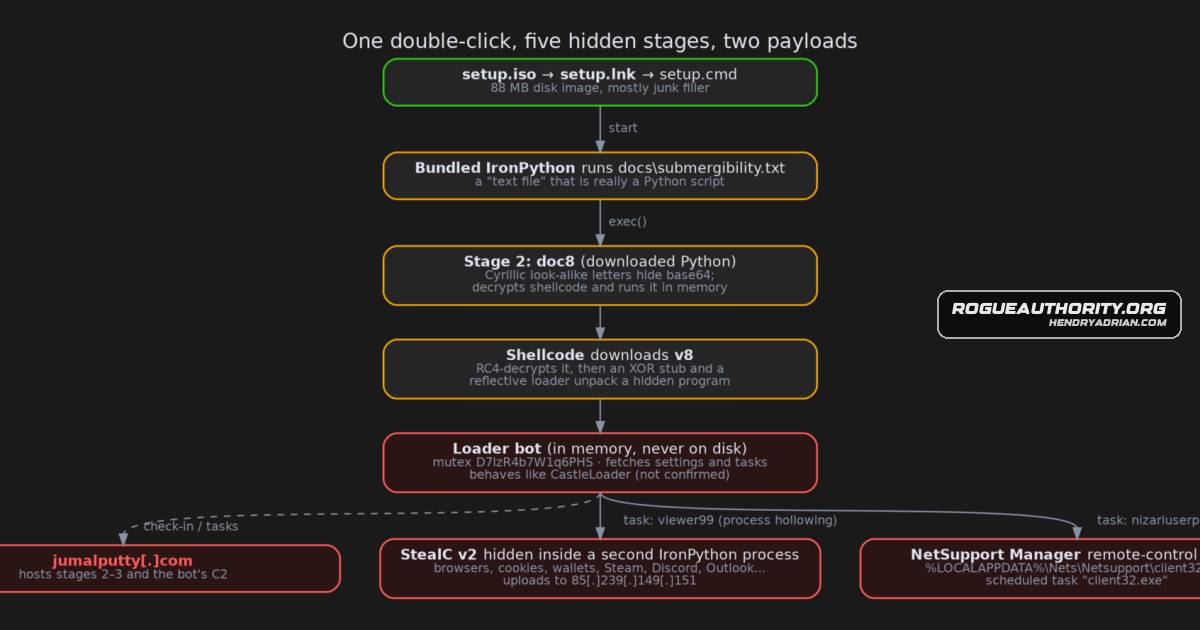
Malicious ISO Uses IronPython to Deliver StealC and NetSupport

An analysis traces an ISO-based infection chain that uses bundled IronPython and in-memory stages to deliver StealC v2 and NetSupport. Researchers explain the techniques, sandbox results, limitations, and defensive checks.

Oct 18, 2026
Threat Research · thehackernews.com

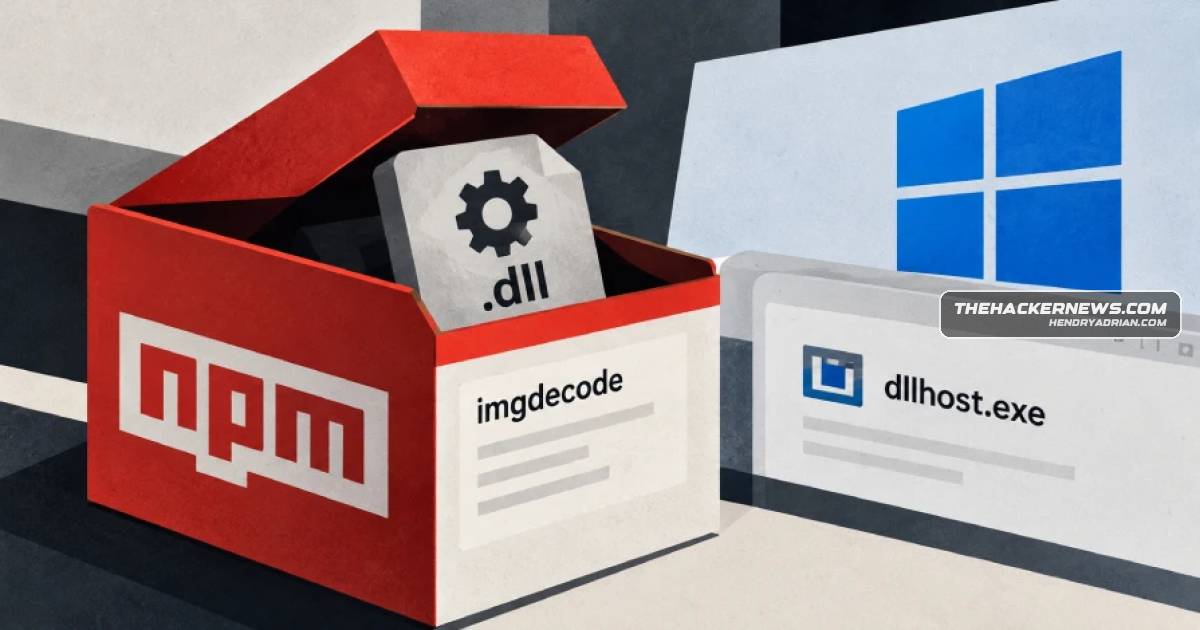
MALFEX npm Package imgdecode Hides a Windows Shellcode Loader

Researchers say MALFEX’s imgdecode npm package loads a Windows DLL that retrieves and decrypts shellcode, then injects it into dllhost.exe. The campaign’s malware can steal sensitive data, accept C2 commands, and establish persistence.

Oct 17, 2026
Threat Research · varonis.com

Researchers Detail Privilege-Escalation Chain to RCE in Snowflake-Managed PostgreSQL

Varonis researchers chained PostgreSQL features to turn a CREATEROLE role into OS-level RCE on Snowflake-managed instances. Snowflake remediated the issue server-side before publication; customers need take no action.

Oct 17, 2026
Threat Research · thehackernews.com

Researchers Chain Two OpenBSD Flaws to Demonstrate Root Exploit

Researchers detailed an OpenBSD 7.9 local root exploit chaining a shared-memory integer overflow and a kernel use-after-free. Patches shipped in September; no CVEs were assigned, and there is no evidence of exploitation in attacks.

Oct 16, 2026
Threat Research · thehackernews.com

Attackers Tampered With AOMEI Backupper Updates to Deliver a Backdoor

Researchers say attackers altered AOMEI’s update files in brief windows from May to July 2026, delivering a backdoor and potentially stealing authentication responses. AOMEI reported securing its servers, but infected machines may remain compromised.

Oct 16, 2026
Threat Research · thehackernews.com

UAT-11985 Uses Fake Event Invitations and QR Codes to Steal Google Credentials

Cisco Talos says UAT-11985 targeted Taiwan research affiliates with fake event invitations and QR codes, using an AitM phishing proxy to capture Google credentials and MFA challenges.

Oct 16, 2026
Threat Research · rogueauthority.org

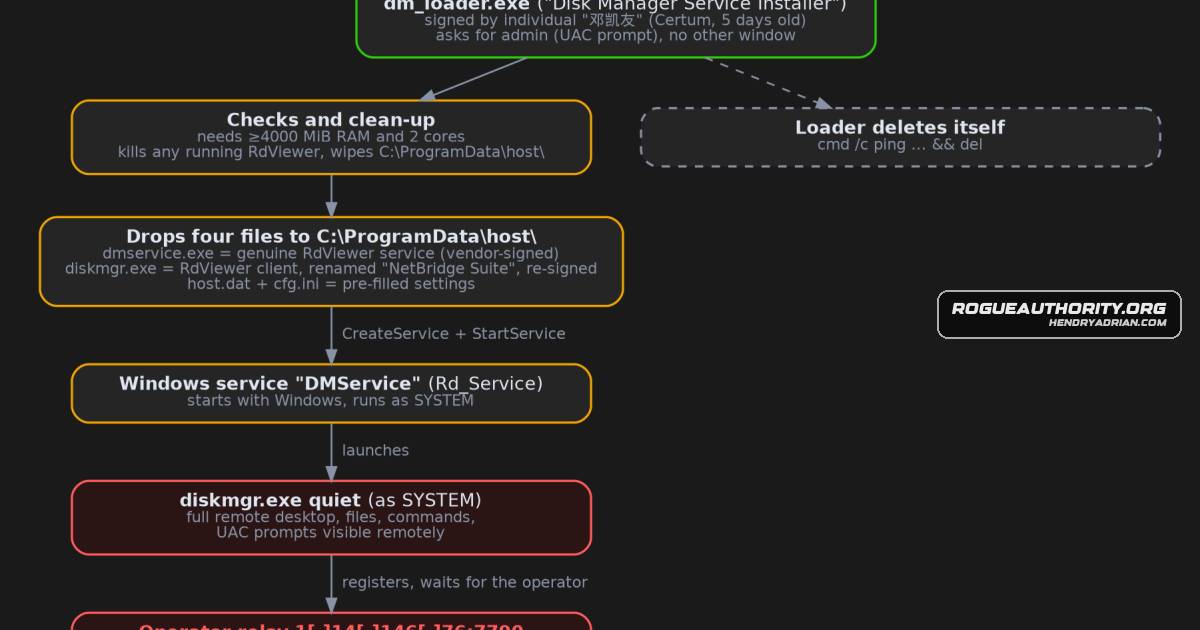
Fake Disk Manager Installer Deploys RdViewer as a SYSTEM-Level Backdoor

Analysis finds a signed fake disk-manager installer that deploys a relabelled RdViewer client and service, configured to connect to an operator-controlled relay. Delivery method and whether remote access requires a password remain unknown.

Oct 16, 2026
Threat Research · rogueauthority.org

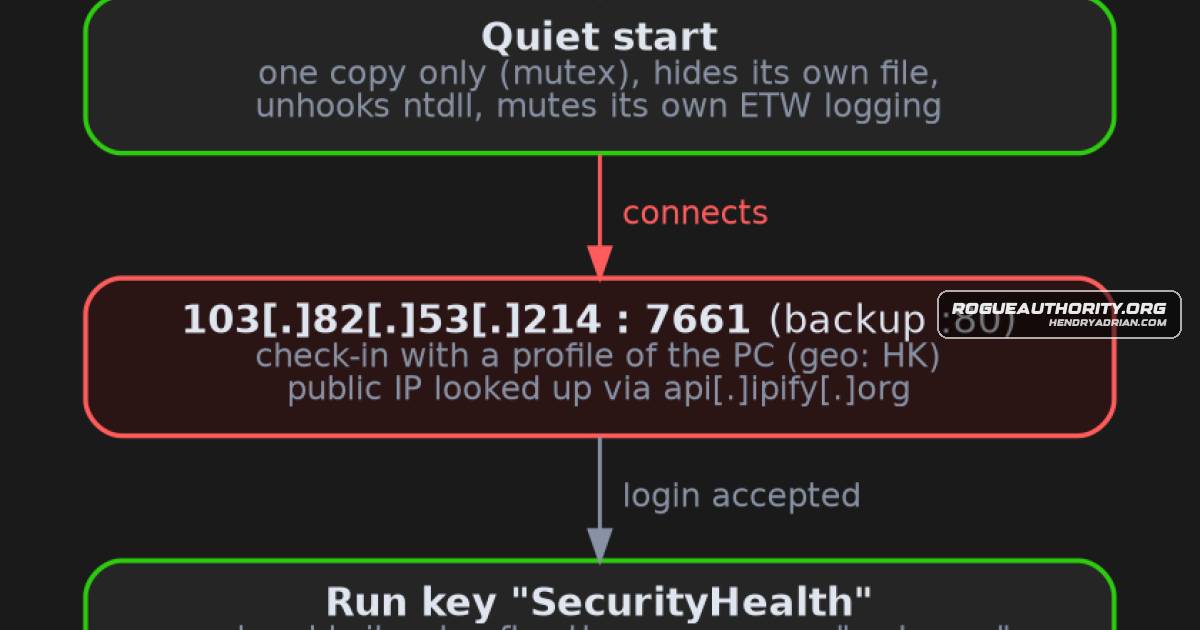
Signed Windows Security Health Service Impersonator Is a Gh0st RAT-Lineage Backdoor

Analysis found a backdoor impersonating Windows Security Health Service, signed with a valid certificate from an unrelated Chinese company. It profiled the infected PC, established persistence, and contacted a Hong Kong-geolocated server; its lineage is assessed with मध

Oct 16, 2026
Threat Research · opensourcemalware.com

GhostAction Adds a VS Code-Launched Credential Stealer and Persistent Remote Access

Researchers found GhostAction malware in 94 repositories. A hidden VS Code task launches a credential stealer, while a cron job enables remote commands every five minutes; the campaign also uses malicious GitHub Actions workflows.

Oct 16, 2026
Threat Research · thehackernews.com

PEERSTITCH Malware Uses FortiOS Flaw to Alter Tagged VPN Sessions

Unit 42 reports that attackers exploited FortiOS CVE-2025-61624 to deploy PEERSTITCH, a memory-resident implant that injects code into FortiOS daemons and alters handling of tagged VPN sessions.

Oct 16, 2026
Threat Research · stealthmole-intelligence-hub.blogspot.com

StealthMole Traces RockHavks’ Earlier Seller Accounts Across Underground Forums

StealthMole linked RockHavks to earlier underground-forum seller accounts through a persistent Session ID, reused listings and a shared typo. Telegram records trace one account’s changing identities, but RockHavks attribution and advertised dataset claims remain unsubst

Oct 16, 2026
Threat Research · huntress.com

Compromised ConnectWise Credentials Used to Access Microsoft 365 Tenants and Plant App Secrets

Huntress confirmed unauthorized Microsoft 365 access using compromised ConnectWise credentials. In two tenants, attackers granted an application Global Administrator and planted secrets in other apps. Data access remains uncertain.

Oct 16, 2026
Threat Research · jamf.com

Samsung Knox Kernel Use-After-Free Exposed an App-Reachable Path to Memory Corruption

CVE-2026-20971 was a use-after-free in Samsung’s PROCA driver. Researchers explained the race and demonstrated limited exploitation primitives; Samsung fixed the issue in its January 2026 security update.

Oct 16, 2026
Threat Research · recordedfuture.com

Recorded Future Traces TAG-217’s Preparations for South Korean Bank Attacks

Recorded Future says exposed infrastructure and logs traced TAG-217’s preparations to August 2026, revealing tools for cryptocurrency theft, Linux access, and mobile testing alongside AI use. The evidence does not show successful compromise in those earlier tests.

Oct 16, 2026
PreviousPage 10 of 100 Next
© 2026 cyber.hendryadrian.com