cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2499 articles

Threat Research · blog.sucuri.net

WordPress Casino-Spam Malware Uses Hidden Payloads and Reinfection Mechanisms

A technical investigation of WordPress casino-spam malware found payloads hidden in the database and a .dat file, redundant execution code in theme and plugin files, and a separate script that restores removed infection code.
Nov 7, 2025
Threat Research · huntress.com

Huntress Details Gootloader’s Return, WOFF2 Evasion and Rapid Domain Controller Compromise

Huntress observed three Gootloader infections since Oct. 27; two led to hands-on intrusions and Domain Controller compromise within 17 hours, with one partner-observed case under an hour. The loader uses WOFF2 glyph substitution and encrypted ZIP delivery.

Nov 5, 2025
Threat Research · hunt.io

Researchers Map Multilingual ZIP Phishing Campaigns Targeting Asian Organizations

Hunt.io researchers linked 28 Chinese-, English-, and Japanese-language phishing pages targeting organizations across Asia, finding shared templates, scripts, and ZIP/RAR lures themed around tax, finance, and government documents.

Oct 29, 2025
Threat Research · threatfabric.com

Herodotus Android Banking Trojan Mimics Human Typing to Evade Detection

Researchers describe Herodotus, an Android banking Trojan active in Italy and Brazil. It uses remote control, overlays and SMS theft, and randomizes text-entry delays to imitate human behavior and potentially evade fraud detection.

Oct 28, 2025
Threat Research · blog.talosintelligence.com

Cisco Talos Details Qilin Ransomware Tactics, from VPN Access to Network Encryption

Cisco Talos analyzes multiple 2025 Qilin incidents, detailing possible VPN access using exposed credentials, credential theft, cloud exfiltration, defense evasion, and ransomware deployment across Windows and virtualized environments.

Oct 27, 2025
Threat Research · huntress.com

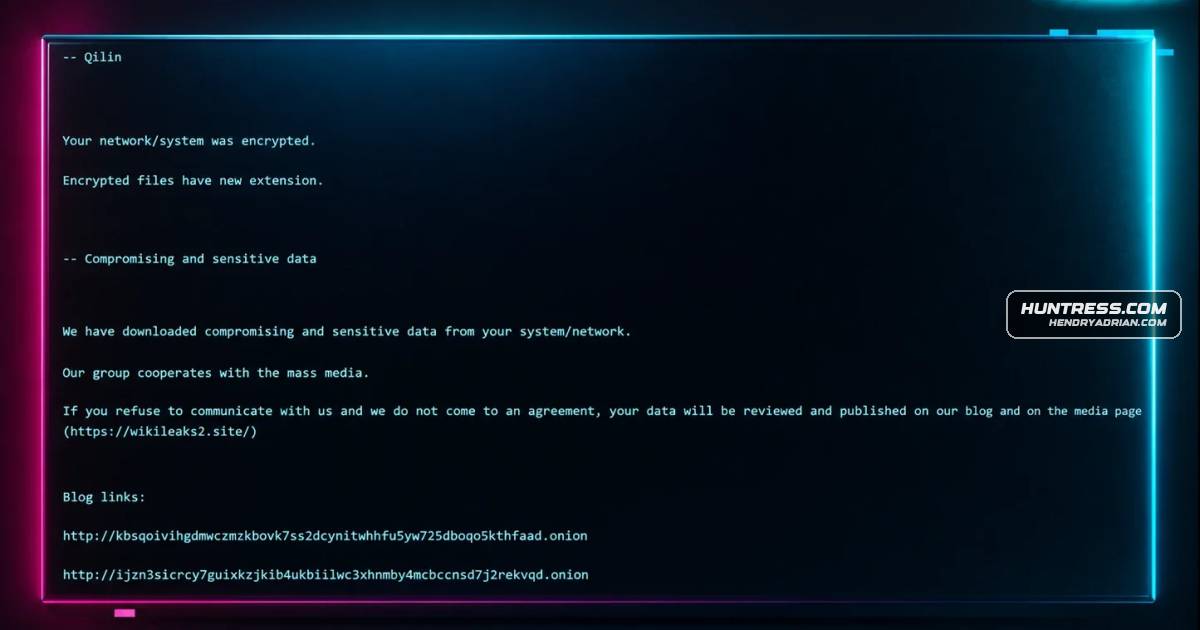
Huntress Reconstructs a Qilin Ransomware Attack from Limited Endpoint Evidence

Huntress analysts used Windows logs and compatibility records to reconstruct a Qilin ransomware incident despite post-incident, single-endpoint visibility, tracing rogue remote access, attempted payload execution, and ransom-note activity.

Oct 22, 2025
Threat Research · darktrace.com

Darktrace Links Citrix Intrusion at European Telecom to Salt Typhoon

Darktrace reports that attackers exploited CVE-2025-5777 to access a European telecom, deployed the SNAPPYBEE backdoor through DLL sideloading, and used multiple C2 channels. The activity was detected and remediated early; attribution to Salt Typhoon is assessed with “/

Oct 20, 2025
Threat Research · blog.talosintelligence.com

BeaverTail and OtterCookie Add Keylogging and Screenshot Capabilities

Cisco Talos details how a trojanized Chessfi Node.js application delivered merged BeaverTail and OtterCookie malware, including a new module that captures keystrokes and screenshots, and examines a possibly related malicious VS Code extension.

Oct 16, 2025
Threat Research · huntress.com

Huntress Details How Ransomware Operators Deploy Their Payloads

Huntress analysts describe ransomware deployment methods observed in incidents, including manual launches, remote network shares, PsExec-based tools, and Active Directory servers, and explain how monitoring can help detect activity.

Oct 16, 2025
Threat Research · hunt.io

Fake Homebrew Sites Deliver Odyssey Stealer and AMOS to macOS Users

Researchers detail a campaign targeting macOS users with fake software download sites that use clipboard-injected Terminal commands to install Odyssey Stealer or AMOS. They identified more than 85 related phishing domains and mapped shared infrastructure.

Oct 16, 2025
Threat Research · huntress.com

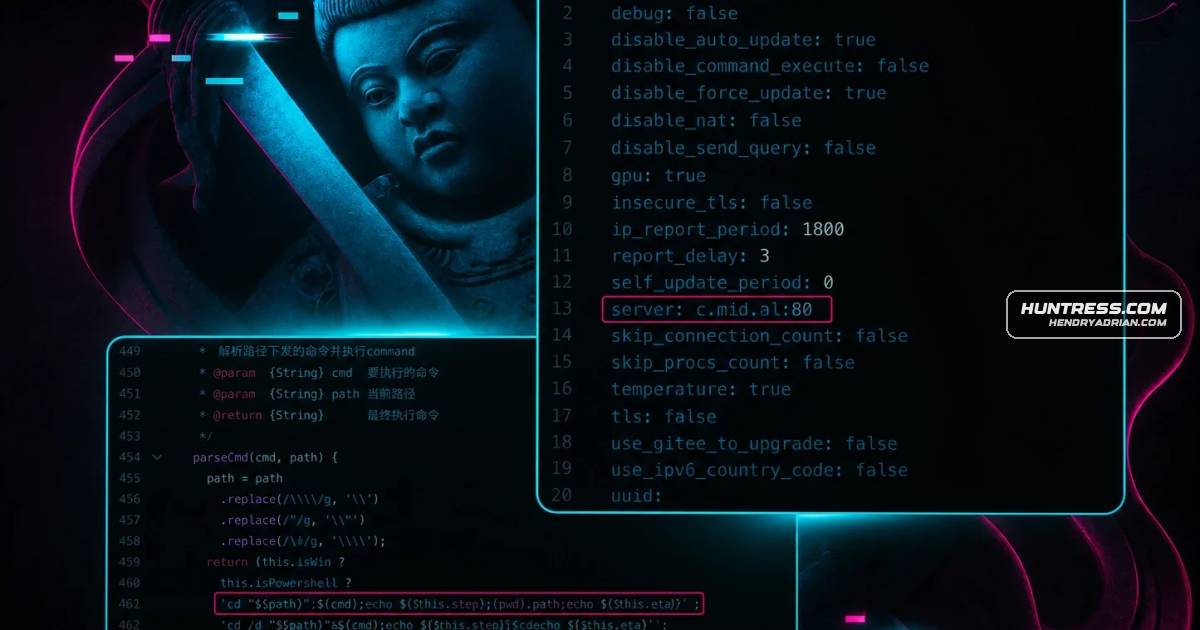
Huntress traces web intrusion using Nezha and Ghost RAT across 100+ potential victims

Huntress traced an August 2025 intrusion using exposed phpMyAdmin, MariaDB log poisoning, a web shell, Nezha and Ghost RAT across 100+ potential victims. A China-nexus attribution was later questioned by an unverified tip.

Oct 15, 2025
Threat Research · aquasec.com

Kaiji Malware Analysis Details Linux Persistence and Evasion Techniques

Aqua researchers analyzed a Kaiji infection on a weak-password SSH honeypot, documenting its DDoS and proxy capabilities, persistence and evasion methods, and campaign infrastructure, including a server with more than 70,000 collective malware downloads.

Oct 14, 2025
Threat Research · cloudsek.com

APT35-Linked Documents Detail Two RATs, Custom Webshells and Malware Operations

CloudSek analyzes documents it attributes to APT35/Charming Kitten, detailing two Windows RATs, custom ASP webshells, operational tooling, targeting claims, and behavioral detection guidance.

Oct 14, 2025
Threat Research · hunt.io

Researchers Map AdaptixC2 Capabilities and More Than 100 Active Servers

Hunt.io analyzes AdaptixC2’s beacon, evasion and pivoting features, and reports 102 active servers found through its telemetry, including 56 returning an AdaptixC2 HTTP header. The article shares hunting indicators and defensive measures.

Oct 9, 2025
Threat Research · volexity.com

China-Aligned UTA0388 Uses LLM-Assisted Phishing and GOVERSHELL Malware, Volexity Reports

Volexity details UTA0388’s multilingual spear-phishing campaigns, rapport-building tactics, and five GOVERSHELL backdoor variants, assessing with high confidence that the China-aligned actor used LLMs to support its operations.

Oct 8, 2025
Threat Research · cloudsek.com

Leaked Documents Reveal APT35’s Espionage Operations, Tooling and Victim Data

CloudSEK analyzes alleged internal APT35 documents describing phishing, rapid vulnerability exploitation, router manipulation, custom malware, EDR evasion, supply-chain attacks, and extensive data theft across government, legal, education, and other sectors.

Oct 7, 2025
Threat Research · blog.sucuri.net

WordPress Theme Injection Loads Malicious Scripts Across at Least 17 Websites

An injected function in a WordPress theme’s functions.php file fetched attacker-controlled JavaScript, enabling redirects and pop-ups. The researchers found the script loading on at least 17 websites and shared two indicators of compromise.

Oct 4, 2025
Threat Research · hunt.io

Hunt.io Details SideWinder Phishing and Malware Campaign Targeting South Asia

Hunt.io links extensive phishing infrastructure, credential-harvesting portals and malware staging to SideWinder activity targeting government, military and maritime organizations across South Asia.

Oct 1, 2025
Threat Research · threatfabric.com

Datzbro Android Trojan Uses Senior Travel Scams to Enable Device Takeover and Financial Fraud

ThreatFabric analyzed Datzbro, an Android Trojan distributed through fake senior-event promotions. Its remote control, overlays, keylogging, and credential theft capabilities can enable financial fraud; researchers also found a leaked C2 application and builder.

Sep 30, 2025
Threat Research · darktrace.com

Darktrace Details Vendor-Compromise Phishing Campaigns Using Trusted Email Relationships

Darktrace describes four vendor-compromise campaigns targeting one customer in two weeks, using trusted senders, hijacked email threads, and legitimate file-sharing services to deliver fake Microsoft login pages and steal credentials.

Sep 30, 2025
Threat Research · thedfirreport.com

Lunar Spider Intrusion Used Tax-Themed JavaScript to Maintain Access for Nearly Two Months

A DFIR investigation details a nearly two-month intrusion that began with a tax-themed JavaScript file and involved multiple malware families, credential theft, lateral movement, and data exfiltration. No ransomware deployment was observed.

Sep 29, 2025
Threat Research · huntress.com

ClickFix Variants Evolve Across Windows, macOS and Linux, Huntress Details Detection Clues

Huntress reports a 631% increase in ClickFix-related incidents over six months and explains ClickFix, FileFix, TerminalFix and DownloadFix, their execution traces, and telemetry chokepoints defenders can monitor.

Sep 29, 2025
Threat Research · global.ptsecurity.com

Researchers Detail Goffee’s Malware and Stealthy Attacks on Russian Organizations

Positive Technologies researchers analyzed Goffee attacks on Russian organizations, detailing new malware and tools, including the Sauropsida Linux rootkit, and the group’s phishing, tunneling, evasion, and infrastructure techniques.

Sep 29, 2025
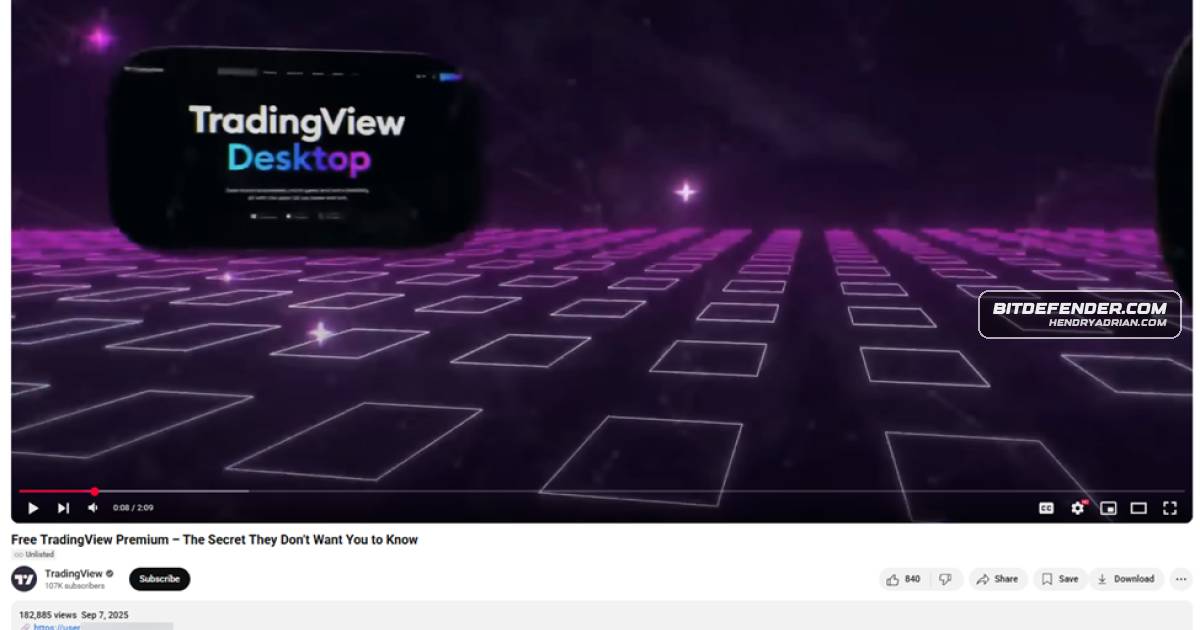
Threat Research · bitdefender.com

TradingView Impersonation Ads Spread Stealer Malware Through Google and YouTube

Bitdefender researchers detail a campaign using hijacked Google and YouTube accounts and TradingView-themed ads to deliver malware. The infection chain leads to a stealer with credential theft, keylogging, and remote-access capabilities.

Sep 25, 2025
PreviousPage 88 of 105 Next
© 2026 cyber.hendryadrian.com