Investigation Details Intrusion Targeting 12 Omani Government Entities, With 26,000 Records Extracted
Summary
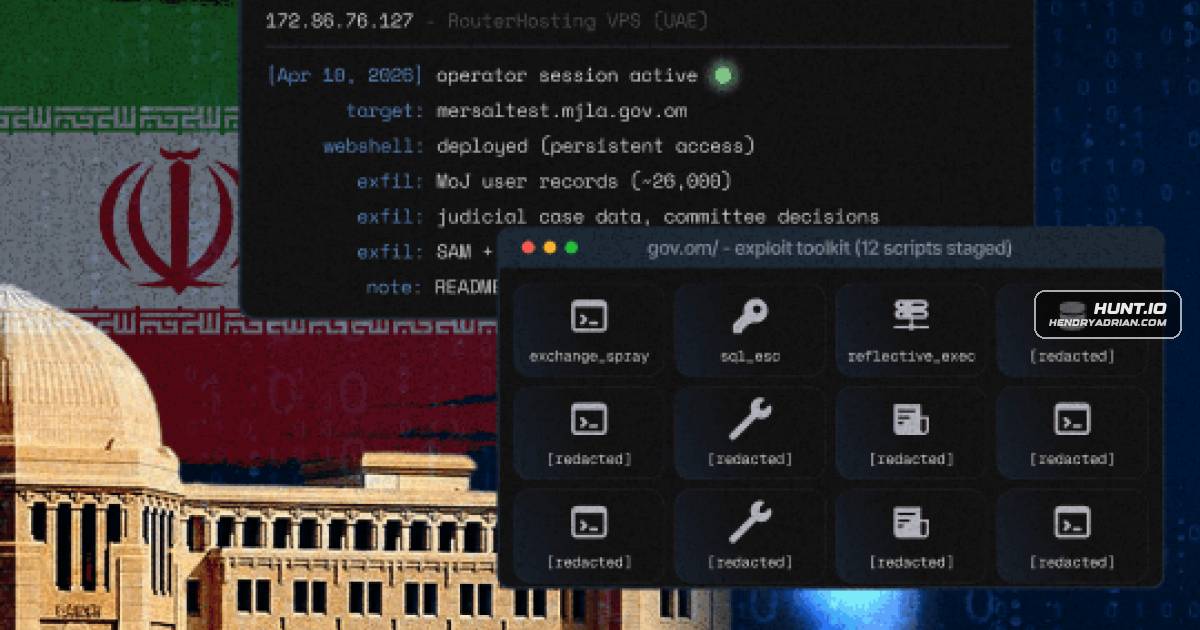
An exposed server revealed tooling and logs from an intrusion targeting Omani government entities. Evidence shows access to the Ministry of Justice and Legal Affairs and extraction of more than 26,000 user records, judicial data, and registry hives.
Key points
- An open directory on a VPS exposed campaign files, C2 code, session logs, and stolen data.
- Recovered scripts mapped activity against 12 Omani government entities; confirmed C2 sessions and data extraction centered on the Ministry of Justice and Legal Affairs.
- A webshell provided command execution. DNN vulnerability scripts suggest CVE-2025-32372 as a possible access route, but the report says this is unconfirmed.
- The operator extracted 26,596 DNN user records, judicial and committee data, and Windows SAM and SYSTEM registry hives.
- The toolkit included Python C2 servers, a PowerShell beacon, Chisel tunneling, and GodPotato privilege escalation; Defender blocked an attempted scheduled-task persistence method.
- Logs show operator sessions on April 10, 2026. Tooling and targeting overlap with Iranian-nexus groups, but the researchers did not attribute the campaign to a specific group.
Article Details
- Attack Vectors
- Password brute-force attempts targeted government portals; recovered tooling also included Exchange password spraying and MSSQL brute-forcing.
- ProxyShell exploit scripts targeted two government mail servers that appeared vulnerable. The recovered files did not establish successful exploitation.
- Scripts targeting a DotNetNuke SSRF vulnerability suggest a possible initial-access path, but the article could not confirm it.
- A deployed ASPX webshell provided command execution inside the Ministry of Justice and Legal Affairs network.
- Recovered scripts covered SQL injection, database extraction, Oracle APEX/ORDS attacks, Citrix exploitation, portal enumeration, authentication reconnaissance, and national ID IDOR vulnerabilities.
- Post-compromise tooling supported privilege escalation, reflective payload execution, credential extraction, HTTP command-and-control, tunneling, and data exfiltration.
- Defensive Notes
- Defender blocked creation of a persistence task named MicrosoftEdgeUpdate; the operator did not retry that task.
- A separate recovered script attempted to forcibly disable antivirus, but the article did not establish that it succeeded.
- An earlier privilege-escalation execution approach was reportedly flagged, after which a subsequent script adopted reflective in-memory loading.
- The exposed C2 server logged all inbound POST requests, including scanner and opportunistic exploitation traffic; those requests should not automatically be treated as victim beacon activity.
- The article did not confirm a connection between every neighboring infrastructure indicator and the government intrusion, and did not attribute the operation to a specific named group.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | brnettlix[.]com | Domain listed in the surrounding infrastructure IOC cluster at 172.86.76[.]124; intrusion linkage is unconfirmed. |
| DOMAIN | brttfrixx[.]com | Domain listed in the surrounding infrastructure IOC cluster at 172.86.76[.]124; intrusion linkage is unconfirmed. |
| DOMAIN | identificara[.]com | Domain listed in the surrounding infrastructure IOC cluster at 172.86.76[.]124; intrusion linkage is unconfirmed. |
| DOMAIN | realprimefix[.]com | Domain listed in the surrounding infrastructure IOC cluster at 172.86.76[.]124; intrusion linkage is unconfirmed. |
| DOMAIN | regorixa[.]com | Domain listed in the neighboring infrastructure IOC cluster associated with a supposed USDT investment platform; intrusion linkage is unconfirmed. |
| DOMAIN | suanefllix[.]com | Domain listed in the surrounding infrastructure IOC cluster at 172.86.76[.]124; intrusion linkage is unconfirmed. |
| DOMAIN | vaermb[.]com | Infrastructure domain containing the C2 hostname and neighboring dubai-# hosts; links between all neighboring hosts and the intrusion remain unconfirmed. |
| HOSTNAME | dubai-1[.]vaermb[.]com | Hostname listed in the neighboring infrastructure IOC cluster, resolving to 172.86.76[.]101; intrusion linkage is unconfirmed. |
| HOSTNAME | dubai-10[.]vaermb[.]com | Domain resolving to the exposed staging and C2 server at 172.86.76[.]127. |
| HOSTNAME | dubai-2[.]vaermb[.]com | Hostname listed in the neighboring infrastructure IOC cluster, resolving to 172.86.76[.]94; intrusion linkage is unconfirmed. |
| HOSTNAME | dubai-3[.]vaermb[.]com | Hostname listed in the neighboring infrastructure IOC cluster, resolving to 172.86.76[.]108; intrusion linkage is unconfirmed. |
| HOSTNAME | dubai-4[.]vaermb[.]com | Hostname listed in the neighboring infrastructure IOC cluster, resolving to 172.86.76[.]112; intrusion linkage is unconfirmed. |
| HOSTNAME | dubai-5[.]vaermb[.]com | Hostname listed in the neighboring infrastructure IOC cluster, resolving to 172.86.76[.]120; intrusion linkage is unconfirmed. |
| HOSTNAME | dubai-6[.]vaermb[.]com | Hostname listed in the neighboring infrastructure IOC cluster, resolving to 172.86.76[.]121; intrusion linkage is unconfirmed. |
| HOSTNAME | dubai-7[.]vaermb[.]com | Hostname listed in the neighboring infrastructure IOC cluster, resolving to 172.86.76[.]124; intrusion linkage is unconfirmed. |
| HOSTNAME | dubai-8[.]vaermb[.]com | Hostname listed in the neighboring infrastructure IOC cluster, resolving to 172.86.76[.]129; intrusion linkage is unconfirmed. |
| HOSTNAME | dubai-9[.]vaermb[.]com | Hostname listed in the neighboring infrastructure IOC cluster, resolving to 172.86.76[.]130; intrusion linkage is unconfirmed. |
| HOSTNAME | myjitsi[.]exceptionnotfound[.]ir | Hostname listed in the surrounding infrastructure IOC cluster at 172.86.76[.]108; intrusion linkage is unconfirmed. |
| HOSTNAME | myjitsi[.]mrnajafipour[.]ir | Associated infrastructure hostname serving a Radio Zamaneh replica; no malicious page code was identified and intrusion linkage is unconfirmed. |
| HOSTNAME | price[.]exceptionnotfound[.]ir | Hostname listed in the associated infrastructure IOC cluster at 45.59.114[.]60; intrusion linkage is unconfirmed. |
| HOSTNAME | s5[.]sideliner[.]ir | Hostname listed in the surrounding infrastructure IOC cluster at 172.86.76[.]112; intrusion linkage is unconfirmed. |
| HOSTNAME | shop[.]exceptionnotfound[.]ir | Hostname listed in the associated infrastructure IOC cluster at 45.59.114[.]60; intrusion linkage is unconfirmed. |
| HOSTNAME | tools[.]exceptionnotfound[.]ir | Cloudflare-hosted hostname explicitly listed in the surrounding infrastructure IOC cluster; intrusion linkage is unconfirmed. |
| IPV4 | 104[.]21[.]27[.]95 | Cloudflare IP explicitly listed for tools.exceptionnotfound[.]ir in the surrounding infrastructure IOC table; intrusion linkage and exclusive attacker control are unconfirmed. |
| IPV4 | 172[.]67[.]142[.]35 | Cloudflare IP explicitly listed for tools.exceptionnotfound[.]ir in the surrounding infrastructure IOC table; intrusion linkage and exclusive attacker control are unconfirmed. |
| IPV4 | 172[.]86[.]76[.]101 | Research indicator in the neighboring infrastructure cluster; hosted a #FreeIran conduit page and a Regorixa investment landing page. Intrusion linkage is unconfirmed. |
| IPV4 | 172[.]86[.]76[.]108 | IP listed in the neighboring infrastructure IOC cluster, hosting dubai-3 and an .ir hostname; intrusion linkage is unconfirmed. |
| IPV4 | 172[.]86[.]76[.]112 | IP listed in the neighboring infrastructure IOC cluster, hosting dubai-4 and s5.sideliner[.]ir; intrusion linkage is unconfirmed. |
| IPV4 | 172[.]86[.]76[.]120 | IP listed in the neighboring dubai-# infrastructure IOC cluster; intrusion linkage is unconfirmed. |
| IPV4 | 172[.]86[.]76[.]121 | IP listed in the neighboring dubai-# infrastructure IOC cluster; intrusion linkage is unconfirmed. |
| IPV4 | 172[.]86[.]76[.]124 | IP listed in the neighboring infrastructure IOC cluster with dubai-7 and several additional domains; intrusion linkage is unconfirmed. |
| IPV4 | 172[.]86[.]76[.]127 | Operator staging and C2 server exposing attack scripts, payloads, session logs, and exfiltrated government data. |
| IPV4 | 172[.]86[.]76[.]129 | IP listed in the neighboring dubai-# infrastructure IOC cluster; intrusion linkage is unconfirmed. |
| IPV4 | 172[.]86[.]76[.]130 | IP listed in the neighboring dubai-# infrastructure IOC cluster; intrusion linkage is unconfirmed. |
| IPV4 | 172[.]86[.]76[.]94 | IP listed in the neighboring dubai-# infrastructure IOC cluster; intrusion linkage is unconfirmed. |
| IPV4 | 45[.]59[.]114[.]60 | Associated infrastructure IP hosting a Radio Zamaneh replica and .ir subdomains; its connection to the government intrusion is unconfirmed. |
| SHA256 | ecc3611f7dcbaa53acf44e67de2f10d78a26e03b3c77ba28bbd3ee16b2e66437 | TLS certificate fingerprint used to connect the associated Swiss server to the UAE infrastructure cluster; not a malware hash. |
MITRE ATT&CK
T1001.003 · Protocol or Service ImpersonationBeacon exfiltration traffic spoofs a Chrome User-Agent, although polling retains a native PowerShell WebClient identifier.T1003.002 · Security Account ManagerThe operator extracted SAM and SYSTEM registry hives from the victim environment.T1016 · System Network Configuration DiscoveryThe webshell defaults to ipconfig to return the compromised host's network configuration.T1033 · System Owner/User DiscoveryThe webshell defaults to whoami /all, and beacon startup callbacks report the victim username.T1041 · Exfiltration Over C2 ChannelThe HTTP C2 environment supported exfiltration, and extracted government data was recovered from its loot and ejustice directories.T1053.005 · Scheduled TaskThe operator attempted to create a scheduled task named MicrosoftEdgeUpdate for persistence; Defender blocked it.T1059.001 · PowerShellPowerShell extracted database schema and user-table data, and a PowerShell beacon polled the HTTP C2 server.T1059.003 · Windows Command ShellThe recovered hc2.aspx webshell executes supplied commands through cmd.exe /c.T1071.001 · Web ProtocolsThe PowerShell beacon polls an HTTP C2 listener every 30 seconds for commands and returns command results.T1074.001 · Local Data StagingExtracted registry hives were staged in C:\Windows\Temp during the recorded operator session.T1082 · System Information DiscoveryThe webshell defaults to hostname, and beacon startup callbacks report the victim hostname.T1105 · Ingress Tool TransferGodPotato is stored in the C2 server's payload directory and retrieved at runtime for execution in the victim environment.T1110.001 · Password GuessingRecovered activity included password brute-force attempts against the eVisa and State Audit Institution portals and MSSQL brute-forcing scripts.T1110.002 · Password CrackingThe operator extracted stored credentials from aspnet_Membership and attempted to crack the hashes offline.T1110.003 · Password SprayingThe government-targeting script collection included Exchange password spraying.T1132.001 · Standard EncodingThe beacon base64-encodes results and returns them in 1,500-character chunks.T1134.001 · Token Impersonation/TheftThe privilege-escalation script runs GodPotato to abuse SeImpersonatePrivilege.T1190 · Exploit Public-Facing ApplicationRecovered scripts attempted ProxyShell exploitation against government mail servers and targeted a DotNetNuke SSRF flaw; successful initial access through these exploits was not confirmed.T1213 · Data from Information RepositoriesThe operator enumerated and extracted application database records, including judicial data, committee decisions, identity information, and more than 26,000 user records.T1505.003 · Web Shellhealth_check_t.aspx provided persistent command execution inside the Ministry of Justice network; hc2.aspx was recovered from the C2 server.T1562.001 · Disable or Modify ToolsA separate recovered script attempted to forcibly disable antivirus on the compromised system; success was not established.T1620 · Reflective Code LoadingA subsequent privilege-escalation script uses reflective loading to execute the payload in memory rather than on disk.
CVE
CVE-2021-31207CVE-2021-34473mail.rfo.gov[.]om Royal Fleet of Oman - VIP air transport ProxyShell exploitation (CVE-2021-34473/34523/31207)CVE-2021-34523CVE-2025-32372/Portals/0/, DotNetNuke's (DNN) default file storage directory. Additional scripts targeting CVE-2025-32372, an SSRF flaw in DNN versions before 9.13.8, point to a likely initial access path, though this cannot be
Threat Actors
Mango SandstormExplicitly identified as an alternate tracking name for MuddyWater, whose tooling overlaps with the reported activity. The article does not attribute this intrusion to it.MuddyWaterNamed as a MOIS-linked group using Chisel, ProxyShell, and PowerShell-heavy tooling in similar regional operations; also tracked as Mango Sandstorm. Attribution of this intrusion remains unconfirmed.OilRigExplicitly identified as an alternate tracking name for APT34, also tracked as Crambus. The article does not attribute this intrusion to it.
Vendors
Cloudflare172.67.142[.]35 tools.exceptionnotfound[.]ir CloudflareFortinetover 50 Python scripts covering a range of platforms and vulnerabilities; WAF bypass techniques, Fortinet appliances, Joomla installations, MSSQL brute-forcing, Oracle APEX and ORDS backends, Spring BootNameSilodubai-10.vaermb[.]com, registered in May 2025 using NameSilo. The naming pattern suggests additional infrastructure, which we'll return to later in this post.RouterHostingto keep their staging server out of view. This one did not. An open directory on 172.86.76[.]127, a RouterHosting VPS in the United Arab Emirates, surfaced an active intrusion campaign against the Omani government,
Products
CitrixRoyal Court Affairs Citrix exploitation, authentication reconnaissance, and MOF-based executionDefenderto further establish persistence via a scheduled task named MicrosoftEdgeUpdate, but it was blocked by Defender and never retried. It should be noted that a separate script on the server showed an attempt toDotNetNuke/Portals/0/, DotNetNuke's (DNN) default file storage directory. Additional scripts targeting CVE-2025-32372, an SSRF flaw in DNN versions before 9.13.8, point to a likely initial access path, though this cannot beExchangeA dedicated gov[.]om folder included 12 exploit scripts, including Exchange spraying, SQL server escalation, and a reflective execution variant.Joomlascripts covering a range of platforms and vulnerabilities; WAF bypass techniques, Fortinet appliances, Joomla installations, MSSQL brute-forcing, Oracle APEX and ORDS backends, Spring Boot Actuator endpoints, andOracle APEXWAF bypass techniques, Fortinet appliances, Joomla installations, MSSQL brute-forcing, Oracle APEX and ORDS backends, Spring Boot Actuator endpoints, and national ID Insecure Direct Object ReferenceORDSWAF bypass techniques, Fortinet appliances, Joomla installations, MSSQL brute-forcing, Oracle APEX and ORDS backends, Spring Boot Actuator endpoints, and national ID Insecure Direct Object Reference (IDOR)PowerShellcredentials and personal information. Database schema information and user tables were extracted via PowerShell and posted to the loot/ directory.SimpleSAMLphp/ITAPortal_AR/, suggesting a common codebase across both organizations. MJLA's SimpleSAMLphp identity provider, if configured for federated authentication within the same portal infrastructure, represents a single pointSpring Boot ActuatorFortinet appliances, Joomla installations, MSSQL brute-forcing, Oracle APEX and ORDS backends, Spring Boot Actuator endpoints, and national ID Insecure Direct Object Reference (IDOR) vulnerabilities.
Tools
AttackCaptureThe server at 172.86.76[.]127 was first observed by AttackCapture scans on April 8, 2026, on port 8000. A second directory, served on port 8002, was captured two days later on April 10th. When combined, both findingsChisel/payloads folder was tagged as containing components for Chisel, a tool commonly used to establish encrypted tunnels through firewalls.GodPotatogp_v6_exec.py runs GodPotato, a Windows privilege escalation tool that abuses thePsiphontwo services under separate ports: a #FreeIran branded conduit status page linking to a legitimate Psiphon GitHub repo on port 80, and a landing page for Regorixa, a supposed subscription-based USDT investment
Countries
IranOn this newly identified server is a replica of Radio Zamaneh, an Amsterdam-based Persian-language media organization serving those in Iran and beyond seeking alternative journalism. The page is served fromOmanOman is a familiar target of cyberespionage and network attacks. In 2025, an Iranian-aligned group connected to the Ministry of Intelligence and Security (MOIS) compromised a mailbox at Oman's Ministry of ForeignSwitzerland45.59.114[.]60) based in Switzerland, that also hosts a Let's Encrypt certificate (SHA-256: ECC3611F7DCBAA53ACF44E67DE2F10D78A26E03B3C77BA28BBD3EE16B2E66437) with a common subject common name linking to the UAE cluster.United Arab Emiratesout of view. This one did not. An open directory on 172.86.76[.]127, a RouterHosting VPS in the United Arab Emirates, surfaced an active intrusion campaign against the Omani government, with the toolkit, C2 code,