
Silver Fox Uses Modified RustSL to Deliver ValleyRAT and ABCDoor
Summary
Researchers attribute tax-themed phishing campaigns in India and Russia to Silver Fox, detailing modified RustSL loaders, ValleyRAT delivery and the ABCDoor Python backdoor, which they traced in the group's arsenal to at least late 2024.
Key points
- Researchers attributed December 2025 and January 2026 tax-themed phishing campaigns targeting organizations in India and Russia to Silver Fox; more than 1,600 malicious emails were recorded in one wave.
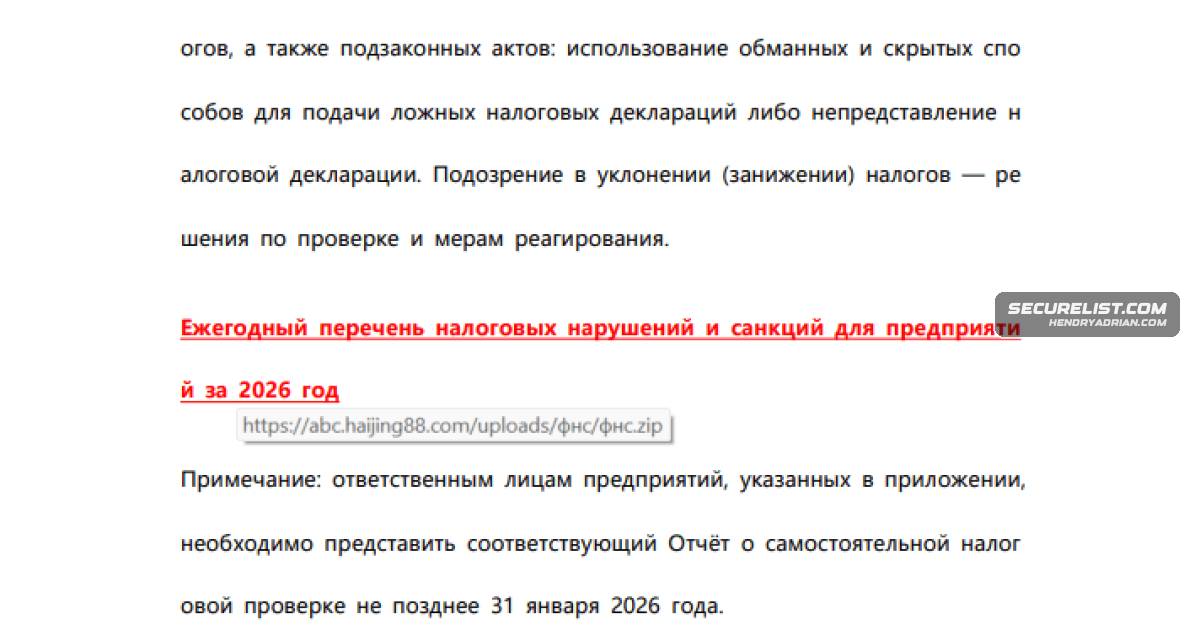
- Emails used malicious attachments or PDFs linking to attacker-controlled downloads; archives contained loaders disguised as documents or other files.
- Silver Fox modified RustSL with custom XOR-based payload unpacking and environment and country checks; one loader also used Phantom Persistence to interfere with shutdown and trigger a reboot.
- The loader's shellcode delivered ValleyRAT (Winos 4.0); newly observed ValleyRAT plugins then downloaded an archive containing ABCDoor and a bundled Python environment.
- ABCDoor is a Cython-compiled Python backdoor that communicates with command-and-control servers over HTTPS and Socket.IO and supports screen broadcasting, file operations, clipboard collection, and remote input.
- ABCDoor establishes persistence through a registry Run key and a scheduled task; researchers traced its development to late 2024 and described changes to its delivery methods through 2025.
Article Details
- Attack Vectors
- Tax-themed phishing emails impersonated tax authorities and delivered malicious archives as attachments or linked to archives through PDFs.
- Modified RustSL loaders unpacked encrypted payloads and downloaded ValleyRAT modules and ABCDoor archives from attacker infrastructure.
- Silver Fox used geofencing checks to restrict loader execution by country and used multiple payload-placement methods, including embedded payloads, hosted images, and files in the same archive as the loader.
- ABCDoor established persistence with an HKCU Run key and a scheduled task named AppClient that runs every minute.
- ABCDoor communicated with its C2 over HTTPS using Socket.IO and could collect and broadcast victims’ screens.
- Defensive Notes
- Verify emails and PDFs that purport to be tax-authority communications, and provide regular employee security-awareness training.
- Monitor for ABCDoor artifacts, including the AppClient Run-key value and scheduled task, the HKCU:SoftwareCarEmu registry entries, and the reported applogs files.
- Use a comprehensive approach to infrastructure security; the report describes segmented, stage-specific infrastructure and multiple payload-delivery methods.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | abc[.]3mkorealtd[.]com | Listed as ABCDoor C2 infrastructure. |
| DOMAIN | abc[.]doublemobile[.]com | Listed as ABCDoor C2 infrastructure. |
| DOMAIN | abc[.]fetish-friends[.]com | Reported ABCDoor staging and C2 domain. |
| DOMAIN | abc[.]ilptour[.]com | Listed as ABCDoor C2 infrastructure. |
| DOMAIN | abc[.]petitechanson[.]com | Listed as ABCDoor C2 infrastructure. |
| DOMAIN | abc[.]woopami[.]com | Listed as ABCDoor C2 infrastructure. |
| DOMAIN | vnc[.]kcii2[.]com | Attacker server contacted by malicious remote-control installers. |
| IPV4 | 108[.]187[.]37[.]85 | Listed ValleyRAT C2 address. |
| IPV4 | 108[.]187[.]42[.]63 | Listed ValleyRAT C2 address. |
| IPV4 | 207[.]56[.]138[.]28 | ValleyRAT C2 address found in the malware configuration. |
| IPV4 | 45[.]118[.]133[.]203 | Listed ABCDoor C2 address; the article gives port 5000. |
| MD5 | 04194f8ddd0518fd8005f0e87ae96335 | Malicious C++ stager used to download a loader for ABCDoor. |
| MD5 | 043e457726f1bbb6046cb0c9869dbd7d | Malicious SFX archive containing the ABCDoor JavaScript loader. |
| MD5 | 11705121f64fa36f1e9d7e59867b0724 | Malicious Go stager used to launch a script that downloads ABCDoor. |
| MD5 | 13669b8f2bd0af53a3fe9ac0490499e5 | Identified ABCDoor .pyd backdoor sample. |
| MD5 | 2b92e125184469a0c3740abcaa10350c | Malicious SFX archive containing the ABCDoor JavaScript loader. |
| MD5 | 2c5a1dd4cb53287fe0ed14e0b7b7b1b7 | RustSL loader sample reported to implement Phantom Persistence. |
| MD5 | 4a5195a38a458cdd2c1b5ab13af3b393 | ValleyRAT plugin sample that downloads the ABCDoor archive. |
| MD5 | 5b998a5bc5ad1c550564294034d4a62c | Earliest identified ABCDoor backdoor sample. |
| MD5 | 6495c409b59deb72cfcb2b2da983b3bb | Malicious ZIP archive containing an SFX archive and ABCDoor JavaScript loader. |
| MD5 | e6362a81991323e198a463a8ce255533 | RustSL loader sample reported with Japan added to its execution country list. |
| MD5 | e66bae6e8621db2a835fa6721c3e5bbe | ValleyRAT plugin sample that downloads the ABCDoor archive. |
| URL | hxxp[:]//154[.]82[.]81[.]205/YD20251001143052.zip | Malicious ABCDoor archive downloaded by a ValleyRAT plugin. |
| URL | hxxp[:]//154[.]82[.]81[.]205/YN20250923193706.zip | Malicious ABCDoor archive downloaded by a ValleyRAT plugin. |
| URL | hxxps[:]//abc[.]fetish-friends[.]com/setup/install | Malicious remote PowerShell script URL used by a Go stager. |
| URL | hxxps[:]//abc[.]fetish-friends[.]com/uploads/appclient.zip | Malicious ABCDoor archive download URL used by a stager. |
| URL | hxxps[:]//mcagov[.]cc/download.php?type=exe | Malicious loader download URL used by a C++ stager. |
| URL | hxxps[:]//roldco[.]com/api/download/c51bbd17-ef08-4d6c-ab4c-d7bf49483dd6 | Malicious payload download URL reached through a TinyURL redirect. |
| URL | hxxps[:]//sudsmama[.]com/api/download/c8ea0a2c-42c2-4159-9337-ee774ed5e7cb | Malicious payload download URL reached through a TinyURL redirect. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationRustSL payloads used encryption, XOR-based decryption, optional encodings, string obfuscation, and junk instructions.T1053.005 · Scheduled TaskABCDoor created an AppClient scheduled task configured to run every minute.T1059.001 · PowerShellPowerShell was used to download payloads and to execute ABCDoor update operations.T1059.006 · PythonThe backdoor was launched as a Python module using pythonw.exe with the argument -m appclient.T1071.001 · Web ProtocolsABCDoor communicated with its C2 over HTTPS using Socket.IO.T1105 · Ingress Tool TransferLoaders and ValleyRAT plugins downloaded additional payloads and archives from attacker servers using methods including InternetReadFile, URLDownloadToFile, PowerShell, and curl.T1113 · Screen CaptureABCDoor used bundled ffmpeg and Desktop Duplication API functions to capture and broadcast victims’ screens.T1547 · Boot or Logon Autostart ExecutionA RustSL sample intercepted shutdown, aborted the shutdown sequence, and restarted the system under the guise of a malware update to achieve persistence.T1547.001 · Registry Run Keys / Startup FolderABCDoor added an AppClient value to the HKCU Run key to launch its Python module automatically.T1566.001 · Spearphishing AttachmentTax-themed emails carried malicious archives, including ITD.-.rar containing the RustSL loader.T1566.002 · Spearphishing LinkPhishing PDFs contained clickable links to attacker-controlled archive downloads.
Threat Actors
Malware
ABCDoormodified RustSL loaders to deliver the ValleyRAT backdoor and a newly documented Python backdoor named ABCDoor.ValleyRATorganizations in India, Russia and other countries, using modified RustSL loaders to deliver the ValleyRAT backdoor and a newly documented Python backdoor named ABCDoor.Winos 4.0Attackers used a customized RustSL loader (Silver Fox RustSL) that unpacks an encrypted payload (shellcode) which then downloads and launches the ValleyRAT (Winos 4.0) backdoor.
Vendors
Products
FFmpegC2, implements persistence via HKCU Run key and a scheduled task, supports screen broadcasting via ffmpeg (DDA), and includes update/self-delete capabilities.NodeJSThe run_direct.ps1 script checked for the presence of NodeJS in the standard directory on the victim’s computer (%USERPROFILE%.nodenode.exe).Pythonother countries, using modified RustSL loaders to deliver the ValleyRAT backdoor and a newly documented Python backdoor named ABCDoor.Tailscale VPNThis path was chosen intentionally: it corresponds to the legitimate utility Tailscale (a mesh VPN service based on the WireGuard protocol that connects devices into a single private network).
Tools
Countries
CambodiaIn customized Silver Fox loaders built prior to January 19, 2026, this list included India, Indonesia, South Africa, Russia, and Cambodia.Indiathrough early 2026 the Silver Fox threat group ran tax-themed phishing campaigns against organizations in India, Russia and other countries, using modified RustSL loaders to deliver the ValleyRAT backdoor and a newlyIndonesiaIn customized Silver Fox loaders built prior to January 19, 2026, this list included India, Indonesia, South Africa, Russia, and Cambodia.JapanCampaigns impersonated tax authorities (India, Russia, Japan) via emails and PDFs that either embedded malicious code or linked to attacker-controlled downloads, resulting in over 1,600 malicious emails recorded in oneRussiaearly 2026 the Silver Fox threat group ran tax-themed phishing campaigns against organizations in India, Russia and other countries, using modified RustSL loaders to deliver the ValleyRAT backdoor and a newlySouth AfricaIn customized Silver Fox loaders built prior to January 19, 2026, this list included India, Indonesia, South Africa, Russia, and Cambodia.
Industries
ConsultingThe campaign impacted organizations across the industrial, consulting, retail, and transportation sectors, with over 1600 malicious emails recorded between early January and early February.IndustrialThe campaign impacted organizations across the industrial, consulting, retail, and transportation sectors, with over 1600 malicious emails recorded between early January and early February.RetailThe campaign impacted organizations across the industrial, consulting, retail, and transportation sectors, with over 1600 malicious emails recorded between early January and early February.TransportationThe campaign impacted organizations across the industrial, consulting, retail, and transportation sectors, with over 1600 malicious emails recorded between early January and early February.