
ConsentFix v3 Automates OAuth Phishing Against Azure Accounts
Summary
ConsentFix v3 automates OAuth authorization-code phishing using pre-consented Microsoft apps and Pipedream to capture refresh tokens; the article says the variant's uptake among cybercriminals remains unclear.
Key points
- The technique targets pre-trusted Microsoft first-party apps and tricks victims into returning an OAuth authorization code from a localhost URL.
- Attackers reportedly verify Azure tenant IDs and collect employee names, roles, and email addresses for personalized phishing.
- Phishing pages hosted on Cloudflare Pages mimic Microsoft/Azure login flows; attackers may embed links in DocSend-hosted PDFs.
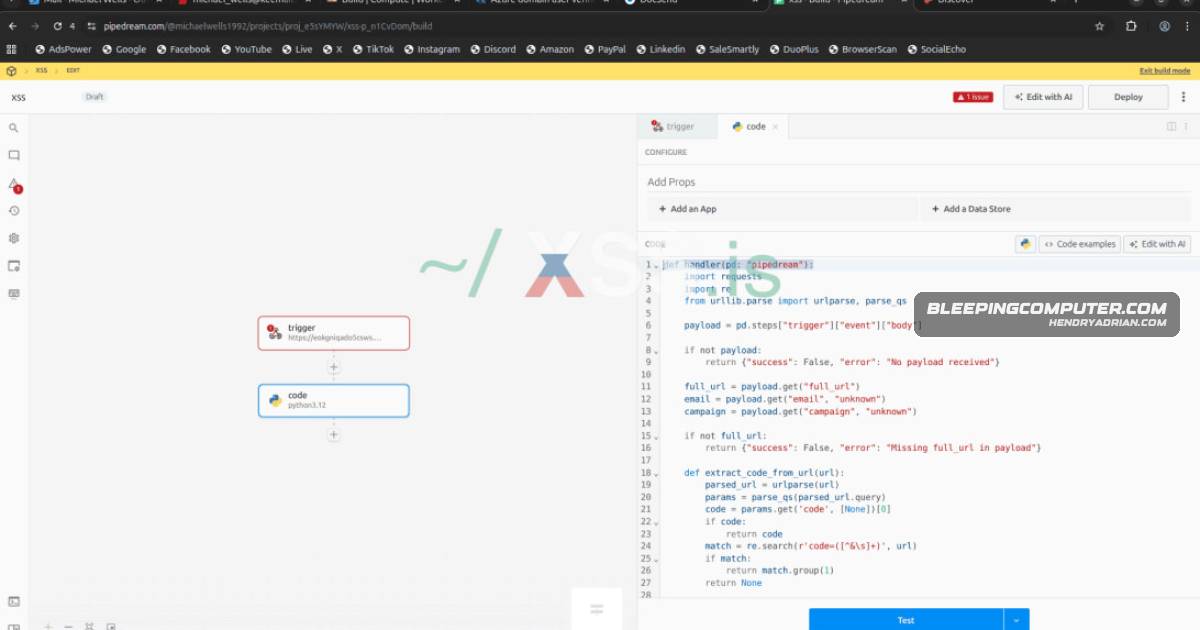
- Pipedream receives captured authorization codes and automates their exchange for refresh tokens, which it also collects.
- Tokens can be imported into Specter Portal to access account resources such as email and files, subject to token permissions.
- Push Security says its testing used personal Microsoft accounts, so impact in organizational tenants may vary with permissions, services, and settings.
- Suggested mitigations include token binding to trusted devices, behavioral detection, and app-authentication restrictions; the article says ConsentFix v3's criminal uptake is unclear.
Article Details
- Attack Vectors
- ConsentFix v3 uses personalized phishing pages hosted on Cloudflare Pages to initiate a real Microsoft OAuth flow. Victims are tricked into pasting or dragging a localhost URL containing an authorization code back into the page.
- Phishing emails use harvested employee names, roles, and email addresses, with malicious links embedded in a PDF hosted on DocSend.
- A Pipedream webhook collects the submitted authorization code; automation exchanges it for refresh tokens, which are then imported into Specter Portal to access resources available to the compromised account.
- Defensive Notes
- Apply token binding to trusted devices.
- Set up behavioral detection rules.
- Apply app authentication restrictions.
MITRE ATT&CK
T1204.001 · Malicious LinkVictims interact with the phishing page and are tricked into pasting or dragging a localhost URL containing an OAuth authorization code.T1526 · Cloud Service DiscoveryThe reported flow checks for valid tenant IDs to verify Azure's presence in the target environment.T1528 · Steal Application Access TokenThe Pipedream automation exchanges a victim's OAuth authorization code for refresh tokens.T1550.001 · Application Access TokenAttackers import obtained tokens into Specter Portal to access Microsoft environment resources permitted by those tokens.T1566.002 · Spearphishing LinkConsentFix v3 phishing emails contain links to phishing pages, including links embedded in DocSend-hosted PDFs.T1585.002 · Email AccountsThe reported preparation includes creating accounts on services such as Outlook and Tutanota to support phishing operations.T1589.002 · Email AddressesAttackers gather employee email addresses to personalize spear-phishing.T1589.003 · Employee NamesAttackers gather employee names to support impersonation and personalized spear-phishing.
People
Vendors
CloudflareAttackers combine tenant discovery, targeted reconnaissance, Cloudflare Pages phishing, and Pipedream automation to immediately exchange authorization codes for refresh tokens and enable postâexploitation via toolsDocSendPhishing pages hosted on Cloudflare Pages initiate real Microsoft login flows and use DocSend PDFs to improve credibility and bypass filters.MicrosoftConsentFix v3 is an automated, scalable evolution of OAuth authorization-code phishing that abuses pre-consented Microsoft firstâparty apps to harvest tokens and hijack Azure accounts.PipedreamAttackers combine tenant discovery, targeted reconnaissance, Cloudflare Pages phishing, and Pipedream automation to immediately exchange authorization codes for refresh tokens and enable postâexploitation via tools
Products
AzureConsentFix v3 is an automated, scalable evolution of OAuth authorization-code phishing that abuses pre-consented Microsoft firstâparty apps to harvest tokens and hijack Azure accounts.Cloudflare PagesAttackers combine tenant discovery, targeted reconnaissance, Cloudflare Pages phishing, and Pipedream automation to immediately exchange authorization codes for refresh tokens and enable postâexploitation via toolsDropbox DocSendPhishing pages hosted on Cloudflare Pages initiate real Microsoft login flows and use DocSend PDFs to improve credibility and bypass filters.PipedreamAttackers combine tenant discovery, targeted reconnaissance, Cloudflare Pages phishing, and Pipedream automation to immediately exchange authorization codes for refresh tokens and enable postâexploitation via toolsSpecter Portalexchange authorization codes for refresh tokens and enable postâexploitation via tools like Specter Portal.