
Sysdig Reports LLM-Agent-Driven Post-Exploitation After Marimo CVE Exploit
Summary
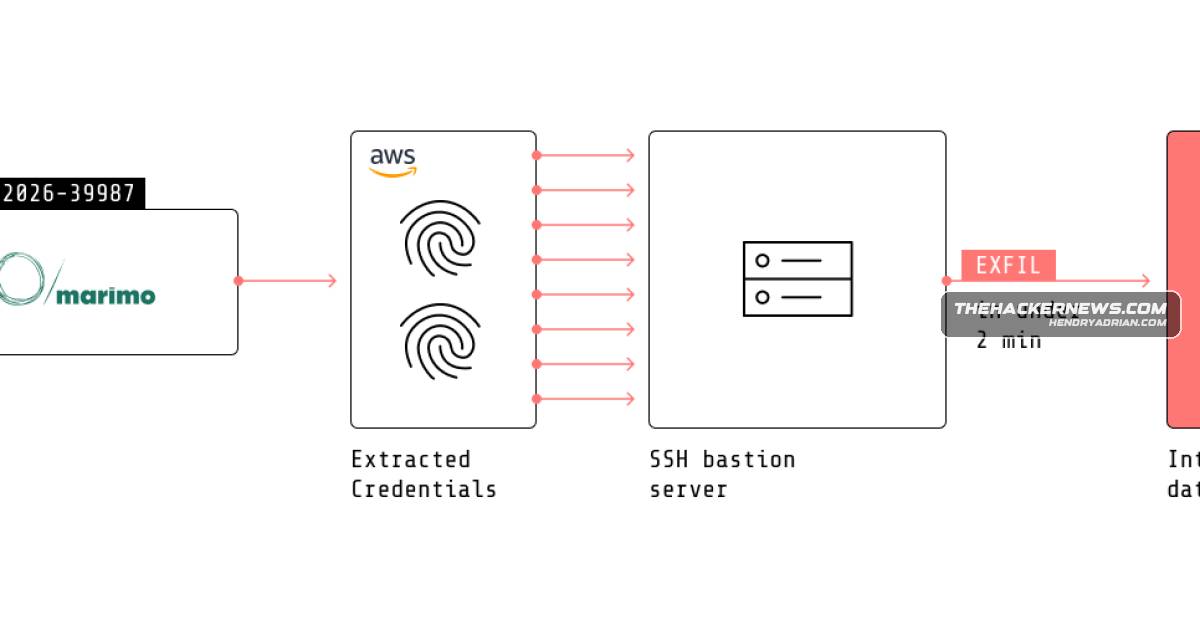
Sysdig reported that an unknown actor exploited Marimo CVE-2026-39987, used AWS credentials and an SSH key to reach a bastion, and exfiltrated an internal PostgreSQL database. It cited command patterns and other evidence of LLM-agent use.
Key points
- Sysdig reported that an unknown actor exploited CVE-2026-39987, an unauthenticated remote-code-execution flaw, on a publicly accessible Marimo instance.
- The actor reportedly extracted cloud credentials and used AWS Secrets Manager to retrieve an SSH private key.
- Sysdig said eight parallel SSH sessions to a bastion were used to exfiltrate the schema and contents of an internal PostgreSQL database in under two minutes.
- Evidence Sysdig cited for LLM-agent involvement included an improvised database dump, a leaked Chinese-language planning comment, machine-oriented command formatting, and values passed between commands.
- Sysdig recorded the activity on May 10, 2026; it said the end-to-end chain lasted a little over an hour.
- Marimo addressed the vulnerability in version 0.23.0. Recommended steps include updating, checking for publicly accessible instances, and rotating credentials and keys.
Article Details
- Attack Vectors
- The attacker exploited CVE-2026-39987 against a publicly accessible Marimo instance to obtain unauthenticated remote code execution.
- After compromising the host, the attacker retrieved cloud credentials and used AWS Secrets Manager to obtain an SSH private key.
- The attacker used the retrieved key to launch eight SSH sessions against a downstream bastion server and exfiltrated an internal PostgreSQL database.
- Defensive Notes
- Update Marimo to version 0.23.0 or later.
- Audit environments for publicly accessible Marimo instances.
- Rotate credentials, API keys, and SSH keys.
MITRE ATT&CK
T1021.004 · SSHThe attacker used the retrieved SSH private key to authenticate to a bastion server and launch eight SSH sessions against a downstream server.T1059.004 · Unix ShellAfter compromise, the attacker executed system commands, including cat and ls commands, to search for and inspect credentials and SSH keys.T1078.004 · Cloud AccountsThe attacker replayed harvested AWS access credentials to make API calls to AWS Secrets Manager.T1190 · Exploit Public-Facing ApplicationThe attacker exploited CVE-2026-39987 against an internet-reachable Marimo instance to gain initial access.T1552.001 · Credentials In FilesThe attacker used cat on ~/.pgpass to obtain database credentials and inspected a private key file under ~/.ssh.T1555.006 · Cloud Secrets Management StoresThe attacker used harvested AWS credentials to access AWS Secrets Manager and retrieve an SSH private key.
CVE
Products
AWS Secrets Managerused an LLM agent to adaptively continue post-compromise actions, including credential harvesting, AWS Secrets Manager access, and SSH access to a bastion host.MarimoAn unknown threat actor exploited CVE-2026-39987 in a public Marimo instance and used an LLM agent to adaptively continue post-compromise actions, including credential harvesting, AWS Secrets Manager access, and SSHPostgreSQLThe intrusion ended with rapid exfiltration of an internal PostgreSQL database, highlighting the growing use of AI-assisted operators for flexible, live attack chains.