
DriveSurge Uses ClickFix and Fake Updates to Deliver Malware Through Compromised Sites
Summary
Silent Push researchers identify DriveSurge, a suspected initial-access broker using zTDS to redirect visitors from thousands of compromised sites to ClickFix and fake-update lures. The analysis details infrastructure fingerprints and a macOS clipboard-hijacking payload
Key points
- Silent Push researchers say DriveSurge used injected code and zTDS to redirect visitors from thousands of compromised websites to malware lures.
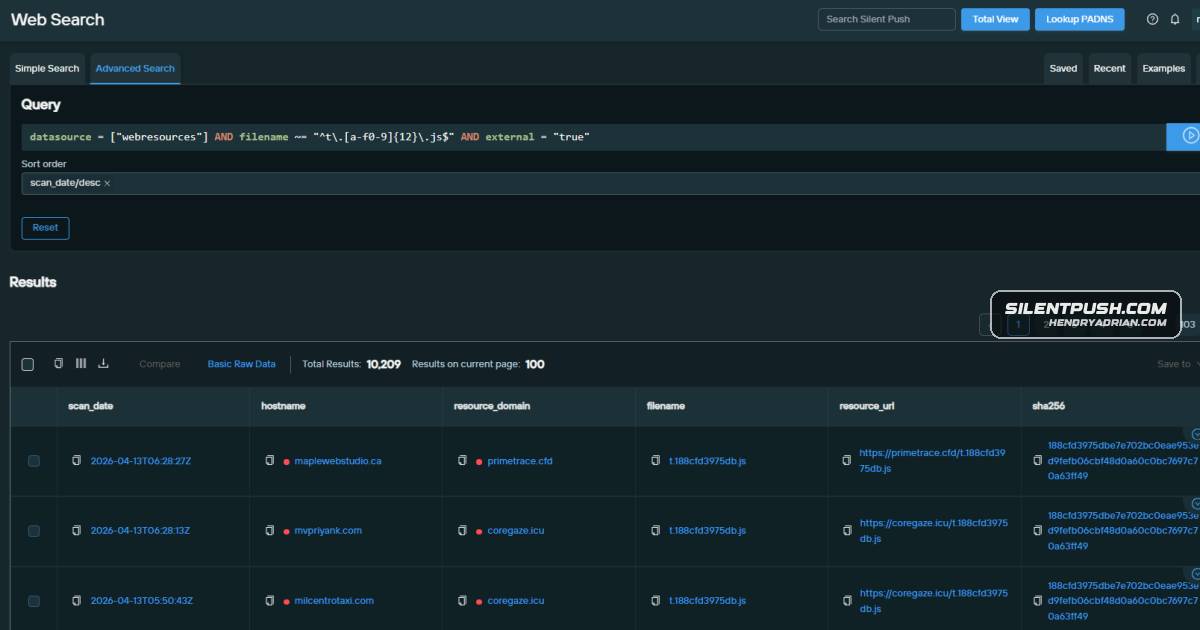
- The researchers describe eight infrastructure fingerprints, including JavaScript filename patterns, server configurations, domain attributes, and WHOIS registration-email pivots.
- Fake-update pages impersonated multiple browsers; one analyzed download contained DLLs and a file named Browser Update.exe.
- A ClickFix lure instructed users to paste a malicious command; in one observed instance it attempted to retrieve code from 91.92.240[.]127.
- Analysis of an obfuscated macOS-targeting script found it replaced clipboard contents with a command that downloads and executes a payload.
- Researchers say the payload’s command downloads and runs a script, then deletes it; they identified payload servers and a C2 connection at 147.45.42[.]205:8133.
- The researchers suspect DriveSurge operates as a pay-per-install initial-access broker; they describe this as a hypothesis, not a confirmed business model.
Article Details
- Attack Vectors
- DriveSurge injects JavaScript into compromised legitimate websites and uses zTDS to profile visitors and redirect selected traffic.
- FakeUpdates pages impersonate browser updates and deliver a ZIP containing DLLs and a file named Browser Update.exe.
- ClickFix lures instruct users to paste commands into a terminal or PowerShell; observed commands download and execute malware.
- A macOS lure impersonates a reCAPTCHA verification, replaces clipboard contents with a malicious shell command, and prompts the victim to paste it into Terminal.
- Injected scripts use Base64 decoding and string concatenation to retrieve zTDS scripts, with backup domains used for failover.
- Defensive Notes
- Monitor externally loaded resources matching the reported t.js?site=32-hex, t.<12-hex>.js, ext(-b)?.<12-hex>.js, and jsrepo?rnd= patterns.
- Inspect compromised WordPress pages for Base64-obfuscated zTDS loaders and scripts that exclude logged-in administrators.
- Warn users not to run commands copied from fake browser updates, error messages, or verification prompts.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | banerpanel[.]live | Suspicious domain loaded into a compromised site and observed serving an advertisement distribution system. |
| DOMAIN | beacontrace[.]bond | Malicious JavaScript injection domain using the reported t.js?site= fingerprint. |
| DOMAIN | brightson[.]icu | Identified by Silent Push as pre-weaponized DriveSurge infrastructure, not yet serving malicious injects at the time of the report. |
| DOMAIN | captioto[.]com | Malicious zTDS failover domain embedded in an injected script. |
| DOMAIN | check[.]first-node[.]rocks | Malicious domain that served a fake Firefox update page and its injected script. |
| DOMAIN | coverlink[.]icu | Identified by Silent Push as pre-weaponized DriveSurge infrastructure, not yet serving malicious injects at the time of the report. |
| DOMAIN | cptoptious[.]com | DriveSurge-associated domain observed serving zTDS. |
| DOMAIN | datumprobe[.]icu | Identified by Silent Push as pre-weaponized DriveSurge infrastructure, not yet serving malicious injects at the time of the report. |
| DOMAIN | eraggifts[.]icu | Identified by Silent Push as pre-weaponized DriveSurge infrastructure, not yet serving malicious injects at the time of the report. |
| DOMAIN | keyview[.]icu | Identified by Silent Push as pre-weaponized DriveSurge infrastructure, not yet serving malicious injects at the time of the report. |
| DOMAIN | newtdsone[.]shop | Malicious zTDS domain embedded in an injected script as a payload-fetch endpoint. |
| DOMAIN | traceglimpse[.]icu | Identified by Silent Push as pre-weaponized DriveSurge infrastructure, not yet serving malicious injects at the time of the report. |
| DOMAIN | tracekey[.]icu | Identified by Silent Push as pre-weaponized DriveSurge infrastructure, not yet serving malicious injects at the time of the report. |
| DOMAIN | webgleam[.]info | Identified as a malicious DriveSurge domain through the reported infrastructure fingerprints. |
| HOSTNAME | ns1[.]erans[.]ru | Name server appearing in the infrastructure pattern associated with the reported malicious DriveSurge domains. |
| HOSTNAME | testio[.]ecartdev[.]com | Silent Push assessed this host as a payload and development server, with files indicating malware staging capability. |
| IPV4 | 147[.]45[.]42[.]200 | Older payload server reported to have hosted the same macOS malware samples. |
| IPV4 | 147[.]45[.]42[.]205 | C2 address the reported malware samples connect to on port 8133. |
| IPV4 | 46[.]226[.]166[.]57 | Attacker payload server hosting macOS malware and providing payload downloads. |
| IPV4 | 91[.]92[.]240[.]127 | IP address from which a ClickFix instance attempted to retrieve malicious code. |
| SHA256 | 7aa15de93cf85729ddf970e8d7897f69ece3ca29608f73e784a9ba40c9cea18d | SHA256 hash of the macOS malware payload available from both reported payload servers. |
| SHA256 | 8ecc7108cd679316bf5900e84f19b256dc399902cdede646493f502ac872cc1a | SHA256 hash of an additional malware sample reported as distributed by the payload servers. |
| SHA256 | e1ce4e6222396a58d13dddfe64c1dd21f1632bcbe11d1867d44bab4fc646883a | SHA256 hash of an additional malware sample reported as distributed by the payload servers. |
| URL | hxxp[:]//147[.]45[.]42[.]200/66856ca57ed?force=1 | Specific malware payload URL reported as distributed by the older payload server. |
| URL | hxxp[:]//147[.]45[.]42[.]200/ce3cbfc887?force=1 | Specific macOS malware payload URL hosted on the older payload server. |
| URL | hxxp[:]//147[.]45[.]42[.]200/e97b7f7ccab3a?force=1 | Specific malware payload URL reported as distributed by the older payload server. |
| URL | hxxp[:]//46[.]226[.]166[.]57/66856ca57ed?force=1 | Specific malware payload URL reported as distributed by the payload server. |
| URL | hxxp[:]//46[.]226[.]166[.]57/ce3cbfc887?force=1 | Specific macOS malware payload URL hosted on the payload server. |
| URL | hxxp[:]//46[.]226[.]166[.]57/e97b7f7ccab3a?force=1 | Specific malware payload URL reported as distributed by the payload server. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe injected JavaScript uses Base64 decoding and string concatenation to conceal zTDS URLs and malicious logic.T1036 · MasqueradingFake update pages disguise malware downloads as legitimate browser updates.T1059.001 · PowerShellThe article describes ClickFix instructions to run malicious commands in PowerShell and a terminal_ps1_downloader staging script.T1059.004 · Unix ShellThe macOS lure supplies a command that downloads a script and executes it with bash.T1059.007 · JavaScriptInjected JavaScript decodes and loads malicious scripts in visitors’ browsers.T1105 · Ingress Tool TransferThe reported shell command uses curl to download a secondary payload from an attacker server.T1189 · Drive-by CompromiseDriveSurge injects code into compromised legitimate websites to redirect selected visitors to malicious content.T1204.004 · Malicious Copy and PasteClickFix and the macOS verification lure rely on victims pasting attacker-provided commands.T1583.001 · DomainsSilent Push reports DriveSurge domains registered through a dedicated email address and uses registration pivots to identify further infrastructure.