
WithSecure Details GREYVIBE’s AI-Assisted Campaigns Targeting Ukraine
Summary
WithSecure links GREYVIBE to attacks targeting Ukraine since at least August 2025, detailing phishing and fake-site delivery chains, custom malware, and evidence of AI assistance. The group’s relationship with the Russian state remains unclear.
Key points
- WithSecure says GREYVIBE has targeted Ukrainian and Ukraine-related military, government, civilian, and business organizations since at least August 2025.
- Reported delivery methods include spear-phishing with malicious archives, fake CAPTCHA pages, fraudulent adult-club sites, and charity-themed websites.
- Campaigns use tools including PhantomRelay, LegionRelay, FallSpy, and WireGuard; reported capabilities include host profiling, data theft, persistence, and remote access.
- Some fake sites introduced a WebRTC live-call feature that could capture victims’ audio and video.
- WithSecure cites evidence that AI platforms may have assisted with malware, obfuscation, loaders, infrastructure, and images; design flaws in LegionRelay reportedly exposed backend functionality.
- WithSecure assesses GREYVIBE’s ties to the Russian cybercrime ecosystem with moderate confidence, but says its precise relationship with the Russian state remains unclear.
Article Details
- Attack Vectors
- Spear-phishing emails distribute links to malicious ZIP or RAR archives hosted on Google Drive and 4sync, containing JavaScript-based loaders.
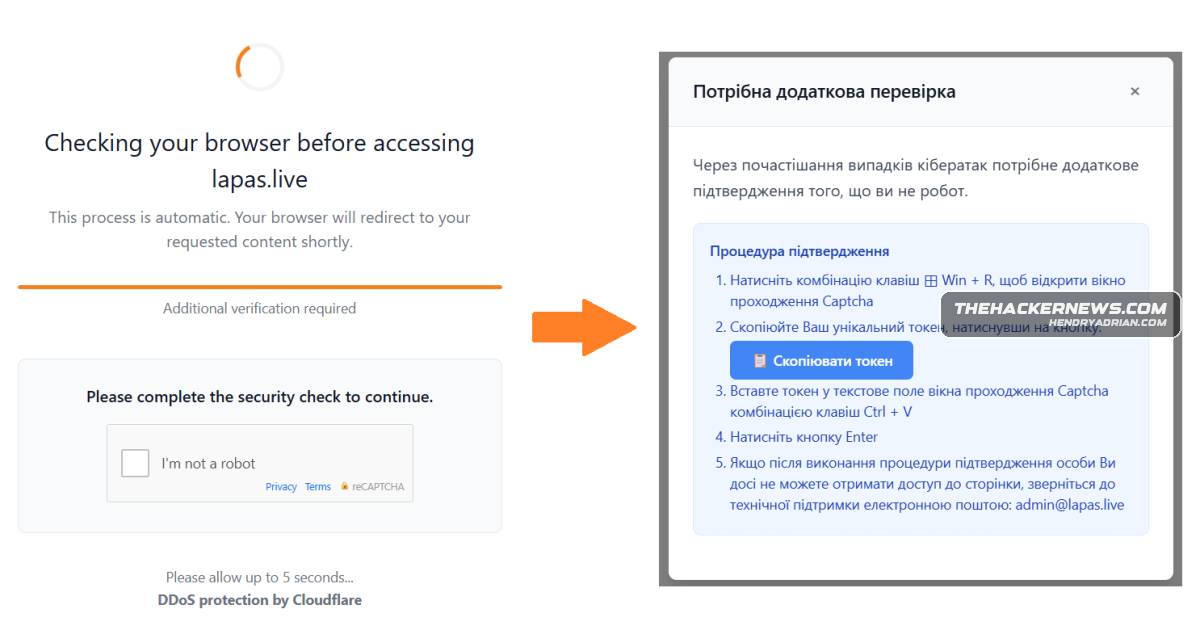
- Fake CAPTCHA pages use ClickFix-style lures to trick users into running commands that initiate a PhantomRelay infection chain.
- Fraudulent Ukrainian adult-club websites deliver FallSpy to Android devices and PhantomRelayV1 or LegionRelay to Windows systems.
- Websites masquerading as charitable foundations supporting the Armed Forces of Ukraine deliver WireGuard and LegionRelay.
- A Russian-language login screen is used as a lure in a FallSpy sample, likely to deceive Ukrainian military personnel.
MITRE ATT&CK
T1021.001 · Remote Desktop ProtocolLegionRelay supports setting up RDP access.T1027 · Obfuscated Files or InformationThe group uses custom-developed obfuscators and AI-assisted obfuscation scripts.T1059.001 · PowerShellPhantomRelay and LegionRelay are PowerShell-based RATs that run PowerShell scripts.T1059.003 · Windows Command ShellPhantomRelay can run Windows commands.T1059.007 · JavaScriptPhantomMail uses JavaScript-based loaders to launch a decoy document.T1113 · Screen CaptureLegionRelay supports screenshot capture.T1123 · Audio CaptureA WebRTC-based feature on later lure sites captures victim audio.T1125 · Video CaptureA WebRTC-based feature on later lure sites captures victim video.T1204.004 · Malicious Copy and PastePhantomClick fake CAPTCHA pages use ClickFix-style lures to trick users into running commands.T1496.001 · Compute HijackingXMRig was deployed on a small number of LegionRelay-infected machines.T1566.002 · Spearphishing LinkPhantomMail uses spear-phishing emails containing links to malicious archives hosted on Google Drive and 4sync.
People
Threat Actors
GREYVIBEWithSecure attributes persistent attacks targeting Ukraine and Ukraine-related entities since at least August 2025 to GREYVIBE. The group is assessed to be Russian-speaking and aligned with Kremlin interests, but the exact relationship to the Russian state remains unclear.Trickbot GroupWithSecure reports that an ISO builder used by GREYVIBE may have suspected ties to the TrickBot gang; this is not presented as confirmed direct involvement in GREYVIBE's operations.UAC-0098WithSecure reports that an ISO builder used by GREYVIBE may have suspected ties to UAC-0098; this is not presented as confirmed direct involvement in GREYVIBE's operations.
Malware
Products
Google Geminiin the attacks likely stems from the use of AI platforms, including Ideogram AI, OpenAI ChatGPT, and Google Gemini, to assist with generating images and developing LegionRelay, as well as obfuscation and loaderIdeogram AIof delivery vectors and tools used in the attacks likely stems from the use of AI platforms, including Ideogram AI, OpenAI ChatGPT, and Google Gemini, to assist with generating images and developing LegionRelay, asOpenAI ChatGPTand tools used in the attacks likely stems from the use of AI platforms, including Ideogram AI, OpenAI ChatGPT, and Google Gemini, to assist with generating images and developing LegionRelay, as well asWireGuard#GREYVIBE
Tools
Countries
Industries
BusinessThe victimology footprint spans military, government, civilian, and business-related organizations.GovernmentThe victimology footprint spans military, government, civilian, and business-related organizations.MilitaryThe victimology footprint spans military, government, civilian, and business-related organizations.