Ousaban Banking Trojan Targets Users in Spain and Portugal
Summary
FortiGuard details an Ousaban campaign targeting Spain and Portugal through phishing PDFs and a staged payload, with geofencing, evasion, persistence, and daily changing C2 domains.
Key points
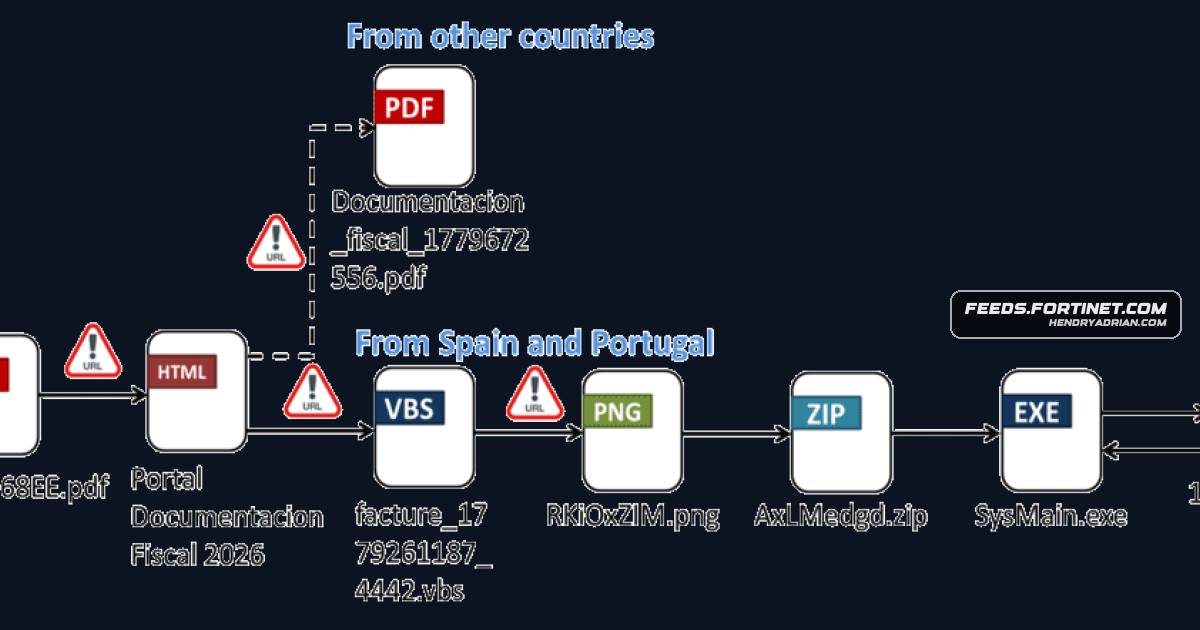
- The campaign uses phishing PDFs that direct targets to a malicious webpage; users in Spain or Portugal receive a VBS file that deploys the Ousaban payload.
- The webpage uses geofencing and environmental checks to restrict access. An updated version performs checks server-side and returns a denial PDF to users outside the target countries.
- The VBS script extracts Ousaban from a ZIP archive hidden in an image, then removes temporary delivery files to reduce its footprint.
- Ousaban establishes persistence through a Windows Run registry key and monitors browser access to targeted banking services.
- The malware uses encrypted communications and daily changing DDNS hostnames to locate its C2 server; its documented capabilities include screenshots, remote control, keylogging, and clipboard injection.
- FortiGuard lists detection names and indicators including domains, IP addresses, and file hashes; it says up-to-date Fortinet protections block the described malware.
Article Details
- Attack Vectors
- A phishing PDF directs victims to a malicious webpage, which checks the victim's environment and downloads a VBS file to eligible users in Spain or Portugal.
- The VBS file downloads a steganographic image, extracts a ZIP archive from it, and retrieves and executes the Ousaban payload.
- Earlier campaign variants used ClickFix to trick victims into executing code that downloaded a VBS file and MSI installer, or used a PDF leading to a phishing webpage that delivered the MSI installer.
- The MSI installer contained a Rust-based downloader that downloaded and executed Ousaban.
- Defensive Notes
- Fortinet reports that FortiGuard Antivirus detects and blocks the malware under the names W32/Ousaban.EY!tr.spy, VBS/Agent.TPX!tr.dldr, and PDF/Agent.STG!tr.
- The article recommends keeping FortiGate, FortiMail, FortiClient, and FortiEDR protections up to date; it also describes FortiSandbox anti-phishing, web filtering, antivirus, and FortiGuard CDR protections.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | controlfacturas[.]site | Listed by the article as a campaign domain IOC. |
| DOMAIN | facture-arsys[.]duckdns[.]org | Listed by the article as a campaign domain IOC. |
| DOMAIN | facture-in[.]pages[.]dev | Listed by the article as a campaign domain IOC. |
| DOMAIN | faturanova[.]duckdns[.]org | Listed by the article as a campaign domain IOC. |
| DOMAIN | faturanova[.]xyz | Listed by the article as a campaign domain IOC. |
| IPV4 | 162[.]33[.]179[.]46 | Listed by the article as an IP IOC. |
| IPV4 | 213[.]159[.]64[.]191 | Listed by the article as an IP IOC. |
| IPV4 | 78[.]40[.]209[.]32 | Listed by the article as an IP IOC. |
| IPV4 | 91[.]92[.]240[.]140 | Listed by the article as an IP IOC. |
| SHA256 | 18fd38988d58dd930f5992d448cc09a9400c1eafba76b820b9a83239ac48cf4e | Hash listed for a campaign EXE artifact. |
| SHA256 | 19ac18a50abb48dc0ea9524850acfaec49359e6b3bcc67c6193c2d56da812c71 | Hash listed for a campaign PDF artifact. |
| SHA256 | 1e77992666acbbfa0d01fcefa9cc8fbdac291e0681b35745be27c6dfb159a375 | Hash listed for a campaign PDF artifact. |
| SHA256 | 21b24f7ee1f6bdbbb670f0394d66009ee0daa8ced57048298da715e88f7a7cdd | Hash listed for a campaign MSI artifact. |
| SHA256 | 48723a33bab89f174750576f9a62da35b3b9e5ac31a5a8f1ce9859a1b35bf8b8 | Hash listed for a campaign PDF artifact. |
| SHA256 | 4c9fdc2823da505ef339d43c6ad38499b7e3447736733e42b5ab6b1afcfd42aa | Hash listed for a campaign PDF artifact. |
| SHA256 | 4ca2c863d740bb7022776dccabd8ae34bb9998768928042d76ebcf08984eefcb | Hash listed for a campaign EXE artifact. |
| SHA256 | 540ee1936e61d2344b5ebc93485589a351ec2f113a9b4940ae16f3baa4807392 | Hash listed for a campaign PDF artifact. |
| SHA256 | 5837e47198a20877e1b04b270c36d9194206ee38d4f32fe3151b3c3b396c4f0d | Hash listed for a campaign EXE artifact. |
| SHA256 | 5a2ed557c357ba8f96f2d55a8a00695987806b5df766cd1dfdab0cbed111774a | Hash listed for a campaign PDF artifact. |
| SHA256 | 5e06af187b45476ade0d953e834fced6197d0a33ac60c2575877660e26ab15e8 | Hash listed for a campaign PDF artifact. |
| SHA256 | 65c1a998bac48e02b52b1c850cd500e9fb87521e21755c3a4a491243f5f9a700 | Hash listed for a campaign PDF artifact. |
| SHA256 | 6bc2e11b0917f47d0557288c4f0cb20bd7589185943b989a969fdc6d3704ee73 | Hash listed for a campaign PDF artifact. |
| SHA256 | 9d07a83cf89685651ea8992047ae694c24f6ddef193044357debd15ce07a64fe | Hash listed for a campaign PDF artifact. |
| SHA256 | 9e81ade09cc18f0fc09d73e72d2e0bffad02f52fdcc26553e473cee8cabc1567 | Hash listed for a campaign PDF artifact. |
| SHA256 | d4eb4ff02df659fdeec17d36b77084627469623bb3c7d16383d257404b52d1c3 | Hash listed for a campaign MSI artifact. |
| SHA256 | e2f0c2d4c1552cd81fa012043e4a5ac832582b639b7b6b7eccc0c4802d7a8ad8 | Hash listed for a campaign PDF artifact. |
| SHA256 | e6e78eb2e9bd41a4bc62f7ad54d095ea9813864bebe37172ae30a1afa631fe14 | Hash listed for a campaign EXE artifact. |
| SHA256 | fadbb8061715128bebecf7bc59132b6bb04fe8cc39b965aa5b8722dffe28d7e7 | Hash listed for a campaign PDF artifact. |
| SHA256 | ffb9eb47cc0cb2f43e04a10dc84df13d04bca1ebacbe47fad0b669728de2f59c | Hash listed for a campaign EXE artifact. |
MITRE ATT&CK
T1055 · Process InjectionThe article reports process injection as a method of running the malicious DLL payload.T1056.001 · KeyloggingThe article reports that Ousaban can implement a keylogger.T1113 · Screen CaptureThe #Iniciar# command starts screenshot capture.T1547.001 · Registry Run Keys / Startup FolderOusaban creates a Financeiro value in the CurrentVersion\Run registry key for persistence.T1574.002 · DLL Side-LoadingThe article reports DLL side-loading to run the malicious payload.
People
Malware
Vendors
Products
FortiClientFortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service.FortiEDRFortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service.FortiMailFortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service.Fortinet FortiGateFortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service.FortiSandboxrecognizes the phishing email as “virus detected.” In addition, real-time anti-phishing provided by FortiSandbox embedded in Fortinet’s FortiMail, web filtering, and antivirus solutions provides advanced protectionMicrosoft WindowsAffected Platforms: Microsoft Windows
Countries
BrazilThis malware has been active in Brazil and is spread through an MSI downloader.PortugalIn May 2026, FortiGuard Labs identified an attack targeting users in Spain and Portugal involving the banking Trojan Ousaban.SpainIn May 2026, FortiGuard Labs identified an attack targeting users in Spain and Portugal involving the banking Trojan Ousaban.