
Armored Likho Targets Government and Power Sectors with BusySnake Stealer
Summary
Kaspersky details Armored Likho campaigns against government and power-sector targets in Russia, Brazil and Kazakhstan, including spear-phishing chains and BusySnake Stealer capabilities for stealing credentials, documents, screenshots and Telegram data.
Key points
- Kaspersky attributes campaigns targeting government agencies and the electric power sector in Russia, Brazil and Kazakhstan to Armored Likho, with both espionage and financially motivated activity reported.
- Spear-phishing lures deliver archives with droppers; other chains abuse Windows shortcut files and CVE-2025-9491, which Microsoft patched in November 2025.
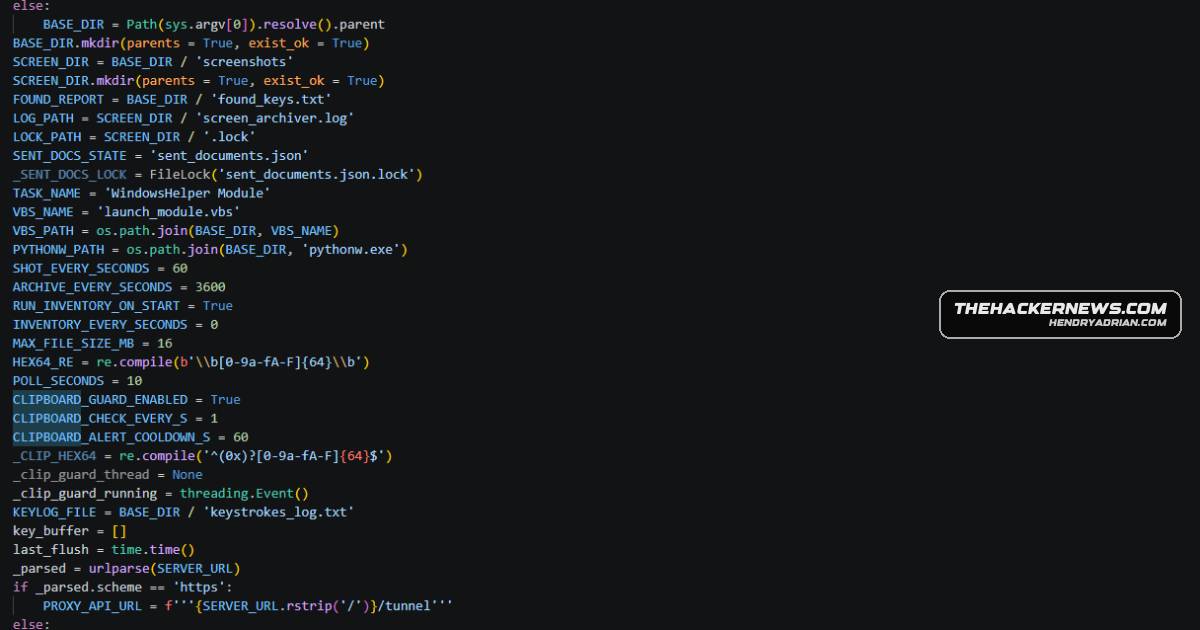
- BusySnake Stealer can collect clipboard contents, documents, screenshots, keystrokes, browser cookies and passwords, Telegram data, and cryptocurrency wallet files.
- The malware uses scheduled tasks for persistence and can communicate with a C2 server, upload collected data, and establish a reverse SSH tunnel using Go2Tunnel.
- Kaspersky reports similarities between BusySnake and AquilaRAT; possible overlap with BI.ZONE-tracked Eagle Werewolf is suggested, but Armored Likho’s origins remain unknown.
- Kaspersky says first-stage loaders and stagers may have been developed with AI assistance, citing redundant comments and code blocks.
Article Details
- Attack Vectors
- Spear-phishing emails use government-notice or social-program lures to distribute RAR archives containing droppers.
- Dropper EXE files retrieve additional payloads, including BusySnake Stealer, from a GitHub repository.
- An alternate chain abuses CVE-2025-9491 through Windows shortcut files to trigger remote code execution and launch an obfuscated PowerShell command.
- VBScript files and scheduled tasks are used to launch the stealer and establish persistence.
- BusySnake Stealer collects clipboard data, screenshots, keystrokes, browser cookies and passwords, Telegram session and credential data, and cryptocurrency wallet files; it can upload user documents to its C2 server.
- Go2Tunnel is used to establish a reverse SSH tunnel to a C2 server.
- Defensive Notes
- Microsoft addressed CVE-2025-9491 in its November 2025 Patch Tuesday updates.
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe malware and PowerShell command are obfuscated, and BusySnake uses evasion techniques to complicate analysis and detection.T1041 · Exfiltration Over C2 ChannelBusySnake uploads user documents and captured credential screenshots to its C2 server.T1053.005 · Scheduled TaskThe malware uses scheduled tasks to launch the stealer and maintain persistence.T1056.001 · KeyloggingC2 commands can direct BusySnake to log keystroke data.T1059.001 · PowerShellThe shortcut vulnerability triggers an obfuscated PowerShell command that launches a loader.T1059.005 · Visual BasicVBScript files are used to erase execution traces and launch the stealer.T1083 · File and Directory DiscoveryBusySnake enumerates files across the system and logs their metadata.T1105 · Ingress Tool TransferDropper EXE files retrieve additional payloads, including the stealer, from a GitHub repository.T1113 · Screen CaptureBusySnake captures screenshots and can take them at intervals specified by C2 commands.T1115 · Clipboard DataBusySnake Stealer collects data from the infected system's clipboard.T1203 · Exploitation for Client ExecutionThe attack chain abuses CVE-2025-9491 in Windows shortcut handling to trigger remote code execution.T1539 · Steal Web Session CookieA BusySnake version includes a module for stealing browser cookies.T1555.003 · Credentials from Web BrowsersBusySnake extracts passwords from Mozilla Firefox and Chromium-based browsers.T1566.001 · Spearphishing AttachmentSpear-phishing emails use government-notice or social-program lures to distribute RAR archives containing droppers.T1572 · Protocol TunnelingGo2Tunnel establishes a reverse SSH tunnel to a C2 server.
CVE
Threat Actors
Armored LikhoKaspersky attributes campaigns targeting government agencies and the electric power sector across Russia, Brazil, and Kazakhstan to Armored Likho; the article describes espionage and financially motivated activity.Eagle WerewolfBI.ZONE tracks Eagle Werewolf as active since May 2023 and reports its targeting of government and defense organizations. The article describes possible overlap with Armored Likho, including similarities between AquilaRAT and BusySnake, but does not establish that they are the same group.
Malware
AquilaRATIts toolkit includes obfuscated RATs, BusySnake Stealer, AquilaRAT, and Go2Tunnel, with attacks delivered through spear-phishing, GitHub-hosted payloads, and abused Windows shortcut chains.BusySnake StealerIts toolkit includes obfuscated RATs, BusySnake Stealer, AquilaRAT, and Go2Tunnel, with attacks delivered through spear-phishing, GitHub-hosted payloads, and abused Windows shortcut chains.
Vendors
BI.ZONEThe Russian cybersecurity vendor said Armored Likho shares possible overlaps with a threat cluster tracked by BI.ZONE under the moniker Eagle Werewolf, which has been active since May 2023.Kaspersky“Armored Likho blends financially motivated campaigns targeting private individuals with targeted cyber espionage aimed at organizations,” Kaspersky said in a technical analysis published today.MicrosoftThe flaw, tracked as CVE-2025-9491 (aka ZDI-CAN-25373), was addressed by Microsoft as part of its Patch Tuesday updates for November 2025.Trend MicroEvidence unearthed by Trend Micro last year revealed that the shortcoming had been weaponized by a dozen hacking groups since 2017.
Products
Chromiuma reverse SSH tunnel using Go2Tunnel, install RustDesk, and extract cookies from Mozilla Firefox and Chromium-based browsers, along with passwords.GitHubIts toolkit includes obfuscated RATs, BusySnake Stealer, AquilaRAT, and Go2Tunnel, with attacks delivered through spear-phishing, GitHub-hosted payloads, and abused Windows shortcut chains.Microsoft WindowsIts toolkit includes obfuscated RATs, BusySnake Stealer, AquilaRAT, and Go2Tunnel, with attacks delivered through spear-phishing, GitHub-hosted payloads, and abused Windows shortcut chains.Mozilla Firefoxdata, establish a reverse SSH tunnel using Go2Tunnel, install RustDesk, and extract cookies from Mozilla Firefox and Chromium-based browsers, along with passwords.RustDeskcollect Telegram session and credential data, establish a reverse SSH tunnel using Go2Tunnel, install RustDesk, and extract cookies from Mozilla Firefox and Chromium-based browsers, along with passwords.TelegramBusySnake Stealer steals clipboard data, screenshots, cookies, passwords, and Telegram data.
Tools
Countries
BrazilArmored Likho is a previously undocumented threat actor targeting government agencies and the electric power sector across Russia, Brazil, and Kazakhstan with espionage and financially motivated campaigns.KazakhstanArmored Likho is a previously undocumented threat actor targeting government agencies and the electric power sector across Russia, Brazil, and Kazakhstan with espionage and financially motivated campaigns.RussiaArmored Likho is a previously undocumented threat actor targeting government agencies and the electric power sector across Russia, Brazil, and Kazakhstan with espionage and financially motivated campaigns.
Industries
DefenseThe hacking group has a track record of targeting government and defense organizations, specifically those involved in UAV development and manufacturing, using droppers, remote access trojans (RATs), and utilities forElectric powerArmored Likho is a previously undocumented threat actor targeting government agencies and the electric power sector across Russia, Brazil, and Kazakhstan with espionage and financially motivated campaigns.GovernmentArmored Likho is a previously undocumented threat actor targeting government agencies and the electric power sector across Russia, Brazil, and Kazakhstan with espionage and financially motivated campaigns.