cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2388 articles

Threat Research · asec.ahnlab.com

Kimsuky Uses Diplomat Impersonation to Deploy PebbleDash and PrxClient

AhnLab details Kimsuky spear-phishing attacks targeting foreign-affairs personnel with malicious LNK files that deploy PebbleDash, PrxClient, RDP tools, keyloggers and other malware to control systems and steal information.
Jul 16, 2026
Threat Research · feeds.fortinet.com

Obfuscated Lua and AutoIt Loaders Deploy RATs and Infostealers in Global Phishing Campaign

Fortinet details a global phishing campaign using obfuscated JScript droppers and disguised Lua or AutoIt loaders to deploy RATs and infostealers, including Remcos, Agent Tesla, XWorm, and a Snake Keylogger variant.

Jul 16, 2026
Threat Research · bleepingcomputer.com

Symantec Details Spirals Ransomware Intrusion That Encrypted Network in Under 24 Hours

Symantec describes Spirals ransomware compromising a South Asian IT services firm through an exposed IIS server, then stealing data and encrypting systems in under 24 hours. The actor was observed in one case.

Jul 16, 2026
Threat Research · bleepingcomputer.com

UAT-11795 Uses Trojanized Software Installers to Deploy Starland RAT

Cisco Talos reports that UAT-11795 has used trojanized installers since at least June 2025 to deploy Starland RAT, steal sensitive data, and deliver CastleStealer or Remcos. The infection vector is unconfirmed; ClickFix is a suspected possibility.

Jul 16, 2026
Threat Research · elastic.co

TELEPUZ Malware Spreads Through ClickFix and VIDAR Infection Chain

Elastic researchers describe TELEPUZ, a modular Windows malware delivered through ClickFix and VIDAR. The actively developed threat uses WebSocket command-and-control and downloadable modules; researchers say it may be malware-as-a-service.

Jul 16, 2026
Threat Research · blog.talosintelligence.com

UAT-11795 Uses Starland RAT and Custom WLDR C2 Implant in Financially Motivated Campaign

Talos details UAT-11795’s campaign targeting users in the U.S. and Europe with trojanized installers that deliver Starland RAT, a custom PowerShell C2 implant, and other malware to steal credentials and cryptocurrency assets.

Jul 16, 2026
Threat Research · thehackernews.com

OkoBot Uses In-App Fake Recovery Prompts to Target Ledger and Trezor Users

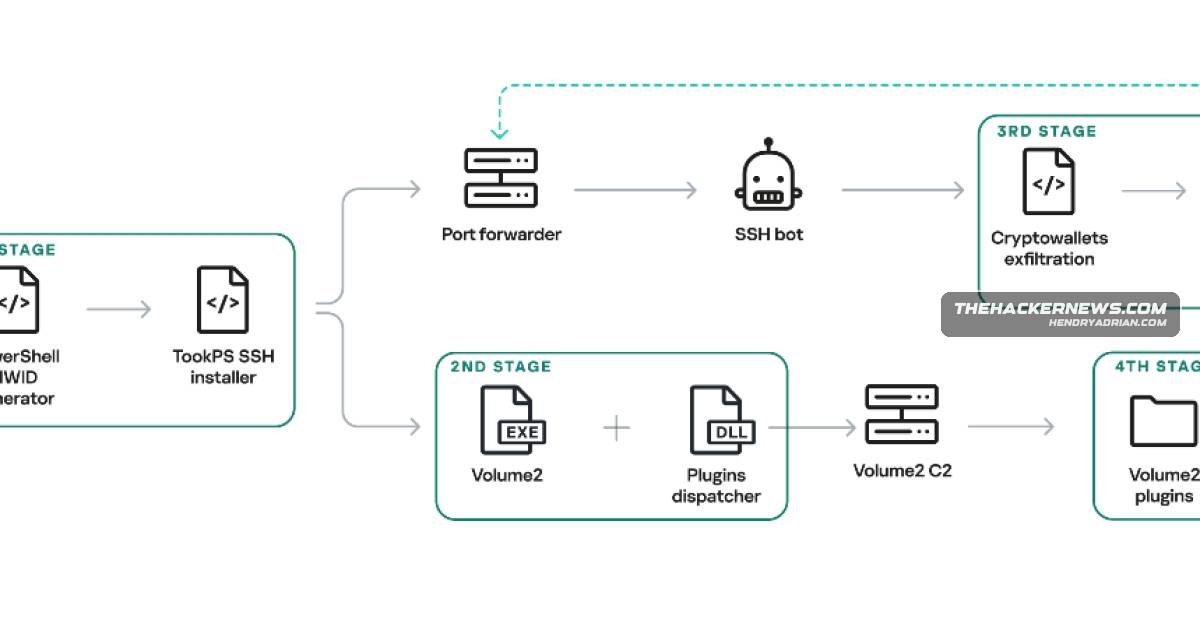
Kaspersky details OkoBot, a Windows framework active since April 2025 that injects fake recovery prompts into Ledger and Trezor apps to capture seed phrases. Its toolkit also enables SSH tunneling, RDP access and surveillance; the report does not say how many users gave

Jul 16, 2026
Threat Research · security.com

New Spirals Ransomware Used in Double-Extortion Attack on South Asian IT Company

A previously unseen Rust-based ransomware called Spirals was deployed against a South Asian IT company in June 2026 after attackers compromised an internet-facing IIS server. The actor is unknown; the attack involved data-theft threats and file encryption.

Jul 16, 2026
Threat Research · dmpdump.github.io

Analysis of a Low-Detection Linux Implant With Hands-On Intrusion Capabilities

Researchers analyzed a low-detection, statically linked Linux backdoor delivered as a PNG-named ELF. It profiles hosts, communicates with C2, executes commands, transfers files, and supports reverse tunnels; later analysis noted similarities to Adaptix Agent.

Jul 16, 2026
Threat Research · thehackernews.com

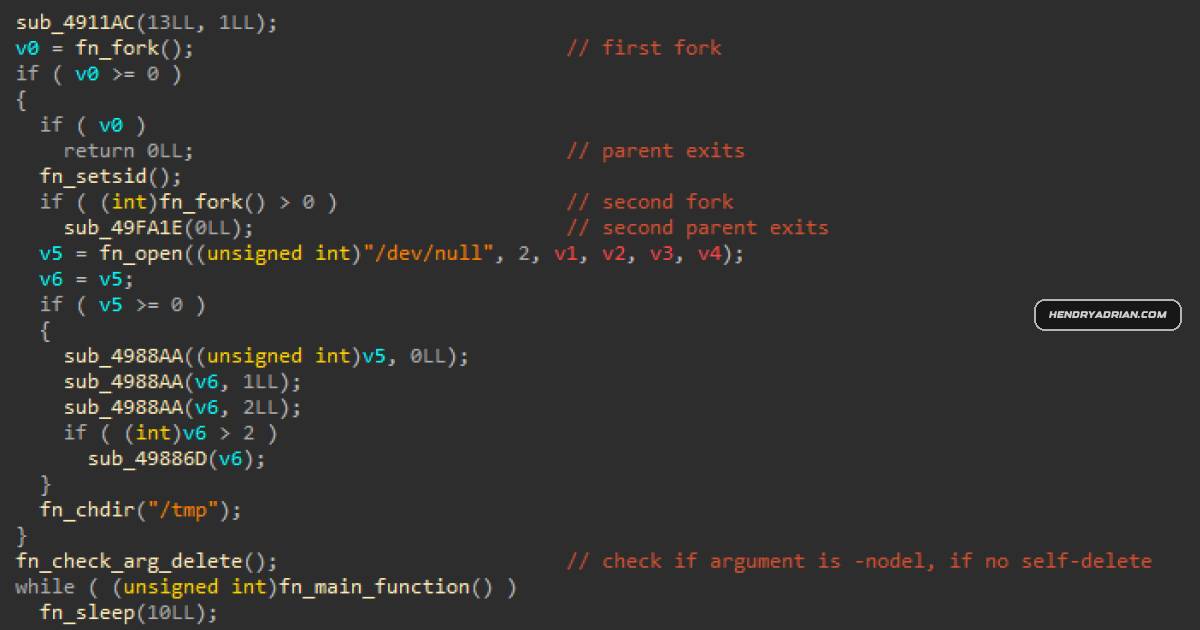
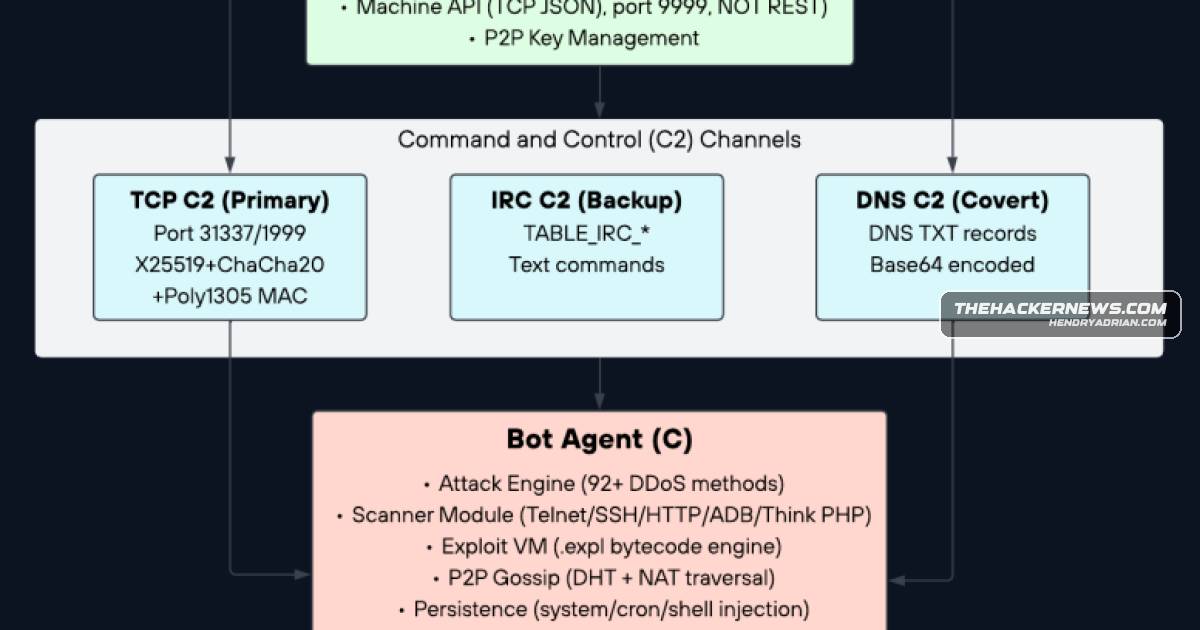
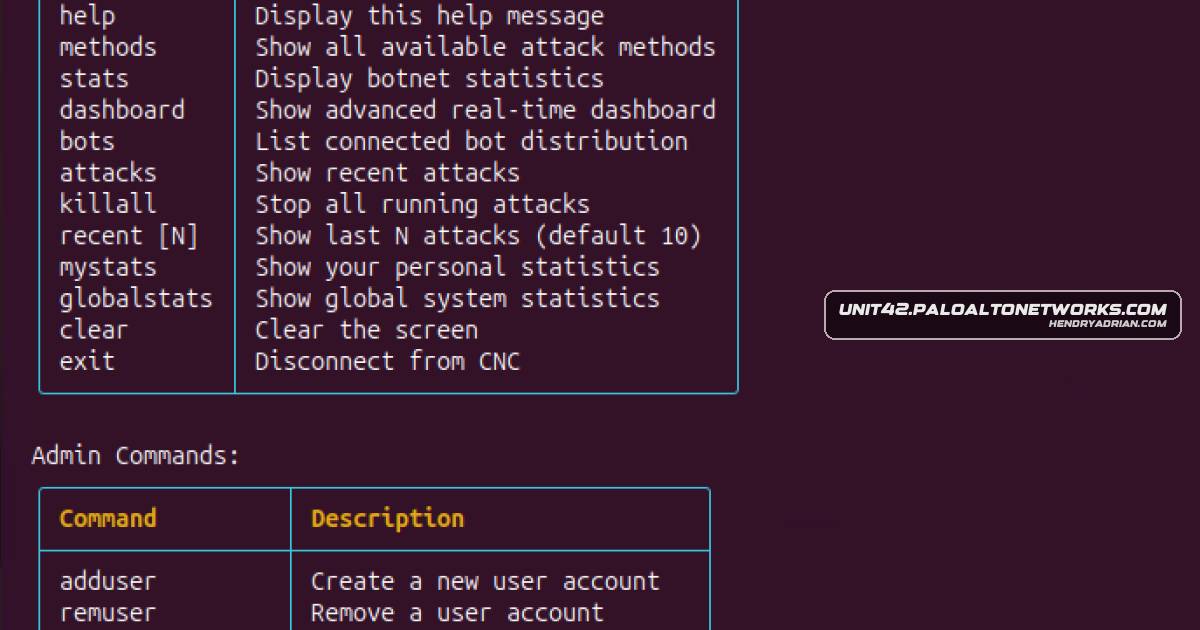
Unit 42 Details TuxBot IoT Botnet’s LLM-Assisted Development and Capabilities

Unit 42 analyzed TuxBot v3 Evolution, an IoT botnet framework with a multi-architecture agent, Go C2, Telnet brute forcing, IoT exploits, and fallback channels. Researchers found signs of LLM assistance and linked its operator to the Keksec ecosystem.

Jul 15, 2026
Threat Research · bleepingcomputer.com

Trend Micro: Threat Actor Used Gemini CLI to Operate Botnet Targeting Dental Clinic

Trend Micro says the actor bandcampro used Gemini CLI to operate a botnet controlling eight systems at a dental clinic, migrate its C2 infrastructure, and access the OpenDental database. The AI also assisted with troubleshooting and password guessing.

Jul 15, 2026
Threat Research · unit42.paloaltonetworks.com

TuxBot v3 IoT Botnet Shows Signs of LLM-Assisted Development

Researchers analyzed TuxBot v3 Evolution, an IoT botnet with working brute-force and DDoS capabilities. Recovered code suggests LLM-assisted development, while implementation bugs disable several exploit and fallback command channels.

Jul 15, 2026
Threat Research · opensourcemalware.com

PolinRider Campaign Expands to 4,367 Malicious GitHub Repositories

A July hunt found 2,417 newly compromised repositories linked to PolinRider, bringing the reported total to 4,367 across 2,152 owners. The campaign primarily injects payloads into project config files and also uses malicious font files.

Jul 15, 2026
Threat Research · securelist.com

OkoBot Malware Framework Targets Cryptocurrency Wallets

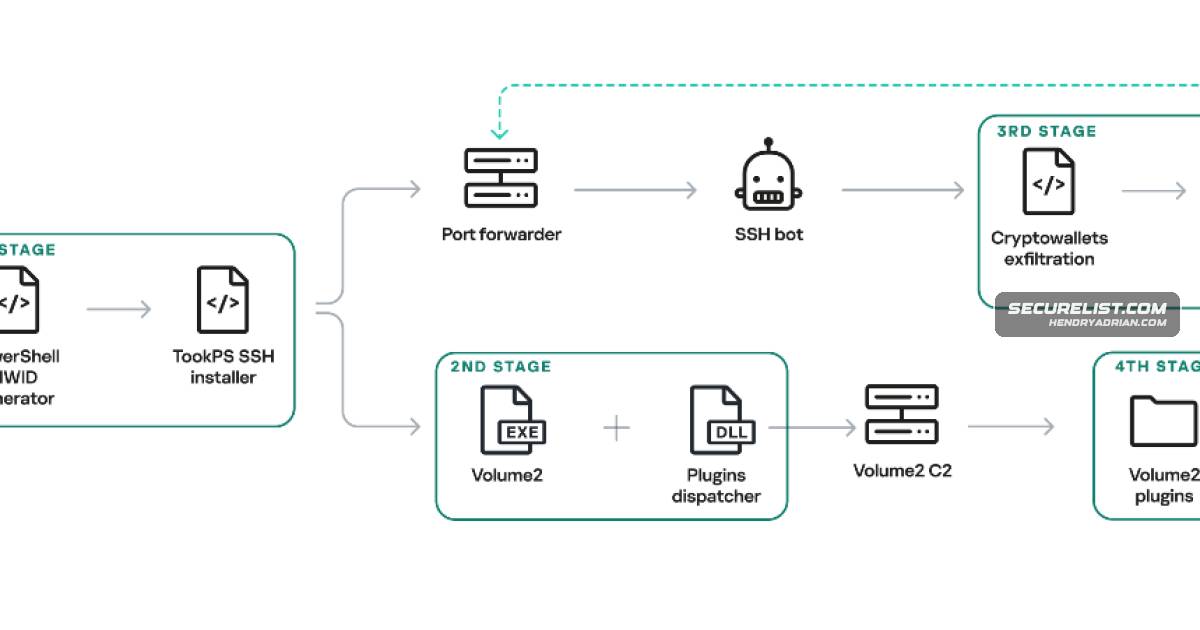
Kaspersky traced OkoBot, an active malware framework that uses TookPS and SSH tunneling to deploy credential theft, spyware and cryptocurrency wallet phishing modules. The campaign has affected hundreds of users in more than 25 countries.

Jul 15, 2026
Threat Research · proofpoint.com

TA458 Uses Half-Click Webmail Exploits to Steal Email and Establish Persistent Access

Proofpoint details TA458’s use of half-click exploits against webmail platforms to steal credentials, contacts, and emails. SpyPress can also establish persistent access on Roundcube, while a SOGo zero-day was patched as CVE-2026-8496.

Jul 15, 2026
Threat Research · proofpoint.com

TA488 Used Zimbra XSS Flaw to Steal Emails and Maintain Access

Proofpoint details how Russia-aligned TA488 exploited CVE-2025-66376 in Zimbra webmail to steal credentials and emails from government and defense targets, establish persistent access, and exfiltrate data.

Jul 15, 2026
Threat Research · wiz.io

Client-Controlled API Flag Bypassed B2B Platform’s Credit Controls, Exposing Contact Data

A security agent found that a B2B platform’s API accepted a client-controlled flag to reveal paywalled contact data without checking account entitlements. The platform fixed the flaw within two hours of triage.

Jul 15, 2026
Threat Research · securityweek.com

Bitdefender Details Windows Bind-Link Techniques That Can Evade EDR

Bitdefender researchers describe three Windows bind-link techniques that can hide attacker-controlled files from EDR tools, including silo-binding. Microsoft rated the findings low severity because they require administrator access.

Jul 15, 2026
Threat Research · bleepingcomputer.com

Arctic Wolf Finds 292 Fake GitHub Repositories Distributing BoryptGrab Infostealer

Arctic Wolf researchers found 292 fake GitHub repositories distributing a BoryptGrab variant. A trojanized DLL sideloaded by a signed updater steals sensitive data and can bypass Chrome App-Bound Encryption through code injection.

Jul 15, 2026
Threat Research · bleepingcomputer.com

Intruder Details AI Pipeline That Found WordPress Plugin SQL Injection CVE

Intruder describes an AI-assisted Joern pipeline that identified CVE-2026-3985, a blind SQL injection in Creative Mail requiring WooCommerce. The plugin was pulled pending review; users are advised to disable it until a patch is available.

Jul 15, 2026
Threat Research · zscaler.com

MacSync Stealer Campaign Uses Malvertising and Shared Claude Chats to Target Mac Users

Zscaler describes a ClickFix campaign that used Google ads and shared Claude chats to deliver MacSync Stealer to Mac users, where it could steal credentials, files, and cryptocurrency data. The shared chats were inaccessible by publication.

Jul 15, 2026
Threat Research · security.com

Daxin Malware Resurfaces in Taiwan Alongside Previously Undocumented Stupig Backdoor

Researchers found Daxin and a previously unknown backdoor, Stupig, on a compromised Taiwanese manufacturer’s host. Stupig can run commands as SYSTEM from the Windows logon screen; a link between the tools is suspected but unconfirmed.

Jul 15, 2026
Threat Research · esentire.com

eSentire Details TAG-150’s ClickFix Chain Delivering DinDoor, DenoRAT and NightshadeC2

eSentire describes a TAG-150 infection at a finance customer, tracing a ClickFix command through DinDoor and DenoRAT to NightshadeC2, and reports that its analysts isolated the affected host.

Jul 15, 2026
Threat Research · sysdig.com

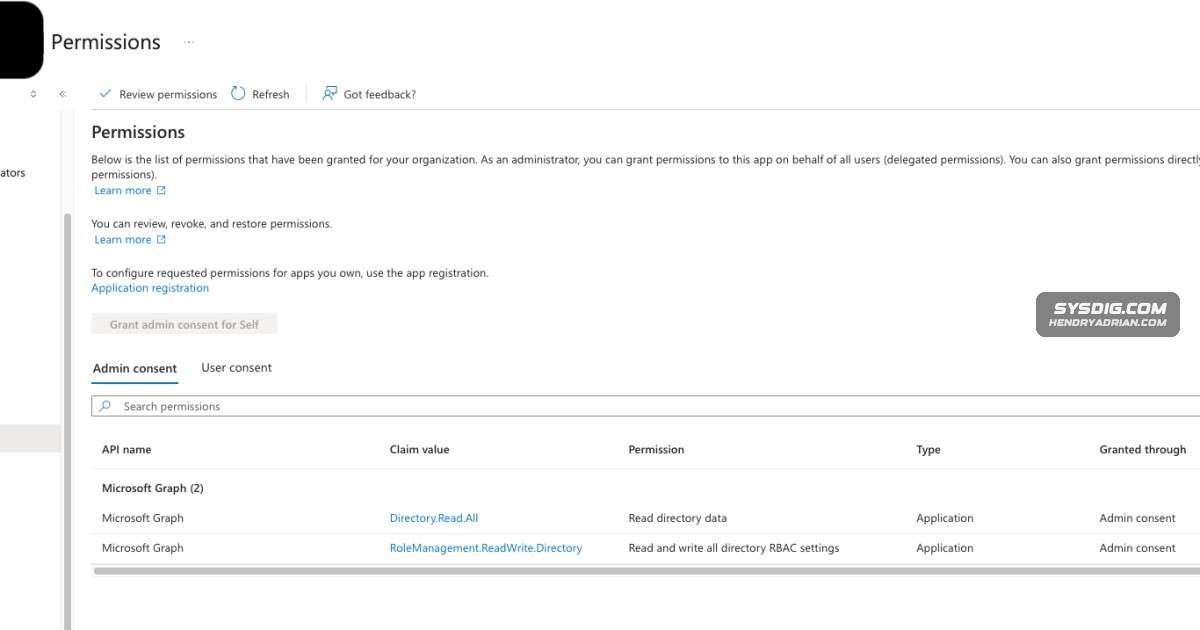
Sysdig Details Azure Tenant Takeover via Leaked Service Principal Secret

Sysdig says an attacker used a leaked Azure service-principal secret to gain Global Administrator and root-level access, harvest keys, and add credentials to 26 app registrations, exposing visibility gaps across five Azure permission planes.

Jul 14, 2026
PreviousPage 43 of 100 Next
© 2026 cyber.hendryadrian.com