
OkoBot Uses In-App Fake Recovery Prompts to Target Ledger and Trezor Users
Summary
Kaspersky details OkoBot, a Windows framework active since April 2025 that injects fake recovery prompts into Ledger and Trezor apps to capture seed phrases. Its toolkit also enables SSH tunneling, RDP access and surveillance; the report does not say how many users gave
Key points
- Kaspersky reports that OkoBot has been active on Windows since April 2025 and observed hundreds of victims across more than 25 countries.
- SeedHunter hooks wallet apps’ Electron internals and injects fake recovery pages into genuine Ledger or Trezor software; it can wait for a wallet device to be connected before displaying the prompt.
- The article says SeedHunter captures typed phrases and sends them as JSON; Kaspersky did not report how many victims entered a phrase.
- Reported entry paths include ClickFix lures and trojanized GitHub software that posed as SQL Server Management Studio but delivered an Audacity build with a malicious implant.
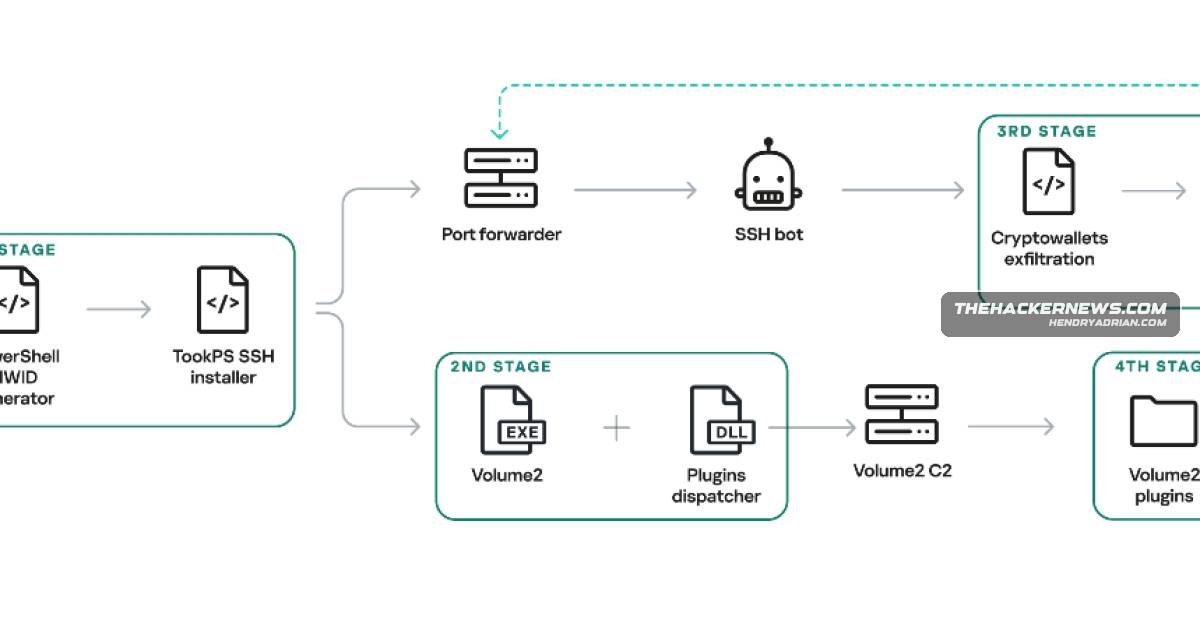
- TookPS establishes SSH tunnels used to collect wallet files, browser data and credentials; the toolkit also enables inbound RDP access and schedules a task to rebuild a reverse tunnel.
- Additional capabilities include window recording, keylogging, screenshots and hidden Chromium extensions; Kaspersky recovered five plugins.
- Kaspersky says it cannot attribute the campaign to a known crimeware actor, and describes Russian-language clues as inconclusive.
Article Details
- Attack Vectors
- OkoBot is delivered through a ClickFix lure or trojanized software; a GitHub repository advertising SQL Server Management Studio instead delivered Audacity containing a malicious implant.
- SeedHunter injects into Ledger Live, Ledger Wallet, or Trezor Suite and hooks the app’s Electron internals to display a fake recovery page. It can wait for a Ledger or Trezor device to be connected before showing the page.
- TookPS downloads the framework, installs SSH, and establishes a tunnel to an attacker-controlled server. An automated SSH bot uses the tunnel to collect files, browser data, and credentials.
- The toolkit enables inbound RDP access and hourly reverse SSH tunnels, and delivers additional modules over SFTP.
- OkoSpyware records selected application windows and keystrokes; MC Keylogger captures input, clipboard and USB activity, and periodic screenshots. A loader also installs hidden Chromium extensions, including Rilide.
- Defensive Notes
- Hunt for the scheduled task named Apple Sync, the listed PROGRAMDATA and USERPROFILE artifacts, and termsrv.dll altered from its shipped build.
- Review unexpected membership in Remote Desktop Users, inbound RDP firewall changes, and outbound SSH connections from user endpoints.
- Check for hidden Chromium extensions in Local Extension Settings that do not appear in the browser’s extension list.
- A recovery-phrase prompt appearing in wallet software after device connection, without a corresponding request on the hardware device screen, is identified as a warning sign.
- The article reports no wallet CVE or vendor patch that closes this endpoint-based attack route.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | moonsand[.]store | SeedHunter contacts this C2 domain. |
MITRE ATT&CK
T1005 · Data from Local SystemThe SSH bot collects wallet files, cookies, browser profiles, and credentials from the infected machine.T1021.001 · Remote Desktop ProtocolThe toolkit opens the firewall for inbound RDP and enables concurrent RDP sessions.T1021.004 · SSHAn automated SSH bot connects back through the tunnel to the infected host.T1027.002 · Software PackingThe article describes the HDUtil launcher as VMProtect-packed.T1041 · Exfiltration Over C2 ChannelCollected files and credentials are sent out through the SSH tunnel.T1053.005 · Scheduled TaskA scheduled task named Apple Sync rebuilds a reverse SSH tunnel hourly.T1055 · Process InjectionA process-injector plugin places SeedHunter into the wallet application process.T1056.001 · KeyloggingMC Keylogger records keystrokes, and SeedHunter captures phrases typed into the fake recovery page.T1059.001 · PowerShellTookPS is a PowerShell downloader executed by both reported infection paths.T1105 · Ingress Tool TransferModules are delivered to the host over SFTP.T1112 · Modify RegistryThe malware writes to the registry to silence Defender notifications.T1113 · Screen CaptureMC Keylogger takes a screenshot every five minutes, and OkoSpyware records selected windows to MP4.T1518.001 · Security Software DiscoveryThe SSH bot inventories installed antivirus software on the infected host.T1548.002 · Bypass User Account ControlThe HDUtil launcher can elevate modules through a Windows RPC UAC bypass.T1572 · Protocol TunnelingTookPS establishes SSH tunnels, including a reverse tunnel for the local RDP port.
Malware
MC KeyloggerMC Keylogger covers input, clipboard, USB devices, and takes a screenshot every five minutes.OkobotOkoBot is a Windows malware framework active since April 2025 that uses its SeedHunter module to steal hardware wallet recovery phrases by injecting fake recovery pages into legitimate Ledger Live, Ledger Wallet, andOkoSpywareOkoSpyware watches for 100-plus executables, Exodus, and 1Password among them.Rilide#OkoBotSeedHunterOkoBot is a Windows malware framework active since April 2025 that uses its SeedHunter module to steal hardware wallet recovery phrases by injecting fake recovery pages into legitimate Ledger Live, Ledger Wallet, andTeviRATTeviRAT is gone. The HDUtil to extl to Rilide chain is gone, folded into a single dispatcher plugin that does the same job.TookPS#OkoBot
Vendors
KasperskyKaspersky found hundreds of victims across more than 25 countries, with notable concentration in Brazil, Vietnam, Canada, Mexico, and Türkiye, while the broader toolkit also enables SSH tunneling, RDP access,Ledgermodule to steal hardware wallet recovery phrases by injecting fake recovery pages into legitimate Ledger Live, Ledger Wallet, and Trezor Suite software.Trezorwallet recovery phrases by injecting fake recovery pages into legitimate Ledger Live, Ledger Wallet, and Trezor Suite software.
Products
AudacityThe SSMS That Was Actually AudacityDefenderIt silences Defender notifications with a registry write and builds itself a desk:Ledger Livemodule to steal hardware wallet recovery phrases by injecting fake recovery pages into legitimate Ledger Live, Ledger Wallet, and Trezor Suite software.Ledger Walletsteal hardware wallet recovery phrases by injecting fake recovery pages into legitimate Ledger Live, Ledger Wallet, and Trezor Suite software.Microsoft WindowsOkoBot is a Windows malware framework active since April 2025 that uses its SeedHunter module to steal hardware wallet recovery phrases by injecting fake recovery pages into legitimate Ledger Live, Ledger Wallet, andTrezor Suiterecovery phrases by injecting fake recovery pages into legitimate Ledger Live, Ledger Wallet, and Trezor Suite software.
Tools
HDUtilA VMProtect-packed launcher called HDUtil runs them and can elevate them silently through a Windows RPC UAC bypass that Project Zero documented in 2019.Volume2The last delivery is Volume2, an open-source utility carrying a malicious protobuf.dll that decrypts and starts the real payload: a plugin dispatcher polling its C2 every 20 seconds.
Countries
BrazilKaspersky found hundreds of victims across more than 25 countries, with notable concentration in Brazil, Vietnam, Canada, Mexico, and Türkiye, while the broader toolkit also enables SSH tunneling, RDP access,Canadafound hundreds of victims across more than 25 countries, with notable concentration in Brazil, Vietnam, Canada, Mexico, and Türkiye, while the broader toolkit also enables SSH tunneling, RDP access, credentialMexicohundreds of victims across more than 25 countries, with notable concentration in Brazil, Vietnam, Canada, Mexico, and Türkiye, while the broader toolkit also enables SSH tunneling, RDP access, credential theft, andVietnamKaspersky found hundreds of victims across more than 25 countries, with notable concentration in Brazil, Vietnam, Canada, Mexico, and Türkiye, while the broader toolkit also enables SSH tunneling, RDP access,