Obfuscated Lua and AutoIt Loaders Deploy RATs and Infostealers in Global Phishing Campaign
Summary
Fortinet details a global phishing campaign using obfuscated JScript droppers and disguised Lua or AutoIt loaders to deploy RATs and infostealers, including Remcos, Agent Tesla, XWorm, and a Snake Keylogger variant.
Key points
- Since late March 2026, attackers have impersonated trusted companies and used business-related or payment-themed phishing emails to deliver malicious archives.
- JScript droppers establish persistence with a scheduled task and unpack interpreter executables, scripts, and encoded payloads.
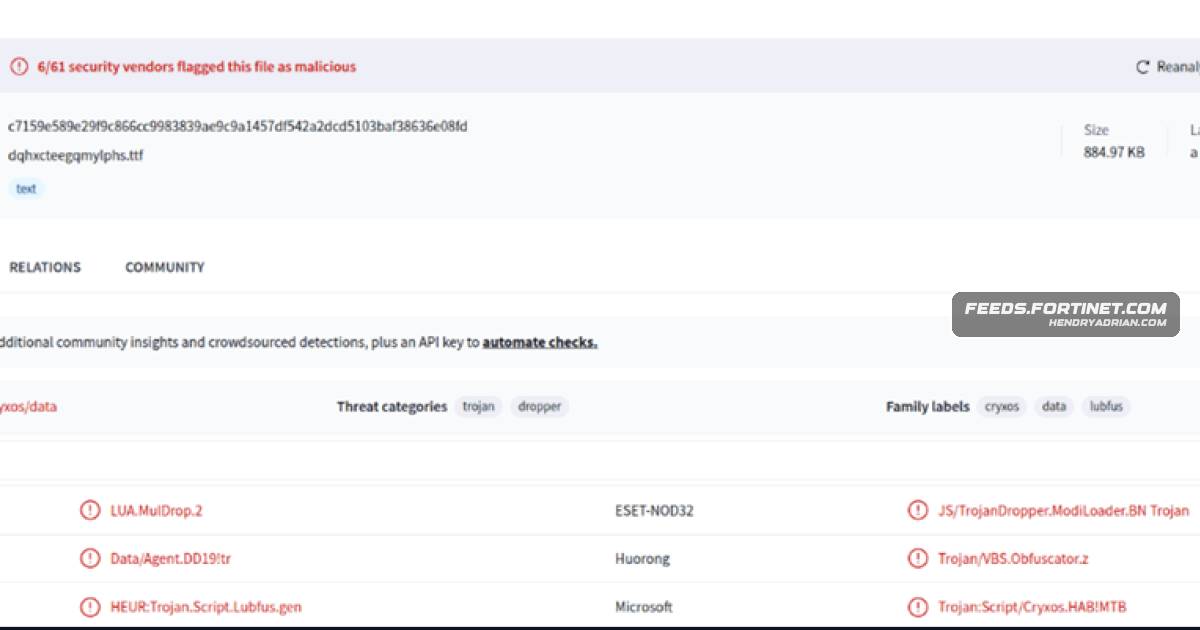
- Lua scripts disguised as .ttf files use custom decoding, memory manipulation, and anti-analysis techniques to execute shellcode.
- An alternative AutoIt loader decrypts a local data file and injects its payload into a suspended process.
- The campaigns deploy Remcos, Agent Tesla, XWorm, and Snake Keylogger variants; Fortinet identifies Best Private LOGGER as a Snake Keylogger variant.
- Fortinet lists antivirus detections and provides command-and-control indicators, URLs, and file hashes.
Article Details
- Attack Vectors
- Phishing emails impersonate reputable companies or use payment-related lures to prompt recipients to open malicious archives or download them from links.
- Obfuscated JScript extracts and launches an AutoIt or Lua-based loader disguised as a .ttf file.
- The AutoIt loader decrypts local data and uses ntdll.dll functions for process injection; the Lua loader decrypts and executes shellcode in memory.
- Defensive Notes
- Fortinet reports that FortiGuard Antivirus detects and blocks the listed malware, and that FortiGate, FortiMail, FortiClient, and FortiEDR support the service.
- The article recommends the FortiGuard CDR service to disarm malicious macros in documents and suggests Fortinet FCF cybersecurity training.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | mail[.]allportcargoservice[.]com | Listed in the article's C2 indicators. |
| DOMAIN | mail[.]taikei-rmc-co[.]biz | Listed in the article's C2 indicators. |
| DOMAIN | mail[.]teamengineersgroup[.]com | Listed in the article's C2 indicators. |
| DOMAIN | mail[.]trimnt[.]com | Listed in the article's C2 indicators. |
| DOMAIN | newremupdate[.]duckdns[.]org | Listed as C2 infrastructure; the source gives port 2404. |
| IPV4 | 104[.]239[.]66[.]86 | Listed as C2 infrastructure; the source gives port 7004. |
| IPV4 | 107[.]174[.]34[.]137 | Listed as C2 infrastructure; the source gives port 443. |
| IPV4 | 46[.]183[.]223[.]21 | Listed as C2 infrastructure; the source gives port 2404. |
| SHA256 | 05390dd0d2c84f77475c0c6aa082638e23977da591302e911cbcb071c42a9451 | Hash listed as a Lua script campaign indicator. |
| SHA256 | 1539468a21a439dd4f8d72a6c34ce503f0585281fc2e88535c3c33727bfdc717 | Hash listed as an AutoIt script campaign indicator. |
| SHA256 | 16516e3298278719123068bf0ed808ea4e00f73c970a8a83377066b4e3c3c950 | Hash listed as an AutoIt script campaign indicator. |
| SHA256 | 16f9692debe0d4e35d76b48312979e5a90a85ce066e7375269ce78f43da52769 | Hash listed as a JScript campaign indicator. |
| SHA256 | 1c4419d687bf45bdc5474b6347e41e89459fc0f5115f0d012c46c57280b242bf | Hash listed as a JScript campaign indicator. |
| SHA256 | 1d9dd914cf623dcae4b88834744a005e5e3eae827ded1aafd23ed1d7be57b90a | Hash listed as a JScript campaign indicator. |
| SHA256 | 2b1248d89fd9a7c716816f9688402942827fc1bfa89d5dccd741521725104279 | Hash listed as an executable campaign indicator. |
| SHA256 | 2fe30eccd36f4346cb117af0cf626c2bca84b50c658b0c9af09110b9f86a53f4 | Hash listed as an executable campaign indicator. |
| SHA256 | 3ace400380bd1fc51e83d008dbbe9ceb70b2572da95264be09d85979a6276a37 | Hash listed as an executable campaign indicator. |
| SHA256 | 417fc4d6119dac40f276b563498a0ad3f9bf42262ec650a4463cbdbe78da388b | Hash listed as a JScript campaign indicator. |
| SHA256 | 41ad1f28134f4b4a443b53af04aeb3fa57a2f72a3cc58a6466e84fc3225f38be | Hash listed as an executable campaign indicator. |
| SHA256 | 4c001e107a42d65c1b1e6092e4aa6932dbd1544d097d1a432ba27e3b4bddfcc1 | Hash listed as an AutoIt script campaign indicator. |
| SHA256 | 5409b3fa21dcc2f854697ec731f9574603dd0b6bdfd892e968a2b412ed85f52c | Hash listed as a Donut shellcode campaign indicator. |
| SHA256 | 5b271a1b1ffe2716ae420f8e9d40dbc8e9e682f6e4125d4f174a335bf070ac29 | Hash listed as a Donut shellcode campaign indicator. |
| SHA256 | 619d2628dcf0c8e15a6febb0e562609556ca57f9f8216800ee77a39e336b8bf4 | Hash listed as a JScript campaign indicator. |
| SHA256 | 6700e6d2a0c285d3ebf1a55aecec63b1e42d7d581f691331c667a8920dac7029 | Hash listed as a JScript campaign indicator. |
| SHA256 | 775ae9a8c7363e2368cbb559f9c2d26a6c479d4e7998fe71d45830885ccde429 | Hash listed as a Donut shellcode campaign indicator. |
| SHA256 | 7df42fc54f053d1bb65f43d4386a75be02770f7923b66e713fb04631582e864e | Hash listed as a Donut shellcode campaign indicator. |
| SHA256 | 81edd5e740bea0fefb5c1bbd14a671bd1daff37bf3641e34f3a1f7e93559184a | Hash listed as a JScript campaign indicator. |
| SHA256 | 8c28bc87eb4f2613117d41a716e78f62d55c19edaeea573c2c96e787da055167 | Hash listed as a Lua script campaign indicator. |
| SHA256 | 9674da676ee226ee456d35c774715d9b58655423806f281de19dc9ef899e9532 | Hash listed as a PDF campaign indicator. |
| SHA256 | 96e22da4d5c0ea4b0efde0ad3eaa8fdedc60228f84fb3c56899afbb9338da2a1 | Hash listed as a JScript campaign indicator. |
| SHA256 | 986d1d5270822af7d7744762ecd8fc4e9b2886c85b3660e9fdf0b5906d6c4117 | Hash listed as a Donut shellcode campaign indicator. |
| SHA256 | b12b743d4ecc0fe7320b6c1533e2a60bb89f94ca39a5be37143e7af27daacf04 | Hash listed as a Lua script campaign indicator. |
| SHA256 | bbeb74e6af12536ecb6761a65ed893fbddd1b86a17cd4a61b616e5fc6106ec9a | Hash listed as a Lua script campaign indicator. |
| SHA256 | be4fcf88a287f783a3d199e889f9f088f77338eafe0dce70a38ade01192fb223 | Hash listed as a Lua script campaign indicator. |
| SHA256 | c7159e589e29f9c866cc9983839ae9c9a1457df542a2dcd5103baf38636e08fd | Hash listed as a Lua script campaign indicator. |
| SHA256 | c92740b6b90582a4bf73fef979ca047b9e6ae432e892a97f71e70b45c09e478e | Hash listed as an executable campaign indicator. |
| SHA256 | ca9639f7db6c3d1b37a004493f44aaa4e1282ea9333bc8ca5eac5d263d899e6a | Hash listed as an executable campaign indicator. |
| SHA256 | cc041def6013da331f025e12f21f43677cea08073018d6be037f15a343a9cc24 | Hash listed as an executable campaign indicator. |
| SHA256 | e2a95dd038a153dfb463c94554912f992cd04cf0f420552a95f4aea3d6f31e18 | Hash listed as a Donut shellcode campaign indicator. |
| SHA256 | ec494785f243f5f1b516b31d8455fadafe5495e11d47a5ce2bd50b1b3791fec6 | Hash listed as an executable campaign indicator. |
| SHA256 | fbf9a87d351ef702d87e0cd9e0148baa44c6d619f50fbf91d79a1c5e37719a77 | Hash listed as a Donut shellcode campaign indicator. |
| URL | hxxps[:]//cdn[.]discordapp[.]com/attachments/1499192125093449759/1511147377979818074/F10097782_Request-9200090_0990[.]PDF[.]JS | Specific Discord-hosted URL listed as a campaign URL indicator for a malicious PDF/JS file. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe JScript and Lua loaders use extensive obfuscation, junk code, encoded strings, and disguised file extensions to impede analysis and detection.T1053.005 · Scheduled TaskThe JScript dropper establishes persistence by creating a Scheduled Task.T1055 · Process InjectionThe AutoIt loader uses low-level ntdll.dll functions for process injection; an earlier Lua sample writes shellcode to a remote process and starts it with CreateRemoteThread.T1059.007 · JavaScriptAn obfuscated JavaScript/JScript file extracts and launches the next stage.T1566.001 · Spearphishing AttachmentThe campaigns use phishing emails containing malicious archives as attachments.T1566.002 · Spearphishing LinkPhishing emails may instead link recipients to download a malicious archive.T1620 · Reflective Code LoadingA Donut reflective loader maps and executes the payload directly in memory.
People
Malware
Agent Teslaand Lua-based loaders with low detection rates to deploy various malware families, including Agent Tesla, Remcos, XWorm, and Best Private LOGGER.Best Private LOGGERlow detection rates to deploy various malware families, including Agent Tesla, Remcos, XWorm, and Best Private LOGGER.Remcosand Lua-based loaders with low detection rates to deploy various malware families, including Agent Tesla, Remcos, XWorm, and Best Private LOGGER.Snake KeyloggerThe identified payloads include Remcos, Agent Tesla, XWorm, and Snake Keylogger variants.Snake VIP KeyloggerAdditionally, we acquired a Snake VIP Keylogger builder and used it to generate both protected and unprotected versions of the payload for comparative analysis, shown in Figure 24.XWormloaders with low detection rates to deploy various malware families, including Agent Tesla, Remcos, XWorm, and Best Private LOGGER.
Vendors
Products
FortiClientFortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard Antivirus Service.FortiEDRFortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard Antivirus Service.FortiGateFortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard Antivirus Service.FortiGuard AntivirusThe malware described in this report are detected and blocked by FortiGuard Antivirus as:FortiGuard CDRThe FortiGuard CDR (content disarm and reconstruction) service can disarm the malicious macros within the document.FortiMailFortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard Antivirus Service.Microsoft WindowsAffected Platforms: Microsoft Windows
Tools
AutoItTo evade detection, the actor employs multi-layered, highly obfuscated stages, including extensive junk code and an AutoIt/Lua loader masquerading as a TrueType Font (.ttf) file.DonutThe function scans for byte sequences and string signatures characteristic of Donut shellcode, then obfuscates them with a mask composed of 144, 204, and randomly generated uppercase characters to evade detection.LuaJITThese dropped files may include an executable for an AutoIt interpreter or LuaJIT, along with accompanying scripts and encoded data.