
OkoBot Malware Framework Targets Cryptocurrency Wallets
Summary
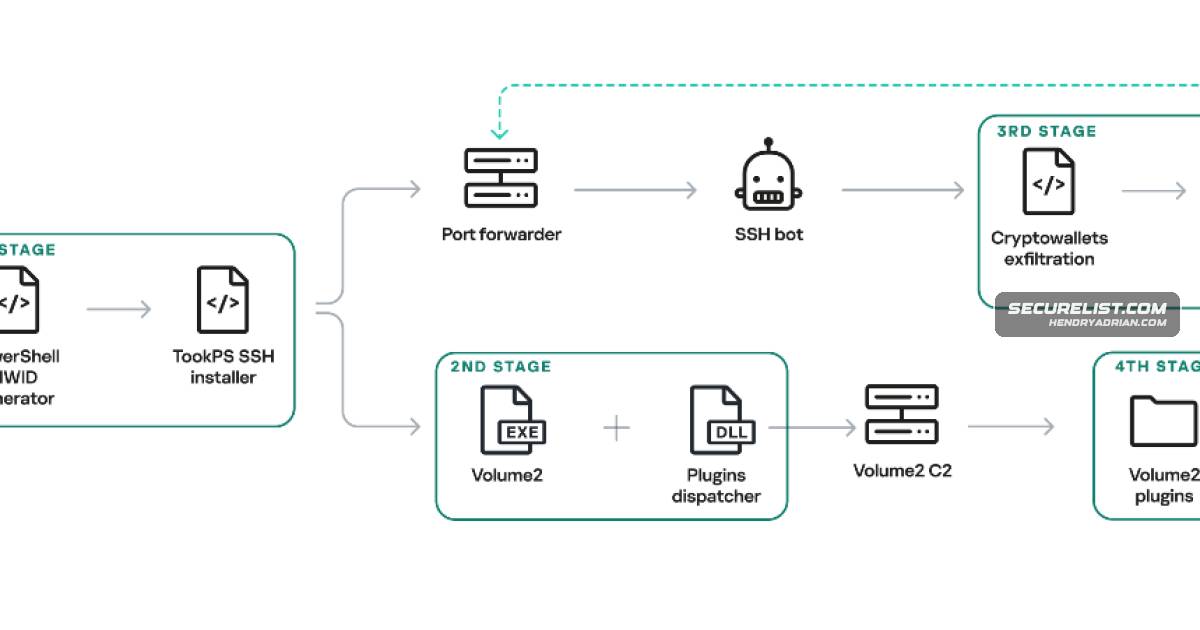
Kaspersky traced OkoBot, an active malware framework that uses TookPS and SSH tunneling to deploy credential theft, spyware and cryptocurrency wallet phishing modules. The campaign has affected hundreds of users in more than 25 countries.
Key points
- ClickFix lures and fake software on GitHub initiate infections with the TookPS PowerShell downloader.
- An automated SSH bot collects credentials and wallet files, configures remote access and retrieves modules over SFTP.
- A malicious plugin dispatcher loads modules for command execution, process injection and additional payload delivery.
- SeedHunter injects into Trezor and Ledger applications and displays phishing pages to capture wallet seed phrases.
- OkoSpyware records targeted application windows and keystrokes, while a separate keylogger captures clipboard data and screenshots.
- In a newer campaign phase, the Volume2 plugin dispatcher replaced the earlier extension-loader chain and TeviRAT.
- Kaspersky detected hundreds of victims across more than 25 countries but could not attribute the campaign to a known actor.
Article Details
- Attack Vectors
- ClickFix lures and fake software distributed through GitHub execute the TookPS PowerShell downloader.
- TookPS establishes an SSH tunnel through which an automated bot collects data and retrieves malicious modules over SFTP.
- A fake SSMS package embeds a malicious implant in a library of the legitimate Audacity application.
- SeedHunter injects into wallet applications and displays phishing pages to capture hardware-wallet seed phrases.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 2baserec2[.]guru | TookPS infrastructure identified in the indicator list. |
| DOMAIN | coffeesaloon[.]online | TookPS infrastructure identified in the indicator list. |
| DOMAIN | kbeautyreviews[.]com | TookPS infrastructure identified in the indicator list. |
| DOMAIN | livewallpapers[.]online | Volume2 dispatcher C2 domain. |
| DOMAIN | moonsand[.]store | SeedHunter C2 domain used to receive stolen seed phrases. |
| DOMAIN | recavb22[.]online | TookPS infrastructure identified in the indicator list. |
| DOMAIN | thatwascringe[.]com | Volume2 dispatcher C2 domain. |
| IPV4 | 104[.]243[.]32[.]213 | SSH bot infrastructure. |
| IPV4 | 104[.]243[.]43[.]16 | SSH bot infrastructure. |
| IPV4 | 62[.]210[.]188[.]209 | SSH bot infrastructure. |
| MD5 | 11dbc8a2bea04b15f8f68f3f01e8faf9 | Malicious extl.exe browser-extension injector. |
| MD5 | 187a1f68ae786e53d3831166dc84e6d2 | Malicious protobuf.dll dispatcher artifact. |
| MD5 | 2157d2429124ad28db7a26f2477cb985 | Malicious environment enumerator plugin. |
| MD5 | 3d2b43f91f65bfbf36a9c71b6b418876 | Malicious ext_daemon.exe injector payload. |
| MD5 | 70fef9fd6e351f4d53cfeee8dcdfcd99 | SeedHunter injector payload. |
| MD5 | 7306885bb4c98f2a9f056104cf092bc9 | Malicious PowerShell wrapper plugin. |
| MD5 | 77cecf5e2a622ae07d8ae9913457ab57 | Malicious dropper plugin. |
| MD5 | 83e6b8fcb92a0b13e109301f8ff649cf | Malicious version.dll dispatcher artifact. |
| MD5 | ac93a821617aea1f56d4bc0bef4af327 | Malicious HDUtil.exe SSH bot utility. |
| MD5 | acd31c9941b6c1cabd4e45e6877b9038 | Malicious keylog_x64.dll injector payload. |
| MD5 | b07d451ee65a1580f20a784c8f0e7a46 | Malicious protobuf.dll dispatcher artifact. |
| MD5 | b4c2e16cdb513be4dc798f88e2527334 | Malicious CMD wrapper plugin. |
| MD5 | d84e8dc509308523e0209d3cd3544619 | Malicious protobuf.dll dispatcher artifact. |
| MD5 | dd52f5108a176c62ad807c327734ad12 | Malicious oko.dll injector payload. |
| MD5 | e0c3bc27a65750e740c4f1719e531c7d | Malicious process injector plugin. |
MITRE ATT&CK
T1021.004 · SSHTookPS establishes an SSH tunnel through which an automated bot accesses the victim system.T1041 · Exfiltration Over C2 ChannelSeedHunter sends stolen wallet seed phrases to its C2 in JSON payloads.T1053.005 · Scheduled TaskThe Apple Sync scheduled task maintains a reverse SSH tunnel forwarding the local RDP port.T1055 · Process InjectionThe extension loader injects an implant into Chromium-based browser processes, and SeedHunter injects into wallet applications.T1056.001 · KeyloggingMC Keylogger and OkoSpyware record keystrokes, including input in targeted application windows.T1059.001 · PowerShellTookPS executes PowerShell scripts for initial infection and artifact exfiltration.T1071.001 · Web ProtocolsThe dispatcher polls its C2 over HTTP, while SeedHunter communicates with its C2 over HTTPS.T1105 · Ingress Tool TransferThe SSH bot retrieves malicious modules over SFTP.T1112 · Modify RegistryThe SSH bot modifies the registry to disable Windows Defender notifications.T1113 · Screen CaptureMC Keylogger takes screenshots every five minutes, while OkoSpyware records targeted application windows.T1115 · Clipboard DataMC Keylogger records clipboard text and file paths and saves copied images.T1136.001 · Local AccountThe SSH bot creates a user in the Remote Desktop Users group.T1176 · Software ExtensionsThe loader silently installs malicious browser extensions, including Rilide, and hides them from the user.T1548.002 · Bypass User Account ControlHDUtil uses Windows RPC and an auto-elevated msconfig.exe to bypass UAC.T1574.002 · DLL Side-LoadingVolume2 loads a modified protobuf.dll, later named version.dll, that launches the malicious dispatcher.
Malware
HDUtil[File names] malicious loader, dispatcher, and payloads – HDUtil.exe, extl.exe, ext_daemon.exe, and 2 more filesMC KeyloggerAll files created by the MC Keylogger and OkoSpyware are sent to the C2 server to the endpoint ir-post.php.OkoSpyware#TookPSRilide#TookPSSeedHunter#TookPSTeviRAT#TookPSTookPSKaspersky identified the active OkoBot campaign, a multi-stage framework that uses TookPS, SSH tunneling, browser extension theft, keylogging, and spyware to steal cryptocurrency wallets and other credentials.
Products
AudacityIn fact, it is actually the legitimate Audacity — a popular audio editor — compiled with a malicious implant embedded in one of its libraries.Ledger LiveSimilarly to extl.exe, this malware monitors the list of active processes in the system and injects an implant into Trezor Suite, Ledger Wallet, and Ledger Live processes.Ledger WalletSimilarly to extl.exe, this malware monitors the list of active processes in the system and injects an implant into Trezor Suite, Ledger Wallet, and Ledger Live processes.SSMSInitial infection is delivered through ClickFix lures and fake software hosted on GitHub, including a disguised SSMS package.Trezor SuiteSimilarly to extl.exe, this malware monitors the list of active processes in the system and injects an implant into Trezor Suite, Ledger Wallet, and Ledger Live processes.Volume2#TookPS
Countries
BrazilThe campaign has affected hundreds of victims across more than 25 countries, with the largest concentration in Brazil, Vietnam, Canada, Mexico, and Türkiye.CanadaThe campaign has affected hundreds of victims across more than 25 countries, with the largest concentration in Brazil, Vietnam, Canada, Mexico, and Türkiye.MexicoThe campaign has affected hundreds of victims across more than 25 countries, with the largest concentration in Brazil, Vietnam, Canada, Mexico, and Türkiye.TürkiyeThe campaign has affected hundreds of victims across more than 25 countries, with the largest concentration in Brazil, Vietnam, Canada, Mexico, and Türkiye.VietnamThe campaign has affected hundreds of victims across more than 25 countries, with the largest concentration in Brazil, Vietnam, Canada, Mexico, and Türkiye.