cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2388 articles

Threat Research · bleepingcomputer.com

Pillar Security demonstrates sandbox escapes in four AI coding agents

Pillar Security demonstrated sandbox escapes in Cursor, Codex CLI, Gemini CLI and Antigravity using workspace files that trusted host tools later executed or scanned. Several flaws were patched; Google downgraded two Antigravity findings.

Jul 20, 2026
Threat Research · thehackernews.com

HollowGraph Uses Microsoft 365 Calendar Events for C2 and Data Exfiltration

Group-IB says HollowGraph uses compromised Microsoft 365 calendars and Graph API traffic for tasking and encrypted file exfiltration, refreshes Entra ID credentials over DNS, and is linked to Cavern; the campaign’s operator remains unattributed.

Jul 20, 2026
Threat Research · thehackernews.com

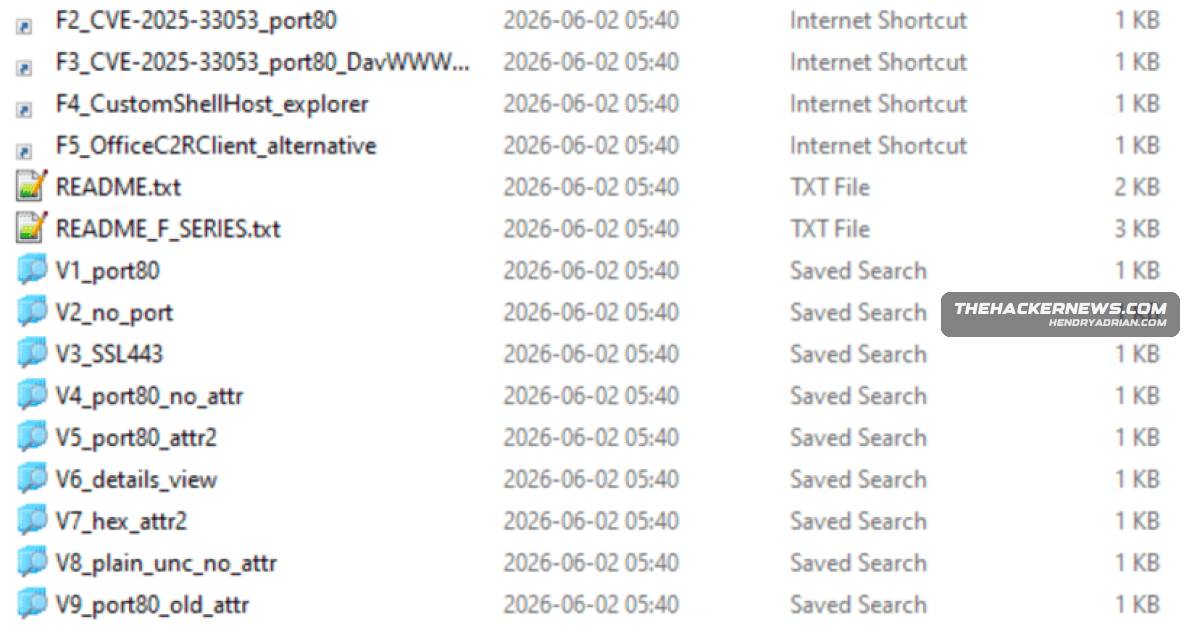
Rapid7 Finds Evidence of AI-Assisted Phishing Toolkit in WebDAV Malware Campaign

Rapid7 says an exposed server held 1,048 files documenting an apparently AI-assisted phishing toolkit and an active Mexico campaign using a fake CURP site and WebDAV delivery tied to CVE-2025-33053. Recorded launch events do not confirm infections.

Jul 20, 2026
Threat Research · bleepingcomputer.com

HollowGraph Malware Uses Microsoft 365 Calendars for Covert C2

Group-IB says HollowGraph uses compromised Microsoft 365 calendars for covert C2 and data theft, with DNS tunneling to refresh Entra ID credentials. Researchers link it to Cavern but say evidence is insufficient to attribute it to Lyceum.

Jul 20, 2026
Threat Research · zscaler.com

ThreatLabz Details TELESHIM Malware Campaign Targeting Middle East Government Entities

ThreatLabz analyzes a July 2026 campaign targeting Middle East government entities, detailing the TELESHIM backdoor’s Telegram-based C2, post-compromise activity, and the MIXEDKEY loader that decrypts and loads BINDCLOAK.

Jul 20, 2026
Threat Research · hunt.io

Exposed Server Staged NGINX and Ghost CMS Exploits for Targets in 11 Countries

Researchers found an exposed server hosting exploits and target lists spanning 11 countries. Scripts used DNS callbacks to check execution, but recovered evidence did not confirm successful compromises.

Jul 20, 2026
Threat Research · aikido.dev

SleeperGem Campaign Targets Dormant RubyGems Maintainer Accounts

Aikido reports that malicious RubyGems releases used git_credential_manager to fetch and run binaries, with a load-time trigger and CI-environment checks. The dependency also appeared in Dendreo; another affected release belonged to a separate maintainer.

Jul 19, 2026
Threat Research · stepsecurity.io

Researchers Trace SleeperGem RubyGems Campaign Dropping Persistent Backdoors

StepSecurity analyzed three RubyGems packages in the SleeperGem campaign, finding CI-evasion checks and a loader that downloads a daemon, installs systemd and cron persistence, and may attempt privilege escalation. The article provides cleanup and credential-rotation 步骤

Jul 19, 2026
Threat Research · bleepingcomputer.com

Microsoft Reports Surge in ACR Stealer Attacks Using ClickFix, WebDAV and MSHTA

Microsoft reports a surge in ACR Stealer attacks targeting enterprise customers. The campaigns use ClickFix, WebDAV and MSHTA to deliver malware that collects browser credentials, tokens and sensitive files.

Jul 18, 2026
Threat Research · thehackernews.com

ViteVenom Uses Seven Malicious npm Packages and Blockchain C2 to Deliver a RAT

Checkmarx identified seven malicious npm packages targeting Vite as part of ViteVenom, an expansion of ChainVeil attributed to SuccessKey. The malware uses blockchain infrastructure to retrieve payloads and deliver a RAT.

Jul 18, 2026
Threat Research · resecurity.com

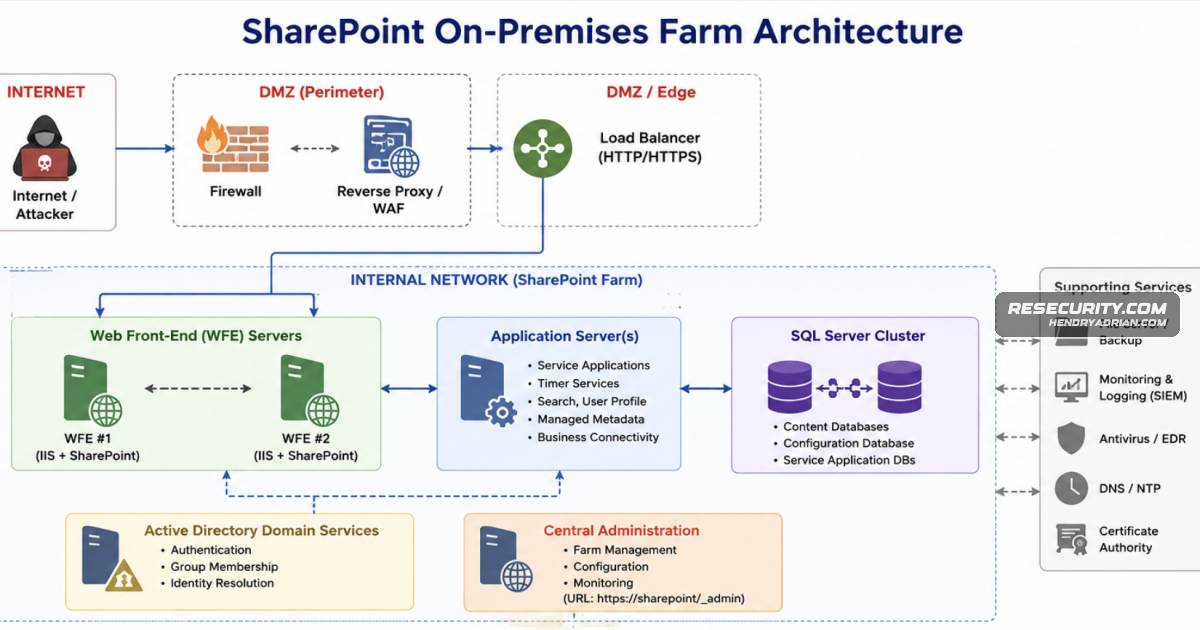
July 2026 SharePoint Flaw Analysis Details Exploit Chains and Defenses

The article says CISA confirmed active exploitation of three of six flaws in on-premises SharePoint Server. It describes web-shell and machine-key theft techniques, lists affected builds and patches, and recommends AMSI scanning, threat hunting, and network hardening.

Jul 18, 2026
Threat Research · elastic.co

Elastic Details Contagious Interview Campaign Using SVG Steganography to Target Developers

Elastic details REF9403, a Contagious Interview campaign using fake coding challenges and SVG steganography to target developers. Startup-triggered payloads steal credentials, wallet data, files and clipboard contents and provide a Socket.IO RAT.

Jul 17, 2026
Threat Research · opensourcemalware.com

Researchers Link ChainVeil and ViteVenom npm Malware to DPRK’s PolinRider Campaign

OpenSourceMalware links the ChainVeil and ViteVenom npm campaigns to PolinRider, citing identical blockchain wallets and XOR keys, shared markers, and overlapping targeting of developer tools.

Jul 17, 2026
Threat Research · volexity.com

Volexity Details Zero-Day Exploitation of SonicWall SMA VPN Appliances

Volexity traced UTA0533’s compromise of SonicWall SMA 1000 appliances to two zero-days, detailing the exploit chain, malware, post-compromise activity, indicators, and available patches.

Jul 17, 2026
Threat Research · seqrite.com

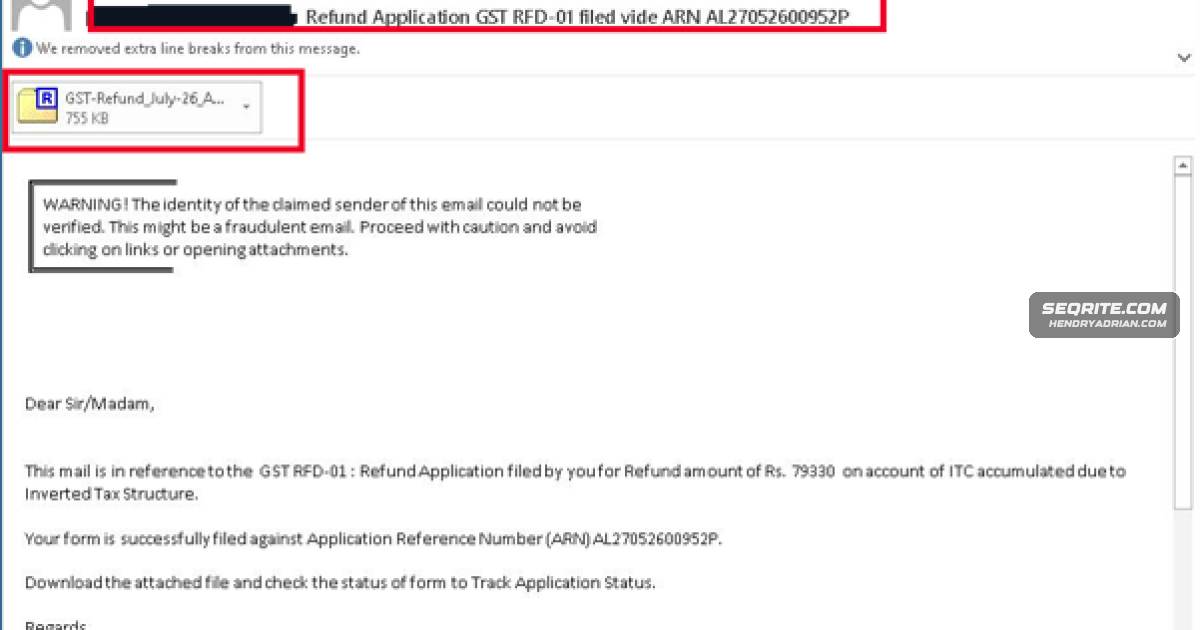
Seqrite Details GST Phishing Chain Delivering Remcos RAT Through .NET Loaders

Seqrite analyzed a GST-themed phishing campaign targeting Indian businesses and taxpayers. Its multi-stage .NET chain concealed payloads in bitmap pixels and delivered Remcos RAT, with fileless execution and persistence techniques.

Jul 17, 2026
Threat Research · levelblue.com

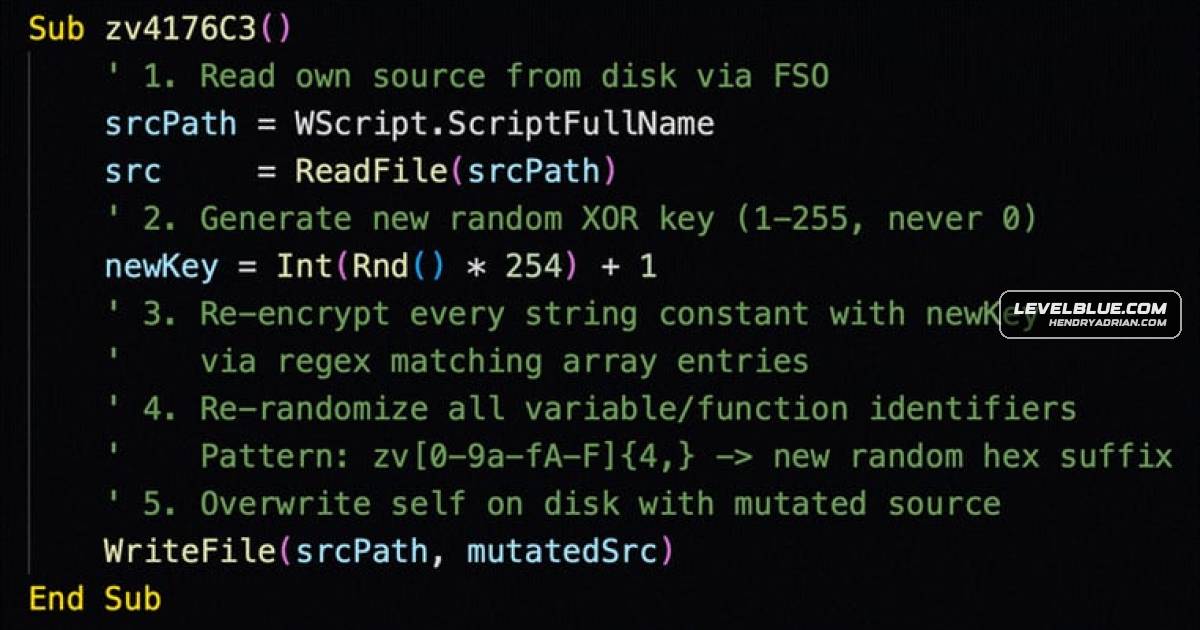
Blind Eagle Updates Loaders and AsyncRAT Toolkit

LevelBlue researchers report new Blind Eagle loader techniques and a customized AsyncRAT build featuring WNF injection and browser profile cloning. Shared Photo Studio artifacts link multiple toolchains.

Jul 17, 2026
Threat Research · securelist.com

GoSerpent Campaign Uses Staged Tools for Data Collection and Exfiltration in Southeast Asia

Researchers describe GoSerpent activity targeting Southeast Asian government and diplomatic entities, using RATs, credential-dumping and file-collection tools, then Stowaway and TmcLoader/TmcPayload for configured network-share exfiltration. A possible TetrisPhantom tie

Jul 17, 2026
Threat Research · reversinglabs.com

ClickFix Uses Fake Verification Pages and Trusted Tools to Deliver Malware

A ReversingLabs investigation details ClickFix attacks using fake verification pages and clipboard-injected commands. One university site reportedly exposed 5–10 students’ browser data; researchers matched 4,000+ samples and recommend behavior-based detection and system

Jul 17, 2026
Threat Research · levelblue.com

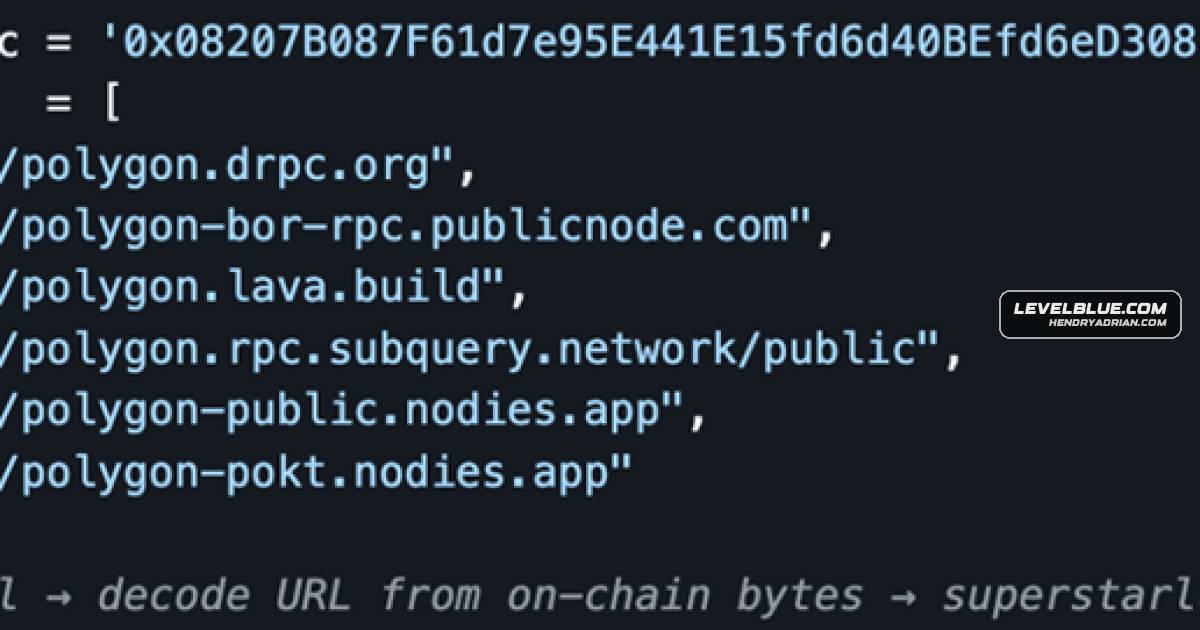
ClickFix Campaign Uses Polygon Smart Contracts to Deliver macOS Infostealer

LevelBlue researchers report finding hundreds of compromised WordPress sites used in a ClickFix campaign. They describe Polygon-based C2 resolution and a macOS infostealer that collects sensitive data and sends it to genomicsforge[.]com.

Jul 17, 2026
Threat Research · kudelskisecurity.com

Researchers Map Evolving Network Infrastructure of DPRK Fake IT Workers

Kudelski Security uses public data and stealer logs to map changes in DPRK fake IT worker infrastructure, identify VPN exit nodes and internal network clusters, and assess possible organizational links with varying levels of confidence.

Jul 17, 2026
Threat Research · huntress.com

Huntress Details SafePay Ransomware Tactics and Detection Opportunities

Huntress analyzes two SafePay ransomware incidents, detailing RDP access with valid credentials, data archiving, network-share encryption, malware behavior, and detection opportunities.

Jul 17, 2026
Threat Research · bleepingcomputer.com

ClickLock macOS Stealer Forces Password Prompts and Installs GSocket Backdoor

Group-IB reports that ClickLock uses fake verification and repeated password prompts to steal macOS credentials and other data. Researchers say it affected at least 100 systems in 33 countries and can install a persistent GSocket backdoor.

Jul 16, 2026
Threat Research · proofpoint.com

Cruciferra Crypter Uses Extensive Evasion to Deliver RATs and Infostealers

Proofpoint analyzes Cruciferra, a crypter used by multiple threat actors to deliver RATs and infostealers. The service employs techniques including BYOVD, indirect syscalls, custom encryption, and modified Process Ghosting to evade defenses.

Jul 16, 2026
Threat Research · securelist.com

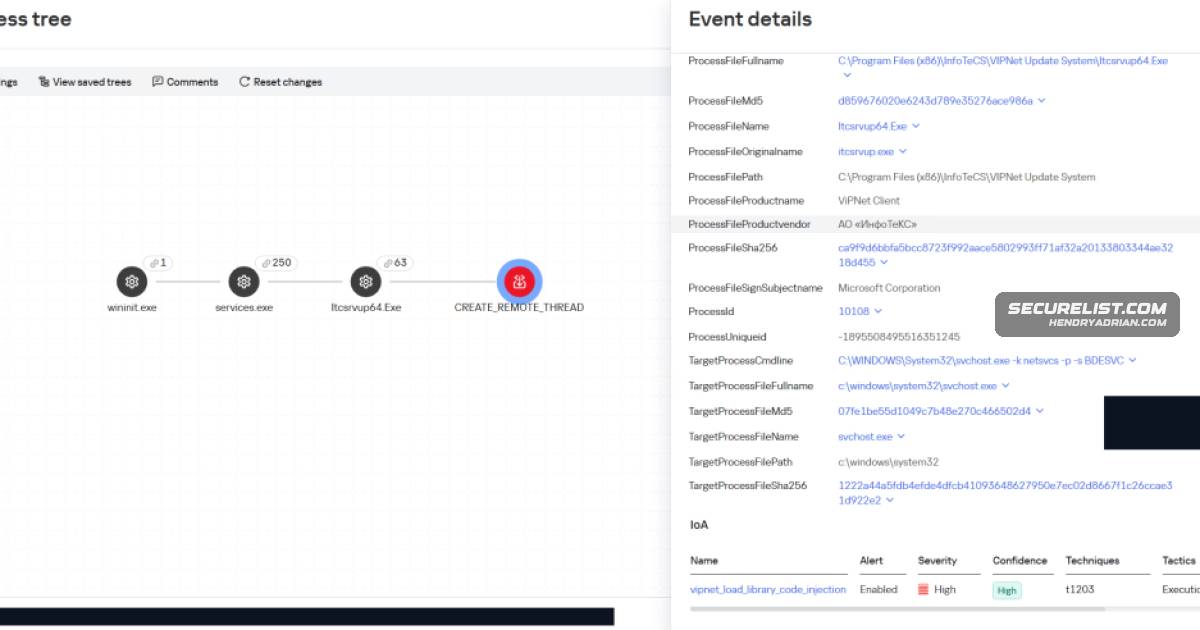
ViPNet Update System Abused to Deploy Five Malicious Modules

Researchers describe an active campaign since at least May 2026 that abuses the ViPNet update system to deploy five malicious modules, including a Rust backdoor. They link it with low confidence to an unknown Chinese-speaking APT group.

Jul 16, 2026
PreviousPage 42 of 100 Next
© 2026 cyber.hendryadrian.com