
Blind Eagle Updates Loaders and AsyncRAT Toolkit
Summary
LevelBlue researchers report new Blind Eagle loader techniques and a customized AsyncRAT build featuring WNF injection and browser profile cloning. Shared Photo Studio artifacts link multiple toolchains.
Key points
- Researchers collected samples from exposed staging servers between late May and early July 2026.
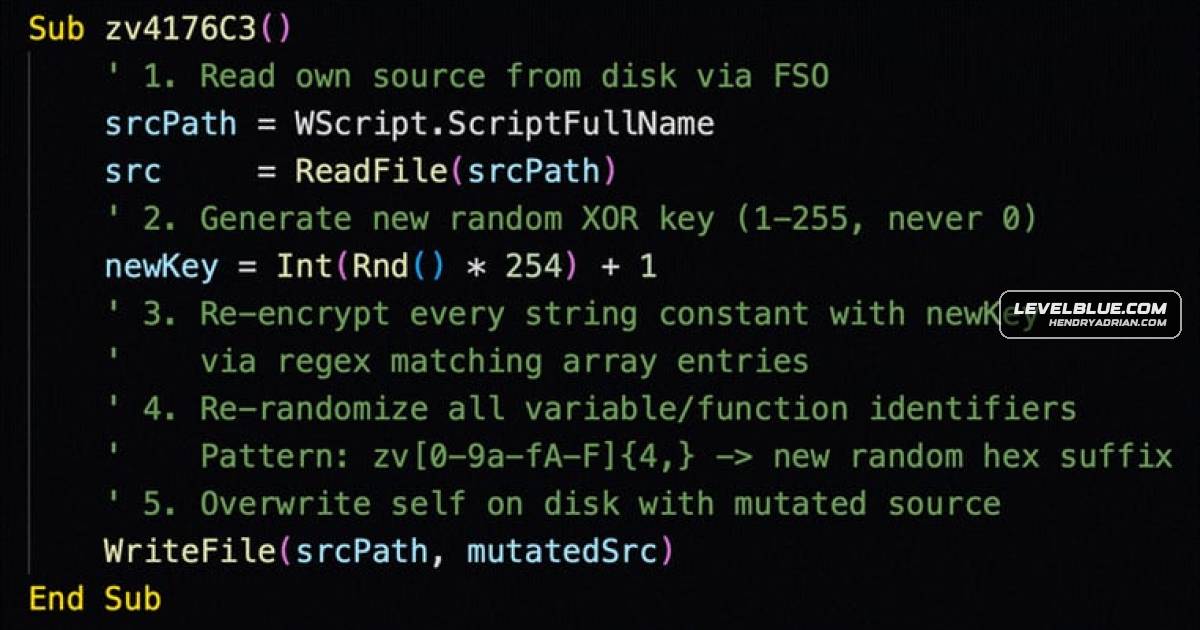
- One VBScript loader rewrites its encrypted strings and identifiers on execution, changing its file hash; another uses a JavaScript AES implementation with a custom S-box and round constants.
- A GitHub-staged chain pairs a legitimate AutoIt interpreter with a separately downloaded script that performs process hollowing and parent-process spoofing.
- Three loader families share Photo Studio persistence code, suggesting a common builder, although researchers did not observe the task-creation routine being invoked in the analyzed code paths.
- The JC-46 AsyncRAT chain uses a custom Base28 encoding and a .NET injector that researchers say uses Windows Notification Facility callbacks, with process hollowing as a fallback.
- Researchers describe hidden-desktop banking fraud, Chromium profile cloning and a Chrome App-Bound Encryption v20 bypass in the customized RAT.
- Suggested hunting pivots include Photo Studio artifacts, script-host-to-PowerShell execution chains and AutoIt scripts launched from user-writable directories.
Article Details
- Attack Vectors
- Spanish-language phishing against Colombian and broader Latin American targets delivers VBScript droppers and commodity RATs.
- Exposed Apache staging directories hosted obfuscated VBScript, JavaScript, batch and AutoIt loader chains.
- VBScript downloaders use PowerShell to retrieve a legitimate AutoIt3 interpreter and a separately staged malicious script from GitHub.
- JC-46 uses WNF-based process injection, hidden desktop access and cloned browser profiles to support banking fraud.
- Defensive Notes
- Detect wscript.exe or cscript.exe spawning PowerShell followed by process injection or hollowing into RegSvcs.exe, MSBuild.exe, jsc.exe or AppLaunch.exe.
- Correlate downloads from trusted services with subsequent execution from user-writable directories; alert on AutoIt3 executing a non-.au3 script from such locations.
- Hunt for the Photo Studio scheduled task and PhotoStudioVBS local application data folder. The scheduled-task creation routine was present in analyzed samples but not observed executing in the statically analyzed paths.
- Monitor for browser profile cloning, non-browser access to Chromium profile data, parent-process spoofing and WNF-based injection.
- Avoid relying on hashes alone for the self-mutating VBScript loader; hunt for its recurring XOR and PowerShell decryption patterns.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | rema200426[.]duckdns[.]org | JC-46 AsyncRAT command-and-control domain. |
| IPV4 | 178[.]16[.]52[.]80 | Open-directory staging server hosting the batch, VBScript and JavaScript dropper chain. |
| IPV4 | 181[.]235[.]8[.]24 | Open-directory staging server hosting the custom stream-cipher loader family. |
| IPV4 | 46[.]246[.]84[.]5 | Open-directory staging server hosting self-mutating VBScript droppers. |
| IPV4 | 64[.]89[.]160[.]17 | Open-directory staging server hosting the AutoIt RunPE loader chain. |
| SHA256 | a4fbd707f4ce7ca68e6137cef1c56b6f408e5f0a0f148434d996bb98c3a21fff | SHA-256 of Paralell.dll, the JC-46 WNF process injector. |
| SHA256 | a73cb9d5d46e19f3daa4a14cfe5d8fa4319a3d62452039e4972e6a316bbb26f4 | SHA-256 of Client1.exe, the JC-46 AsyncRAT payload. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationLoader chains conceal strings and payloads with XOR, custom ciphers, AES and Base28 encoding.T1036 · MasqueradingLoader stages disguise their persistence components as Photo Studio or a photo viewer.T1053.005 · Scheduled TaskThree loader families contain callable code to create a Photo Studio scheduled task, although the analyzed paths did not invoke it.T1055 · Process InjectionParalell.dll uses WNF callbacks to inject the JC-46 payload into MSBuild.exe.T1055.012 · Process HollowingLoaders hollow processes including RegSvcs.exe, AppLaunch.exe and jsc.exe.T1056.001 · KeyloggingThe JC-46 AsyncRAT build includes a keylogger.T1059.001 · PowerShellLoaders execute in-memory PowerShell decryptors and a payload orchestrator.T1059.005 · Visual BasicVBScript droppers and downloaders assemble and launch later stages.T1059.007 · JavaScriptThe hold.js stage decrypts content using a custom AES implementation.T1105 · Ingress Tool TransferVBScript downloaders use PowerShell to fetch an AutoIt interpreter and malicious script from GitHub.T1113 · Screen CaptureJC-46 includes screenshot streaming capabilities.T1134.004 · Parent PID SpoofingThe AutoIt loader selects explorer.exe as the apparent parent of a hollowing target.T1140 · Deobfuscate/Decode Files or InformationScripts decode and decrypt embedded strings and payloads before execution.T1555.003 · Credentials from Web BrowsersJC-46 steals Chromium-family credentials and implements a Chrome App-Bound Encryption bypass.T1562.001 · Disable or Modify ToolsJC-46 can disable Windows Defender real-time protection and add exclusions.
Threat Actors
Malware
AsyncRATLevelBlue SpiderLabs reports that Blind Eagle has continued evolving its delivery chains in 2026, including new obfuscation schemes, a GitHub-staged AutoIt loader, and a heavily upgraded AsyncRAT build.JC-46#BlindEagleLimeRATstubs, wscript/cscript spawning PowerShell) and the payloads riding on top of them (NjRAT, AsyncRAT, LimeRAT) have barely changed in years, and that stability is the point, not an oversight.njRATAES decryption stubs, wscript/cscript spawning PowerShell) and the payloads riding on top of them (NjRAT, AsyncRAT, LimeRAT) have barely changed in years, and that stability is the point, not an oversight.
Products
AutoIt3Researchers identified four major developments: a new JavaScript AES obfuscation scheme, a bare AutoIt3 RunPE loader staged from GitHub, a reused “Photo Studio” persistence disguise, and an upgraded AsyncRAT buildGoogle Chromeinfrastructure patterns while adding WNF injection, HVNC banking fraud, browser profile cloning, and a Chrome App-Bound Encryption bypass.Windows Defender[T1562.001] Impair Defenses – The RAT disables Windows Defender protections and adds exclusions (‘Disables Windows Defender’s real-time protection and adds exclusions’).