cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2388 articles

Threat Research · bleepingcomputer.com

Chaos Ransomware Gang Uses msaRAT to Route C2 Traffic Through Chrome and Edge

Cisco Talos says the Chaos group uses Rust-based msaRAT to control headless Chrome or Edge and relay encrypted C2 traffic through Cloudflare Workers and Twilio TURN, obscuring attacker infrastructure.
Jul 23, 2026
Threat Research · bleepingcomputer.com

Sysdig Says JadePuffer Used EncForge Ransomware to Target AI/ML Assets

Sysdig says JadePuffer used custom Go ransomware EncForge against a vulnerable Langflow instance, exploiting an exposed Docker socket to encrypt AI/ML assets. Researchers found no evidence of data theft and recommend patching Langflow and restricting socket access.

Jul 23, 2026
Threat Research · recordedfuture.com

TAG-195 Evolves Its Malware-as-a-Service Toolkit with Four New Malware Families

Recorded Future details four new TAG-195 malware families, including a modular ChonkyChicken variant that loads capabilities on demand. The tools support credential theft, surveillance, reconnaissance and lateral movement, with ClickFix observed for initial access.

Jul 23, 2026
Threat Research · trendmicro.com

Tech Support Scam Campaign Sent 13 Million Emails to Japanese Addresses

Trend Micro analyzed a 165-day tech-support scam campaign that sent 13.38 million emails, mostly to .jp addresses, linking recipients to rapidly rotated fake alert sites and scam call centers; workplace-themed lures appeared in May.

Jul 23, 2026
Threat Research · hunt.io

Unattended Hermes AI Agent Used in Targeting of Thailand Finance Ministry, Researchers Find

Hunt.io researchers found an unattended Hermes agent, Hades implant, web shells and tailored attack tools targeting Thailand’s Ministry of Finance. Evidence indicates access to multiple systems; the initial access method and any data exfiltration remain unconfirmed.

Jul 23, 2026
Threat Research · socket.dev

Compromised GitHub Actions Repositories Fuel cPanel/WHM Exploitation and Credential Theft

Socket Dev Research found a broad campaign using malicious GitHub Actions workflows in compromised repositories to scan for and exploit cPanel/WHM CVE-2026-41940, then steal credentials. Affected Packagist versions reflected repository compromise; installing them alone,

Jul 22, 2026
Threat Research · sentinelone.com

SentinelLabs Tests Frontier AI Models on Long-Horizon Malware Analysis

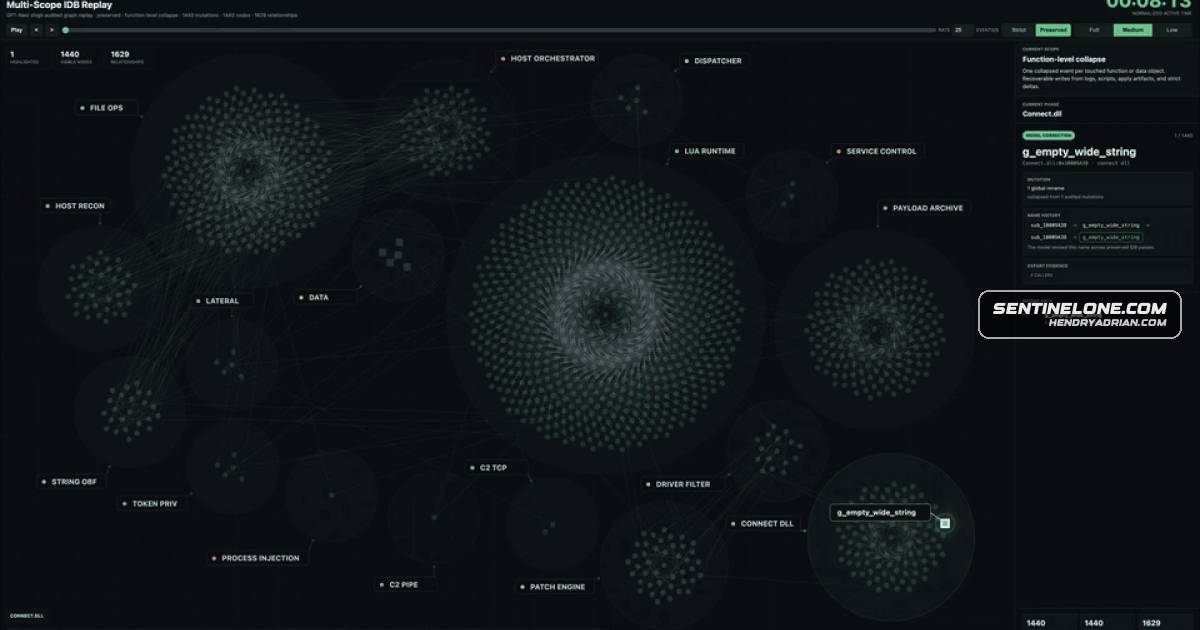
SentinelLabs benchmarked frontier models on an eight-stage reverse-engineering investigation of the fast16 implant. GPT-5.6 Sol completed all three runs, but the authors say human oversight remains essential.

Jul 22, 2026
Threat Research · feeds.fortinet.com

Fortinet Analyzes TrickBot Variant Using DNS Tunneling for C2

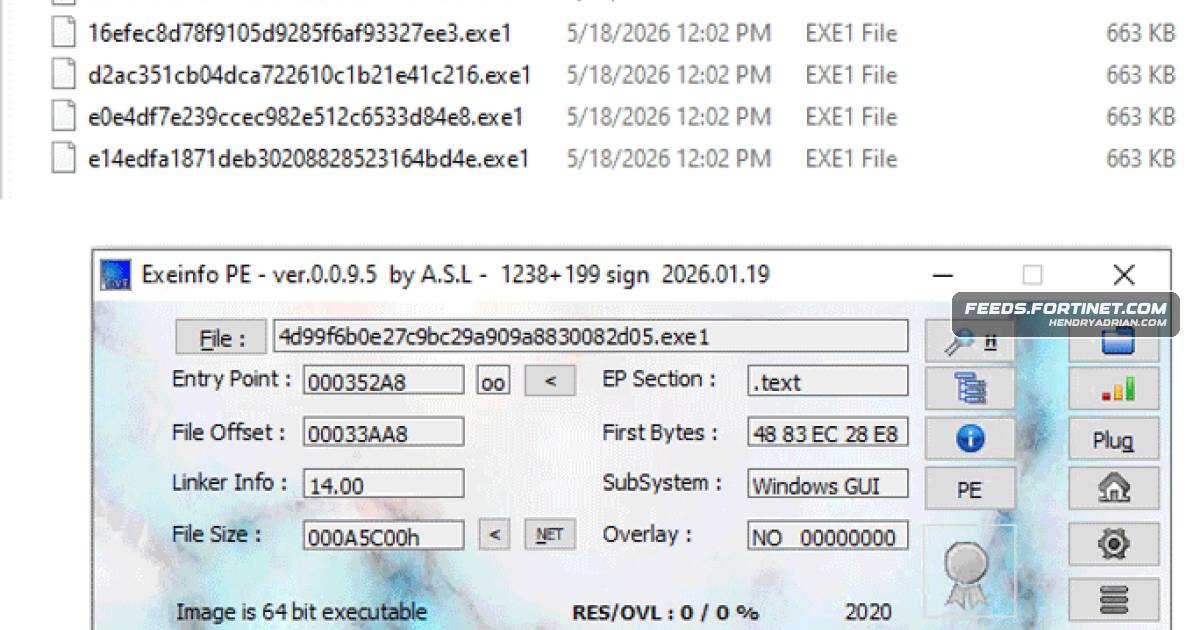
Fortinet details a TrickBot variant that uses DNS tunneling for command-and-control, persists through scheduled tasks, and can download and execute modules. The analyzed C2 server was offline, so researchers simulated its responses.

Jul 22, 2026
Threat Research · reversinglabs.com

Researchers Detail How Attackers Use Malicious SVGs for Phishing and Redirects

ReversingLabs analyzed malicious SVG samples amid a reported early-2026 rise, finding JavaScript used for redirects, phishing pages and input collection. Researchers could not access sites linked by some voicemail-themed samples.

Jul 22, 2026
Threat Research · aikido.dev

Aikido Finds Eight High-Severity Vulnerabilities in NodeBB

Aikido says a white-box assessment found eight high-severity flaws in NodeBB, including XSS, authorization bypasses, private-message exposure and post manipulation. The maintainers fixed the issues; users should upgrade to newer versions.

Jul 22, 2026
Threat Research · huntress.com

Fake Claude Desktop Ads Deliver SectopRAT to 29 Organizations

Huntress reports that malvertising led users to a malicious Claude Artifact and fake desktop installer, delivering SectopRAT to at least 29 organizations. The campaign used DLL sideloading, GPU anti-VM checks, and blockchain-based C2; Anthropic removed the artifact.

Jul 22, 2026
Threat Research · varonis.com

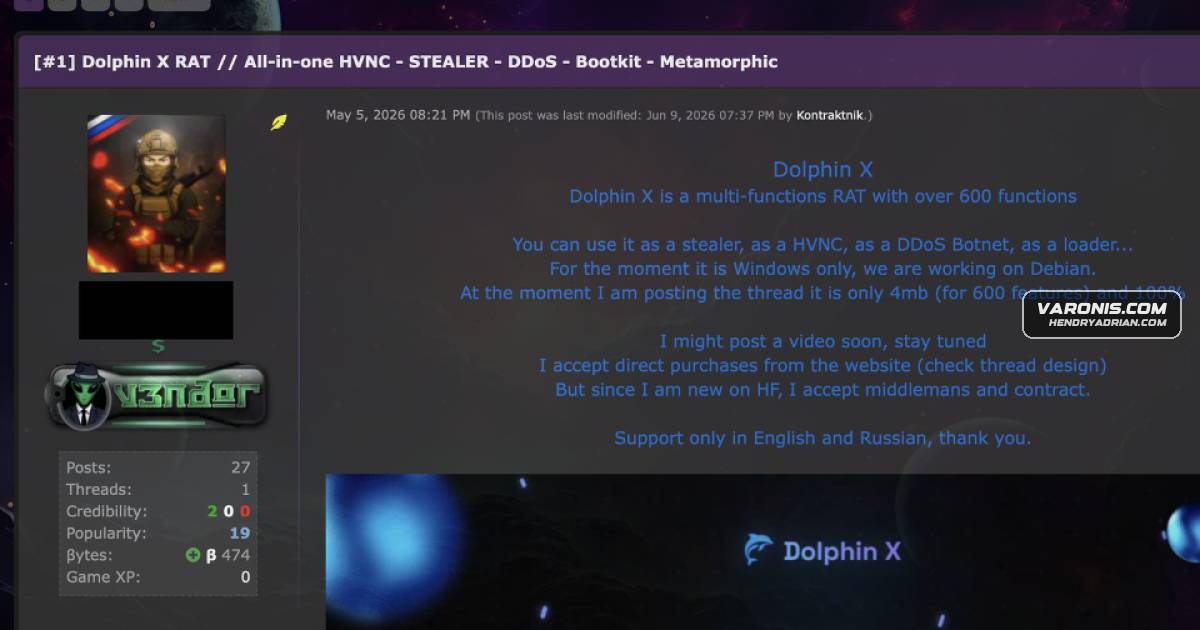
Dolphin X Infostealer Advertises 300+ Targets and AI-Assisted Victim Profiling

Varonis Threat Labs analyzed Dolphin X’s operator panel, which advertises collection of credentials from more than 300 applications and AI-assisted victim ranking. The researchers caution that most agent capabilities were not confirmed in execution.

Jul 22, 2026
Threat Research · trendmicro.com

Device-Code Phishing Turns Legitimate Microsoft Sign-In Into an MFA Bypass

Attackers trick victims into approving genuine Microsoft device-code sign-ins, giving attackers the resulting tokens. A reported account takeover used the access to register devices, hide mailbox activity, and send more phishing.

Jul 22, 2026
Threat Research · esentire.com

UNC6692 Uses Email Bombing, IT Impersonation and Quick Assist to Deploy Edgecution

eSentire details a UNC6692 phishing campaign that used email bombing and Microsoft Teams IT impersonation to gain Quick Assist access, steal Office 365 credentials, and attempt to install the Edgecution backdoor.

Jul 22, 2026
Threat Research · securelist.com

CAV3RN Module Uses Outlook Calendar Events for C2 and DNS AAAA Records for Configuration Recovery

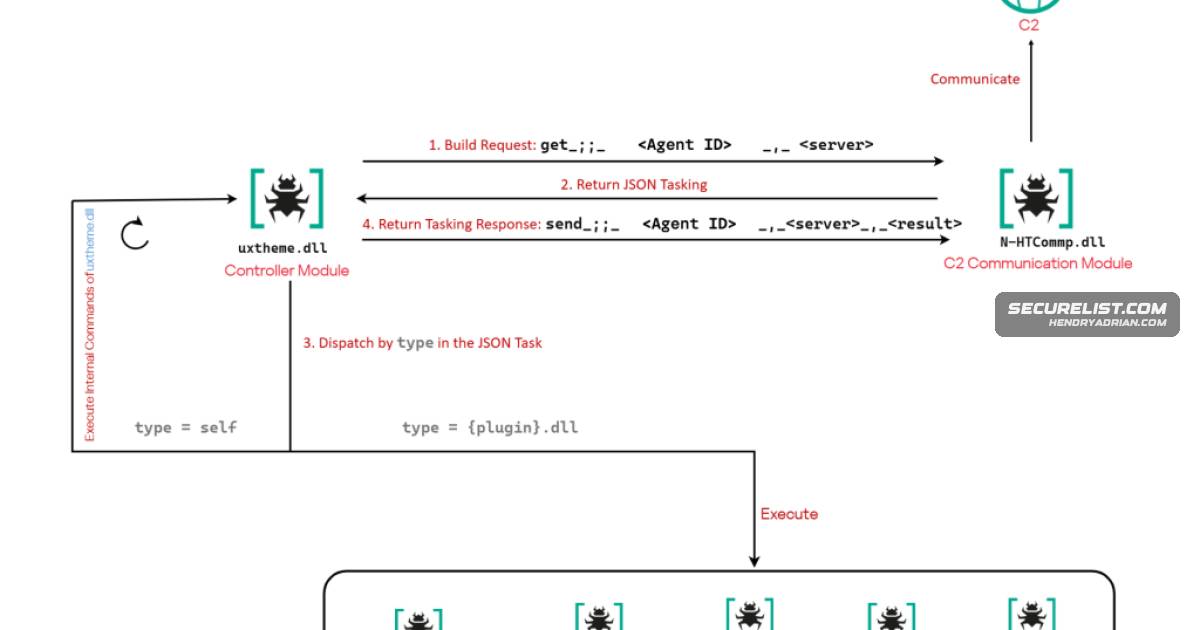
Kaspersky analyzes Project CAV3RN’s AzureCommunication.dll, which uses Microsoft Graph Outlook calendar events for C2 and DNS AAAA responses to recover configuration if Graph access fails. Its OilRig (APT34) association remains low-confidence.

Jul 21, 2026
Threat Research · infoblox.com

AiTM Phishing Campaign Targets Global Institutions With Procurement-Themed Lures

Researchers detail a campaign targeting universities, businesses, and international institutions with procurement-themed phishing. It uses compromised accounts, aged domains, and multiple AiTM kits to steal credentials and authenticated sessions.

Jul 21, 2026
Threat Research · arcticwolf.com

Arctic Wolf Details Qilin Intrusions Using CVE-2026-0257

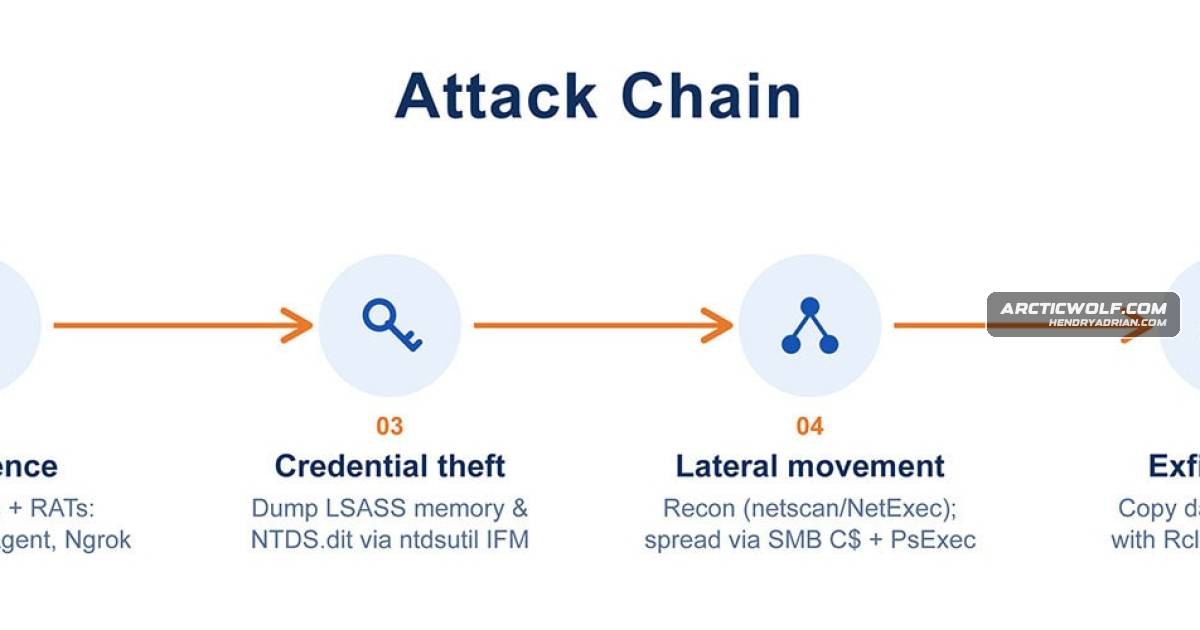
Arctic Wolf Labs details June 2026 intrusions where attackers exploited CVE-2026-0257 in Palo Alto Networks GlobalProtect to deploy Qilin ransomware, steal credentials, move laterally and, in some cases, exfiltrate data.

Jul 21, 2026
Threat Research · securityweek.com

HollowGraph Malware Uses Microsoft 365 Calendar for Command and Control

Group-IB reports that HollowGraph uses Microsoft 365 calendar events for command and control and file exfiltration, with DNS tunneling for configuration updates. It identified 12 victims; attribution to Lyceum remains low-confidence.

Jul 21, 2026
Threat Research · rapid7.com

Exposed WebDAV Server Reveals Malware Delivery Lab and Phishing Campaigns

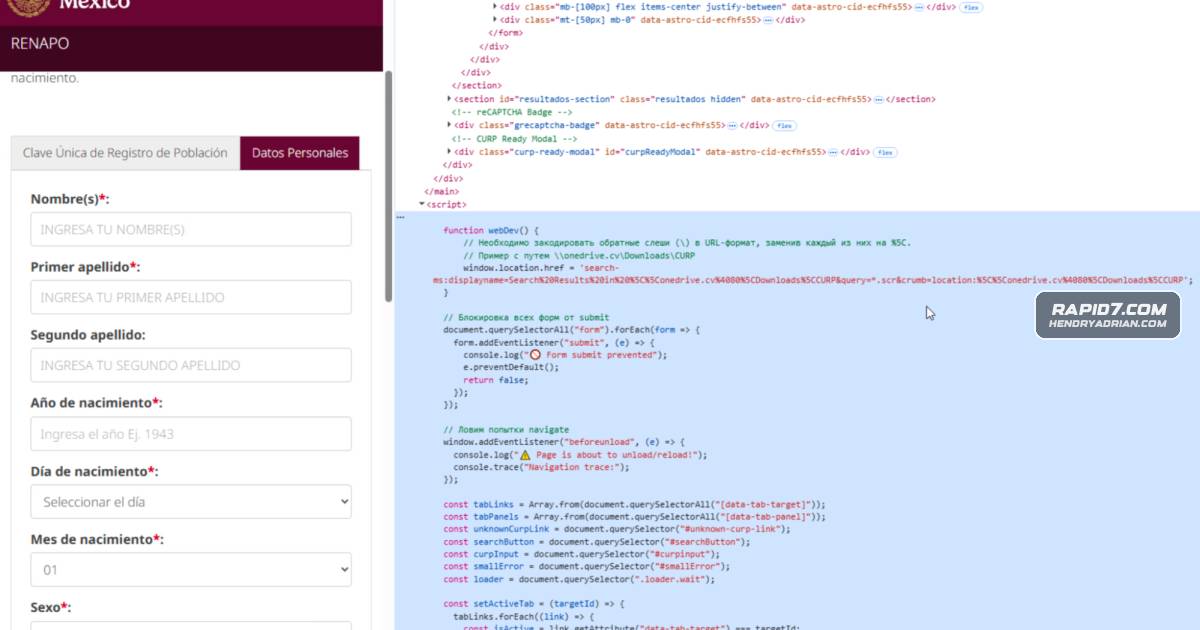
Rapid7 traced an alert to an exposed WebDAV delivery lab containing over 1,000 artifacts. Its investigation details a CURP-themed phishing chain, a separate DlrtyGames RAT chain and evidence suggesting AI-assisted development.

Jul 21, 2026
Threat Research · sysdig.com

JADEPUFFER Deploys ENCFORGE Ransomware Targeting AI Model Assets

Sysdig reports that JADEPUFFER exploited a Langflow flaw and deployed ENCFORGE, ransomware targeting AI model files and datasets. Researchers analyzed its encryption and container-escape techniques and found no evidence of data exfiltration.

Jul 21, 2026
Threat Research · guardsix.com

Atomic Arch Campaign Used Compromised AUR Packages to Deliver an Infostealer

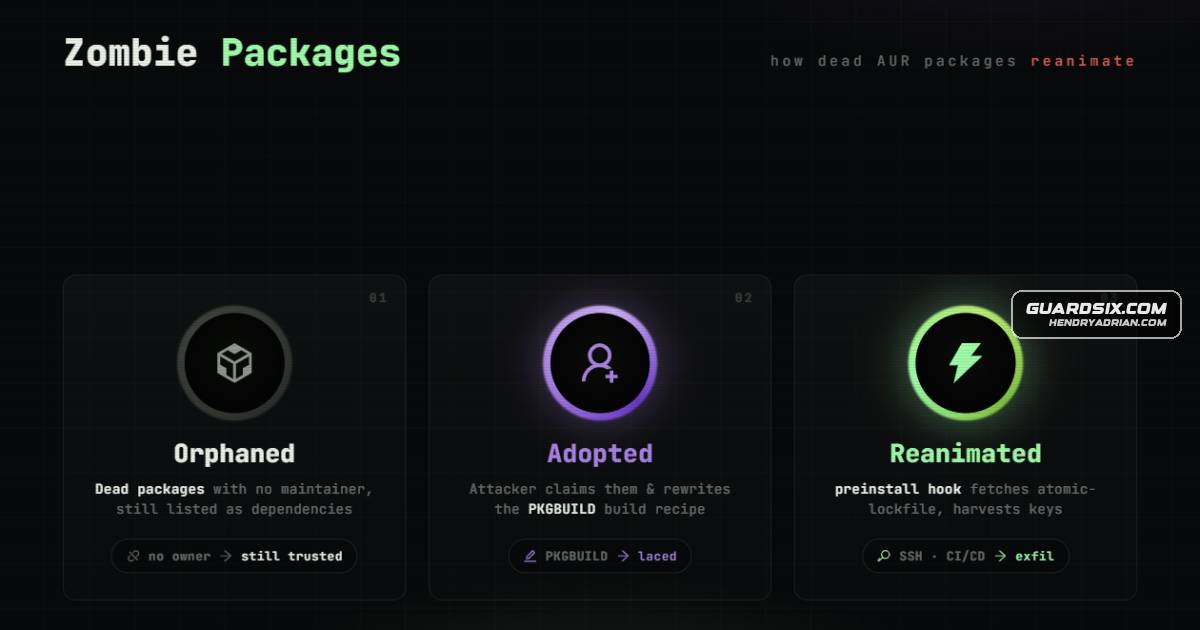
Attackers altered more than 1,900 orphaned Arch User Repository packages to fetch malicious npm or Bun dependencies. The payload stole developer credentials, established persistence and could hide activity with an eBPF rootkit.

Jul 21, 2026
Threat Research · bleepingcomputer.com

Volexity details SonicWall SMA1000 zero-day chain used to deploy custom malware

Volexity says UTA0533 exploited two SonicWall SMA1000 zero-days from June 22, 2026, chaining unauthenticated WebSocket tunneling and root command injection to install custom malware. Patches are available.

Jul 21, 2026
Threat Research · any.run

Kali365 Uses Device-Code Phishing to Target US Organizations and Obtain OAuth Tokens

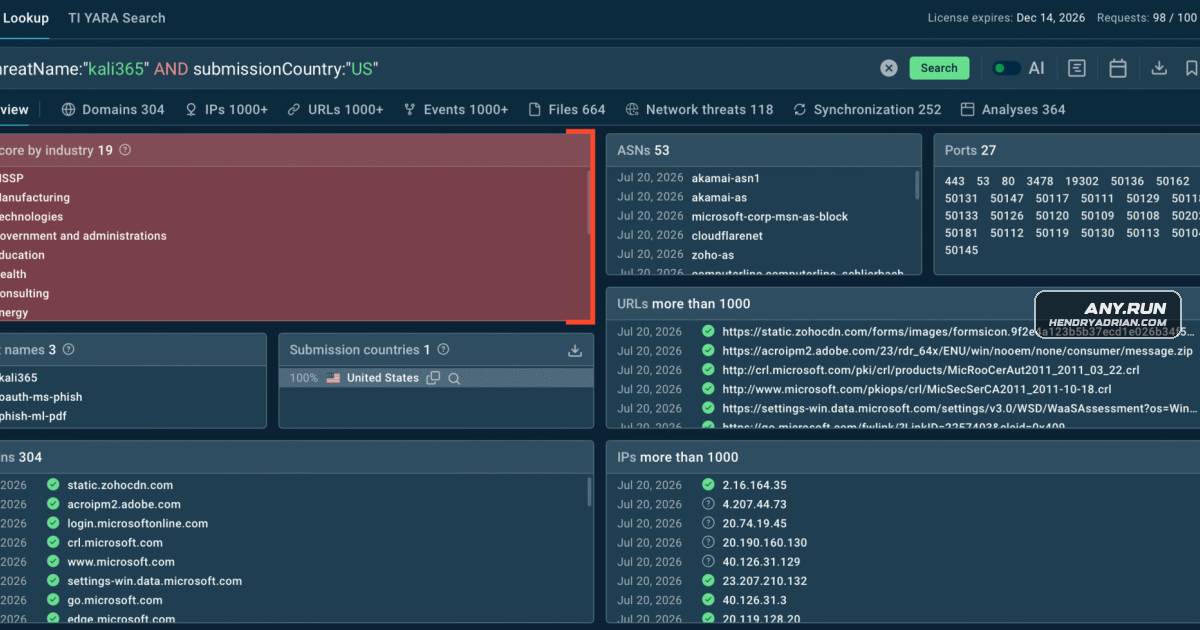
ANY.RUN reports that Kali365 targets US organizations with device-code phishing, using branded lures and legitimate Microsoft or Google login flows to obtain OAuth tokens and potentially access cloud resources.

Jul 21, 2026
Threat Research · acronis.com

Lampion Phishing Campaign Targets Portugal With Multistage Malware

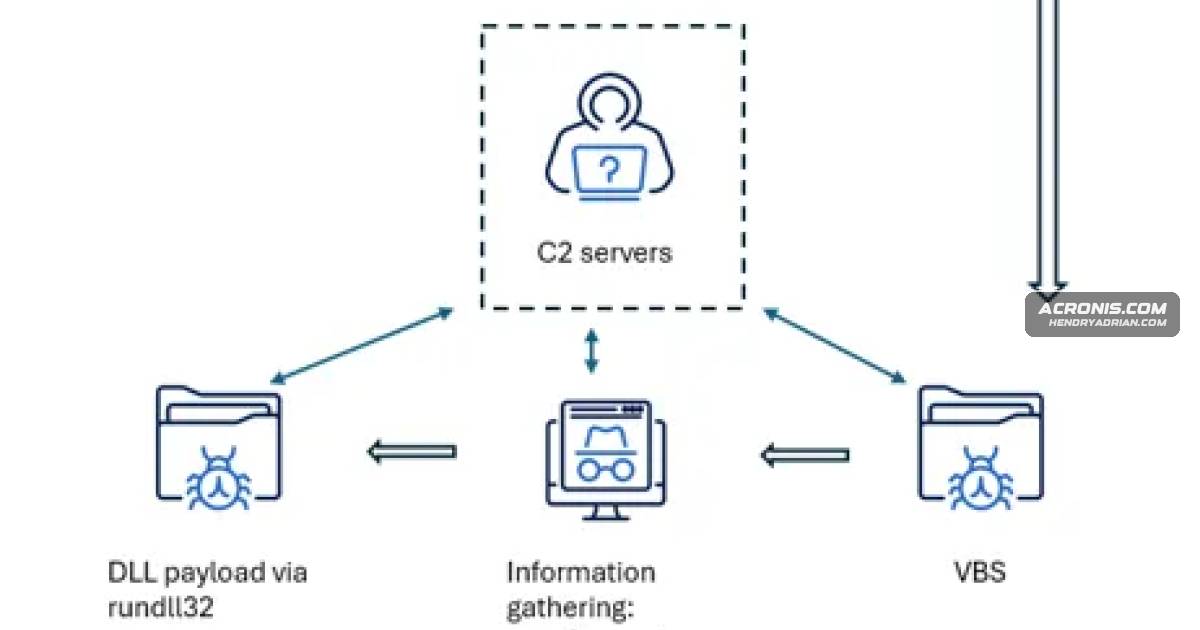
Acronis researchers detail a Lampion campaign targeting Portuguese users with phishing emails and obfuscated ZIP, HTML and VBS stages that install a remote-access payload; 94.6% of detections were in Portugal.

Jul 21, 2026
PreviousPage 41 of 100 Next
© 2026 cyber.hendryadrian.com