
ClickFix Campaign Uses Polygon Smart Contracts to Deliver macOS Infostealer
Summary
LevelBlue researchers report finding hundreds of compromised WordPress sites used in a ClickFix campaign. They describe Polygon-based C2 resolution and a macOS infostealer that collects sensitive data and sends it to genomicsforge[.]com.
Key points
- Researchers say hundreds of WordPress sites across regions and industries carried the same malicious injection.
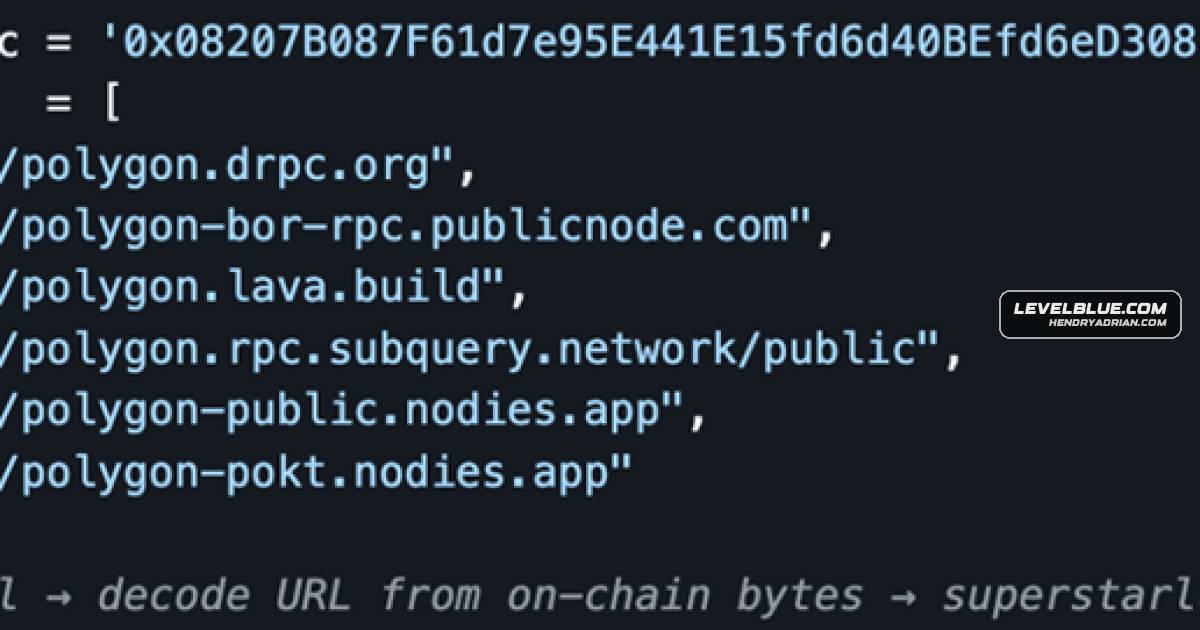
- Injected scripts query a Polygon smart contract through six public RPC endpoints to retrieve C2 details, then fingerprint visitors and display platform-specific pages.
- A fake Cloudflare verification overlay prompts macOS users to paste a command; the iframe can write that command to the clipboard.
- The command pipes a downloaded script from genomicsforge[.]com directly to zsh; a gzip-compressed, Base64-encoded payload then executes in memory.
- The macOS payload uses osascript to collect Keychain, browser, and SSH data, screenshots, and saved passwords, staging data in /tmp/osalogging.zip.
- The archive is uploaded in 10 MB chunks to genomicsforge[.]com/gate and deleted after a successful upload; the article recommends credential rotation and site and endpoint checks.
Article Details
- Attack Vectors
- Compromised WordPress sites inject a script that resolves a C2 URL from a Polygon smart contract and displays a full-screen, platform-specific iframe overlay.
- A fake Cloudflare verification prompt instructs macOS visitors to paste a command into Terminal; the command downloads a script from attacker infrastructure and pipes it to zsh.
- The downloaded payload is gzip-compressed and Base64-encoded, decompresses and evaluates in memory, then retrieves an AppleScript payload via osascript.
- The infostealer collects macOS Keychain, browser, SSH, screenshot, and saved-password data, stages it in /tmp/osalogging.zip, and uploads it in chunks before deleting the archive.
- Defensive Notes
- For WordPress sites, audit injected script tags, rotate CMS and hosting credentials, and scan for unauthorized file modifications.
- For potentially affected macOS devices, rotate passwords, revoke SSH keys, check ~/Library/LaunchAgents/ for unknown persistence, inspect /tmp/ for osalogging.zip, and consider a full macOS reinstall if sensitive accounts were active.
- Defenders are advised to block superstarlog[.]click and genomicsforge[.]com; alert on osascript as a child of shell pipelines, PUT requests to /gate?buildtxd=, and browser-originated eth_call requests to Polygon RPC endpoints.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | genomicsforge[.]com | Attacker infrastructure used to deliver the macOS script and receive stolen data. |
| DOMAIN | holopebamiy[.]bond | Listed among domains associated with the ClickFix overlay infrastructure. |
| DOMAIN | memshowblob[.]forum | Listed among domains associated with the ClickFix overlay infrastructure. |
| DOMAIN | merabs[.]pro | Listed among domains associated with the ClickFix overlay infrastructure. |
| DOMAIN | superboomer[.]world | Listed as an attacker-controlled ClickFix overlay domain. |
| DOMAIN | superstarlog[.]click | Attacker-controlled ClickFix overlay domain used to serve the macOS landing page. |
MITRE ATT&CK
T1005 · Data from Local SystemThe infostealer collects local files and browser artifacts, along with Keychain and SSH data.T1027 · Obfuscated Files or InformationThe downloaded payload is gzip-compressed and Base64-encoded before being decompressed and evaluated in memory.T1041 · Exfiltration Over C2 ChannelCollected data is uploaded in chunks to genomicsforge[.]com/gate.T1059.002 · AppleScriptThe malware retrieves an AppleScript payload and executes it via osascript.T1059.004 · Unix ShellThe pasted command downloads a script and pipes it to zsh on macOS.T1105 · Ingress Tool TransferThe command downloads a script from genomicsforge[.]com, and the payload later retrieves an AppleScript payload.T1113 · Screen CaptureThe infostealer can capture screenshots from the victim's macOS system.T1132.001 · Standard EncodingThe payload is Base64-encoded during staging.T1189 · Drive-by CompromiseThe campaign uses compromised WordPress websites to deliver the malicious overlay and script to visitors.T1204.004 · Malicious Copy and PasteVictims are instructed to paste the clipboard-provided malicious command into Terminal.T1555.001 · KeychainThe payload accesses the macOS Keychain to collect stored data.
Products
macOSA ClickFix campaign is abusing compromised WordPress sites and a fake Cloudflare verification prompt to trick macOS users into pasting a malicious Terminal command that deploys a three-stage infostealer.WordPressA ClickFix campaign is abusing compromised WordPress sites and a fake Cloudflare verification prompt to trick macOS users into pasting a malicious Terminal command that deploys a three-stage infostealer.
Industries
CharitiesFrom restaurants, dental practices, law firms, construction companies, charities, and more across North America, Europe, Asia-Pacific, and South America.ConstructionFrom restaurants, dental practices, law firms, construction companies, charities, and more across North America, Europe, Asia-Pacific, and South America.Dental practicesFrom restaurants, dental practices, law firms, construction companies, charities, and more across North America, Europe, Asia-Pacific, and South America.Law firmsFrom restaurants, dental practices, law firms, construction companies, charities, and more across North America, Europe, Asia-Pacific, and South America.RestaurantsFrom restaurants, dental practices, law firms, construction companies, charities, and more across North America, Europe, Asia-Pacific, and South America.