
ViPNet Update System Abused to Deploy Five Malicious Modules
Summary
Researchers describe an active campaign since at least May 2026 that abuses the ViPNet update system to deploy five malicious modules, including a Rust backdoor. They link it with low confidence to an unknown Chinese-speaking APT group.
Key points
- Researchers report targeted infection attempts against large Russian organizations in government, energy, transport, education, logistics, and industry; the campaign was still active at publication.
- Attackers placed wtsapi32.dll in the ViPNet update directory for DLL sideloading. HelloInjector then injected code into svchost.exe and loaded payloads in memory.
- HelloProxy intercepted socket-related functions and could act as a proxy or loader; it listened on ports 5003 and 5060 and used a handshake to identify command-server traffic.
- HelloExecutor ran Windows commands to gather user, network, system, and ViPNet-directory information.
- The Rust-based HelloBackdoor accepted connections on TCP port 443 and supported file upload, download, stopping the backdoor, and command execution.
- Attackers used renamed PuTTY/Plink executables for SSH tunneling. Detection guidance recommends checking executable identity and command lines, as well as monitoring injection from ViPNet update processes.
Article Details
- Attack Vectors
- The attackers placed wtsapi32.dll in the ViPNet Update System directory so itcsrvup64.exe could load it at startup, establishing persistence through DLL sideloading.
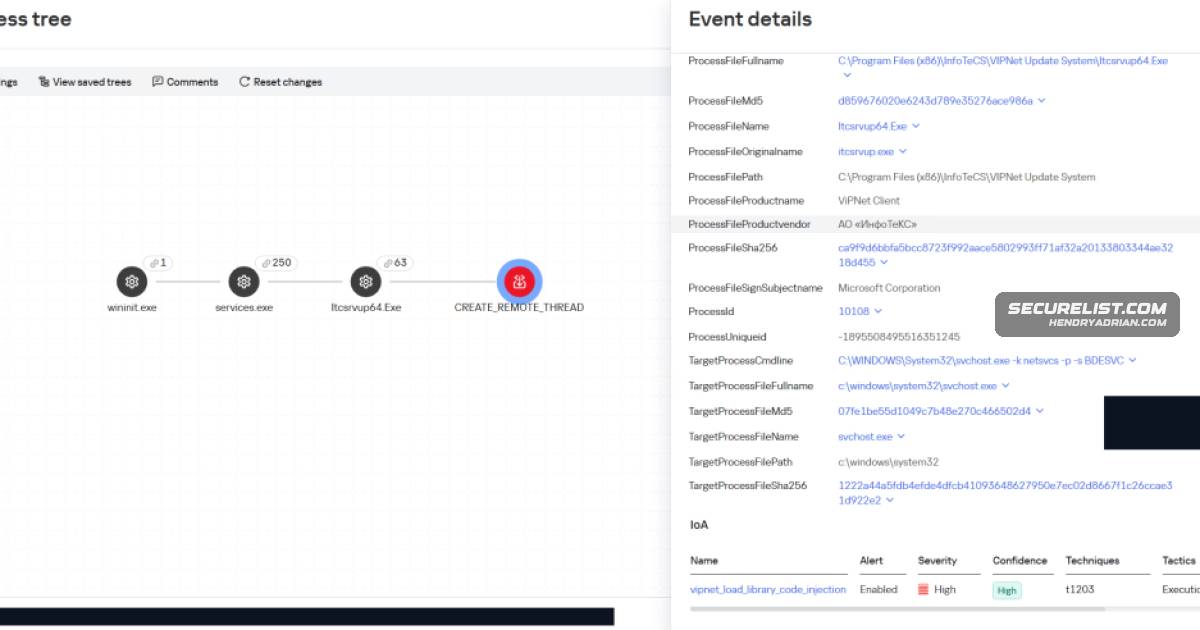
- HelloInjector searched for svchost.exe processes and injected code using NtWriteVirtualMemory and NtCreateThreadEx, then loaded payloads into memory.
- HelloProxy intercepted socket-related functions, listened on ports 5003 and 5060, forwarded traffic, and could load executables received from the command server.
- The attackers used a renamed PuTTY/Plink executable to create SSH reverse tunnels from infected systems to command-server infrastructure.
- HelloBackdoor accepted TCP connections on port 443 and supported file upload, download, and stop commands.
- Defensive Notes
- Monitor network traffic on the ports identified in the report for signs of compromise.
- Monitor creation of wtsapi32.dll in ViPNet directories and unusual or unsigned processes launched by ViPNet update processes.
- Alert on process injection into svchost.exe originating from itcsrvup64.exe or itcsrvup.exe.
- Detect renamed PuTTY/Plink binaries using their original PE filename, version information, strings, or hash, and review their command lines for port-forwarding patterns.
- Ensure SIEM collection includes Windows Sysmon events 1, 7, and 11, and Security events 4688 and 4663, to support the described detection and hunting rules.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 176[.]32[.]34[.]135 | Reported command-server endpoint used for an SSH tunnel from infected infrastructure. |
| IPV4 | 5[.]39[.]253[.]206 | Reported command-server endpoint used for an SSH tunnel from infected infrastructure. |
| MD5 | 0cfdffc56f0fa325d0c4d24780b46597 | MD5 hash listed for the malicious wtsapi32.dll loader. |
| MD5 | 41c938b3cd7e55d4077e34976929b140 | MD5 hash of a utility reported as adding exclusions to Windows Defender. |
| MD5 | 6001829a128fe264b4403138700c11a8 | MD5 hash of a HelloBackdoor dropper identified as infotecsvipnet clientpuh.exe. |
| MD5 | 9f5606a0755bc633b9bd7db6d179c09e | MD5 hash listed for the malicious wtsapi32.dll loader. |
| MD5 | b103cd21280b4061f88b2bcc51394894 | MD5 hash listed for the malicious wtsapi32.dll loader. |
| MD5 | ee4ff46ddd8489e81447962f927bc3f6 | MD5 hash of a HelloBackdoor dropper identified as infotecsvipnet clientstore.exe. |
| MD5 | f9eed2f0158dc98e7012fb809152209c | MD5 hash listed for a HelloBackdoor sample. |
| SHA256 | 16c211c96735f2fae9361b89bd7a31bf1bfe2b9493128574907a8279256a8bcc | SHA-256 hash listed for a HelloBackdoor sample. |
MITRE ATT&CK
T1005 · Data from Local SystemHelloBackdoor supported downloading files from infected machines, and reported commands read local files.T1016 · System Network Configuration DiscoveryThe attackers used ipconfig /all and other network-configuration commands during reconnaissance.T1021.004 · SSHThe attackers launched SSH tunnels from infected systems using renamed PuTTY/Plink binaries.T1036 · MasqueradingThe attackers renamed a PuTTY/Plink executable to frontpage.exe to conceal its use.T1049 · System Network Connections DiscoveryThe reported reconnaissance commands included netstat -ano to inspect network connections.T1055 · Process InjectionHelloInjector used NtWriteVirtualMemory and NtCreateThreadEx to inject code into svchost.exe.T1059.003 · Windows Command ShellThe article reports commands executed through cmd.exe, including reconnaissance and service-management commands.T1074.001 · Local Data StagingThe reported commands copied files into public directories for later use.T1083 · File and Directory DiscoveryHelloExecutor ran dir commands to enumerate ViPNet, user, and other directories.T1090 · ProxyHelloProxy created sockets and forwarded traffic between them.T1105 · Ingress Tool TransferHelloProxy accepted an executable from the command server and loaded it into memory.T1112 · Modify RegistryThe reported commands changed AppMgmt registry parameters, including ServiceDll and ServiceMain.T1543.003 · Windows ServiceThe reported activity created and configured the AppMgmt Windows service.T1562.001 · Disable or Modify ToolsHelloProxy intercepted socket-related functions to hinder user-mode security solutions filtering network connections.T1574.001 · DLLThe attackers placed wtsapi32.dll in the ViPNet Update System directory for itcsrvup64.exe to load at startup.
Malware
HelloBackdoorthe ViPNet update system to deploy HelloInjector, HelloProxy, HelloExecutor, HelloCleaner, and HelloBackdoor against large Russian organizations across multiple sectors since at least May 2026.HelloCleanercampaign has been abusing the ViPNet update system to deploy HelloInjector, HelloProxy, HelloExecutor, HelloCleaner, and HelloBackdoor against large Russian organizations across multiple sectors since at least May 2026.HelloExecutorA new APT campaign has been abusing the ViPNet update system to deploy HelloInjector, HelloProxy, HelloExecutor, HelloCleaner, and HelloBackdoor against large Russian organizations across multiple sectors since at leastHelloInjectorA new APT campaign has been abusing the ViPNet update system to deploy HelloInjector, HelloProxy, HelloExecutor, HelloCleaner, and HelloBackdoor against large Russian organizations across multiple sectors since at leastHelloProxyA new APT campaign has been abusing the ViPNet update system to deploy HelloInjector, HelloProxy, HelloExecutor, HelloCleaner, and HelloBackdoor against large Russian organizations across multiple sectors since at least
Vendors
Products
Kaspersky Anti Targeted AttackUPD 16.07.2026: Added detection of the malicious campaign in network traffic using Kaspersky Anti Targeted Attack (KATA) with the NDR module.Kaspersky Endpoint Detection and Response ExpertKaspersky security solutions, such as Kaspersky Endpoint Detection and Response Expert, successfully detect malicious activity within the described attacks.Kaspersky Next ExpertThis approach is embedded in the architecture of the Kaspersky Next Expert line of solutions, designed to protect businesses from APT-level threats, including attacks similar to the one described in this article.Kaspersky SIEMUPD 16.07.2026: Added rules to protect companies using our SIEM system Kaspersky SIEM, and listed events for developing custom detection rules or conducting Threat hunting.ViPNetA new APT campaign has been abusing the ViPNet update system to deploy HelloInjector, HelloProxy, HelloExecutor, HelloCleaner, and HelloBackdoor against large Russian organizations across multiple sectors since at least
Tools
AutoIt[T1218 ] Signed Binary Proxy Execution – AutoIt and other trusted binaries were used as proxy execution (‘autoit3.exe … data.dat’).Plink#ViPNet #HelloInjector #HelloProxy #HelloExecutor #HelloCleaner #HelloBackdoor #Kaspersky #PuTTY #Plink #svchost.exePuTTY#ViPNet #HelloInjector #HelloProxy #HelloExecutor #HelloCleaner #HelloBackdoor #Kaspersky #PuTTY #Plink #svchost.exe
Industries
EducationDuring our research, we identified attempts of targeted infection of large Russian organizations from the government, energy, transport, education, and logistics sectors, as well as industry.EnergyDuring our research, we identified attempts of targeted infection of large Russian organizations from the government, energy, transport, education, and logistics sectors, as well as industry.GovernmentDuring our research, we identified attempts of targeted infection of large Russian organizations from the government, energy, transport, education, and logistics sectors, as well as industry.IndustryDuring our research, we identified attempts of targeted infection of large Russian organizations from the government, energy, transport, education, and logistics sectors, as well as industry.logisticsDuring our research, we identified attempts of targeted infection of large Russian organizations from the government, energy, transport, education, and logistics sectors, as well as industry.TransportDuring our research, we identified attempts of targeted infection of large Russian organizations from the government, energy, transport, education, and logistics sectors, as well as industry.