Cruciferra Crypter Uses Extensive Evasion to Deliver RATs and Infostealers
Summary
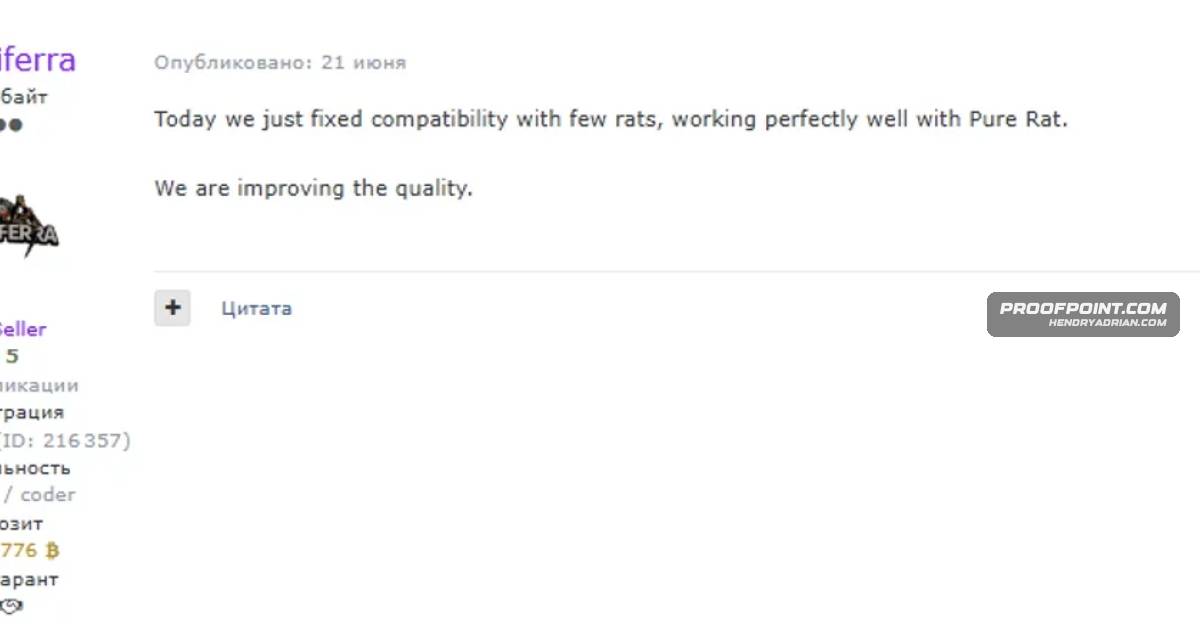
Proofpoint analyzes Cruciferra, a crypter used by multiple threat actors to deliver RATs and infostealers. The service employs techniques including BYOVD, indirect syscalls, custom encryption, and modified Process Ghosting to evade defenses.
Key points
- Proofpoint observed Cruciferra in campaigns by multiple unrelated actors, delivered through email and archive files.
- Payloads include AsyncRAT, XWorm, zgRAT, Agent Tesla, Formbook, Remcos, and infostealers.
- Campaign lures impersonated tax authorities and the Social Security Administration, and included guest-complaint themes targeting hospitality and travel organizations.
- Cruciferra uses DLL side-loading and checks for sandboxes and malware-analysis environments before deploying payloads.
- Its evasion methods include BYOVD to terminate security processes, indirect syscalls, API and IAT unhooking, privilege elevation, persistence, and notification suppression.
- The crypter uses more than 90 varied, often customized cryptographic routines to protect payloads and complicate static analysis.
- A modified Process Ghosting technique and frequent new samples indicate ongoing development; Proofpoint says it will continue monitoring the service.
Article Details
- Attack Vectors
- Cruciferra is delivered in email campaigns, including through tax- and government-themed lures and guest-complaint messages.
- Campaign emails and PDF attachments contain links to attacker-controlled landing pages that host ZIP files containing an executable and DLL pair.
- Some campaigns use links to download VHD files or zipped LNK files; the LNK campaign launches PowerShell commands and scripts before downloading another ZIP archive.
- Cruciferra is loaded through DLL side-loading and can drop a payload to disk or download it from a staging server.
- Cruciferra attempts UAC bypass using the COM Elevation Moniker, establishes registry Run-key persistence, and uses a vulnerable helper driver to terminate endpoint-defense processes.
- Defensive Notes
- Proofpoint reports tracking Cruciferra using YARA signatures, PE metadata formatting, and other indicators.
- The article describes Cruciferra’s use of indirect system calls, API and IAT unhooking, BYOVD-based EDR tampering, notification suppression, and a modified Process Ghosting technique as detection-evasion behaviors.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 0zbqnac1t4dv2t2wuodv1m[.]com | zgRAT command-and-control domain. |
| DOMAIN | gatuso[.]duckdns[.]org | XWorm command-and-control domain. |
| IPV4 | 89[.]34[.]90[.]99 | IP address listed as an indicator with the zgRAT C2 entry. |
| SHA256 | 09bedbf7a41e0f8dabe4f41d331db58373ce15b2e9204540873a1884f38bdde1 | Hash listed for the NTIOLib_X64.sys helper driver used in Cruciferra's BYOVD technique. |
| SHA256 | 17aae57cf6255c7eb169bf62ea67376d9708976eb7831f8cdd0ea38bdcb37dc4 | Hash listed for the vulnerable Core64.sys helper driver used in Cruciferra's BYOVD technique. |
| SHA256 | 2fdfdd13a0c548bb68c9d5aa8599a9265d4659da3e237fe7a42ac6ac06b9a06a | Hash listed for the vulnerable GoFlyDrv.sys helper driver used in Cruciferra's BYOVD technique. |
| SHA256 | 3c181f642e24c28602a87be7f195e2f3d1ffa30b37e20f5121d99f88b22ab80e | SHA-256 indicator for a TA4922 Cruciferra/AsyncRAT payload. |
| SHA256 | 3f31aee0948d16f8d64bf6bec69a4331099993e502b11bfc56b2c0112024489d | SHA-256 indicator for a Cruciferra/zgRAT payload. |
| SHA256 | 59ad96dd3b4d5f10a5c53bbd465446e52dc7701a4ac633632f762bf1336d3347 | SHA-256 indicator for a Cruciferra campaign payload. |
| SHA256 | 5b4f59236a9b950bcd5191b35d19125f60cfb9e1a1e1aa2e4f914b6745dde9df | Hash listed for the ProcessMonitorDriver.sys helper driver used in Cruciferra's BYOVD technique. |
| SHA256 | 66dbe675480dc229e5b3ab8ad74207f73486e64e57805074f784bb2e01bcb865 | SHA-256 indicator listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| SHA256 | 6dbd6f9f2fa636c16ac4fa81418b68a604424861b9650dd9c4f2b0ba6f67d6ac | SHA-256 indicator for a Cruciferra campaign payload. |
| SHA256 | 7887e919555fb5948c217556ba149392a72982b1bc427d3db779db9dcbf09ee8 | Hash listed for the MemoryInformer.sys helper driver used in Cruciferra's BYOVD technique. |
| SHA256 | a6fb779be35592fb0ff624a8f8e12ab3cafe7bcfc312cd98263814db7fb01e02 | SHA-256 indicator for a Cruciferra campaign payload. |
| SHA256 | c46e907886e2158cbc453e767183aecf07887b5ac8848f19684451883d69f5f0 | Hash listed for the selfprot.sys helper driver used in Cruciferra's BYOVD technique. |
| SHA256 | c4e93449453cf67c5d5605bb8f425207a738a242fdb432d720acc32faa74926c | Hash listed for the HwOs2Ec.sys helper driver used in Cruciferra's BYOVD technique. |
| SHA256 | c5b1e9aafc8f2b4ab05effc00fd43f3114b9ef1d592a086c952793ac4e299809 | Hash listed for the LnvMSRIO.sys helper driver used in Cruciferra's BYOVD technique. |
| URL | hxxp[:]//faeytrdeaw[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxp[:]//figyuyrqwr[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxp[:]//fiusyevr[.]live | URL listed as a Cruciferra campaign indicator. |
| URL | hxxp[:]//fuaytrwese[.]love | URL listed as a Cruciferra campaign indicator. |
| URL | hxxp[:]//hfyuayustrv[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxp[:]//hsahyteiows[.]gu[.]cc | TA4922 Cruciferra/AsyncRAT payload URL listed as an indicator. |
| URL | hxxp[:]//jaiydteds[.]love | URL listed as a Cruciferra campaign indicator. |
| URL | hxxp[:]//jsiruytrawey[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxp[:]//kawosyetw[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxp[:]//kawuuterta[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxp[:]//laiwutrencr[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxp[:]//lasiduutfe[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxp[:]//lisiutegrm[.]live | URL listed as a Cruciferra campaign indicator. |
| URL | hxxp[:]//maisytawe[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxp[:]//mksfuuerwo[.]live | URL listed as a Cruciferra campaign indicator. |
| URL | hxxp[:]//ncduuyese[.]live | URL listed as a Cruciferra campaign indicator. |
| URL | hxxp[:]//nciyeyrawoe[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxp[:]//nviuawusye[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxp[:]//nvsieyrrawe[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxp[:]//paiwudyea[.]love | URL listed as a Cruciferra campaign indicator. |
| URL | hxxp[:]//pmcjsuyraw[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxp[:]//qeuasytua[.]love | URL listed as a Cruciferra campaign indicator. |
| URL | hxxp[:]//svuatwea[.]love | URL listed as a Cruciferra campaign indicator. |
| URL | hxxp[:]//syfiaydytea[.]live | URL listed as a Cruciferra campaign indicator. |
| URL | hxxp[:]//viuyeyrwqs[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxp[:]//vusuydryt[.]love | URL listed as a Cruciferra campaign indicator. |
| URL | hxxp[:]//xkcifgieusr[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxp[:]//xnbscuya[.]love | URL listed as a Cruciferra campaign indicator. |
| URL | hxxp[:]//xuastyrdqk[.]love | URL listed as a Cruciferra campaign indicator. |
| URL | hxxp[:]//yicoweytcbtw[.]gu[.]cc | URL listed among TA4922 Cruciferra/AsyncRAT campaign indicators. |
| URL | hxxps[:]//almacensantangel[.]com/wp-includes/assets/YourSSA_Documents_0000000676152_05_187_2026_Document_0000000676152[.]rar | Specific Cruciferra/XWorm payload URL identified in the indicators. |
| URL | hxxps[:]//digital-magicians[.]com/photo295825092412[.]zip?_r=ea623202 | Specific Cruciferra/zgRAT payload URL identified in the indicators. |
| URL | hxxps[:]//fvxcuvuyte[.]live | URL listed as a Cruciferra campaign indicator. |
| URL | hxxps[:]//hsauyeet[.]live | URL listed as a Cruciferra campaign indicator. |
| URL | hxxps[:]//kdsuyrse[.]live | URL listed as a Cruciferra campaign indicator. |
| URL | hxxps[:]//oakwusya[.]love | URL listed as a Cruciferra campaign indicator. |
MITRE ATT&CK
T1055 · Process InjectionCruciferra uses a modified Process Ghosting method to map and execute a payload in a process from a deleted backing file.T1059.001 · PowerShellA campaign's zipped LNK file launches PowerShell commands and a PowerShell script before downloading an archive.T1547.001 · Registry Run Keys / Startup FolderCruciferra establishes persistence by writing to the registry Run key.T1548.002 · Bypass User Account ControlCruciferra attempts to elevate privileges by bypassing UAC through the COM Elevation Moniker.T1562.001 · Disable or Modify ToolsCruciferra uses a vulnerable helper driver to attempt to terminate EDR processes and impair defenses.T1566.001 · Spearphishing AttachmentCruciferra campaigns deliver malware through emails using tax, government, and guest-complaint lures.T1574.002 · DLL Side-LoadingCruciferra is executed through DLL side-loading from an archive containing an executable and a DLL.
Threat Actors
Malware
AgentTeslaResearchers have observed Cruciferra delivered alongside multiple malware payloads such as zgRAT, AgentTesla, AsyncRAT, XLoader, XWorm, Phantom Stealer, Formbook, and Remcos.AsyncRATResearchers have observed Cruciferra delivered alongside multiple malware payloads such as zgRAT, AgentTesla, AsyncRAT, XLoader, XWorm, Phantom Stealer, Formbook, and Remcos.CruciferraCruciferra is a sophisticated crypter service used by multiple unrelated cybercriminal threat clusters.DarkCloud StealerDarkCloud Stealer DCRatAsyncRAT / DCRAT FormBookResearchers have observed Cruciferra delivered alongside multiple malware payloads such as zgRAT, AgentTesla, AsyncRAT, XLoader, XWorm, Phantom Stealer, Formbook, and Remcos.Phantom StealerResearchers have observed Cruciferra delivered alongside multiple malware payloads such as zgRAT, AgentTesla, AsyncRAT, XLoader, XWorm, Phantom Stealer, Formbook, and Remcos.RemcosResearchers have observed Cruciferra delivered alongside multiple malware payloads such as zgRAT, AgentTesla, AsyncRAT, XLoader, XWorm, Phantom Stealer, Formbook, and Remcos.Snake KeyloggerSnake Keylogger ValleyRATValleyRAT (also known as Winos4.0) XLoaderResearchers have observed Cruciferra delivered alongside multiple malware payloads such as zgRAT, AgentTesla, AsyncRAT, XLoader, XWorm, Phantom Stealer, Formbook, and Remcos.XWormResearchers have observed Cruciferra delivered alongside multiple malware payloads such as zgRAT, AgentTesla, AsyncRAT, XLoader, XWorm, Phantom Stealer, Formbook, and Remcos.zgRATResearchers have observed Cruciferra delivered alongside multiple malware payloads such as zgRAT, AgentTesla, AsyncRAT, XLoader, XWorm, Phantom Stealer, Formbook, and Remcos.
Products
IDA ProFigure 7: IDA Pro snippet showing a typical list of exported functions in a Cruciferra sample.Microsoft WindowsCruciferra uses a unique technique to prevent console windows from spawning from its processes (which could alert the user to an infection).VirusTotalHere are some examples from samples in VirusTotal:
Tools
AdaptixC2This malware then led to XWorm and AdaptixC2.PowerShellThese messages contained URLs masquerading as links to evidence provided by a guest, but led to the download of a zipped LNK file that launched a PowerShell command, which then executed a PowerShell script.YARAUsing Yara signatures, metadata formatting, and other indicators, we can track uploads of Cruciferra in VirusTotal.
Countries
Industries
Financial ServicesAlthough the targeting is opportunistic, some verticals were observed more frequently in campaigns, including financial services, healthcare, and government entities.GovernmentAlthough the targeting is opportunistic, some verticals were observed more frequently in campaigns, including financial services, healthcare, and government entities.HealthcareAlthough the targeting is opportunistic, some verticals were observed more frequently in campaigns, including financial services, healthcare, and government entities.HospitalityIn a Cruciferra campaign observed at the end of June, threat actors leveraged email themes related to bed bugs and guest complaints to target organizations in the hospitality and travel industries.TravelIn a Cruciferra campaign observed at the end of June, threat actors leveraged email themes related to bed bugs and guest complaints to target organizations in the hospitality and travel industries.