
CAV3RN Module Uses Outlook Calendar Events for C2 and DNS AAAA Records for Configuration Recovery
Summary
Kaspersky analyzes Project CAV3RN’s AzureCommunication.dll, which uses Microsoft Graph Outlook calendar events for C2 and DNS AAAA responses to recover configuration if Graph access fails. Its OilRig (APT34) association remains low-confidence.
Key points
- AzureCommunication.dll exchanges commands and results through Microsoft Graph Outlook calendar events scheduled in a fixed one-hour window in 2050.
- Inbound commands use RSA-OAEP-SHA256 to protect an AES-256-GCM key; encrypted command output is split into attachments and uploaded through Graph.
- If Graph authentication or validation fails, the module queries cloudlanecdn[.]com for AAAA responses that encode replacement tenant, client, secret, and mailbox configuration values.
- The DNS recovery protocol uses AAAA responses as data containers, discarding two bytes and retrieving configuration in fragments of up to 14 bytes.
- The module is compiled with .NET Native AOT, which removes much of the metadata and intermediate language normally available for analysis.
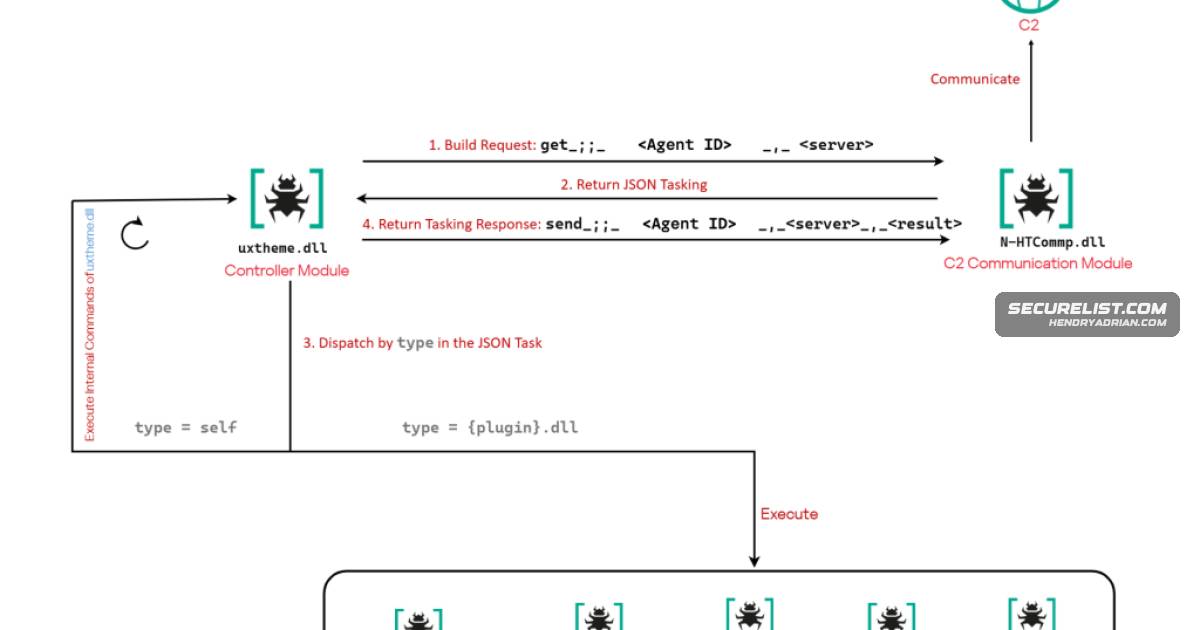
- Kaspersky assesses that the module was designed to replace CAV3RN’s previous HTTP/WebSocket communication component, though the updated controller was not recovered.
- Kaspersky retains a low-confidence association with OilRig (APT34), citing behavioral similarities but finding no direct code reuse or infrastructure overlap.
Article Details
- Attack Vectors
- AzureCommunication.dll uses Microsoft Graph and Outlook calendar events to exchange commands, heartbeats, and results in a fixed 2050-05-13 22:00–23:00 UTC window.
- If OAuth token acquisition or tenant validation fails, the module attempts to recover TenantId, ClientId, ClientSecret, and UserEmail through DNS AAAA queries to cloudlanecdn[.]com.
- The module downloads command attachments and decrypts them using RSA-OAEP-SHA256 and AES-256-GCM; it encrypts results, splits them into chunks of up to 10 MiB, and uploads them as calendar attachments.
- Defensive Notes
- Monitor Microsoft Graph calendar activity for events in the reported 2050 time window with subjects beginning Event ID:, Boss update ID:, or Boss Report ID:.
- Look for DNS AAAA queries matching the article's configuration-recovery patterns to cloudlanecdn[.]com and its authoritative nameservers.
- The article identifies AzureCommunication.dll and logAzure.txt as module and configuration-file names, and provides sample hashes for the module.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | cloudlanecdn[.]com | Actor-controlled DNS configuration-recovery domain used by the module. |
| DOMAIN | ns1[.]cloudlanecdn[.]com | Actor-controlled authoritative nameserver for the DNS recovery domain. |
| DOMAIN | ns2[.]cloudlanecdn[.]com | Actor-controlled authoritative nameserver for the DNS recovery domain. |
| DOMAIN | ns3[.]cloudlanecdn[.]com | Actor-controlled authoritative nameserver for the DNS recovery domain. |
| DOMAIN | ns4[.]cloudlanecdn[.]com | Actor-controlled authoritative nameserver for the DNS recovery domain. |
| IPV4 | 144[.]172[.]108[.]205 | IP address identified for the actor-controlled authoritative DNS infrastructure. |
| IPV4 | 216[.]126[.]237[.]197 | IP address identified for the actor-controlled authoritative DNS infrastructure. |
| MD5 | 29b2b8c5d99f05bfcdd0d8d976eb5678 | Hash of an AzureCommunication.dll malware-module sample. |
| MD5 | c092b02fbc0fdf7ee9608dd016673806 | Hash of a NewProject.dll sample listed with the Project CAV3RN file indicators. |
| MD5 | caf021dda726b8ba049c2aa395e505a1 | Hash of an AzureCommunication.dll malware-module sample. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationAzureCommunication.dll uses .NET Native AOT compilation, which removes much of the metadata and intermediate language.T1048 · Exfiltration Over Alternative ProtocolThe module sends encrypted command output to the operator as attachments on Microsoft Graph calendar events.T1071.001 · Web ProtocolsThe earlier communication component used HTTP, and the new module makes HTTPS requests to Microsoft Graph.T1071.004 · DNSThe module uses DNS AAAA queries to cloudlanecdn[.]com as a fallback to retrieve Microsoft Graph configuration values.T1071.007The earlier CAV3RN communication component used WebSocket-enabled C2.T1105 · Ingress Tool TransferThe module downloads command attachments from Outlook calendar events before deleting the consumed event.T1132.001 · Standard EncodingThe module converts the Agent ID bytes to uppercase hexadecimal and embeds the result in DNS recovery queries.T1567.002 · Exfiltration to Cloud StorageThe framework uses Microsoft-hosted Graph and Outlook services to exchange commands and results.
Threat Actors
OilRigThe article retains a low-confidence assessment that Project CAV3RN is associated with OilRig; it reports no direct code reuse or infrastructure overlap. The article gives APT34 parenthetically as an alternate name.SOLAR IONThe article gives APT34 parenthetically as an alternate name for OilRig and assesses the Project CAV3RN association with low confidence.
Malware
Vendors
Products
Microsoft 365 Apps for Enterprise “UserEmail”: “***@*********.co.il”, // Compromised target Microsoft 365 mailboxMicrosoft EntraThe DLL contains a complete default configuration, including the Microsoft Entra tenant ID, application credentials, target mailbox, DNS bootstrap host, and cryptographic keys required to establish communication.Microsoft GraphKaspersky detailed Project CAV3RN, a modular cyberespionage framework targeting Israel that now uses AzureCommunication.dll and Microsoft Graph Outlook calendar events for C2.OutlookKaspersky detailed Project CAV3RN, a modular cyberespionage framework targeting Israel that now uses AzureCommunication.dll and Microsoft Graph Outlook calendar events for C2.