
Exposed WebDAV Server Reveals Malware Delivery Lab and Phishing Campaigns
Summary
Rapid7 traced an alert to an exposed WebDAV delivery lab containing over 1,000 artifacts. Its investigation details a CURP-themed phishing chain, a separate DlrtyGames RAT chain and evidence suggesting AI-assisted development.
Key points
- An alert involving a file retrieved through WebDAV led investigators to an exposed workspace containing 1,048 lure, testing, payload and documentation artifacts.
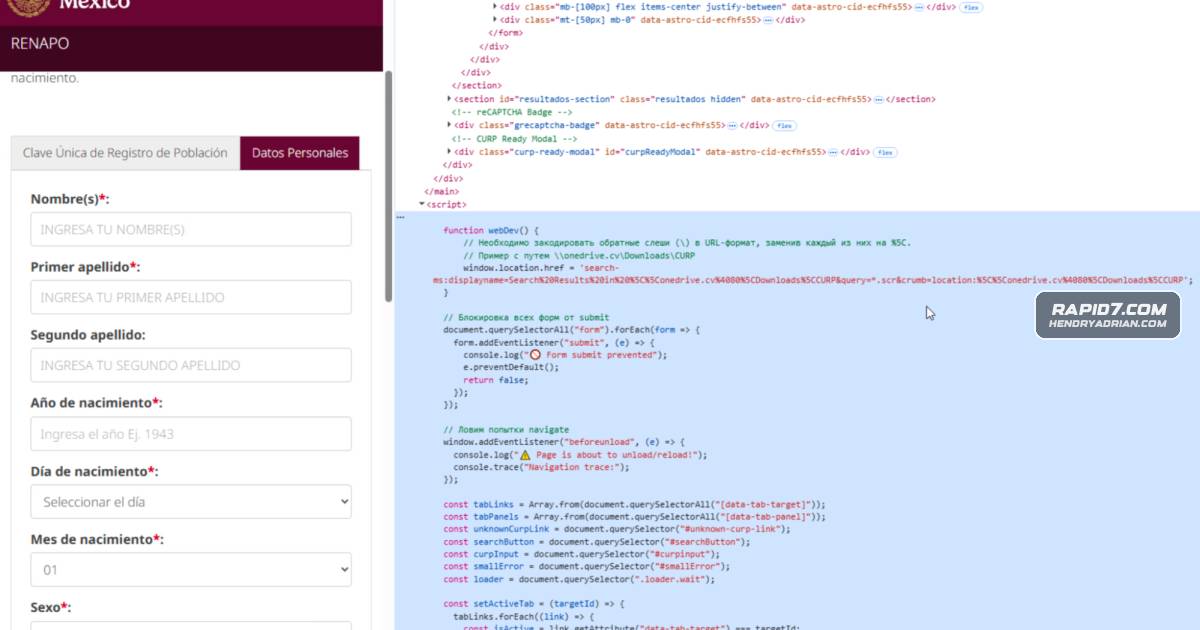
- A phishing site impersonating Mexico’s CURP lookup service used a search-ms URI to open a remote WebDAV share containing an executable disguised as a PDF.
- The CURP chain loaded a .NET information stealer in memory and used process hollowing; the payload targeted browser credentials, wallet data and messaging sessions.
- The DlrtyGames chain sideloaded a malicious DLL through a signed Ubisoft binary, extracted encrypted modules from PNG IDAT chunks and injected a modular RAT into a signed host process.
- Panel records showed 2,384 accesses to the CURP lure during the observation window. Researchers cautioned that executable requests did not confirm endpoint execution.
- The workspace included tests inspired by CVE-2025-33053 and structured documentation that researchers said suggested LLM-assisted development; the evidence does not establish that AI wrote the malware.
Article Details
- Attack Vectors
- A CURP-themed phishing site opened an attacker-controlled WebDAV share through a search-ms URI, presenting a disguised executable as a PDF.
- ClickFix pages impersonated verification checks and application errors to persuade users to run commands.
- The exposed workspace contained tests using shortcuts, remote working directories, trusted Windows binaries, and filename spoofing.
- The DlrtyGames chain used a trojanized DLL alongside a signed executable to load a modular RAT.
- Defensive Notes
- The attacker’s test documentation stated that the CVE-2025-33053 iediagcmd.exe test required the June 2025 Microsoft patch to be absent.
- WebDAV panel launch events represented executable requests or apparent attempts to run files, not confirmed endpoint execution.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | google[.]services[.]ug | Domain identified as an alias for the CURP-chain stealer C2. |
| DOMAIN | onedrive[.]cv | Attacker-controlled WebDAV delivery server used for the CURP executable. |
| DOMAIN | summerartcamp[.]net | WebDAV host from a previously reported attack path reproduced in the operator’s test documentation. |
| HOSTNAME | www[.]gobf[.]mx | Phishing hostname where a user encountered the CURP lure. |
| IPV4 | 23[.]94[.]252[.]228 | C2 endpoint associated with the DlrtyGames chain. |
| IPV4 | 77[.]110[.]127[.]205 | CURP-chain stealer C2 and exfiltration endpoint. |
| SHA256 | 04a8018191f2e9e76072d072a933371d9d669a42de2b2a087541cd3a653b0ba7 | Hash of the RTLO-disguised ReportFinal SCR lure. |
| SHA256 | 449d1121fa275879af22a20407aa7253ac750ac8fa7ff5691101752600d645df | Hash of the trojanized discord-rpc.x64.dll sideloading component. |
| SHA256 | 51a02eccdcae0483c7cbb9796738eee6c2a13b740d30e5417cda09bf418ea93b | Hash of loader-pool.db, the PNG carrier containing encrypted modules. |
| SHA256 | 82e67735cf822db8f2f759e742e5bf8c54fdbd01a4170619b9e0916e1b3f5923 | Hash of the DlrtyGames chain’s .NET RAT. |
| SHA256 | a88f5ee748e60f889d046718bfe3ddcf1c5f3cba2001cad587e8953a76bf7aa9 | Hash of profiler16.dll, the mapped DlrtyGames loader stage. |
| SHA256 | e8be17a7fbef48b45f1e958b3ae5ebdfcad58808969982c431a905eefcae5268 | Hash of the DlrtyGames.exe self-extracting dropper. |
| URL | hxxps[:]//gobf[.]mx | CURP-themed phishing site impersonating a Mexican government service. |
MITRE ATT&CK
T1027.003 · SteganographyThe DlrtyGames loader stored encrypted modules across PNG IDAT chunks in loader-pool.db.T1027.007 · Dynamic API ResolutionThe DlrtyGames DLL resolved APIs by hash.T1036.002 · Right-to-Left OverrideThe CURP ReportFinal lure used a right-to-left override to disguise its SCR extension.T1041 · Exfiltration Over C2 ChannelThe CURP stealer sent collected data to its C2 as a multipart HTTP POST over TLS.T1055.012 · Process HollowingBoth analyzed chains used process hollowing to run malicious code inside signed host processes.T1056.001 · KeyloggingThe modular RAT included a keylogger with payment, banking, and cryptocurrency keyword triggers.T1113 · Screen CaptureThe stealer captured a desktop screenshot, and the RAT included a screenshot plugin.T1140 · Deobfuscate/Decode Files or InformationThe CURP loader decrypted and unpacked its embedded payload using AES and GZip.T1204.002 · Malicious FileA user executed a file retrieved from a WebDAV share; the CURP lure presented an SCR executable as a PDF.T1497.003 · Time Based ChecksThe DlrtyGames loader slept for 45 seconds before reassembling and decrypting embedded content.T1548.002 · Bypass User Account ControlThe DlrtyGames loader performed COM auto-elevation through dllhost.exe.T1555.003 · Credentials from Web BrowsersThe payloads targeted saved browser login data, including usernames and passwords.T1574.001 · DLLA signed Ubisoft executable sideloaded the trojanized discord-rpc.x64.dll.T1620 · Reflective Code LoadingThe CURP loader loaded the decrypted .NET payload directly into memory with Assembly.Load(byte[]).T1622 · Debugger EvasionThe CURP stealer checked IsDebuggerPresent and terminated when it detected monitoring or debugging.