
Lampion Phishing Campaign Targets Portugal With Multistage Malware
Summary
Acronis researchers detail a Lampion campaign targeting Portuguese users with phishing emails and obfuscated ZIP, HTML and VBS stages that install a remote-access payload; 94.6% of detections were in Portugal.
Key points
- Phishing emails impersonate financial or administrative messages and use ZIP attachments containing oversized, obfuscated HTML files.
- The HTML displays a fake SAPO Transfer page and retrieves a JavaScript stage from attacker-controlled infrastructure.
- Multiple obfuscated VBS stages use scheduled tasks to download and run the final payload.
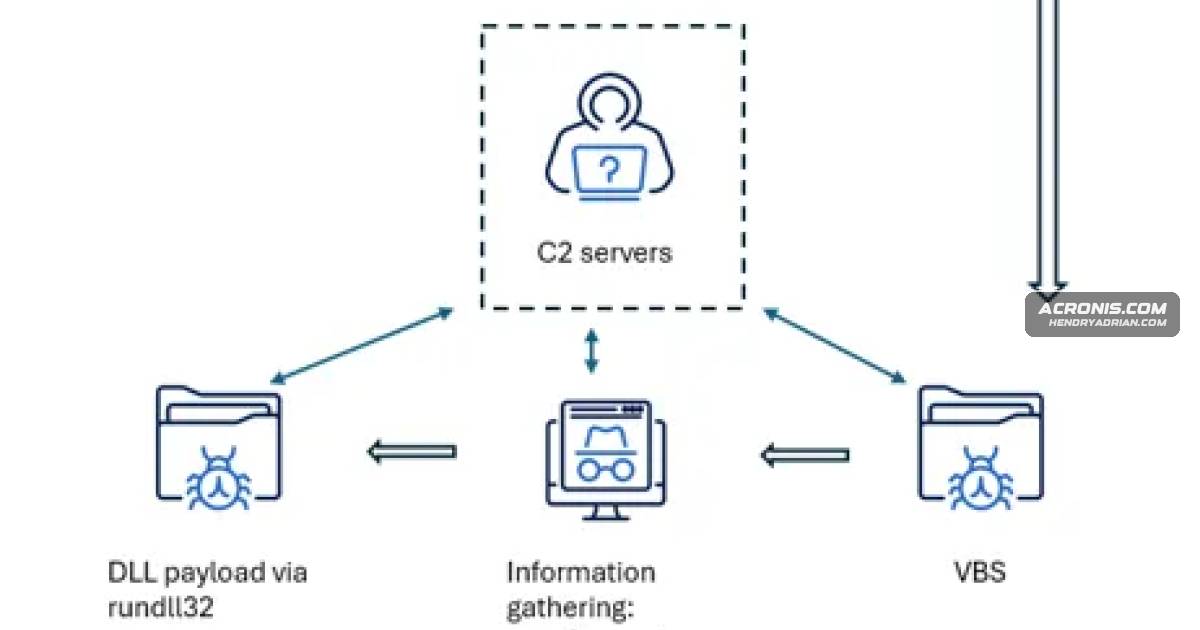
- The final stage fingerprints victims, communicates with command-and-control infrastructure, and downloads a large DLL in HTTP range chunks.
- The DLL is executed with rundll32 and provides remote access and data-exfiltration capabilities.
- Portugal accounted for 94.6% of detections; Spain and the United Kingdom accounted for most of the remainder.
- Acronis reports its EDR/XDR detects and blocks the threat, and the article provides hashes, domains, C2 hosts, and hunting artifacts.
Article Details
- Attack Vectors
- Phishing emails impersonating financial or administrative communications deliver ZIP archives containing obfuscated HTML lures.
- The HTML lure impersonates a SAPO Transfer page and retrieves JavaScript from attacker-controlled infrastructure; that script is injected into the page and executed.
- A multistage VBS chain creates downloader scripts, schedules tasks, and retrieves the final DLL payload in HTTP Range chunks.
- The final DLL is executed using rundll32, providing remote access and data-exfiltration capabilities.
- Defensive Notes
- Hunt for rundll32 loading a DLL from %APPDATA%\<14-digit timestamp>\<same timestamp>.dll, particularly when the export is jangadeiro or another Portuguese word.
- Inspect scheduled tasks that run cmd /c move into %APPDATA% or schedule a self-restart about five minutes later.
- Look for VBScript in %TEMP% that reassembles files using ADODB.Stream and Range-based HTTP chunks, or deletes other *.vbs files in %TEMP%.
- Investigate unusually large DLLs written under timestamp-named folders in %APPDATA%.
- The listed IP-based C2 URLs are described as time-bound and potentially reassigned; validate them before blocking.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | auto-contabilistica[.]com | Domain listed as involved in the Lampion campaign. |
| DOMAIN | autoridade-contabilistica[.]org | Domain listed as involved in the Lampion campaign. |
| DOMAIN | autoridade-financeira[.]com | Domain listed as involved in the Lampion campaign. |
| DOMAIN | fat-contabislitaca[.]com | Domain listed as involved in the campaign's malicious payload-delivery infrastructure. |
| SHA256 | 036c8f32012abdcb9a389ae9c284da89505e830bca74eb1aa9ea3794b067aab6 | SHA-256 of a malicious HTML file in the infection chain. |
| SHA256 | 050e84d134a32ed7c4885a9d57ce37f8ae5f910960b67e2156941961bd5781ba | SHA-256 of a malicious HTML file in the infection chain. |
| SHA256 | 1541c23f34eb05dfcbede3830741427681d719cee1dfd397a2c04110e0fa81b2 | SHA-256 of a malicious final-stage VBS script. |
| SHA256 | 1bd347ce5deee3d783a038e2d2d224bc30cc074e0471a3897c5409ce99816dc9 | SHA-256 of a malicious second-stage VBS script. |
| SHA256 | 643c0093baec45952a46b0210f7a6f8fb26883b396b66f1cb609c5b55e6dae1e | SHA-256 of a malicious HTML file in the infection chain. |
| SHA256 | 7ad89fb0a4a5449a381b8f540238193019673adc7cfb1c008dcd14a745891551 | SHA-256 of a malicious second-stage VBS script. |
| SHA256 | 87efeada5fe39a94cefc6151fd84af223d0e0e2b070daec606274481ed87b87b | SHA-256 of a phishing email identified in the campaign. |
| SHA256 | ab46f7c4d3f717bb1e61d2f236917976d2a85be6958ae099fee79ea6e9031e37 | SHA-256 of a phishing email identified in the campaign. |
| SHA256 | b1c101bd1ba134ffbea61f9fac2b7c8fbd13ca113a37944abdc131ef86da92ac | SHA-256 of a malicious ZIP attachment. |
| SHA256 | c6618bb692fb3f5d7959f8db1fedaaac5e8a36fb901397a008aa2b88874448fd | SHA-256 of a malicious ZIP attachment. |
| SHA256 | d25d32478ae67403484a309591b6409224d26ca3d094c5ccd8428ebef7efcfd1 | SHA-256 of a malicious HTML file in the infection chain. |
| SHA256 | fe769fd85a7440751e1508614c8d9ef0de00bece803329bf3318ff863a146216 | SHA-256 of a malicious final-stage VBS script. |
| URL | hxxp[:]//18[.]218[.]184[.]201/03_metal7342/trapezio.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//18[.]222[.]100[.]142/17_moldura8210/regerem.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//18[.]222[.]100[.]142/18_prateleira1967/revigore.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//3[.]135[.]194[.]95/09_nsabdo/receado.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//3[.]139[.]85[.]102/17_eudhfj/regerem.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//3[.]139[.]85[.]102/18_vdsyuh/revigore.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//3[.]139[.]85[.]102/20_fjegydk/destravares.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//3[.]141[.]199[.]105/13_ytdshe/reimpresso.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//3[.]141[.]199[.]105/15_rjhsymc/unificador.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//3[.]141[.]199[.]105/16_kdsgyue/raquete.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//3[.]144[.]37[.]134/01_sdneow/fruais.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//3[.]144[.]37[.]134/02_sjdhie/reestruturado.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//3[.]144[.]37[.]134/03_osneops/trapezio.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//3[.]148[.]240[.]228/05_dnwodu/equivaler.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//3[.]148[.]240[.]228/06_sndiwds/galgassem.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//3[.]150[.]134[.]118/05_papel6197/equivaler.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//3[.]150[.]134[.]118/06_couro8254/galgassem.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxp[:]//52[.]14[.]160[.]173/10_algodao9148/reunia.php | Final-stage VBS C2 URL listed for the campaign. |
| URL | hxxps[:]//fat-contabislitaca[.]com/js/1898.php | Attacker-controlled URL used by the HTML stage to retrieve the next-stage JavaScript payload. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe campaign uses obfuscation across its HTML and VBS stages.T1027.001 · Binary PaddingJunk padding inflates the HTML, VBS files, and final DLL.T1053.005 · Scheduled TaskThe VBS stages create scheduled tasks for downloading, moving, and restarting components.T1059.005 · Visual BasicThe multistage infection chain uses VBS scripts.T1059.007 · JavaScriptEmbedded JavaScript retrieves and executes the next-stage loader.T1071.001 · Web ProtocolsThe article describes HTTP-based C2 communications.T1105 · Ingress Tool TransferThe final-stage script downloads the payload in HTTP Range chunks.T1204.002 · Malicious FileThe infection chain relies on the recipient opening the malicious attachment.T1218.011 · Rundll32The downloaded DLL is executed with rundll32, invoking the jangadeiro export.T1497 · Virtualization/Sandbox EvasionThe article maps the campaign's evasion behavior to virtualization or sandbox evasion.T1518.001 · Security Software DiscoveryThe final-stage beacon includes the victim's antivirus product display name.T1566.001 · Spearphishing AttachmentThe campaign delivers ZIP-attached HTML lures in phishing emails.