
Kaspersky Details Armored Likho’s Telegram-Stealing and Audio-Surveillance Toolkit
Summary
Kaspersky reports a Russia-focused campaign it attributes with high confidence to Armored Likho. A fake donation app deploys the Rust-based Still Toolkit, which steals Telegram data and records audio when speech is detected.
Key points
- The campaign targets users in Russia, primarily private individuals, as well as corporate, government, IT, and education organizations.
- A Rust app built with the Tauri framework impersonates a donation service; its distribution method is unknown. After the user enters a password, the dropper launches the next-stage payload in the background.
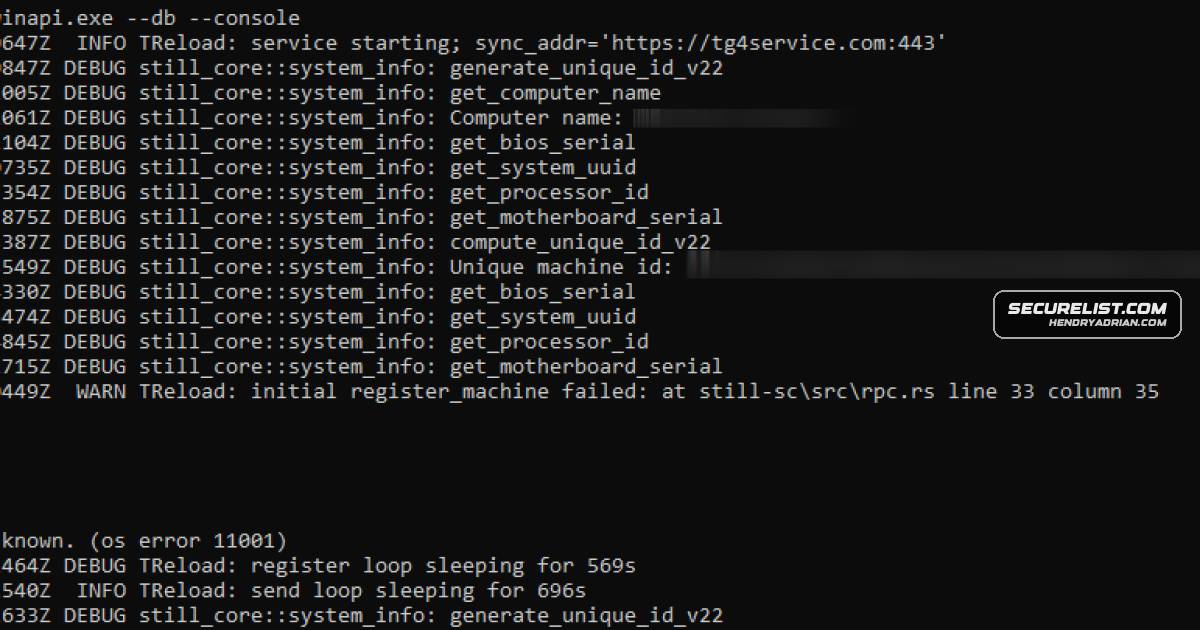
- Still Sync steals Telegram session data and can use the Telegram API to collect account details, chats, and media. Its activity depends on settings retrieved from its command-and-control server.
- Still Audio uses voice-activity detection based on audio signal levels to trigger recording, then sends recordings to a command-and-control server.
- If its command-and-control server is unreachable for three days, Still Audio can retrieve a fallback address from a GitHub repository; the address is Base64-encoded and Blowfish-encrypted.
- Kaspersky says code, encryption, system-identification, and infrastructure similarities support its high-confidence attribution to Armored Likho. It found no direct domain or IP overlap with the February campaign.
- Kaspersky products detect the threat as Trojan.Win64.Agent.* and HEUR:Backdoor.Win32.Generic.
Article Details
- Attack Vectors
- A fake donation-service app, written in Rust using Tauri, prompts the victim for a password and displays a donation catalog while decrypting and launching the next-stage payload.
- Still Sync searches for Telegram tdata files on the victim’s device, then uses the recovered session data to access the victim’s Telegram account and collect chats, media, and account information.
- Still Sync can use Windows backup mechanisms, including Shadow Copy and Robocopy in backup mode, to access files when standard access methods fail.
- Still Audio monitors microphone input, records when its voice-activity threshold is met, and sends the recordings to a command-and-control server.
- If its current command-and-control server remains unreachable for three days, Still Audio retrieves an updated server address from a GitHub repository.
- Defensive Notes
- Kaspersky products detect the threat as Trojan.Win64.Agent.* and HEUR:Backdoor.Win32.Generic.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | managementapiservice[.]com | Domain listed as campaign infrastructure. |
| DOMAIN | orderapiserver[.]info | Campaign infrastructure used by the fake donation app to retrieve catalog data. |
| DOMAIN | screenserv[.]com | Domain listed as campaign infrastructure. |
| DOMAIN | service8date[.]com | Domain listed as campaign infrastructure. |
| DOMAIN | srwinservice[.]com | Default command-and-control domain used by Still Audio. |
| DOMAIN | tg4service[.]com | Still Sync command-and-control domain; also listed as campaign infrastructure. |
| DOMAIN | updateservs[.]com | Domain listed as campaign infrastructure. |
| DOMAIN | windowserv[.]net | Domain listed as campaign infrastructure. |
| IPV4 | 145[.]223[.]68[.]66 | IP address listed in the campaign infrastructure table for updateservs[.]com. |
| IPV4 | 145[.]223[.]69[.]143 | IP address listed in the campaign infrastructure table for service8date[.]com. |
| IPV4 | 159[.]198[.]37[.]74 | IP address listed as campaign infrastructure associated with the tg4service[.]com C2 domain. |
| IPV4 | 187[.]127[.]153[.]38 | IP address listed as campaign infrastructure associated with the orderapiserver[.]info domain. |
| IPV4 | 188[.]212[.]124[.]178 | IP address listed in the campaign infrastructure table for managementapiservice[.]com. |
| IPV4 | 213[.]252[.]244[.]123 | IP address listed as campaign infrastructure associated with the srwinservice[.]com C2 domain. |
| IPV4 | 23[.]26[.]237[.]250 | IP address listed in the campaign infrastructure table for screenserv[.]com. |
| IPV4 | 23[.]27[.]24[.]30 | IP address listed in the campaign infrastructure table for windowserv[.]net. |
| MD5 | 17674b250d8b422a50a86c9ff207186d | MD5 hash of a dropper sample listed in the article. |
| MD5 | 2ca8adbab98ebe305eacf272cf48f5a0 | MD5 hash of a Still Audio sample listed in the article. |
| MD5 | 3ac41b097236a7723821848ae31ef141 | MD5 hash of a Still Audio sample listed in the article. |
| MD5 | 439255736797bc88bd19f282449e0436 | MD5 hash of a Still Audio sample listed in the article. |
| MD5 | 4bd7c352ae277b0e38d07beedd4dd507 | MD5 hash of a Still Sync sample listed in the article. |
| MD5 | 62801f6223e860a7cca271522e303b2d | MD5 hash of a dropper sample listed in the article. |
| MD5 | 68f0365d2fa8c828d012d8859e52a773 | MD5 hash of a Still Sync sample listed in the article. |
| MD5 | c1d1ee16b92e6a138ffa048855f75d7d | MD5 hash of a dropper sample listed in the article. |
| MD5 | d4bc09fb10ea2a5dc0bcbeeda5e5afdd | MD5 hash of a Still Sync sample listed in the article. |
| URL | hxxps[:]//raw[.]githubusercontent[.]com/mmarln/pi-mono/refs/heads/main/packages/pods/src/array12.json | Specific GitHub-hosted dead-drop resolver resource from which Still Audio retrieves the current C2 address. |
MITRE ATT&CK
T1005 · Data from Local SystemStill Sync searches local Telegram tdata directories and collects files containing Telegram session data.T1027 · Obfuscated Files or InformationThe C2 address stored in the GitHub repository is Base64-encoded and encrypted with Blowfish.T1036.005 · Match Legitimate Resource Name or LocationThe Still Audio sample is named IntAudio.exe and appears in Windows microphone settings as “Intel Audio.”T1041 · Exfiltration Over C2 ChannelStill Sync sends collected Telegram data and Still Audio sends recordings to command-and-control servers.T1071.001 · Web ProtocolsThe implants communicate with their command-and-control servers using HTTP or HTTPS, including POST requests.T1078 · Valid AccountsStill Sync uses stolen Telegram session data to authenticate to and access the victim’s account.T1082 · System Information DiscoveryStill Sync collects motherboard and BIOS serial numbers, CPU ID, system UUID, and computer domain name during device registration.T1102.001 · Dead Drop ResolverWhen its current C2 server is unreachable for three days, Still Audio retrieves the current C2 address from a GitHub repository.T1119 · Automated CollectionWhen enabled, Still Sync automatically retrieves Telegram chats, media, and account information through the Telegram API.T1123 · Audio CaptureStill Audio captures microphone audio and records conversations when its voice-activity detection threshold is met.T1204.002 · Malicious FileThe victim launches the fake donation app and interacts with its password prompt and catalog, allowing the dropper to decrypt and launch the next-stage payload.T1543.003 · Windows ServiceStill Sync creates a TReload service and Still Audio creates an auxhost service to continue running in the background.
Threat Actors
Armored LikhoKaspersky assesses with high confidence that Armored Likho is behind the campaign, citing code, encryption, and infrastructure overlaps with its earlier activity.Eagle WerewolfThe article identifies Eagle Werewolf as another name for Armored Likho, which Kaspersky assesses with high confidence is behind the campaign.
Malware
AquilaRATThe campaign shares code, encryption logic, and infrastructure patterns with earlier Armored Likho and AquilaRAT-related activity.Still Audioapp to deliver the Rust-based Still Toolkit, which includes Still Sync for Telegram data theft and Still Audio for covert voice surveillance.Still Synccampaign in Russia using a fake donation app to deliver the Rust-based Still Toolkit, which includes Still Sync for Telegram data theft and Still Audio for covert voice surveillance.
Products
GitHub[T1027 ] Obfuscated Files or Information – The GitHub-based C2 address is Base64-encoded and Blowfish-encrypted (‘the server URL Base64-encoded and encrypted with the Blowfish algorithm’).Microsoft Windows[T1584.001 ] Compromise Infrastructure: Domains – The operators register and use multiple lookalike domains for infrastructure (‘their domain names follow similar naming patterns that mimic Windows system services’).TelegramRussia using a fake donation app to deliver the Rust-based Still Toolkit, which includes Still Sync for Telegram data theft and Still Audio for covert voice surveillance.
Countries
Industries
corporateArmored Likho targeted private individuals and organizations in Russia across corporate, government, IT, and education sectors.EducationArmored Likho targeted private individuals and organizations in Russia across corporate, government, IT, and education sectors.GovernmentArmored Likho targeted private individuals and organizations in Russia across corporate, government, IT, and education sectors.