
Starknex Finds Dataverse and Power Pages Misconfigurations Could Expose Sensitive Data
Summary
Starknex says guest access and overly broad Power Pages permissions can expose Dataverse user data and other records. It links Exfilsquad's breach claims to data consistent with these misconfigurations; 30.3% of surveyed sites remained vulnerable on Aug. 10, 2026.
Key points
- Starknex says guest accounts may access the Dataverse systemusers table in default environments that cannot be scoped to a security group.
- Power Pages Global-scope Read permissions combined with Web API or OData access can expose entire tables; Anonymous Users permissions can make access unauthenticated.
- A directly reachable Entra ID login endpoint may let an existing guest sign in to a portal and receive the Authenticated Users role, even if the login option is hidden.
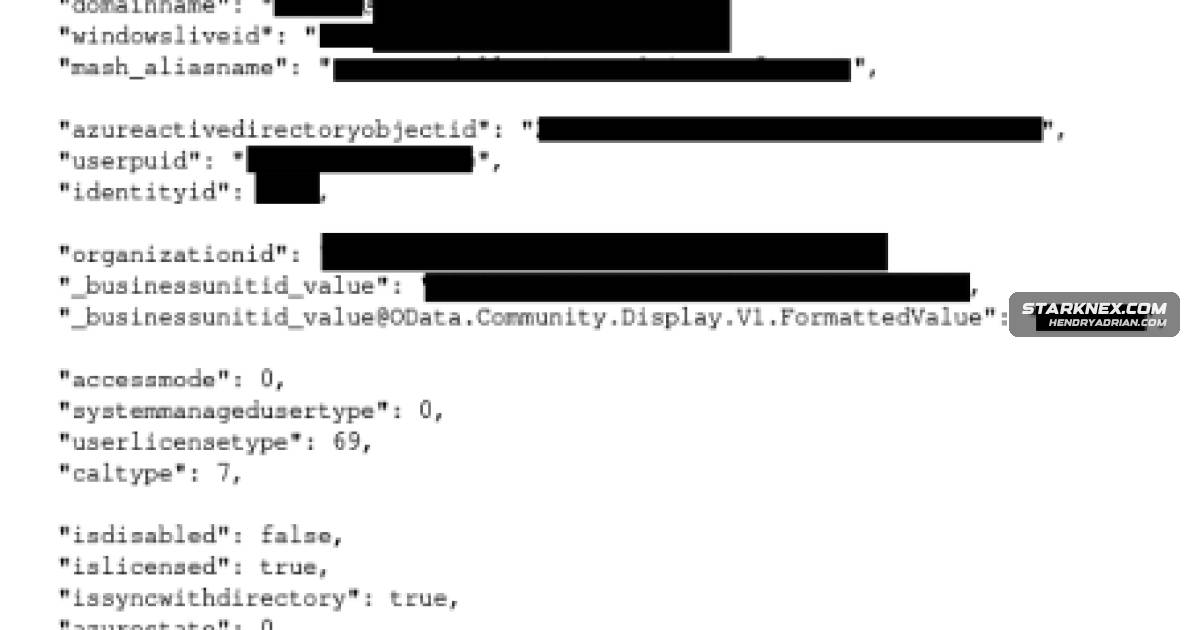
- Potentially exposed records include Entra ID user details, customer PII, documents, support tickets, portal identities, and password hashes on some sites.
- Starknex says Exfilsquad's public breach claims and sample data were consistent with Dataverse records; the article does not establish that the reported exposure resulted in data theft.
- In Starknex's re-sweep, 30.3% of sites remained vulnerable on Aug. 10, 2026, while 69.7% no longer returned exposed records.
- Recommended measures include restricting guest access with Conditional Access, reviewing Global-scope table permissions, disabling unused APIs and OData feeds, auditing access, and using WAF logs for monitoring.
Article Details
- Attack Vectors
- A guest or external account in a tenant may be able to query the Default Dataverse environment's systemusers table through the Web API and enumerate tenant users.
- Power Pages tables with Global-scope Read permissions assigned to Anonymous Users may be exposed without authentication through the Web API or OData feeds; assigning the permission to Authenticated Users can expose data to signed-in guests.
- A guest may be able to authenticate through a directly reachable Entra ID external-login endpoint even when the identity-provider button is hidden, then access tables exposed to the Authenticated Users role.
- Starknex reports that Exfilsquad claimed breaches involving Microsoft Power Apps/Dynamics 365 misconfigurations, with sample data it assessed as consistent with Dataverse records; the access path was not confirmed.
- Defensive Notes
- Use Conditional Access to block guest and external users from Dataverse and apply appropriate policies to each Power Pages portal application.
- Audit guest accounts, remove orphaned or suspicious accounts, restrict guest invitations, and limit guest directory enumeration.
- Assign security groups to non-Default Dataverse environments; the Default environment cannot be security-group scoped.
- Disable unused Power Pages Web API and OData feeds, and audit table permissions for Global-scope Read access, especially for Anonymous Users and Authenticated Users.
- Enable Dataverse auditing and retain logs for incident response and threat hunting.
- Place a WAF in front of Power Pages sites, rate-limit /_api and /_odata requests, and review WAF logs for sequential pagination, high request volumes, and OData query parameters.
- Monitor requests to /api/data/v9.2/systemusers and guest sign-ins to portal enterprise applications; treat guest access to systemusers as requiring review.
MITRE ATT&CK
T1078.004 · Cloud AccountsStarknex describes a possible access path using an existing guest or external cloud account to sign in to a tenant; it assesses that this may have enabled access to Dataverse data, but does not confirm the actor used this path.T1087.004 · Cloud AccountA guest with access to an unscoped Default environment may query the systemusers table through the Dataverse Web API to enumerate tenant users.T1213.004 · Customer Relationship Management SoftwareExfilsquad claimed breaches involving Power Apps/Dynamics 365 misconfigurations, and Starknex assessed the published sample as consistent with records from Dataverse incident, email, contact, and systemusers tables.
Threat Actors
Vendors
Products
Microsoft DataverseStarknex reported a widespread default-configuration exposure in Microsoft Dataverse and Microsoft Power Pages that could allow unauthenticated or guest users to read sensitive records, including Microsoft Entra ID userMicrosoft Dynamics 365actor publicly known as “Exfilsquad”, who has claimed breaches derived from Microsoft Power Apps/Dynamics 365 misconfigurations, describing datasets consistent with Global-scopeMicrosoft Entra IDPower Pages that could allow unauthenticated or guest users to read sensitive records, including Microsoft Entra ID user data, PII, documents, tickets, and portal credentials.Microsoft Power AppsStarknex identified a widespread, default-configuration data exposure affecting Microsoft Dataverse and Microsoft Power Pages (formerly Power Apps Portals).Microsoft Power PagesStarknex reported a widespread default-configuration exposure in Microsoft Dataverse and Microsoft Power Pages that could allow unauthenticated or guest users to read sensitive records, including Microsoft Entra ID user