Fortinet Details Evooo1Bot, a Modular Linux Botnet Targeting Internet-Facing Devices
Summary
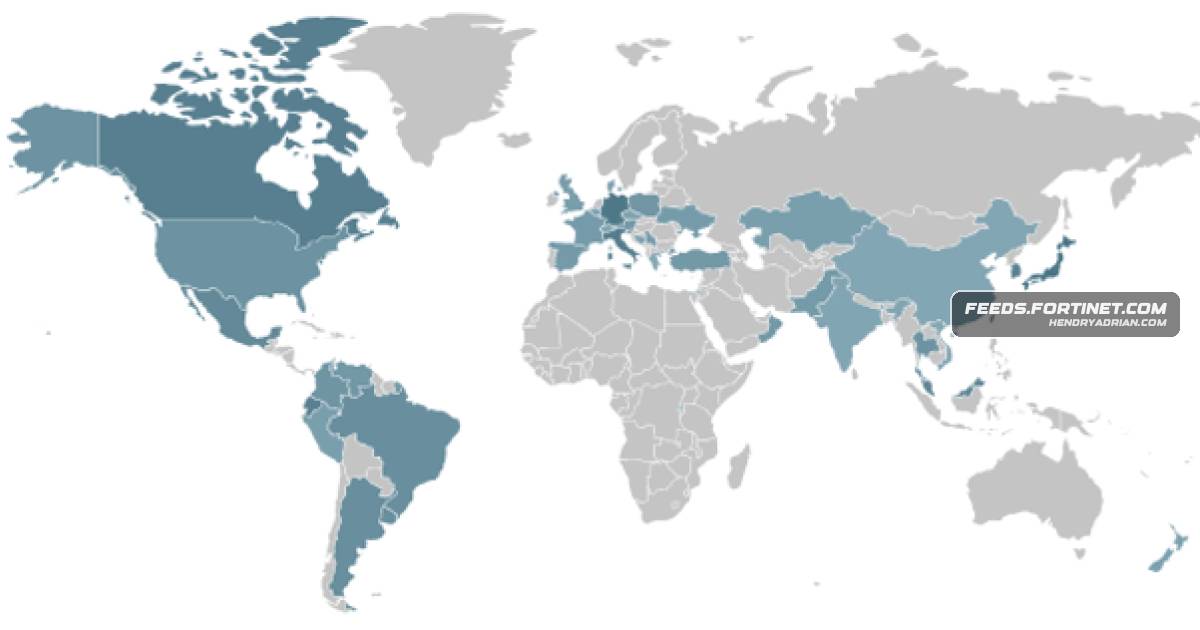
FortiGuard Labs analyzes Evooo1Bot, a Linux botnet observed exploiting vulnerabilities in internet-facing devices since July 2026. Its capabilities include DDoS, SSH brute force, credential sniffing, and SOCKS proxying.
Key points
- FortiGuard Labs observed Evooo1Bot exploitation attempts against internet-facing edge devices beginning in July 2026, using a shared loader to install architecture-specific binaries.
- The botnet targets multiple known vulnerabilities in routers, cameras, network appliances, and enterprise products; some exploit entries are nonfunctional as implemented.
- Its modules include a Mirai-derived DDoS engine, an SSH brute-force scanner with more than 150 credentials, a credential sniffer, and remote shell and file-transfer functions.
- A SOCKS5 relay can turn compromised devices into proxies, including through an outbound encrypted connection that avoids exposing a listener.
- Evooo1Bot uses multiple persistence mechanisms and checks for analysis tools, honeypots, and virtualized environments.
- Fortinet reports antivirus, web-filtering, and IPS protections for the malware and related activity; it recommends patching internet-facing devices, updating firmware, and monitoring outbound connections.
Article Details
- Attack Vectors
- FortiGuard Labs observed exploitation of Internet-facing edge devices, with payload callbacks pointing to a shared loader script.
- The loader downloads and executes architecture-matched binaries using wget, busybox wget, curl, or tftp, then clears Bash history.
- A built-in SSH scanner attempts logins using a dictionary of more than 150 credentials and delivers persistence payloads only after targets pass honeypot checks.
- An HTTP-based exploit dispatcher substitutes an operator-supplied payload host into delivery commands. Some embedded exploit entries have implementation errors and are non-exploitable as shipped, including the reported MOVEit Transfer entry.
- The malware supports remote shell execution, bidirectional file transfers, credential sniffing, SOCKS5 proxying, and multiple DDoS flood methods.
- The persistence command installs systemd, SysV init, cron, shell-profile, and rc.local mechanisms simultaneously.
- Defensive Notes
- Prioritize timely patching and regular firmware updates for Internet-facing devices and network appliances.
- Continuously monitor suspicious outbound connections and promptly remediate vulnerable systems.
- Startup checks search for analysis tools, sandbox services, virtual-machine fingerprints, and container fingerprints; SSH propagation separately checks banners and post-login host characteristics for honeypots.
- C2 connections use port 443 to blend with expected HTTPS traffic, while reverse SOCKS relaying establishes outbound encrypted connections rather than exposing a listening port.
- Fortinet states that FortiGuard Antivirus detects the malware as Linux/Agent.BDS!tr and that up-to-date signatures in its integrated products protect against the described malware components.
- Fortinet states that its Web Filtering Service blocks the C2 server and that its IPS signatures cover the vulnerabilities listed in the protection section.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 91[.]92[.]40[.]118 | IP explicitly listed as an IOC and used to host the Evooo1Bot loader script. |
| SHA256 | 4c0886349e9d348569fffe1b7a31e474d514508bf0cd6f1e5dd99c2a73525e4d | Malware hash listed in the Evooo1Bot IOC section. |
| SHA256 | f13cb360768363d3424e2192c7805b8c8015eb8706dbbbcdead6aed8cf390109 | Malware hash listed in the Evooo1Bot IOC section. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationCompile-time string protection uses AES-256-CTR, ChaCha20, and XOR, with encryption keys split into embedded constants.T1036.004 · Masquerade Task or ServiceThe malicious systemd unit uses Description=Apache HTTPD Cache Manager.T1037.004 · RC ScriptsPersistence installs a SysV init script under /etc/init.d and appends a downloader to /etc/rc.local.T1040 · Network SniffingThe sniffer intercepts HTTP Basic Authorization and Cookie headers and writes captured data to /tmp/.sniff.log.T1053.003 · CronA cron entry downloads and executes the persistence script every five minutes.T1059.004 · Unix ShellPersistence scripts execute through /bin/sh, and remote commands provide interactive shell and command execution capabilities.T1070.003 · Clear Command HistoryThe loader clears Bash history after infection.T1082 · System Information DiscoveryThe !info command returns system information to the operator.T1090.001 · Internal ProxyThe SOCKS5 module turns an infected host into a proxy, using either a local listener or outbound reverse relay connections.T1105 · Ingress Tool TransferThe loader retrieves architecture-specific binaries using wget, busybox wget, curl, or tftp; bot commands also support downloads and self-updates.T1110.001 · Password GuessingThe SSH scanner attempts authentication using an embedded dictionary containing more than 150 credential entries.T1140 · Deobfuscate/Decode Files or InformationThe binary reconstructs keys through XOR at runtime and decrypts more than 60 protected string blocks.T1190 · Exploit Public-Facing ApplicationObserved exploitation of Internet-facing edge devices delivers the shared loader; the malware also contains an HTTP-based vulnerability exploit dispatcher.T1497.001 · System ChecksStartup checks look for analysis tooling, running analysis processes, sandbox services, and VM or container fingerprints; SSH propagation also probes for honeypots.T1498.001 · Direct Network FloodThe DDoS module supports direct UDP, TCP SYN, TCP ACK, GRE, and other network flood methods.T1498.002 · Reflection AmplificationThe DDoS method table includes Valve Source Engine query amplification.T1543.002 · Systemd ServiceThe persistence command creates a systemd unit with Restart=always.T1546.004 · Unix Shell Configuration ModificationPersistence injects a script into /etc/profile.d/ for execution on login.T1573.001 · Symmetric CryptographyEvooo1Bot uses encrypted C2 communications and encrypted outbound connections for its reverse SOCKS relay.
CVE
CVE-2007-3010CVE-2007-3010: Alcatel OmniPCX Enterprise Remote Code Execution VulnerabilityCVE-2016-6277CVE-2016-6277: NETGEAR Multiple Routers Remote Code Execution VulnerabilityCVE-2018-14558CVE-2018-14558: Tenda AC7, AC9, and AC10 Routers Command Injection VulnerabilityCVE-2019-14931CVE-2019-14931: Mitsubishi Electric Europe B.V. ME-RTU devices and INEA ME-RTU devices remote Command Injection vulnerabilityCVE-2020-10987CVE-2020-10987: Tenda AC1900 Router AC15 Model Remote Code Execution VulnerabilityCVE-2021-36260CVE-2021-36260 Hikvision IP Camera /SDK/webLanguageCVE-2021-46422CVE-2021-46422: Telesquare SDT-CW3B1 Command Injection vulnerabilityCVE-2022-26134CVE-2022-26134 Atlassian Confluence /%24%7B%28%23a%3D%40org.apache.commons.io.IOUtilsCVE-2022-29464CVE-2022-29464 WSO2 products /fileupload/CVE-2022-30525CVE-2022-30525 Zyxel Firewall /ztp/cgi-bin/handlerCVE-2022-37055CVE-2022-37055: D-Link Routers Buffer Overflow VulnerabilityCVE-2023-1389CVE-2023-1389 TP-Link Archer AX21 /cgi-bin/luci/;stok=/localeCVE-2023-34362Take CVE-2023-34362 as an example. This vulnerability targets MOVEit Transfer.CVE-2024-10914CVE-2024-10914 D-Link NAS /cgi-bin/account_mgr.cgiCVE-2024-29269CVE-2024-29269, Telesquare TLR-2005KSH Command Injection VulnerabilityCVE-2024-4577CVE-2024-4577 PHP-CGI (Windows) allow_url_include%3DCVE-2025-10123CVE-2025-10123, D-Link DIR-823X Command Injection VulnerabilityCVE-2025-1974CVE-2025-1974 Kubernetes ingress-nginx /apis/networking/v1/ingressesCVE-2025-55583CVE-2025-55583: D-Link DIR-868L B1 router Command Injection Vulnerability
People
Malware
Evooo1BotFortiGuard Labs has been tracking a previously undocumented Linux botnet family, which we have named Evooo1Bot.MiraiWhile the malware reuses the DDoS engine from the publicly leaked Mirai source code, it extends the original framework with numerous capabilities, including encrypted C2 communications, an SSH brute-force scanner, a
Vendors
AlcatelCVE-2007-3010: Alcatel OmniPCX Enterprise Remote Code Execution VulnerabilityAlcatel-Lucentin the download command (for example, -s mitsu for Mitsubishi Electric targets and rep.alcatel for Alcatel-Lucent targets), indicating that the operator independently tracks per-vulnerability infection yield.AtlassianCVE-2022-26134 Atlassian Confluence /%24%7B%28%23a%3D%40org.apache.commons.io.IOUtilsD-LinkCVE-2022-37055: D-Link Routers Buffer Overflow VulnerabilityFortinetFortinet ProtectionsHikvisionCVE-2021-36260 Hikvision IP Camera /SDK/webLanguageINEACVE-2019-14931: Mitsubishi Electric Europe B.V. ME-RTU devices and INEA ME-RTU devices remote Command Injection vulnerabilityMitsubishi ElectricCVE-2019-14931: Mitsubishi Electric Europe B.V. ME-RTU devices and INEA ME-RTU devices remote Command Injection vulnerabilityMitsubishi Electric Europe B.V.CVE-2019-14931: Mitsubishi Electric Europe B.V. ME-RTU devices and INEA ME-RTU devices remote Command Injection vulnerabilityNETGEARCVE-2016-6277: NETGEAR Multiple Routers Remote Code Execution VulnerabilityTelesquareCVE-2021-46422: Telesquare SDT-CW3B1 Command Injection vulnerabilityTendaCVE-2018-14558: Tenda AC7, AC9, and AC10 Routers Command Injection VulnerabilityTP-LinkCVE-2023-1389 TP-Link Archer AX21 /cgi-bin/luci/;stok=/localeWSO2CVE-2022-29464 WSO2 products /fileupload/ZyxelCVE-2022-30525 Zyxel Firewall /ztp/cgi-bin/handler
Products
AC10CVE-2018-14558: Tenda AC7, AC9, and AC10 Routers Command Injection VulnerabilityAC15CVE-2020-10987: Tenda AC1900 Router AC15 Model Remote Code Execution VulnerabilityAC1900CVE-2020-10987: Tenda AC1900 Router AC15 Model Remote Code Execution VulnerabilityAC7CVE-2018-14558: Tenda AC7, AC9, and AC10 Routers Command Injection VulnerabilityAC9CVE-2018-14558: Tenda AC7, AC9, and AC10 Routers Command Injection VulnerabilityAtlassian ConfluenceCVE-2022-26134 Atlassian Confluence /%24%7B%28%23a%3D%40org.apache.commons.io.IOUtilsD-Link NASCVE-2024-10914 D-Link NAS /cgi-bin/account_mgr.cgiDIR-823XCVE-2025-10123, D-Link DIR-823X Command Injection VulnerabilityDIR-868L B1CVE-2025-55583: D-Link DIR-868L B1 router Command Injection VulnerabilityFortiClientThe FortiGuard AntiVirus service engine is integrated into FortiGate, FortiMail, FortiClient, and FortiEDR.FortiEDRThe FortiGuard AntiVirus service engine is integrated into FortiGate, FortiMail, FortiClient, and FortiEDR.FortiGateThe FortiGuard AntiVirus service engine is integrated into FortiGate, FortiMail, FortiClient, and FortiEDR.FortiGuard AntivirusThe malware described in this report is detected and blocked by FortiGuard Antivirus as:FortiGuard IP Reputation and Anti-Botnet Security ServiceThe FortiGuard IP Reputation and Anti-Botnet Security Service proactively blocks infrastructure associated with this campaign by correlating malicious IP intelligence collected from Fortinet’s global sensor network,FortiGuard Web Filtering ServiceThe FortiGuard Web Filtering Service blocks the C2 server.FortiMailThe FortiGuard AntiVirus service engine is integrated into FortiGate, FortiMail, FortiClient, and FortiEDR.Hikvision IP CameraCVE-2021-36260 Hikvision IP Camera /SDK/webLanguageKubernetes ingress-nginxCVE-2025-1974 Kubernetes ingress-nginx /apis/networking/v1/ingressesLinuxAffected Platforms: LinuxME-RTUCVE-2019-14931: Mitsubishi Electric Europe B.V. ME-RTU devices and INEA ME-RTU devices remote Command Injection vulnerabilityMicrosoft WindowsCVE-2024-4577 PHP-CGI (Windows) allow_url_include%3DMOVEit TransferThis vulnerability targets MOVEit Transfer.OmniPCX EnterpriseCVE-2007-3010: Alcatel OmniPCX Enterprise Remote Code Execution VulnerabilityPHP-CGICVE-2024-4577 PHP-CGI (Windows) allow_url_include%3DSDT-CW3B1CVE-2021-46422: Telesquare SDT-CW3B1 Command Injection vulnerabilityTLR-2005KSHCVE-2024-29269, Telesquare TLR-2005KSH Command Injection VulnerabilityTP-Link Archer AX21CVE-2023-1389 TP-Link Archer AX21 /cgi-bin/luci/;stok=/localeZyxel FirewallCVE-2022-30525 Zyxel Firewall /ztp/cgi-bin/handler
Tools
anubisSandbox service name check: sandboxie, cuckoo, anubis, threatexpert, joebox, comodo, hybrid-analysis, cape-sandbox, fireeye, normanbox, and drakvuf.ANY.RUNVM and container environment fingerprints check: vmware, vbox, virtualbox, qemu, firejail, bubblewrap, gvisor, kata, cuckoo, joesandbox, cape, any.run, and hybrid-analysis.auditdwireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit, clamdscan, clamscan, volatility, vol.py,ausearchwireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit, clamdscan, clamscan, volatility, vol.py, and gcorebinwalkidat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit,bpftraceretdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit, clamdscan, clamscan, volatility,busybox wgetThen the loader script wget.sh downloads 12 binary variants using wget, busybox wget, curl, or tftp, in that order.capeSandbox service name check: sandboxie, cuckoo, anubis, threatexpert, joebox, comodo, hybrid-analysis, cape-sandbox, fireeye, normanbox, and drakvuf.cape-sandboxSandbox service name check: sandboxie, cuckoo, anubis, threatexpert, joebox, comodo, hybrid-analysis, cape-sandbox, fireeye, normanbox, and drakvuf.chkrootkitssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit, clamdscan, clamscan, volatility, vol.py, and gcoreclamdscanforemost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit, clamdscan, clamscan, volatility, vol.py, and gcoreclamscansysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit, clamdscan, clamscan, volatility, vol.py, and gcoreCowrieCowrie SSH-2.0-paramiko SSH-2.0-GoCuckooSandbox service name check: sandboxie, cuckoo, anubis, threatexpert, joebox, comodo, hybrid-analysis, cape-sandbox, fireeye, normanbox, and drakvuf.curlThen the loader script wget.sh downloads 12 binary variants using wget, busybox wget, curl, or tftp, in that order.CutterFilesystem presence check: strace, ltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump,drakvufSandbox service name check: sandboxie, cuckoo, anubis, threatexpert, joebox, comodo, hybrid-analysis, cape-sandbox, fireeye, normanbox, and drakvuf.ettercapida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis,fatracetshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit, clamdscan, clamscan, volatility, vol.py, and gcoreforemostobjdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit, clamdscan,FridaRunning process name check: gdb, lldb, strace, ltrace, radare2, r2, rizin, rr, valgrind, perf, ida, ida64, ghidra, sysdig, bpftrace, frida, and frida-serverfrida-serverRunning process name check: gdb, lldb, strace, ltrace, radare2, r2, rizin, rr, valgrind, perf, ida, ida64, ghidra, sysdig, bpftrace, frida, and frida-servergcoreausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit, clamdscan, clamscan, volatility, vol.py, and gcoregdbFilesystem presence check: strace, ltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump,GhidraFilesystem presence check: strace, ltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump,ghidraRunpresence check: strace, ltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep,GLUTTONGlutton russh_ SSH-2.0-ServerHonSSHHonSSH Twisted SSH-2.0-CISCO_WLChybrid-analysisSandbox service name check: sandboxie, cuckoo, anubis, threatexpert, joebox, comodo, hybrid-analysis, cape-sandbox, fireeye, normanbox, and drakvuf.iaitoFilesystem presence check: strace, ltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump,IDAcheck: strace, ltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap,ida64strace, ltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara,idatltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep,idat64gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk,inotifywaitngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit, clamdscan, clamscan, volatility, vol.py, and gcorejoeboxSandbox service name check: sandboxie, cuckoo, anubis, threatexpert, joebox, comodo, hybrid-analysis, cape-sandbox, fireeye, normanbox, and drakvuf.joesandboxVM and container environment fingerprints check: vmware, vbox, virtualbox, qemu, firejail, bubblewrap, gvisor, kata, cuckoo, joesandbox, cape, any.run, and hybrid-analysis.KippoKippo SSH-2.0-libssh SSH-2.0-ParkslldbFilesystem presence check: strace, ltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump,ltraceFilesystem presence check: strace, ltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump,lynisettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit, clamdscan, clamscan, volatility, vol.py, and gcorengrepghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait,normanboxSandbox service name check: sandboxie, cuckoo, anubis, threatexpert, joebox, comodo, hybrid-analysis, cape-sandbox, fireeye, normanbox, and drakvuf.objdumplldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk,OpenCanaryOpenCanary ssh2js SSH-2.0-MocanaSSHperfFilesystem presence check: strace, ltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump,r2Filesystem presence check: strace, ltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump,radare2Filesystem presence check: strace, ltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump,readelfvalgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig,retdec-decompilerradare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace,rizinFilesystem presence check: strace, ltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump,rkhunteryara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit, clamdscan, clamscan, volatility, vol.py, and gcorerrRunning process name check: gdb, lldb, strace, ltrace, radare2, r2, rizin, rr, valgrind, perf, ida, ida64, ghidra, sysdig, bpftrace, frida, and frida-serversandboxieSandbox service name check: sandboxie, cuckoo, anubis, threatexpert, joebox, comodo, hybrid-analysis, cape-sandbox, fireeye, normanbox, and drakvuf.ssdeepidat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter,StraceFilesystem presence check: strace, ltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump,sysdigreadelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit, clamdscan, clamscan,tcpdumpghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace,tftpThen the loader script wget.sh downloads 12 binary variants using wget, busybox wget, curl, or tftp, in that order.threatexpertSandbox service name check: sandboxie, cuckoo, anubis, threatexpert, joebox, comodo, hybrid-analysis, cape-sandbox, fireeye, normanbox, and drakvuf.tsharkiaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace,valgrindFilesystem presence check: strace, ltrace, gdb, lldb, valgrind, perf, radare2, r2, rizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump,vol.pyauditd, ausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit, clamdscan, clamscan, volatility, vol.py, and gcorevolatilitybpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter, chkrootkit, clamdscan, clamscan, volatility, vol.py, and gcorewgetWe observed active exploitation attempts targeting a range of edge devices, with all payload callbacks pointing to the same loader URL at 91.92.40[.]118/wget.sh.Wiresharkrizin, cutter, iaito, ghidra, ghidraRun, ida, ida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch,YARAida64, idat, idat64, objdump, readelf, retdec-decompiler, wireshark, tshark, tcpdump, ngrep, ettercap, yara, ssdeep, binwalk, foremost, sysdig, bpftrace, auditd, ausearch, fatrace, inotifywait, lynis, rkhunter,