
Investigation Links XSS Moderator Quake3 to Alleged REvil Developer Persona
Summary
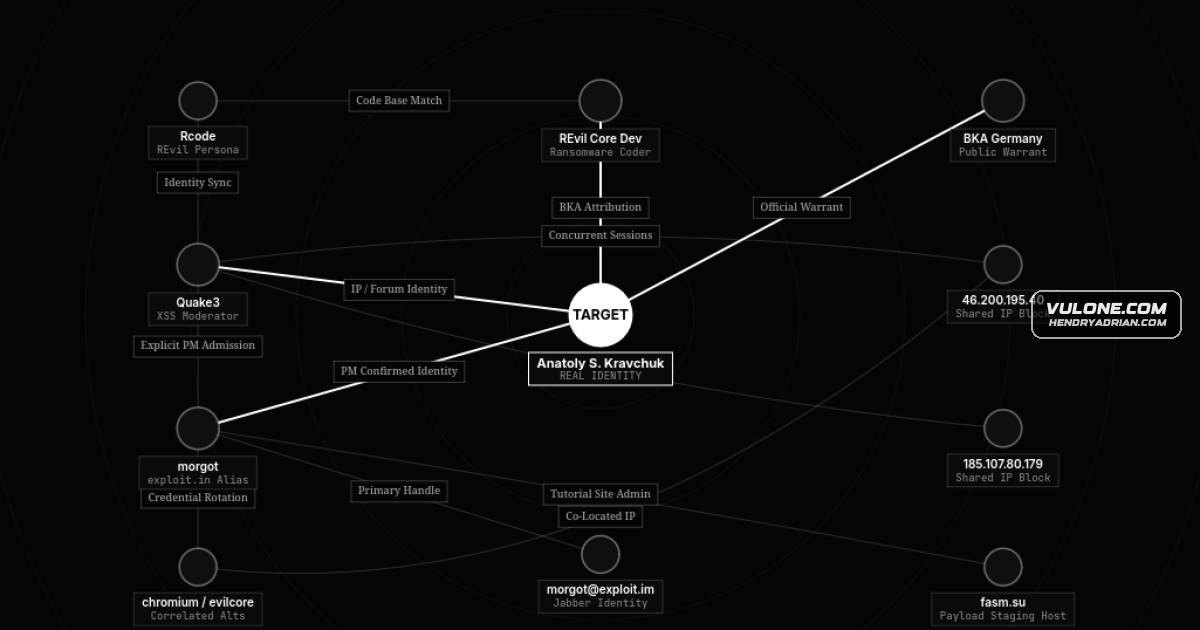
An investigation links Quake3 to morgot, chromium and evilcore using forum messages and shared IP activity, then connects those identities to a REvil developer persona. The proposed real-world identification is assessed with moderate confidence.
Key points
- The investigation cites September and October 2018 messages in which Quake3 identified himself as morgot, a moderator on exploit[.]in.
- According to the reported forum logs, Quake3, chromium and evilcore alternated activity on two IP addresses unused by other accounts; clustered password changes provide additional attribution evidence.
- Historical correspondence describes offers to build MBR lockers, loaders and botnet administration tools, alongside a malware-review service involving limited reverse engineering.
- A loader builder distributed through fasm[.]su reportedly downloaded and launched a configured executable; the quoted developer acknowledged antivirus alerts from network activity and process creation.
- The article connects the aliases to a REvil developer persona through DEF CON 33 reporting, while assessing the identification as Anatoly Sergeevitsch Kravchuk with moderate confidence.
- The article reports that German authorities named Kravchuk as a REvil developer. Its forum-account correlations and historical coding activity do not independently establish that he authored REvil.
Article Details
- Attack Vectors
- A loader builder distributed in 2013 allowed customers to specify a remotely hosted executable and its local filename; the loader downloaded and launched the executable.
- The article describes REvil using msmpeng.exe DLL side-loading, RC4-obfuscated configuration, and ECC Curve25519 / Salsa20 encryption.
- Historical correspondence describes offers to develop MBR lockers, botnet command queues, and account brute-force software. The custom locker negotiation ended when the subject reported that available antivirus-evasion methods were detected.
- Defensive Notes
- The historical loader's author identified network activity and creation of a new executable process as observable antivirus alert sources.
- Treat the historical fasm.su loader resource as time-bound evidence: the article states that the original domain expired and was re-registered by an unrelated organization in 2019.
- The article assesses the link between the forum persona and Anatoly Sergeevitsch Kravchuk with moderate confidence; it explicitly does not prove that a specific passport-holder wrote specific REvil code.
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe article describes REvil configuration obfuscation using RC4.T1055 · Process InjectionHistorical correspondence attributed to Quake3 discusses Andromeda injection and a mapping-based loader evasion method, which he said antivirus products had begun detecting.T1105 · Ingress Tool TransferQuake3 described a working loader that downloaded an executable from a customer-specified hosting path and then launched it.T1486 · Data Encrypted for ImpactThe article describes REvil ransomware encryption using ECC Curve25519 / Salsa20 and cites authorities alleging its use in German extortions.T1574.002 · DLL Side-LoadingThe article identifies msmpeng.exe DLL side-loading as part of REvil's implementation.
People
Threat Actors
Anatoly Sergeevitsch KravchukAccording to the article's account of BKA and Karlsruhe authorities, accused of programming REvil malware and its darknet page. The investigation assesses his identity link to Quake3, Morgot, and Rcode with moderate confidence rather than claiming definitive proof.chromiumThe article infers that this forum account was operated by Quake3 from shared IP addresses and account-maintenance timing, and alleges its involvement in a multi-account voting scheme.evilcoreThe article infers that this forum account was operated by Quake3 from shared IP addresses and interleaved activity, and alleges its involvement in contest vote manipulation.MorgotName used in the cited DEF CON 33 operator table for REvil's source-code developer, with Rcode and Quake3 listed as aliases; the article links this persona to Quake3's self-identification as morgot.Quake3Forum persona whose quoted correspondence offers loader and locker development. The article links Quake3 to morgot through self-identification, cites DEF CON 33 reporting associating Quake3, Morgot, and Rcode with REvil source-code development, and assesses the passport identity as Anatoly Sergeevitsch Kravchuk with moderate confidence.UNKNThe article identifies UNKN as Daniil Maksimovich Shchukin's alias and reports that he advertised REvil on XSS in June 2019 and recruited affiliates.