Evooo1Bot Linux Botnet Combines Mirai DDoS Code With Exploits and SOCKS Relays
Summary
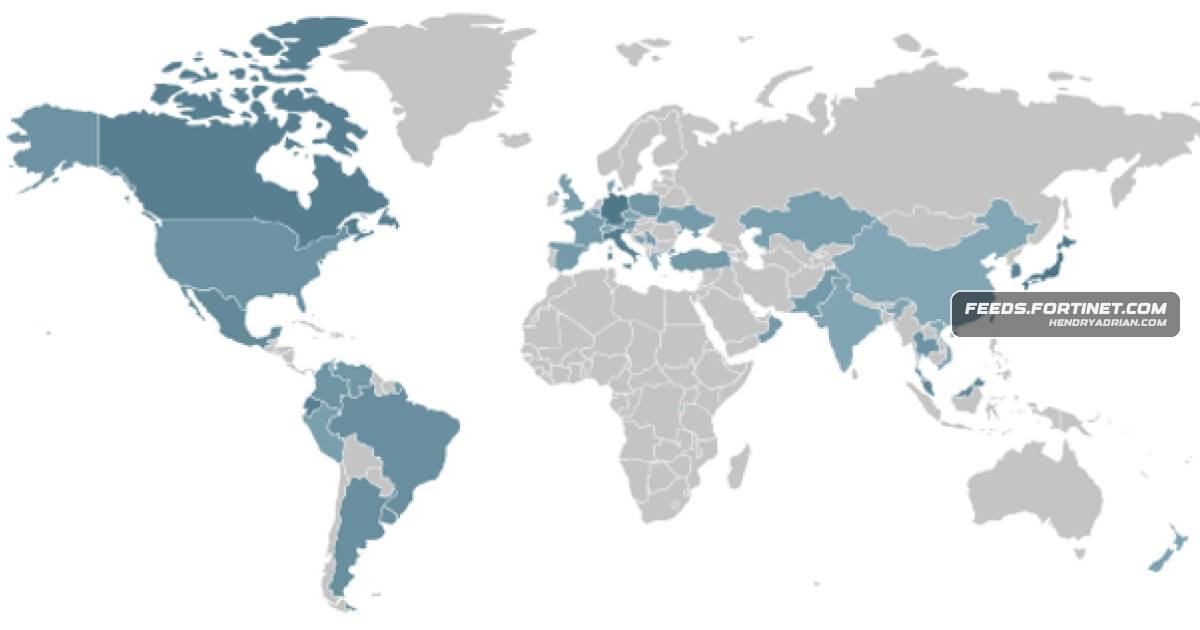
Fortinet researchers detail Evooo1Bot, a Linux botnet exploiting vulnerabilities in internet-facing devices. It combines Mirai-derived DDoS, SSH brute forcing, credential sniffing, persistence, and SOCKS proxy capabilities.
Key points
- Fortinet telemetry observed the botnet targeting internet-facing devices since July 2026, using multiple known vulnerabilities across edge devices and enterprise products.
- The malware downloads CPU-specific binaries through a loader, establishes encrypted C2 communications over port 443, and uses anti-analysis checks.
- Its capabilities include SSH brute forcing with more than 150 credentials, HTTP credential and cookie sniffing, file transfer, remote shell access, and 16 DDoS methods.
- A reverse SOCKS relay can route attacker traffic through compromised systems, potentially masking its origin or enabling access to internal networks.
- Persistence methods include systemd, SysV init, cron, shell profiles, and rc.local; the malware also supports self-updating.
- Fortinet says its antivirus detects the malware and its security services block associated infrastructure; it recommends patching exposed devices and monitoring suspicious outbound connections.
Article Details
- Attack Vectors
- Exploits vulnerabilities in internet-facing routers, edge devices, and enterprise applications to download and execute architecture-matched botnet binaries.
- Brute-forces SSH using an embedded credential dictionary, then delivers the payload to hosts that pass its honeypot checks.
- Uses infected hosts for DDoS attacks, SOCKS5 proxy relaying, credential sniffing, and remote command execution.
- Defensive Notes
- Prioritize patching and firmware updates for internet-facing devices and network appliances, and monitor for suspicious outbound connections.
- Fortinet reports that FortiGuard Antivirus detects the malware as Linux/Agent.BDS!tr, its Web Filtering Service blocks the C2 server, and IPS signatures cover the listed exploit activity.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 91[.]92[.]40[.]118 | IP address serving the wget.sh loader used to deliver Evooo1Bot payloads. |
| SHA256 | 4c0886349e9d348569fffe1b7a31e474d514508bf0cd6f1e5dd99c2a73525e4d | Hash listed in the article's Evooo1Bot IOCs. |
| SHA256 | f13cb360768363d3424e2192c7805b8c8015eb8706dbbbcdead6aed8cf390109 | Hash listed in the article's Evooo1Bot IOCs. |
MITRE ATT&CK
T1037.004 · RC ScriptsA persistence option appends a script to /etc/rc.local.T1040 · Network SniffingThe sniffer reads /proc/net/tcp, intercepts HTTP Basic Authorization and Cookie headers, and writes them to a log file.T1053.003 · CronA persistence option installs a cron task that downloads and executes a script every five minutes.T1059.004 · Unix ShellThe loader and persistence mechanisms execute shell commands and scripts on infected Linux systems.T1090.003 · Multi-hop ProxyThe SOCKS module turns infected hosts into proxy relays, including through an outbound connection to an operator-specified relay server.T1105 · Ingress Tool TransferThe wget.sh loader downloads and executes architecture-matched botnet binaries; the malware also supports self-update downloads.T1110.001 · Password GuessingIts built-in SSH scanner attempts logins using an embedded dictionary of more than 150 credentials.T1190 · Exploit Public-Facing ApplicationEvooo1Bot exploits vulnerabilities in internet-facing devices and applications to deliver its payload.T1498.001 · Direct Network FloodThe botnet's DDoS module includes UDP, TCP SYN, DNS, and HTTP flood methods.T1543.002 · Systemd ServiceA persistence option installs a systemd service configured to restart automatically.T1546.004 · Unix Shell Configuration ModificationA persistence option injects a script into /etc/profile.d/ for execution at login.
CVE
CVE-2007-3010CVE-2007-3010: Alcatel OmniPCX Enterprise Remote Code Execution VulnerabilityCVE-2016-6277CVE-2016-6277: NETGEAR Multiple Routers Remote Code Execution VulnerabilityCVE-2018-14558CVE-2018-14558: Tenda AC7, AC9, and AC10 Routers Command Injection VulnerabilityCVE-2019-14931CVE-2019-14931: Mitsubishi Electric Europe B.V. ME-RTU devices and INEA ME-RTU devices remote Command Injection vulnerabilityCVE-2020-10987CVE-2020-10987: Tenda AC1900 Router AC15 Model Remote Code Execution VulnerabilityCVE-2021-36260CVE-2021-36260 Hikvision IP Camera /SDK/webLanguageCVE-2021-46422CVE-2021-46422: Telesquare SDT-CW3B1 Command Injection vulnerabilityCVE-2022-26134CVE-2022-26134 Atlassian Confluence /%24%7B%28%23a%3D%40org.apache.commons.io.IOUtilsCVE-2022-29464CVE-2022-29464 WSO2 products /fileupload/CVE-2022-30525CVE-2022-30525 Zyxel Firewall /ztp/cgi-bin/handlerCVE-2022-37055CVE-2022-37055: D-Link Routers Buffer Overflow VulnerabilityCVE-2023-1389CVE-2023-1389 TP-Link Archer AX21 /cgi-bin/luci/;stok=/localeCVE-2024-10914CVE-2024-10914 D-Link NAS /cgi-bin/account_mgr.cgiCVE-2024-29269CVE-2024-29269, Telesquare TLR-2005KSH Command Injection VulnerabilityCVE-2024-4577CVE-2024-4577 PHP-CGI (Windows) allow_url_include%3DCVE-2025-10123CVE-2025-10123, D-Link DIR-823X Command Injection VulnerabilityCVE-2025-1974CVE-2025-1974 Kubernetes ingress-nginx /apis/networking/v1/ingressesCVE-2025-55583CVE-2025-55583: D-Link DIR-868L B1 router Command Injection Vulnerability
People
Malware
Evooo1BotFortiGuard Labs has been tracking a previously undocumented Linux botnet family, which we have named Evooo1Bot.MiraiWhile the malware reuses the DDoS engine from the publicly leaked Mirai source code, it extends the original framework with numerous capabilities, including encrypted C2 communications, an SSH brute-force scanner, a
Vendors
Alcatel-Lucentin the download command (for example, -s mitsu for Mitsubishi Electric targets and rep.alcatel for Alcatel-Lucent targets), indicating that the operator independently tracks per-vulnerability infection yield.AtlassianCVE-2022-26134 Atlassian Confluence /%24%7B%28%23a%3D%40org.apache.commons.io.IOUtilsD-LinkCVE-2022-37055: D-Link Routers Buffer Overflow VulnerabilityHikvisionCVE-2021-36260 Hikvision IP Camera /SDK/webLanguageINEACVE-2019-14931: Mitsubishi Electric Europe B.V. ME-RTU devices and INEA ME-RTU devices remote Command Injection vulnerabilityMitsubishi ElectricCVE-2019-14931: Mitsubishi Electric Europe B.V. ME-RTU devices and INEA ME-RTU devices remote Command Injection vulnerabilityNETGEARCVE-2016-6277: NETGEAR Multiple Routers Remote Code Execution VulnerabilityTelesquareCVE-2021-46422: Telesquare SDT-CW3B1 Command Injection vulnerabilityTendaCVE-2018-14558: Tenda AC7, AC9, and AC10 Routers Command Injection VulnerabilityTP-LinkCVE-2023-1389 TP-Link Archer AX21 /cgi-bin/luci/;stok=/localeWSO2CVE-2022-29464 WSO2 products /fileupload/ZyxelCVE-2022-30525 Zyxel Firewall /ztp/cgi-bin/handler
Products
Alcatel OmniPCX EnterpriseCVE-2007-3010: Alcatel OmniPCX Enterprise Remote Code Execution VulnerabilityAtlassian ConfluenceCVE-2022-26134 Atlassian Confluence /%24%7B%28%23a%3D%40org.apache.commons.io.IOUtilsD-Link DIR-823XCVE-2025-10123, D-Link DIR-823X Command Injection VulnerabilityD-Link DIR-868L B1CVE-2025-55583: D-Link DIR-868L B1 router Command Injection VulnerabilityHikvision IP CameraCVE-2021-36260 Hikvision IP Camera /SDK/webLanguageINEA ME-RTUCVE-2019-14931: Mitsubishi Electric Europe B.V. ME-RTU devices and INEA ME-RTU devices remote Command Injection vulnerabilityKubernetes ingress-nginxCVE-2025-1974 Kubernetes ingress-nginx /apis/networking/v1/ingressesLinuxAffected Platforms: LinuxPHP-CGICVE-2024-4577 PHP-CGI (Windows) allow_url_include%3DProgress MOVEit TransferThis vulnerability targets MOVEit Transfer.Telesquare SDT-CW3B1CVE-2021-46422: Telesquare SDT-CW3B1 Command Injection vulnerabilityTelesquare TLR-2005KSHCVE-2024-29269, Telesquare TLR-2005KSH Command Injection VulnerabilityTenda AC1900 Router AC15CVE-2020-10987: Tenda AC1900 Router AC15 Model Remote Code Execution VulnerabilityTenda AC7CVE-2018-14558: Tenda AC7, AC9, and AC10 Routers Command Injection VulnerabilityTP-Link Archer AX21CVE-2023-1389 TP-Link Archer AX21 /cgi-bin/luci/;stok=/localeZyxel FirewallCVE-2022-30525 Zyxel Firewall /ztp/cgi-bin/handler