cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2375 articles

Threat Research · infoblox.com

Infoblox Links Sable Squirrel’s Expired Domains to Streaming, Gambling and RAT C2

Infoblox reports that Sable Squirrel controls over 10,000 domains and estimates it spent more than $7 million acquiring expired domains. Its investigation links 405 domains to malware C2 and over 31,000 samples, but does not confirm ransomware execution.
Nov 5, 2026
Threat Research · securelist.com

Kaspersky Details Storm-2603’s Fileless ToolShell Intrusion and Detection Clues

Kaspersky analyzes a Storm-2603-attributed ToolShell intrusion using an in-memory SharePoint webshell, Velociraptor and tunneling tools. Kaspersky says its endpoint protection blocked a Warlock ransomware launch attempt and details runtime detection clues.

Nov 5, 2026
Threat Research · socradar.io

ARTEX AI Framework Linked to Multiple 2026 Intrusion Campaigns

SOCRadar reviews reports linking ARTEX, an LLM-agent pentesting framework, to espionage and financially motivated intrusions. CrowdStrike reported 200+ targets and nine confirmed post-exploitation victims; suggested defenses focus on identity hardening and behavior-

Nov 5, 2026
Threat Research · bitdefender.com

GhostMap Android Flaw Can Trigger Persistent Crash Loops From a Crafted App

Bitdefender researchers detail GhostMap, an Android ZIP-parsing flaw that can make a crafted app trigger a persistent system crash loop, potentially requiring a data-erasing reset. Reproduced on Android 10+; no in-the-wild use observed, and Google says no security fix.

Nov 5, 2026
Threat Research · aikido.dev

RubyGems Extensions and Plugins Can Execute Code During Installation

Aikido reports that RubyGems extensions and plugins can execute code during installation, and plugins can run on later gem commands. It found four gems sending data; opt-out controls are available in RubyGems and Bundler 4.1 prereleases, not stable 4.0.x.

Nov 5, 2026
Threat Research · hunt.io

Researchers Trace PHP2Shell PAN-OS Exploitation From Reconnaissance to Enterprise Access

Hunt.io researchers analyzed an exposed toolkit documenting PAN-OS exploitation, reporting 19,182 scanned management portals and logs indicating 25 root compromises. They detail the exploit chain, persistence, lateral movement, and AI-assisted tooling.

Nov 5, 2026
Threat Research · security.com

Anubis Ransomware Attack Used Lindnor Backdoor and BYOVD Tools, but Encryption Was Blocked

In an October 2026 intrusion, Anubis operators used the newly identified Backdoor.Lindnor, 13 security-disabling executables, five vulnerable drivers and AnyDesk configured for Safe Mode. The encryption payload was blocked; no files were reported encrypted.

Nov 5, 2026
Threat Research · bleepingcomputer.com

CWPdoor Backdoor Hides in Trojanized CWP Web Server

XLab says CWPdoor is distributed through a trojanized CWP web server. The passive backdoor accepts signed, encrypted HTTP commands and suppresses access logs; researchers recommend checking for indicators and replacing compromised binaries.

Nov 5, 2026
Threat Research · bleepingcomputer.com

Fake AI Event Invitations Use Phishing Kits to Target Microsoft and Google Accounts

Push Security reports that fake OpenAI, SpaceX and Anthropic event pages use Kali365 device-code phishing and VoidProxy AiTM attacks to steal Microsoft and Google credentials and sessions.

Nov 5, 2026
Threat Research · crowdstrike.com

CrowdStrike Finds Adversaries Weaponize Public Vulnerability Research Within Hours

CrowdStrike observed a median of less than a day from public POC release to exploitation; 91% of observed vulnerabilities with public POCs were exploited within 48 hours. Case studies show adversaries adapting public exploits.

Nov 5, 2026
Threat Research · sonatype.com

Researchers Link Loaders in 12 Hijacked npm Releases to PolinRider Activity

Sonatype found concealed loaders in 12 releases across 10 hijacked npm packages. They use Ethereum transactions to locate and execute remote JavaScript; shared wallet, infrastructure, and retrieval paths support a link to PolinRider activity.

Nov 4, 2026
Threat Research · sekoia.com

Sekoia Details APT29-Linked Watering-Hole Campaign Using Patched Mobile Exploits

Sekoia details a watering-hole campaign assessed with moderate-to-high confidence as APT29, using compromised sites and Plerdy to deliver patched iOS and Android exploits that stole cookies, Wi-Fi passwords and device data.

Nov 4, 2026
Threat Research · netspi.com

NetSPI Demonstrates Microsoft Graph Notifications for Email and Teams Data Exfiltration

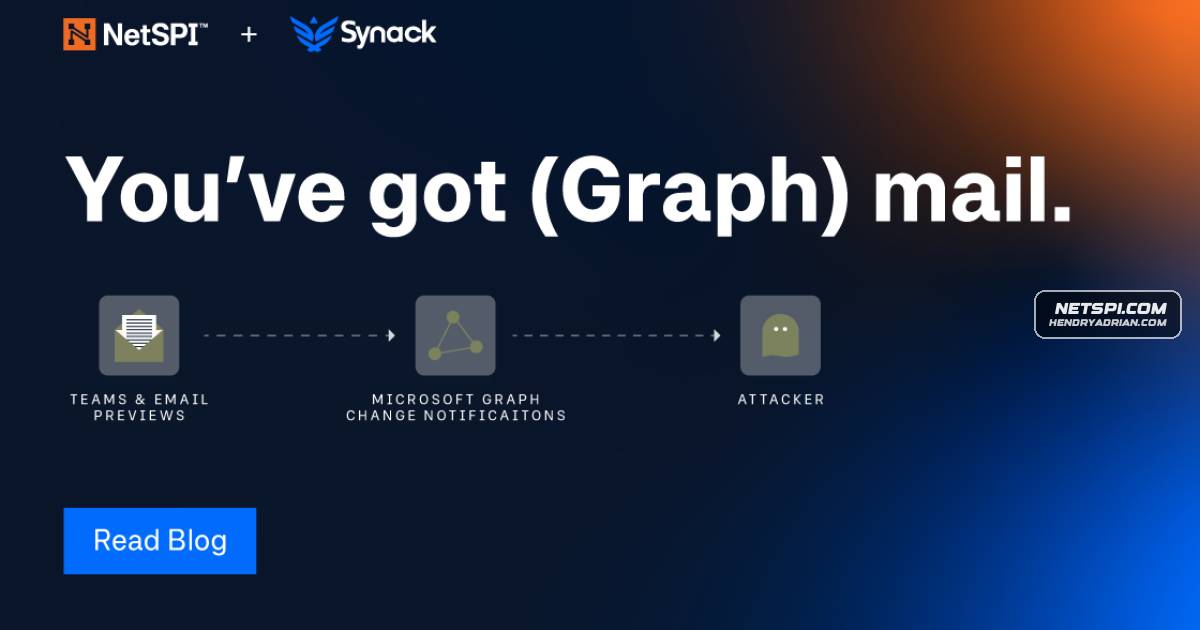
NetSPI demonstrates how attackers with compromised user or service-principal access can use Microsoft Graph Rich Notifications to exfiltrate Outlook snippets and Teams messages, and describes monitoring via the added GraphNotificationsActivityLogs table.

Nov 4, 2026
Threat Research · rogueauthority.org

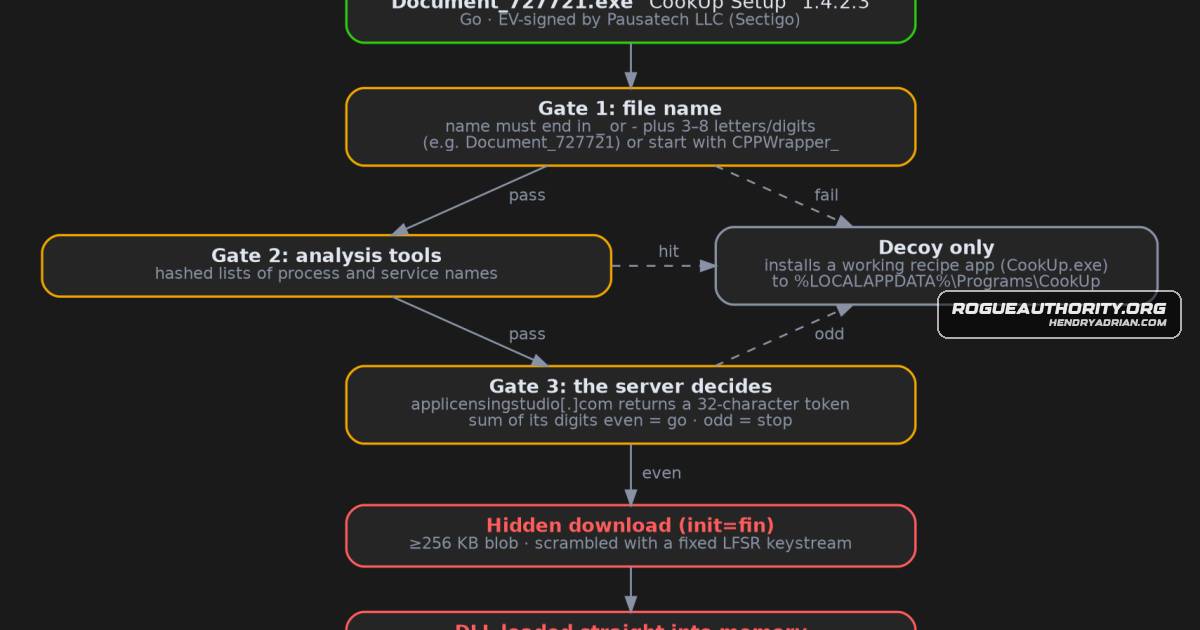
CookUp Installer Uses Server-Side Gating to Hide an In-Memory DLL Loader

Researchers mapped a signed CookUp installer that installs a harmless recipe app but can use three gates and a server-issued token to fetch and run a DLL in memory. The server refused observed sessions, leaving the final payload unknown.

Nov 4, 2026
Threat Research · thehackernews.com

SlippyNunchucks Uses Sogou DNS Hijacking to Deliver DarkVigil

ESET attributes a surveillance campaign to SlippyNunchucks, which tampered with DNS responses for Sogou Input Method’s HTTP configuration requests to deliver DarkVigil. Tencent patched the issue in version 16.10 (CVE-2026-120422).

Nov 4, 2026
Threat Research · rogueauthority.org

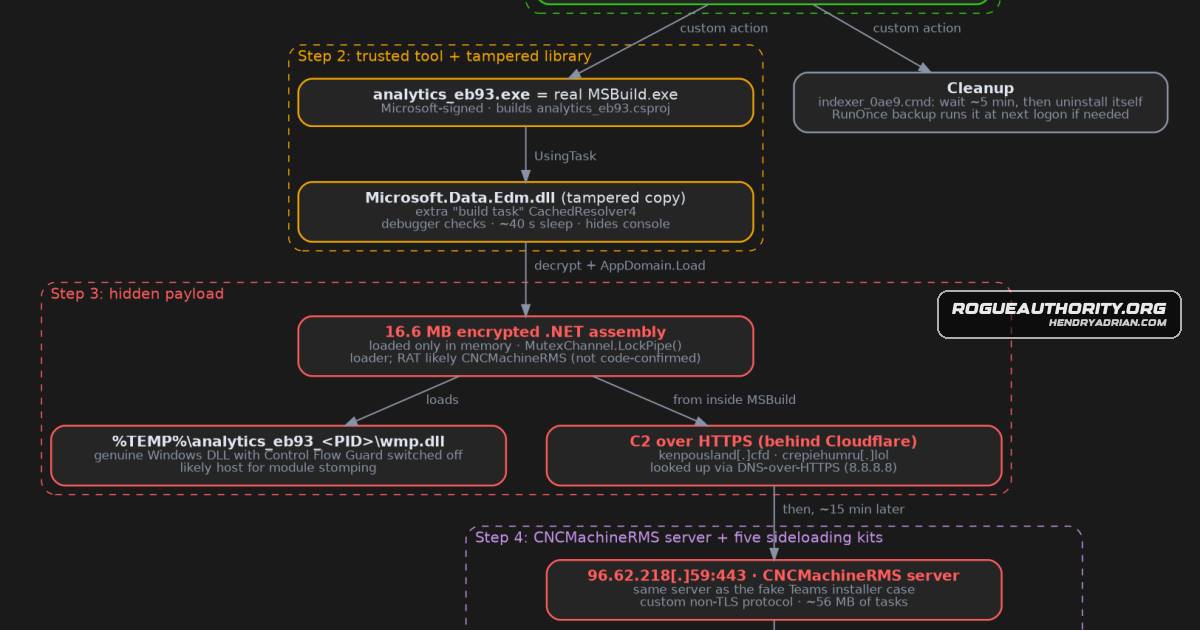
Fake Marvell RAID Utility Uses Signed MSBuild to Load Malware

A fake Marvell RAID MSI uses renamed Microsoft-signed MSBuild and a tampered .NET library to decrypt and run a payload in memory, then downloads five DLL-sideloading kits. Researchers link its C2 to CNCMachineRMS by behavior, but have no code-level match.

Nov 4, 2026
Threat Research · reversinglabs.com

TraderTraitor Toolkit Analysis Finds Earlier Malware, but Binance Link Remains Unconfirmed

ReversingLabs details TraderTraitor-associated developer malware found in telemetry before public disclosure, including earlier ROOFDECK samples. The FBI attributed the Binance theft to TraderTraitor, but no link to the analyzed samples is established.

Nov 4, 2026
Threat Research · acronis.com

Acronis Details BOSSAI AI-Agent Campaign Targeting 11 Countries

Acronis TRU describes BOSSAI, a 12-agent AI attack mesh operated by one person and used against organizations in 11 countries. The investigation reports confirmed data access or exfiltration at roughly 10 targets, including emergency services and universities.

Nov 4, 2026
Threat Research · databreachtoday.com

AI Models Succeed in Eight OT Attack Scenarios in Isolated Lab Tests

Booz Allen researchers found two AI models succeeded across eight OT attack scenarios in an isolated lab. Human approval was required for physical actions; conventional defenses slowed the models but did not consistently stop them.

Nov 4, 2026
Threat Research · bleepingcomputer.com

Operation CloudFire Used Calendar Invites to Hijack Google Sessions and Bypass MFA

Material Security says Operation CloudFire used Google Calendar invites, reverse-proxied sign-in pages, and relayed MFA prompts to capture live Google sessions. Its takedown effort reported 897 domains over one month; activity appears to have dispersed.

Nov 4, 2026
Threat Research · circleid.com

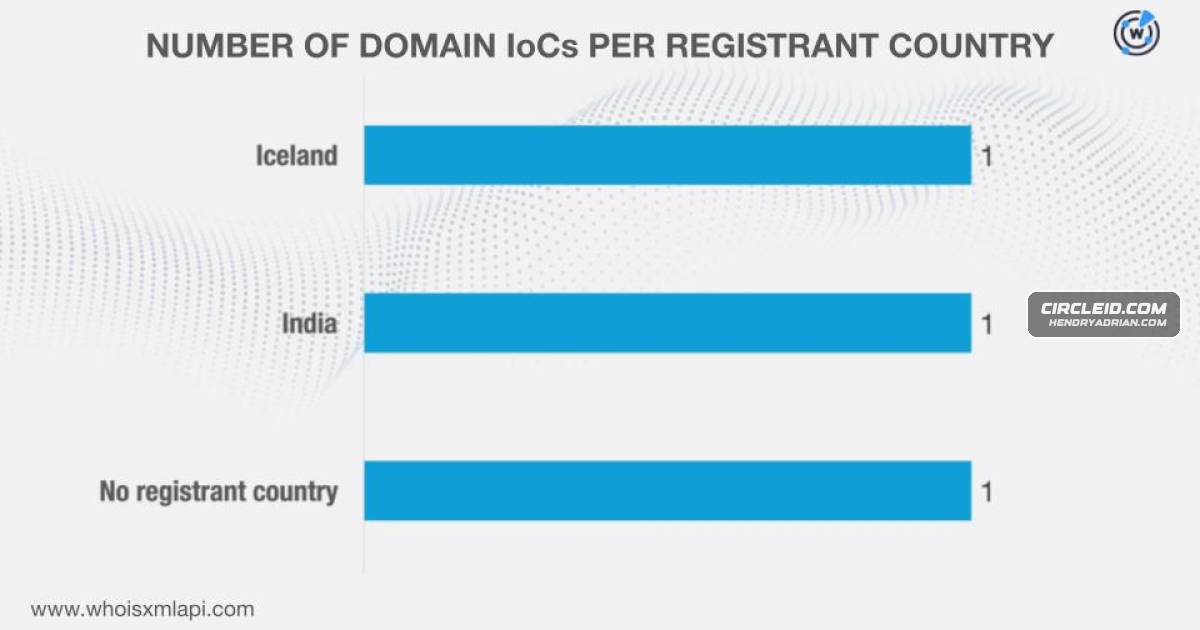
APT36 Uses Four Malware Variants in RapidRust Campaign, DNS Analysis Finds

A DNS investigation of APT36’s RapidRust campaign linked its known indicators to 341 email-connected domains, lookalike domains, and two IPs classified as malicious by a threat-intelligence API. The authors caution that some flagged entities may be benign.

Nov 4, 2026
Threat Research · welivesecurity.com

ESET Details SlippyNunchucks’ Sogou Input Method Hijack to Deploy DarkVigil

ESET details how SlippyNunchucks allegedly hijacked Sogou Input Method’s insecure HTTP traffic to deliver DarkVigil via a malicious configuration. The DNS manipulation point remains unknown; Tencent fixed the issue in version 16.10.

Nov 4, 2026
Threat Research · hunt.io

Hunt.io Traces ARTEX Infrastructure Through Exposed Directories and Tooling

Hunt.io analyzed exposed directories linked to ARTEX, finding AI model-routing components, remote-access and proxy tools, and staged JNDI/LDAP exploitation infrastructure. The artifacts’ relationship to the reported South Korean breaches remains unconfirmed.

Nov 4, 2026
Threat Research · chainalysis.com

Chainalysis Details DPRK Fake-Interview Tactics and Blockchain-Based C2

Chainalysis describes DPRK-linked fake-interview schemes, their reported losses, and blockchain-based malware C2 techniques. Binance’s initial findings say a fake job process gave attackers an employee foothold; the investigation is ongoing.

Nov 3, 2026
PreviousPage 2 of 99 Next
© 2026 cyber.hendryadrian.com