
APT36 Uses Four Malware Variants in RapidRust Campaign, DNS Analysis Finds
Summary
A DNS investigation of APT36’s RapidRust campaign linked its known indicators to 341 email-connected domains, lookalike domains, and two IPs classified as malicious by a threat-intelligence API. The authors caution that some flagged entities may be benign.
Key points
- Zscaler tracks RapidRust as an operation by Pakistan-linked APT36, also known as Transparent Tribe.
- The campaign used four malware variants: RUSTYSHADE, RUSTYMOVE, PSNATCH, and BASHNATCH.
- The researchers examined five network indicators and used historical WHOIS data and reverse WHOIS searches to identify 341 additional email-connected domains.
- Some connected domains appeared to mimic well-known brands; the article says none of these domains were then considered malicious.
- DNS lookups identified two IP addresses that a threat-intelligence API classified as malicious; one was associated with malware distribution from September 19, 2026.
- The authors caution that entities labeled as threats may prove harmless and recommend further investigation.
Article Details
- Attack Vectors
- APT36 reportedly used lookalike domains to impersonate popular Indian news outlets.
- The RapidRust subdomain clients-easy[.]s3[.]us-east-005[.]backblazeb2[.]com was categorized as a malware host.
- The subdomain f005[.]backblazeb2[.]com resolved to an IP address listed for phishing.
- Defensive Notes
- The article recommends supplementary investigation to corroborate entities identified as malicious, since their status may change with further investigation or context.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
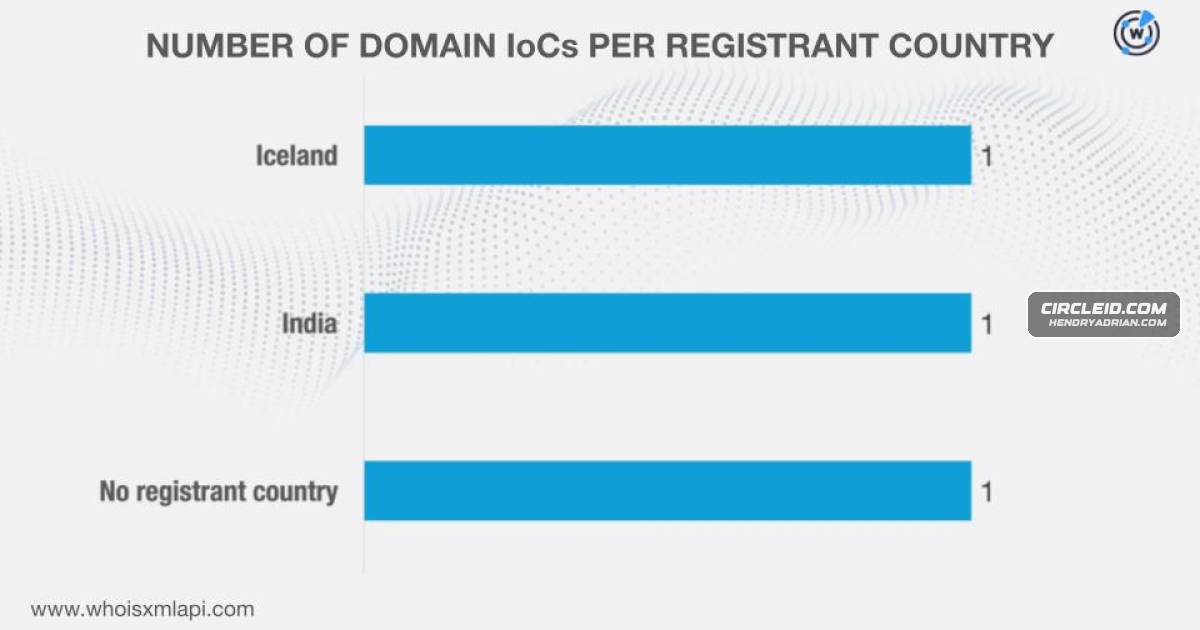
| DOMAIN | indiatodays[.]org | Listed as a RapidRust domain IoC; the article reports APT36 used lookalike domains to impersonate popular Indian news outlets. |
| DOMAIN | officialinfo[.]org | Listed as a RapidRust domain IoC in the article's domain investigation. |
| DOMAIN | theprints[.]org | Listed as a RapidRust domain IoC; the article reports APT36 used lookalike domains to impersonate popular Indian news outlets. |
| HOSTNAME | clients-easy[.]s3[.]us-east-005[.]backblazeb2[.]com | RapidRust subdomain categorized by the Threat Intelligence API as a malware host; DNS findings indicated it was not Backblaze-authored. |
| HOSTNAME | f005[.]backblazeb2[.]com | RapidRust subdomain resolving to an IP address listed for phishing by the Threat Intelligence API. |
| IPV4 | 147[.]182[.]160[.]170 | The article reports this IP address was associated with malware distribution. |
MITRE ATT&CK
Threat Actors
APT36Reportedly conducted the RapidRust operation and used lookalike domains to impersonate Indian news outlets; the article says the group deployed four malware variants.Mythic LeopardThe article identifies Mythic Leopard as another name for APT36, which it reports conducted the RapidRust operation.Transparent TribeThe article identifies Transparent Tribe as another name for APT36, which it reports conducted the RapidRust operation.
Malware
BASHNATCHThe Pakistan-linked threat group used four malware variants—RUSTYSHADE, RUSTYMOVE, PSNATCH, and BASHNATCH—in their latest campaigns.PSNATCHThe Pakistan-linked threat group used four malware variants—RUSTYSHADE, RUSTYMOVE, PSNATCH, and BASHNATCH—in their latest campaigns.RUSTYMOVEThe Pakistan-linked threat group used four malware variants—RUSTYSHADE, RUSTYMOVE, PSNATCH, and BASHNATCH—in their latest campaigns.RUSTYSHADEThe Pakistan-linked threat group used four malware variants—RUSTYSHADE, RUSTYMOVE, PSNATCH, and BASHNATCH—in their latest campaigns.