cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · decodedsecurity.com

A Four-Week Study Strategy for the CompTIA Security+ Exam

The article recommends a three-phase, four-week Security+ study plan: map exam topics, learn fundamentals, start practice tests early, review missed topics, and aim for consistent 80%+ scores before scheduling the exam.
Apr 8, 2026
Security Insights · bleepingcomputer.com

A $30,000 AI GPU Lags Consumer GPUs in Password-Cracking Tests

In a Specops-sponsored comparison using Hashcat benchmarks across five hash algorithms, the RTX 5090 outperformed the Nvidia H200 and AMD MI300X. The article also discusses password length, reuse, breached credentials and MFA.

Apr 8, 2026
Security Insights · huntress.com

Stryker Attack Highlights Risks of Remote Wipes and Five Defensive Steps

A report on the Stryker attack describes alleged access to its device-management environment, mass remote wipes and data theft claims. It offers steps to protect management platforms, limit destructive actions, manage BYOD and practice recovery.

Apr 8, 2026
Security Insights · hackingarticles.in

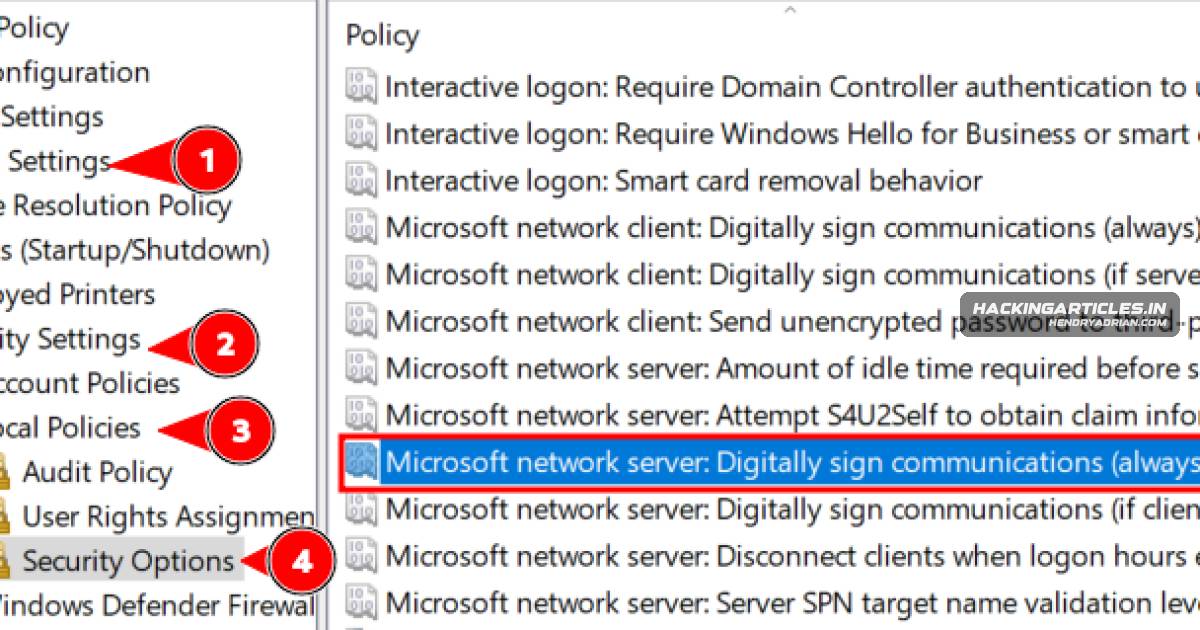
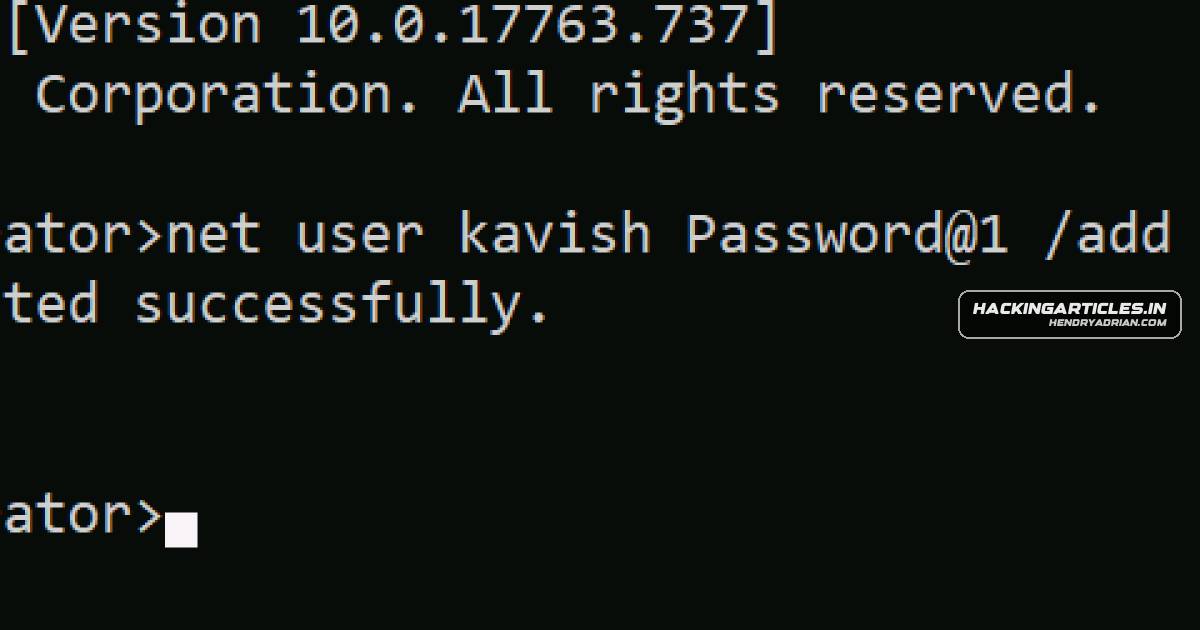
Walkthrough Demonstrates How NTLM Reflection and Delegation Misconfigurations Can Compromise Active Directory

A lab walkthrough chains NTLM reflection/relay, disabled SMB signing, unconstrained delegation and Kerberos ticket abuse to escalate from low-privileged domain access to DCSync and Active Directory domain control, then outlines mitigations.

Apr 7, 2026
Security Insights · hackingarticles.in

Article Demonstrates Windows LOLBin Techniques for DLL Reverse-Shell Execution

The article demonstrates how Windows LOLBins can load a reverse-shell DLL, including process injection with mavinject.exe, and outlines detection ideas and mitigations such as application controls, egress filtering, and privilege limits.

Apr 4, 2026
Security Insights · dti.domaintools.com

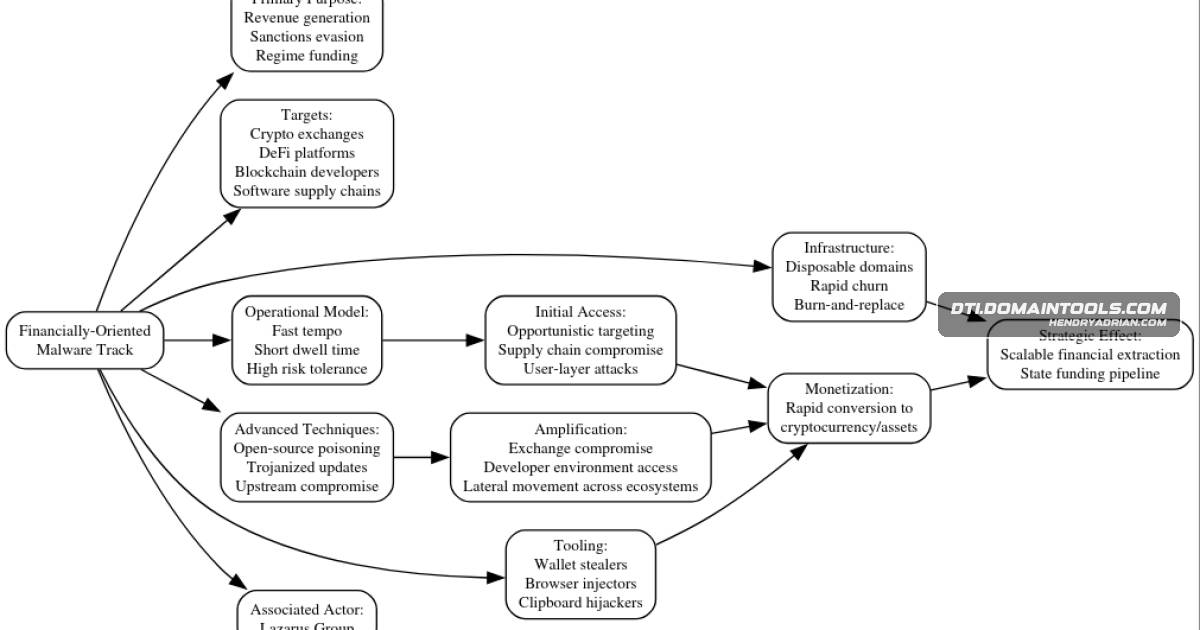
Analysis Frames DPRK Malware as Mission-Specific and Replaceable

The article argues North Korea operates separate espionage, financial and disruptive malware tracks, replacing exposed tools rapidly. It outlines common tactics and recommends behavior-, identity-, supply-chain- and cloud-focused defenses.

Apr 4, 2026
Security Insights · infostealers.com

Unverified Infostealer Credentials Can Trigger False Alerts and Automation Failures

The article argues that recycled or synthetic URL:login:password (ULP) data can poison credential feeds, triggering false alerts and throttled automation. It recommends reserving automated resets for infostealer logs with device and telemetry provenance.

Apr 4, 2026
Security Insights · hackingarticles.in

Lab Walkthrough Shows Kerberos Constrained Delegation Abuse Against SQL Server

A lab walkthrough demonstrates how an attacker with credentials for a misconfigured service account can use S4U2Self and S4U2Proxy to access a SQL Server as an administrator, then extract credentials and obtain a SYSTEM shell. It also covers detection and mitigations.

Apr 2, 2026
Security Insights · decodedsecurity.com

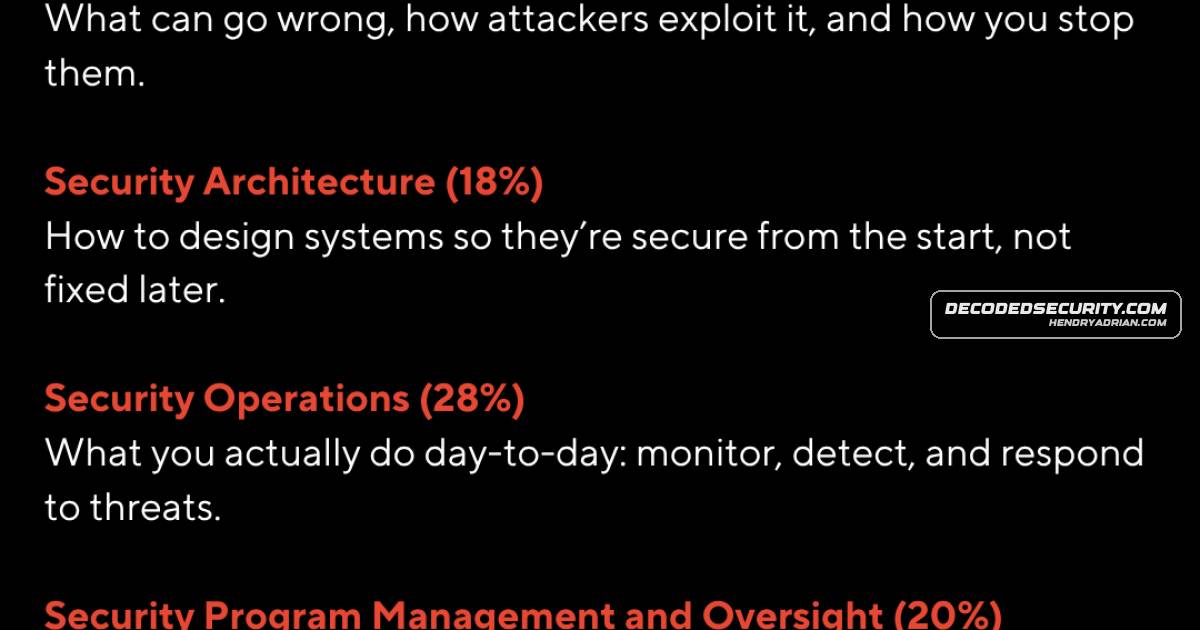
CompTIA Security+ SY0-701 Study Guide: Key Topics Across Five Domains

A study guide outlining the five CompTIA Security+ SY0-701 domains and topics to prioritize, including attacks, secure design, incident response, and risk management. It notes that foundational concepts make up about 12% of the exam.

Apr 2, 2026
Security Insights · thehackernews.com

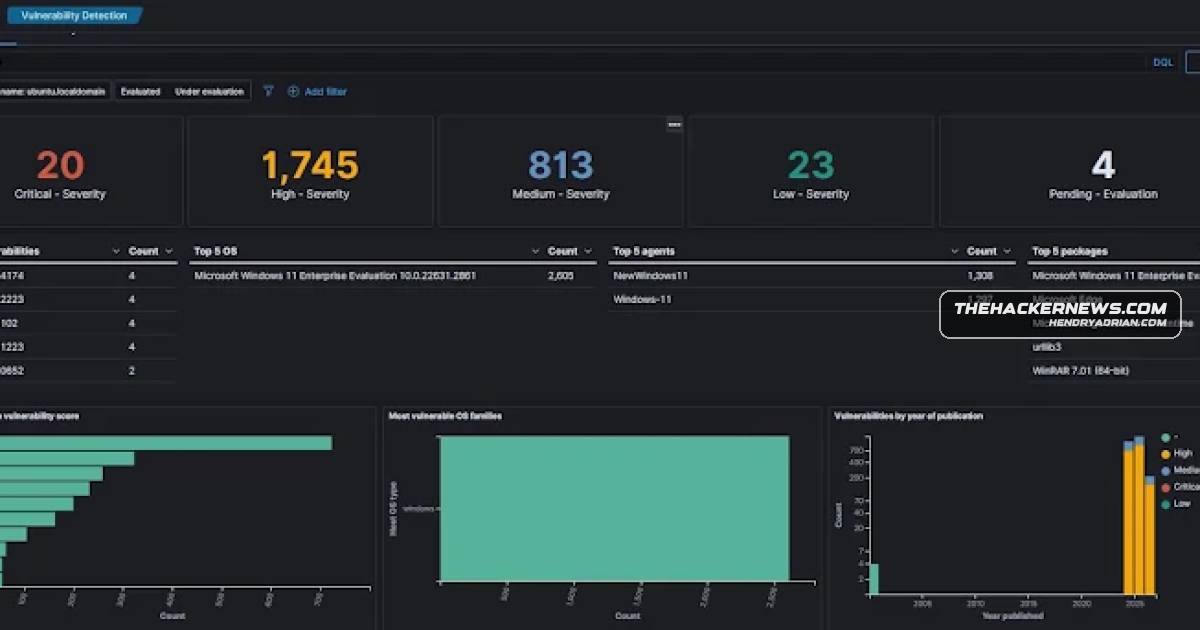
How Wazuh Supports Proactive Vulnerability Management

The article describes how Wazuh combines system inventory, vulnerability detection, CTI enrichment, exploitation alerts, and remediation tracking to support continuous, exploit-aware vulnerability management.

Apr 2, 2026
Security Insights · threatfabric.com

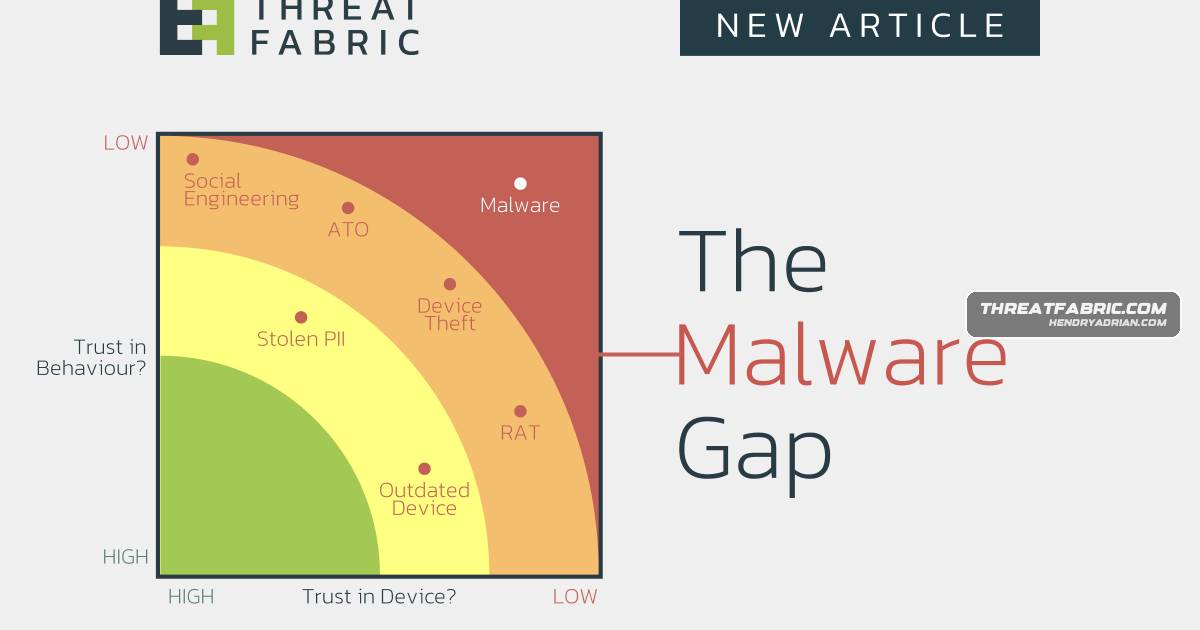
Why Fraud Controls Miss Mobile Malware on Trusted Devices

Mobile malware can combine social engineering, device takeover and automated fraud while evading behavioral and device checks. The article explains how malware intelligence can help identify compromised devices and connect fraud signals.

Apr 2, 2026
Security Insights · opensourcemalware.com

How Attackers Use Social Engineering to Target Open-Source Maintainers

The article explains five tactics used to gain access to open-source projects, including phishing, trust-building and fake job lures, and offers maintainers practical steps to reduce account and supply-chain compromise risks.

Apr 1, 2026
Security Insights · cybersecurityclub.substack.com

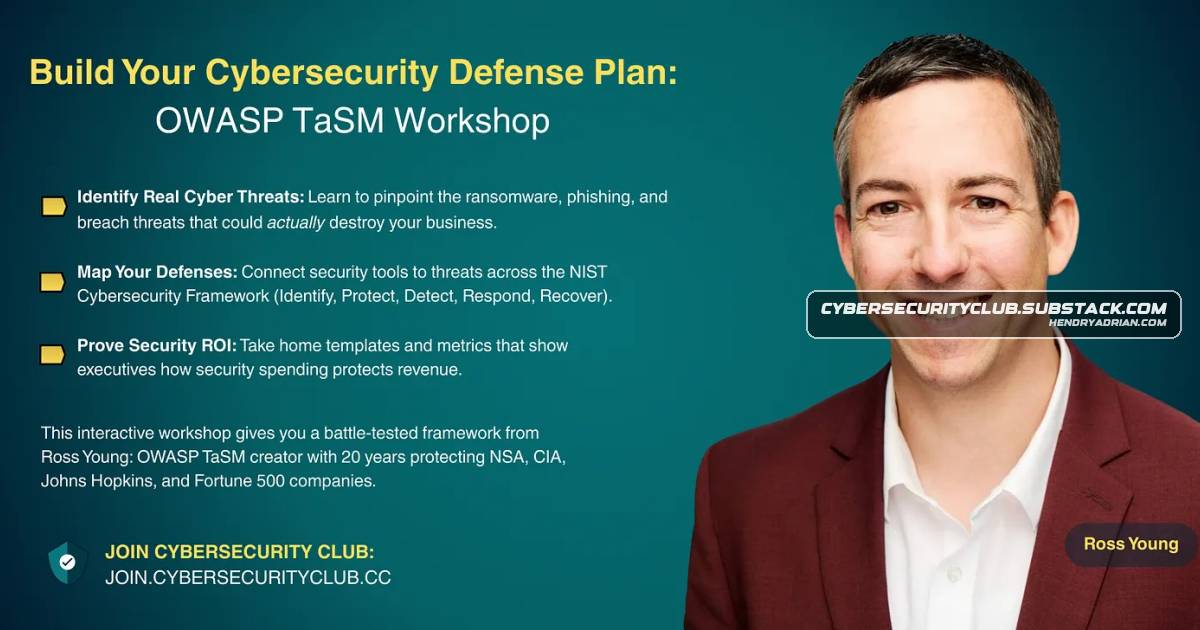
OWASP TaSM Workshop Shows How to Map Threats to Security Safeguards

A workshop demonstrated how OWASP’s Threat and Safeguard Matrix maps risks such as phishing and ransomware to safeguards across the NIST Cybersecurity Framework, including controls for preventing sensitive data leaks into AI tools.

Apr 1, 2026
Security Insights · huntress.com

Three-Finger Test Is an Unreliable Deepfake Defense, Experts Warn

A viral three-finger check can expose flaws in some real-time deepfakes, but experts warn newer tools may overcome it. The article recommends process-based identity verification, such as callbacks and second-channel approval, over visual tells.

Apr 1, 2026
Security Insights · toxsec.com

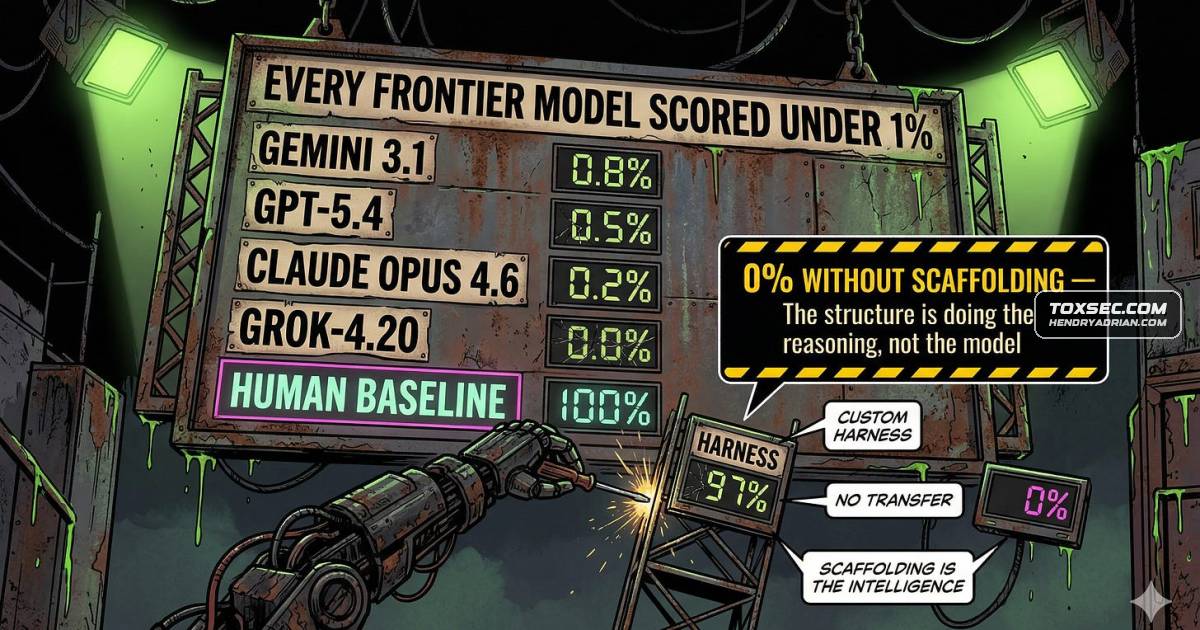
ARC-AGI-3 Scores Highlight AI Agents’ Reasoning Limits as Claude Dispatch Expands Prompt-Injection Risk

The article reports frontier models scoring below 1% on ARC-AGI-3 and argues that Claude Dispatch’s claimed full filesystem access outside Cowork’s sandbox increases prompt-injection risk. It recommends least privilege, network segregation and assuming breach.

Mar 31, 2026
Security Insights · cybersecuritypulse.net

RSAC and BSidesSF 2026 Takeaways: AI Agents, SOC Architecture, and Supply-Chain Risk

A conference recap argues that MCP-enabled AI agents and decoupled data architectures are reshaping security operations, while AI-related data-access concerns and recent supply-chain compromises heighten risks.

Mar 31, 2026
Security Insights · securityweek.com

Why Data Integrity Is Becoming a Cybersecurity Concern

The article argues that manipulated or poorly governed data can undermine AI outputs and security detection. It recommends clear dataset ownership, controlled and traceable changes, audit trails, and authoritative sources.

Mar 31, 2026
Security Insights · securityweek.com

Stolen Credentials Fuel Ransomware, Supply-Chain and Nation-State Attacks

The article links industrial-scale credential theft to ransomware, SaaS and supply-chain attacks, and geopolitical operations, citing 2025 trends and recommending closer monitoring of human and machine identity activity.

Mar 31, 2026
Security Insights · thecyberexpress.com

Jennifer Cox on the Human and Operational Challenges of Security Automation

Tines' Jennifer Cox says automation's benefits depend on aligning people and processes, not simply adding tools. She cites alert handling, investigations and compliance as use cases, and recommends guardrails, resilient error handling and business-focused metrics.

Mar 31, 2026
Security Insights · hackingarticles.in

Pass-the-Certificate Demonstrates Active Directory Access With PFX and Kerberos Tickets

A hands-on guide demonstrates using PFX certificates and derived CCACHE tickets for remote execution across Active Directory protocols, compares tools’ execution artifacts, and outlines detection opportunities and defenses.

Mar 31, 2026
Security Insights · decodedsecurity.com

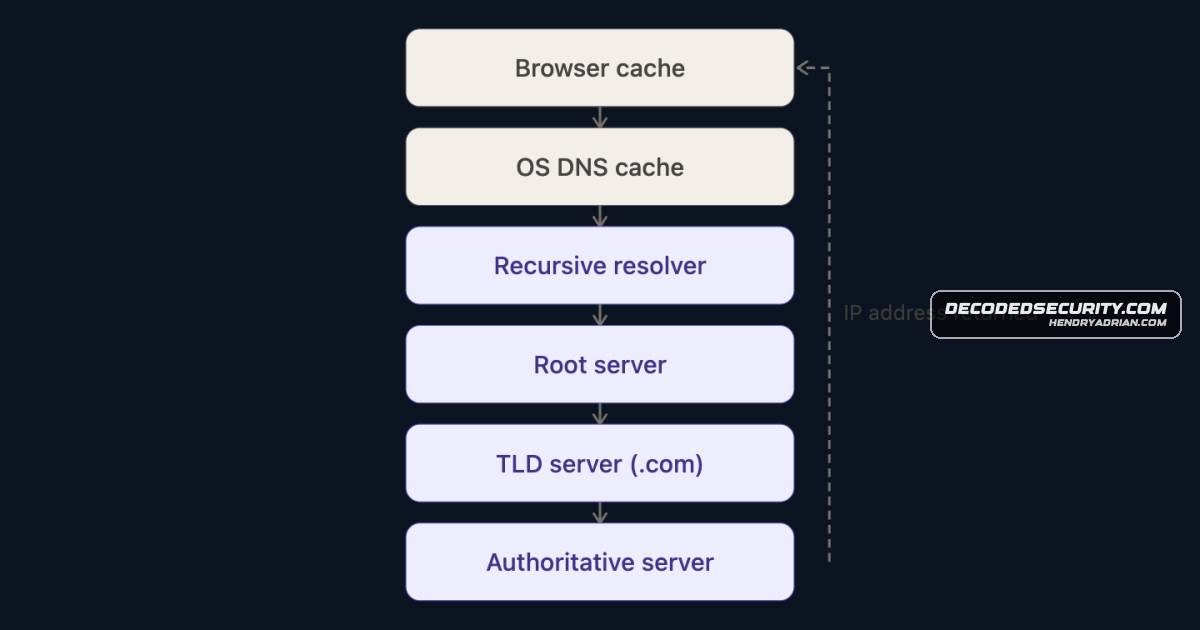
How a Browser Loads a Website: DNS, TCP, TLS, HTTP, and Rendering

An explainer walks through URL parsing, DNS resolution, the TCP handshake, TLS authentication and key exchange, HTTP requests, and browser rendering, with a Docker lab for practicing DNS, HTTP, and TLS.

Mar 31, 2026
Security Insights · bleepingcomputer.com

How to Categorize Enterprise AI Agents and Prioritize Their Security Risks

The article groups enterprise AI agents into chatbots, local agents, and production agents, explaining how access and autonomy shape risk and why identity visibility, governance, and least-privilege permissions matter.

Mar 31, 2026
Security Insights · trendmicro.com

AI-Assisted “Vibecoding” Can Outpace Security Reviews and Increase Software Risk

Trend Micro argues that AI-generated code can accelerate development faster than teams can review, govern, and understand changes, increasing risks from unsafe defaults, dependencies, weak secret handling, and unclear ownership.

Mar 31, 2026
Security Insights · blog.sucuri.net

Nulled WordPress Plugins Can Expose Sites to Malware, Backdoors, and Unpatched Vulnerabilities

Nulled WordPress plugins may contain malware and backdoors, miss security updates, and lead to SEO and legal consequences. The article recommends checking suspicious installations, using legitimate alternatives, and maintaining updates, scanning, strong passwords, 2FA,和

Mar 30, 2026
PreviousPage 35 of 54 Next
© 2026 cyber.hendryadrian.com