

Okta-Sponsored Webinar to Discuss IAM Blind Spots and Identity Risks
A sponsored webinar on October 29, 2026, will discuss identity and access management risks, including orphaned accounts, fragmented identities, and manual access processes.
A sponsored webinar on October 29, 2026, will discuss identity and access management risks, including orphaned accounts, fragmented identities, and manual access processes.
An AXA XL cyber risk executive says cybercrime is operating like an industry, with AI helping threats move faster and scale. She highlights people, governance, training and tested crisis exercises as parts of resilience before a breach.
A workshop demonstrated how OWASP’s Threat and Safeguard Matrix maps risks such as phishing and ransomware to safeguards across the NIST Cybersecurity Framework, including controls for preventing sensitive data leaks into AI tools.
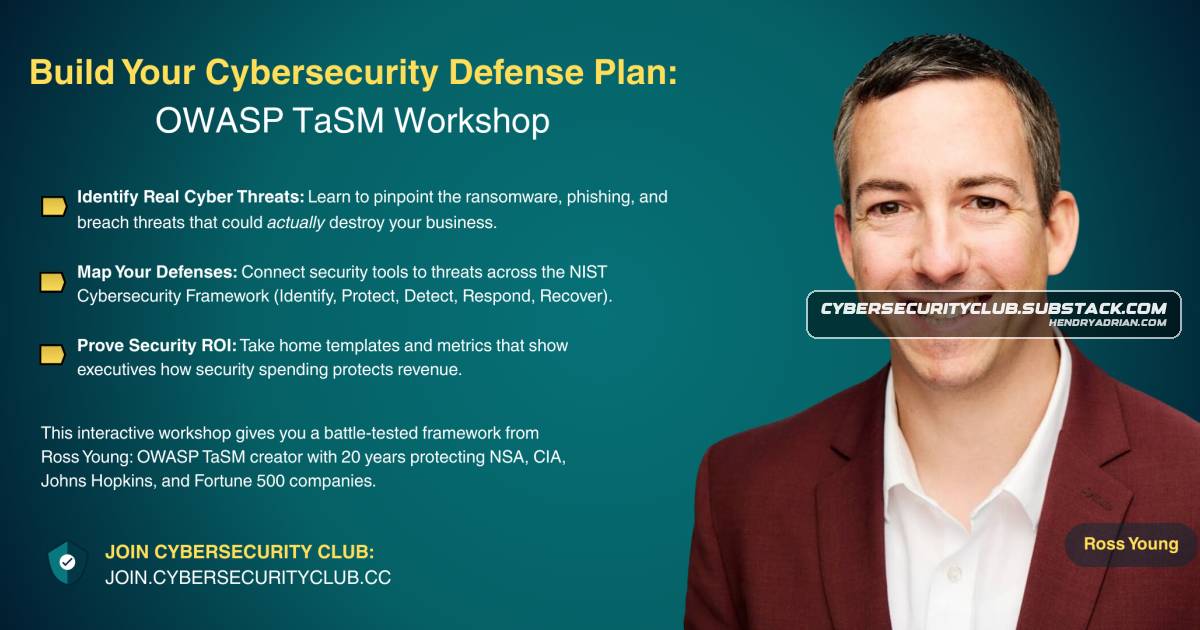
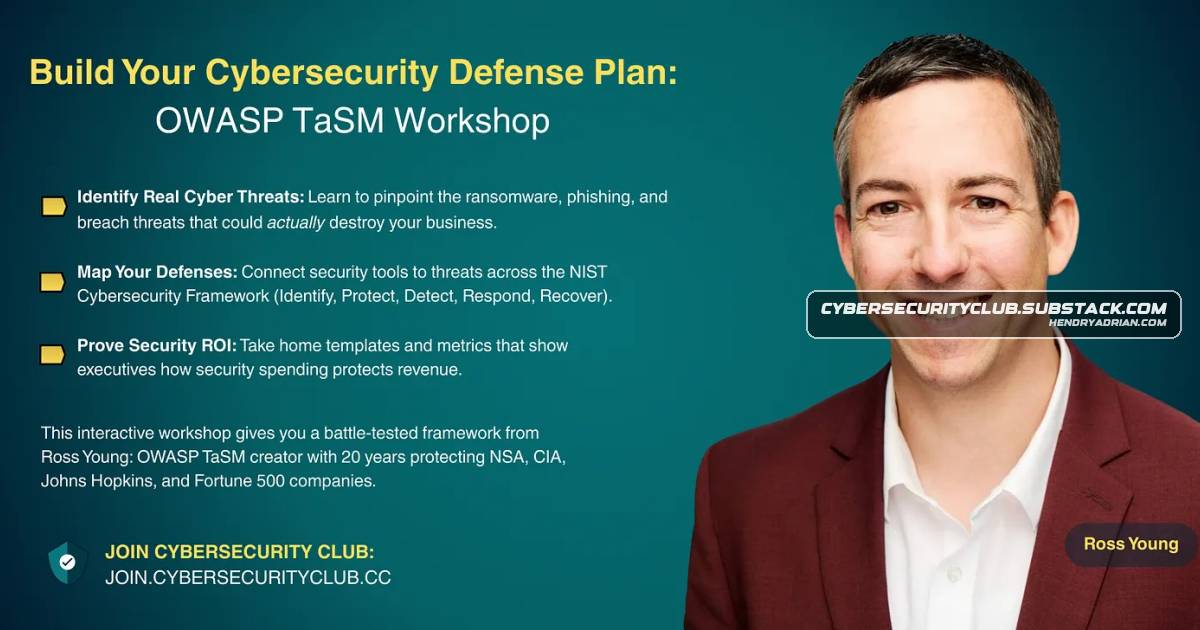
A workshop led by Ross Young, a former CIA and NSA officer and corporate CISO, was scheduled for March 31, 2026. It was to cover the TaSM framework, threat prioritization, security metrics, and budget justification.
A promotional overview of HTB Academy’s hands-on cybersecurity training, including role-based and skill-based learning paths, offensive security modules, and a signup offer for 50 free cubes.
The article recommends mapping controls across the NIST Cybersecurity Framework’s five functions, then using the TaSM framework to prioritize safeguards against business-relevant threats. It promotes a virtual workshop on the approach.
The article outlines how a threat matrix using the TaSM framework can help organizations map and prioritize AI risks, including data leaks, model supply-chain issues, and misuse, and promotes a live workshop on applying it.
Cybersecurity Club highlights resources for cloud security certification, intelligence analysis, Munge vulnerability research, binary exploitation, reverse engineering, and foundational IT learning.
The article explains how security teams can connect controls and threats to business outcomes using the Threat and Safeguard Matrix (TaSM), executive scorecards, and related workshop materials.
A phased roadmap introduces Linux fundamentals, command-line and virtual-machine practice, then security-focused distributions and tools for controlled cybersecurity labs.
The article recommends seven tools for adding automated API and application security scanning to CI/CD pipelines, including OWASP ZAP, Snyk, Burp Suite, Checkmarx, SonarQube, Trivy, and StackHawk.
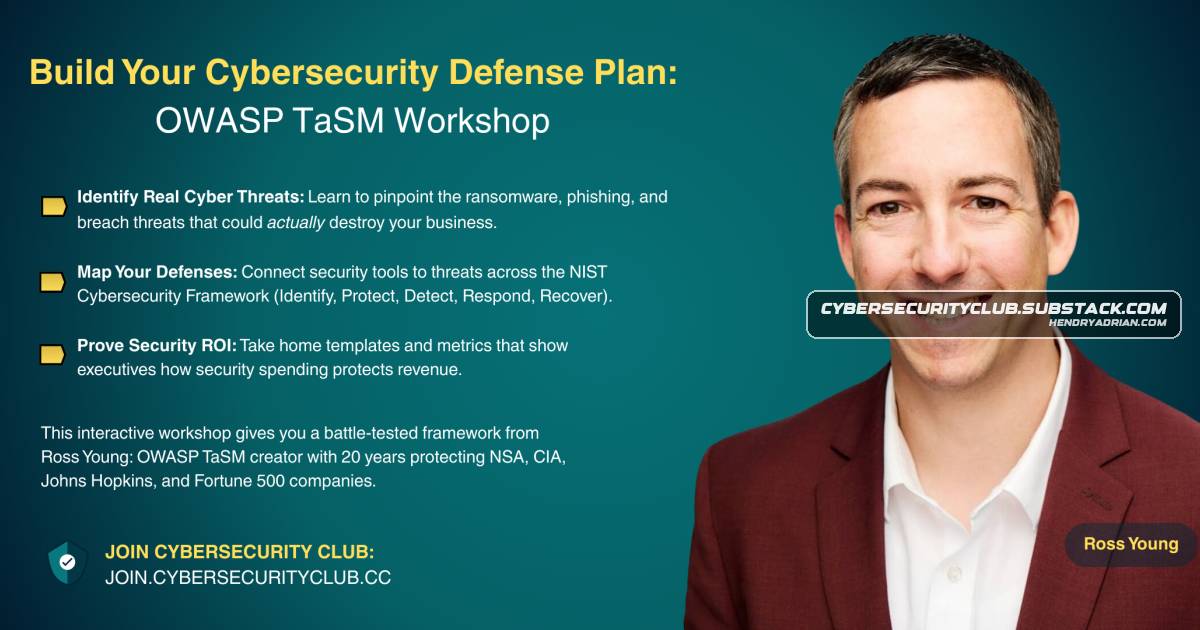
A virtual workshop on March 31, 2026, will guide participants through using the OWASP Threat and Safeguard Matrix to prioritize organizational threats, map defenses across the NIST CSF, measure progress, and justify security budgets.
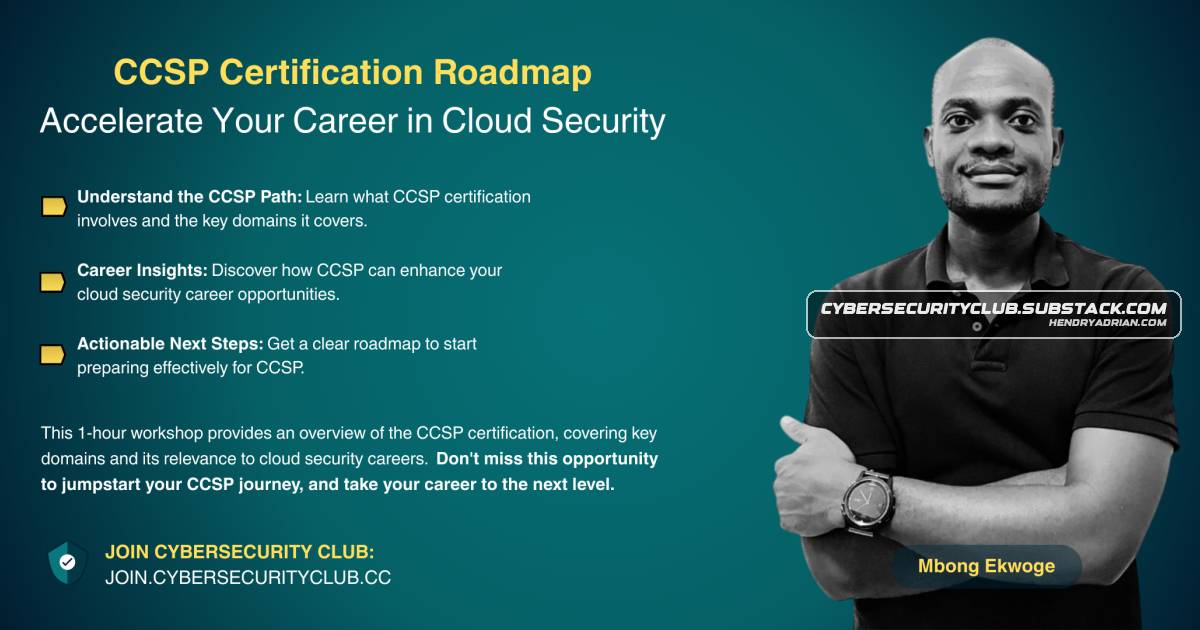
A Cybersecurity Club session recapped CCSP exam preparation, cloud security career paths, and practical guidance on AI, DevSecOps, and study resources.