
Analysis Frames DPRK Malware as Mission-Specific and Replaceable
Summary
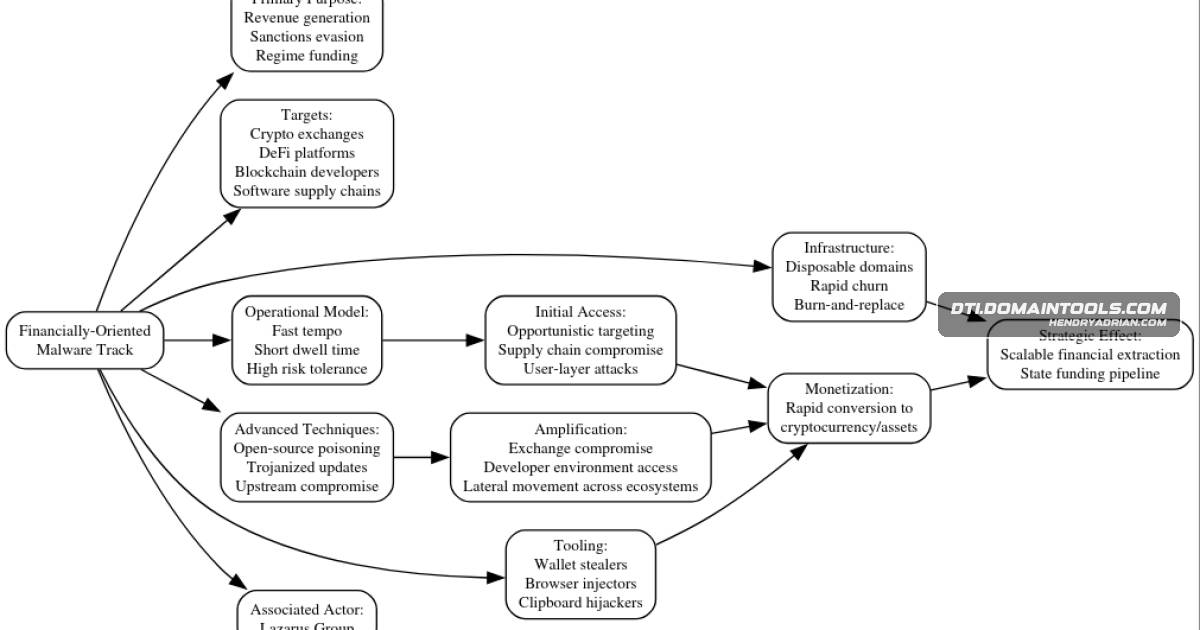
The article argues North Korea operates separate espionage, financial and disruptive malware tracks, replacing exposed tools rapidly. It outlines common tactics and recommends behavior-, identity-, supply-chain- and cloud-focused defenses.
Key points
- The article argues DPRK malware operations are divided into espionage, financial and disruptive tracks, with exposed tools treated as replaceable.
- It associates espionage operations with spearphishing, PowerShell or VBS loaders, memory-resident backdoors, credential abuse and trusted cloud services.
- It describes financial operations as targeting cryptocurrency through wallet stealers, browser injectors, clipboard hijacking and supply-chain compromises.
- It characterizes disruptive operations as using wipers or ransomware-like payloads and rapid lateral movement for short-term impact.
- The analysis points to shared loader designs, cryptographic routines, infrastructure preferences and social engineering across the mission tracks.
- It recommends prioritizing behavioral analytics, identity monitoring, supply-chain security and cloud telemetry rather than relying on malware signatures alone.
Article Details
- Topic
- Mission-aligned compartmentalization and rapid replacement of DPRK malware across espionage, financial theft, and disruptive operations
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| SHA256 | 0518a163b90e7246a349440164d02d10f31d514a7e5cce842b6cf5b3a0cc1bfa | NodalBaker sample listed under GOLDEN CHOLLIMA's revenue track. |
| SHA256 | 05feed9762bc46b47a7dc5c469add9f163c16df4ddaafe81983a628da5714461 | Hoplight malware sample listed under LABYRINTH CHOLLIMA. |
| SHA256 | 081804b491c70bfa63ecdbe9fd4618d3570706ad8b71dba13e234069648e5e48 | TwoPence Electric sample listed under PRESSURE CHOLLIMA's crypto-theft track. |
| SHA256 | 1579347265f948f9646931335d57e7960fe65dd429394be84b4ae15bca73dfde | MagikCookie sample listed under PRESSURE CHOLLIMA's crypto-theft track. |
| SHA256 | 2110a6e89d98a626f846ec8deccbac057300d194933ae0cbf1ef4831a4cc829e | Anycon sample listed under GOLDEN CHOLLIMA's revenue track. |
| SHA256 | 2ef212f433b722b734d80b41a2364a41ca0453dbfe3e6ec8b951eca795075a02 | PipeDown sample listed under GOLDEN CHOLLIMA's revenue track. |
| SHA256 | 357c9daf6c4343286a9a85a27bc25defdc056877ce1be2943d2e8ede3bce022c | MataNet sample listed under PRESSURE CHOLLIMA's crypto-theft track. |
| SHA256 | 453d8bd3e2069bc50703eb4c5d278aad02304d4dc5d804ad2ec00b2343feb7a4 | Hawup RAT malware sample listed under LABYRINTH CHOLLIMA. |
| SHA256 | 4fe3c853ab237005f7d62324535dd641e1e095d1615a416a9b39e042f136cf6b | Joanap malware sample listed under LABYRINTH CHOLLIMA. |
| SHA256 | 512877c98fd83cd51bb287da4462b44f9d276d7ce51890f4ded1b915a6d2d5e1 | NedDnLoader sample listed under LABYRINTH CHOLLIMA. |
| SHA256 | 56e51244e258c39293463c8cf02f5dddb085be90728fab147a60741cf014aa4d | GhostShip sample listed under PRESSURE CHOLLIMA's crypto-theft track. |
| SHA256 | 58f2972c6a8fc743543f7b8c4df085c5cf2c6e674e5601e85eec60cd269cfb3c | HiberRAT malware sample listed under LABYRINTH CHOLLIMA. |
| SHA256 | 666c50b8b772101b0e2e35ff1de52a278c2727027b54858e457571d296fec50b | StatusSymbol sample listed under PRESSURE CHOLLIMA's crypto-theft track. |
| SHA256 | 73edc54abb3d6b8df6bd1e4a77c373314cbe99a660c8c6eea770673063f55503 | KorDLL Bot malware sample listed under LABYRINTH CHOLLIMA. |
| SHA256 | 7dee2bd4e317d12c9a2923d0531526822cfd37eabfd7aecc74258bb4f2d3a643 | Dozer malware sample listed under LABYRINTH CHOLLIMA. |
| SHA256 | 9ba02f8a985ec1a99ab7b78fa678f26c0273d91ae7cbe45b814e6775ec477598 | SparkDownloader sample listed under PRESSURE CHOLLIMA's crypto-theft track. |
| SHA256 | a61ecbe8a5372c85dcf5d077487f09d01e144128243793d2b97012440dcf106e | SwDownloader sample listed under PRESSURE CHOLLIMA's crypto-theft track. |
| SHA256 | a795964bc2be442f142f5aea9886ddfd297ec898815541be37f18ffeae02d32f | Koredos malware sample listed under LABYRINTH CHOLLIMA. |
| SHA256 | b6995c31a7ee88392fc25fd6d1a3a7975b3cb4ec3a9a318c3fcfaaf89eb65ce1 | SnakeBaker sample listed under GOLDEN CHOLLIMA's revenue track. |
| SHA256 | b9f6a9d4f837f5b8a5dc9987a91ba44bc7ae7f39aa692b5b21dba460f935a0ae | Scuzzyfuss sample listed under PRESSURE CHOLLIMA's crypto-theft track. |
| SHA256 | cbd1634cf7c638f2faf5e3ec79137db6704ec9de8df798fc46aeeed38de3da9b | FudModule sample listed under LABYRINTH CHOLLIMA and GOLDEN CHOLLIMA. |
| SHA256 | d0cf9c1f87eac9b8879684a041dd6a2e1a0c15e185d4814a51adda19f9399a9b | CitriLoader sample listed under GOLDEN CHOLLIMA's revenue track. |
| SHA256 | d2359630e84f59984ac7ddebdece9313f0c05f4a1e7db90abadfd86047c12dd6 | Brambul malware sample listed under LABYRINTH CHOLLIMA. |
| SHA256 | dced1acbbe11db2b9e7ae44a617f3c12d6613a8188f6a1ece0451e4cd4205156 | Manuscrypt malware sample listed under LABYRINTH CHOLLIMA. |
| SHA256 | e0aa5ef3af26681a8c8b46d95656580779d0ff3c2fe531b95a59ee918686e443 | AlertConf sample listed under PRESSURE CHOLLIMA's crypto-theft track. |
| SHA256 | f749c7e84809ffc3939eaed06ad90e15b0e11375f98d7348c0aa1bf35d3f0b8e | OpenSSL Downloader sample listed under LABYRINTH CHOLLIMA. |
| SHA256 | f9586fdf4e0a65b17ee32bc3c3f493a055409abde373720d594d27fd24adffa0 | UnderGroundRAT malware sample listed under LABYRINTH CHOLLIMA. |
| SHA256 | fde50c3a373ebc2661e08c99c1cb50dc34efc022a3880c317ab5b84108ef83aa | DevobRAT sample listed under GOLDEN CHOLLIMA's revenue track. |
| SHA256 | fe948451df90df80c8028b969bf89ecbf501401e7879805667c134080976ce2e | Jeus sample listed under GOLDEN CHOLLIMA's revenue track. |
| SHA256 | ff32bc1c756d560d8a9815db458f438d63b1dcb7e9930ef5b8639a55fa7762c9 | HTTPHelper sample listed under GOLDEN CHOLLIMA's revenue track. |
MITRE ATT&CK
T1059.001 · PowerShellEspionage malware uses PowerShell in script-heavy loaders.T1059.005 · Visual BasicEspionage malware uses VBS in script-heavy loaders.T1071.001 · Web ProtocolsThe article identifies use of trusted cloud services for command-and-control and staging.T1078 · Valid AccountsOperations rely on credential abuse and trusted account usage to maintain access.T1115 · Clipboard DataFinancial malware hijacks clipboard contents to redirect cryptocurrency transfers.T1195 · Supply Chain CompromiseOperators embed malicious code in open-source packages or trojanize software updates.T1485 · Data DestructionDisruptive operations deploy wipers to cause widespread disruption.T1566.001 · Spearphishing AttachmentEspionage operations use weaponized documents and tailored lures for initial access.
Threat Actors
AndarielLinked in the article to disruptive campaigns emphasizing sabotage and rapid execution.Golden ChollimaThe appendix associates this tracked cluster with revenue operations targeting fintech and cryptocurrency and lists representative malware samples.Hidden CobraThe article says U.S. agencies use this collective designation for North Korean state actors associated with published malware reports.Jade SleetThe appendix associates this tracked cluster with high-payout cryptocurrency theft and lists representative malware samples.KimsukyAssessed in the article as a DPRK intelligence-collection component associated with sustained espionage.Labyrinth ChollimaThe appendix associates this tracked cluster with espionage and lists representative malware samples.Lazarus GroupAssociated in the article with DPRK revenue-focused operations targeting financial and cryptocurrency ecosystems.
Malware
AppleJeus[Malware Family Names ] Government- and vendor-published family labels linked to DPRK activity – BLINDINGCAN, Joanap, Manuscrypt, AppleJeus, and many additional families documented by CISA/industry.BADCALLBADCALL – Proxy server malware with Fake TLS methods.BLINDINGCAN[Malware Family Names ] Government- and vendor-published family labels linked to DPRK activity – BLINDINGCAN, Joanap, Manuscrypt, AppleJeus, and many additional families documented by CISA/industry.Brambul(Dozer), d2359630e84f59984ac7ddebdece9313f0c05f4a1e7db90abadfd86047c12dd6 (Brambul), and 30+ other SHA256 exemplars cited in the appendix.COPPERHEDGECOPPERHEDGE – Manuscrypt family variant attributed to North Korean APT targeting exchanges/crypto ecosystems.Dozerfrom multiple DPRK-linked clusters – 7dee2bd4e317d12c9a2923d0531526822cfd37eabfd7aecc74258bb4f2d3a643 (Dozer), d2359630e84f59984ac7ddebdece9313f0c05f4a1e7db90abadfd86047c12dd6 (Brambul), and 30+ other SHA256ELECTRICFISHELECTRICFISH – Proxy malware for tunnelled traffic.Joanap[Malware Family Names ] Government- and vendor-published family labels linked to DPRK activity – BLINDINGCAN, Joanap, Manuscrypt, AppleJeus, and many additional families documented by CISA/industry.MANUSCRYPT[Malware Family Names ] Government- and vendor-published family labels linked to DPRK activity – BLINDINGCAN, Joanap, Manuscrypt, AppleJeus, and many additional families documented by CISA/industry.TAINTEDSCRIBETAINTEDSCRIBE – Full-featured beaconing implant used by DPRK actors.
Countries
Industries
Academic researchvalue rather than their economic utility, encompassing government ministries, defense contractors, academic research centers, think tanks, and organizations operating at the margins of policy formation.CryptocurrencyTargeting is broad and opportunistic, with a pronounced focus on cryptocurrency exchanges, blockchain developers, decentralized finance platforms, and the software supply chains that underpin them.Defensefor their informational value rather than their economic utility, encompassing government ministries, defense contractors, academic research centers, think tanks, and organizations operating at the margins of policyfinanceParallel to this, target environments particularly in finance, technology, and government have become more defensively mature, with improved telemetry, faster incident response cycles, and greater cross-sectorGovernment[Malware Family Names ] Government- and vendor-published family labels linked to DPRK activity – BLINDINGCAN, Joanap, Manuscrypt, AppleJeus, and many additional families documented by CISA/industry.TechnologyParallel to this, target environments particularly in finance, technology, and government have become more defensively mature, with improved telemetry, faster incident response cycles, and greater cross-sector